
super-trouper
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
android-securitybinary-analysisdebuggers+5
crissyfield/super-trouperMCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
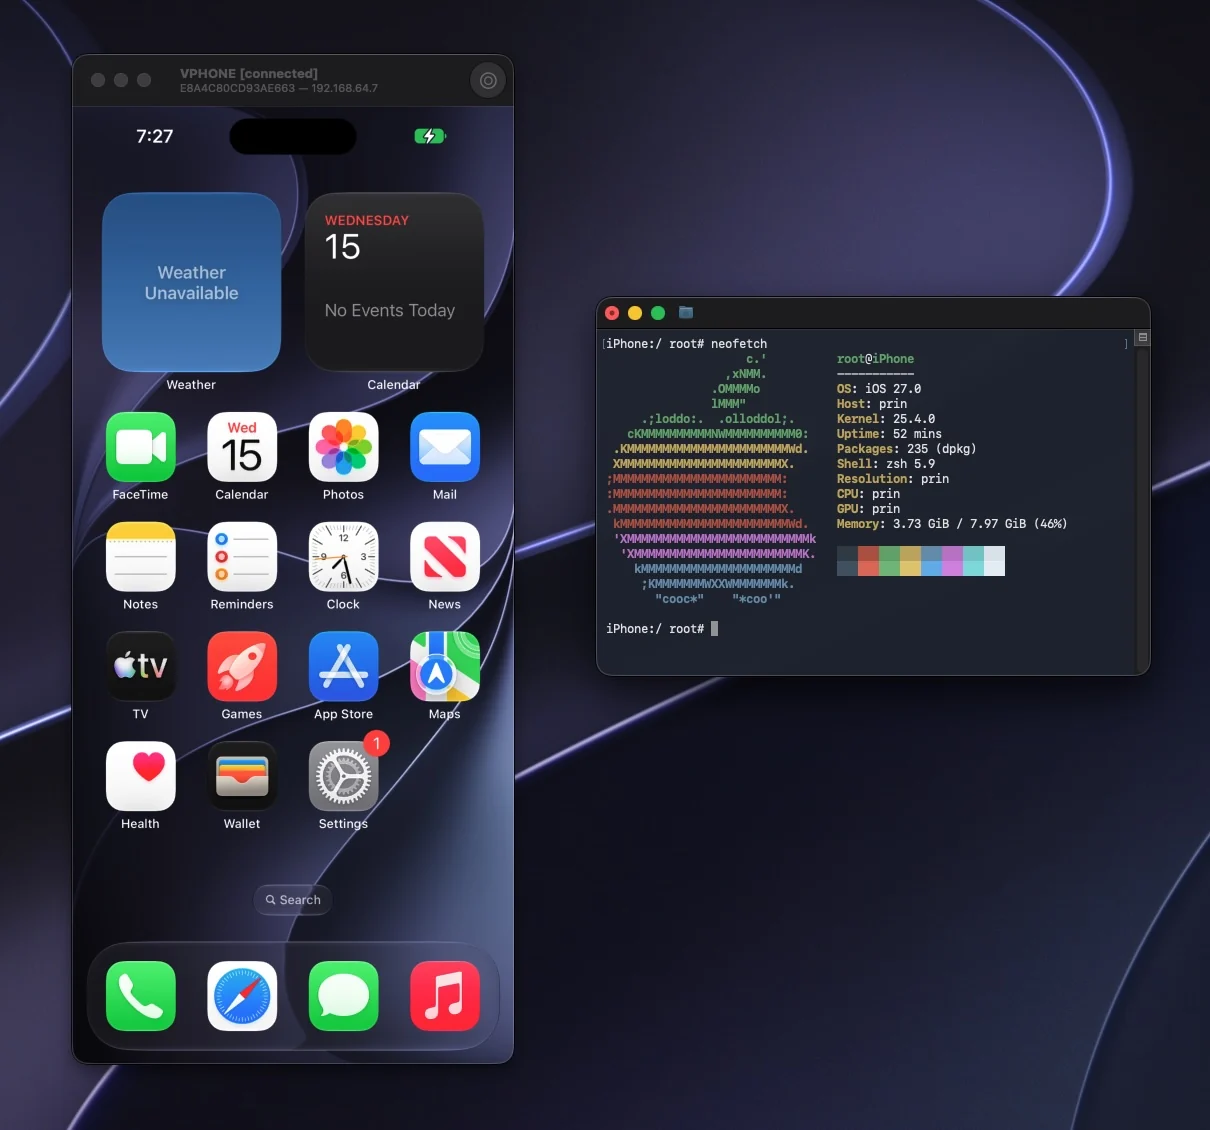 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 palera1n/palera1n
Jailbreak for A8 through A11, T2 devices, on iOS/iPadOS/tvOS 15.0, bridgeOS 5.0 and higher.
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 kpwn/yalu102
incomplete iOS 10.2 jailbreak for 64 bit devices by qwertyoruiopz and marcograssi
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 felix-pb/kfd
kfd, short for kernel file descriptor, is a project to read and write kernel memory on Apple devices.
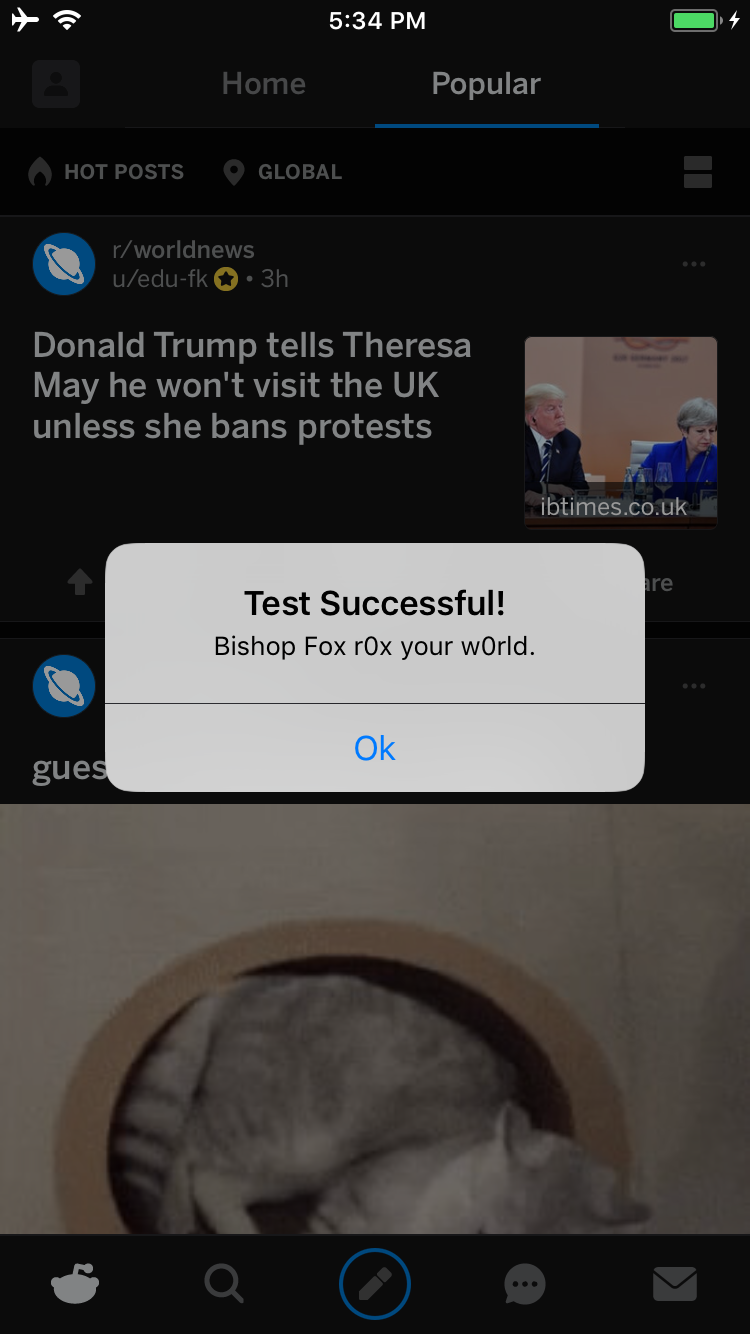 bishopfox/bfinject
Dylib injection for iOS 11.0 - 11.1.2 with LiberiOS and Electra jailbreaks
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 soulghost/iblessing
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
 kpwnz/def1nit3lyn0taja1lbr3aktool
A jailbreak tool for all arm64 devices on iOS 16.0 to iOS 16.6.1
 potmdehex/multicast_bytecopy
kernel r/w exploit for iOS 15.0 - 15.1.1
 b1n4r1b01/desc_race
iOS 15.1 kernel exploit POC for CVE-2021-30955
 0x36/weightbufs
ANE kernel r/w exploit for iOS 15 and macOS 12
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…