
iDescriptor
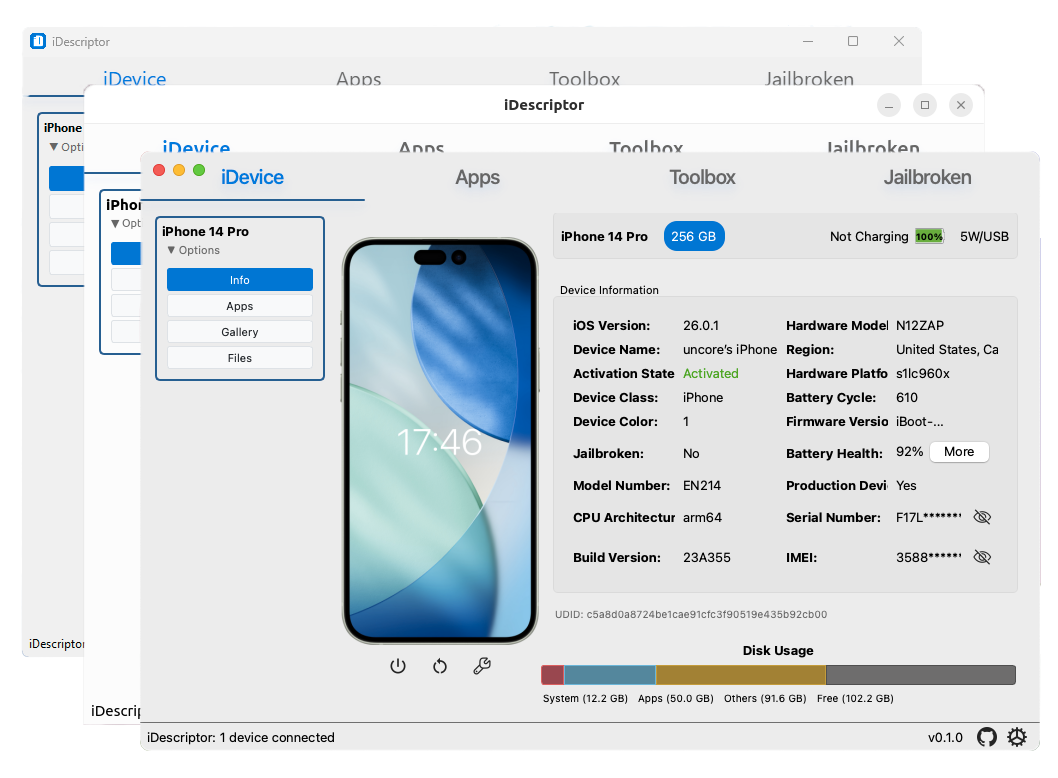
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
digital-forensicsforensicsinformation-gathering+6
4.7k
idescriptor/idescriptorprivacy-first, open-source and free idevice management tool written in Rust and Qt
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 l3onkers/fuxios
Modernized Python 3 exploit PoC for CVE-2016-4631 targeting iOS devices. Features network scanning, malformed IP/TCP payload generation, and packet…
 feliam/cve-2014-4378
Exploit analysis for CVE-2014-4378: information disclosure in Apple CoreGraphics via crafted PDF, enabling memory layout leak and bypass of ASLR,…
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 speedyfriend433/cve-2026-28867-poc
Kernel info leak Proof of Concept patched in iOS 26.4 / macOS 26.4
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 illusionofchaos/ios-gamed-0day
iOS gamed exploit (fixed in 15.0.2)
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
 illusionofchaos/ios-nehelper-enum-apps-0day
iOS 15 0-day exploit (still works in 15.0.2)
 bazad/x18-leak
CVE-2018-4185: iOS 11.2-11.2.6 kernel pointer disclosure introduced by Apple's Meltdown mitigation.
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 biscuitehh/cve-2022-46718-leaky-location
CVE-2022-46718: an app may be able to read sensitive location information.