
awesome-ios-security
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
ctfcurated-resourcesdynamic-analysis-sandboxing+9
680
cy-clon3/awesome-ios-securityA curated list of awesome iOS application security resources.
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 reverseclabs/needle
The iOS Security Testing Framework
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 vaib25vicky/awesome-mobile-security
An effort to build a single place for all useful android and iOS security related stuff. All references and tools belong to their respective owners.…
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
 dmayer/idb
idb is a tool to simplify some common tasks for iOS pentesting and research
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 frida/frida
Main repo for hosting release binaries
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 signalapp/signal-ios
Open-source iOS messenger providing end-to-end encrypted text, voice, and video calls via the Signal Protocol, with no analytics or telemetry…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
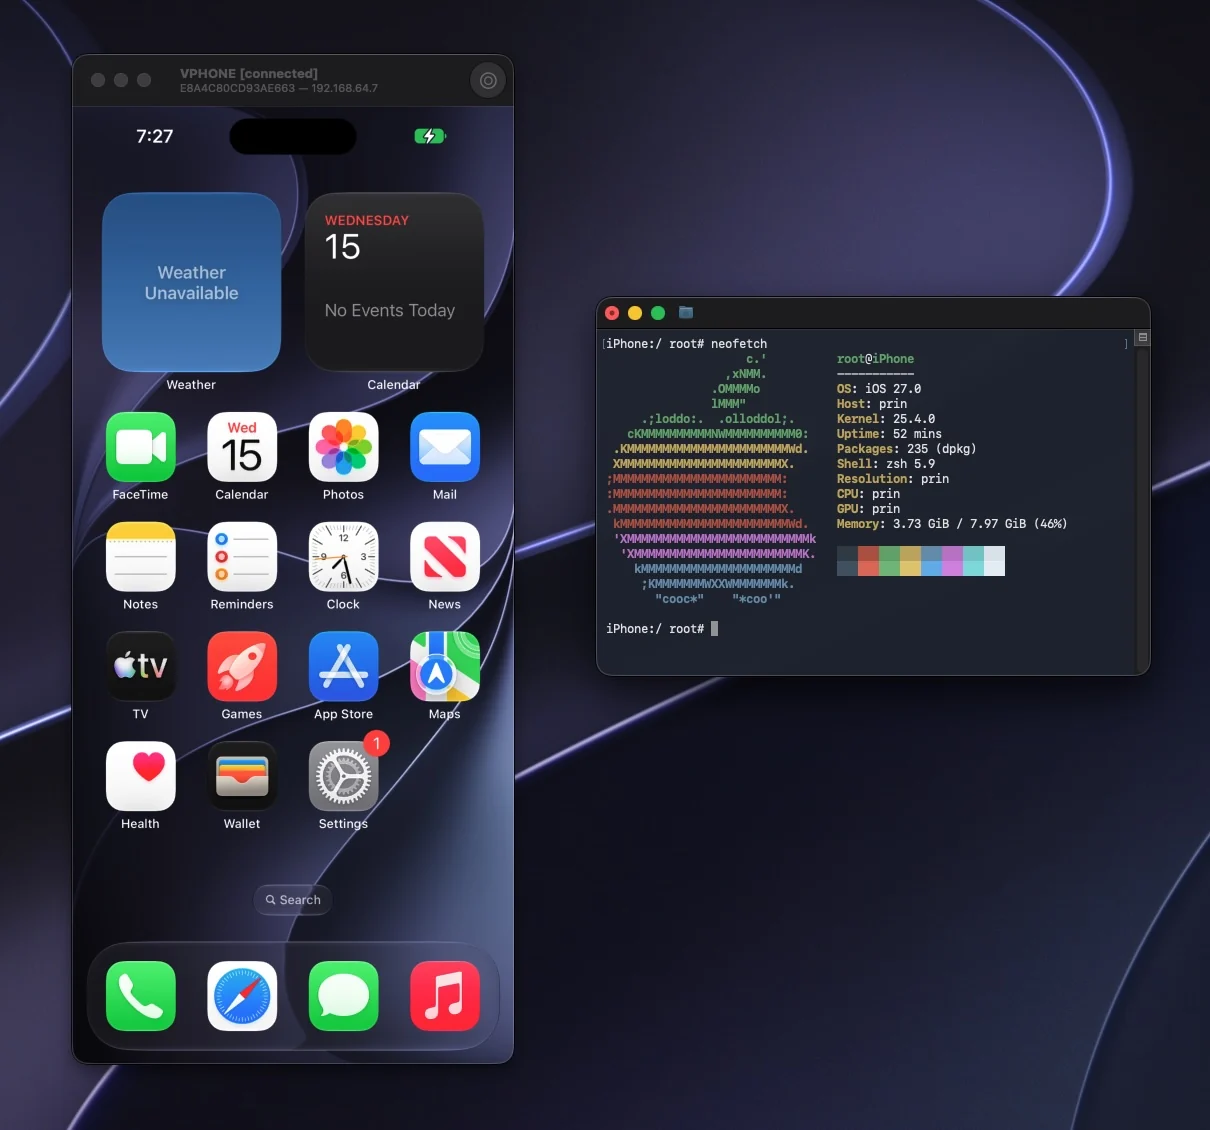 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…