Inferno
 chefkissinc/inferno
Apple Silicon device emulator.
embedded-systems-securityhardware-securityios-security+3
chefkissinc/infernoApple Silicon device emulator.
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
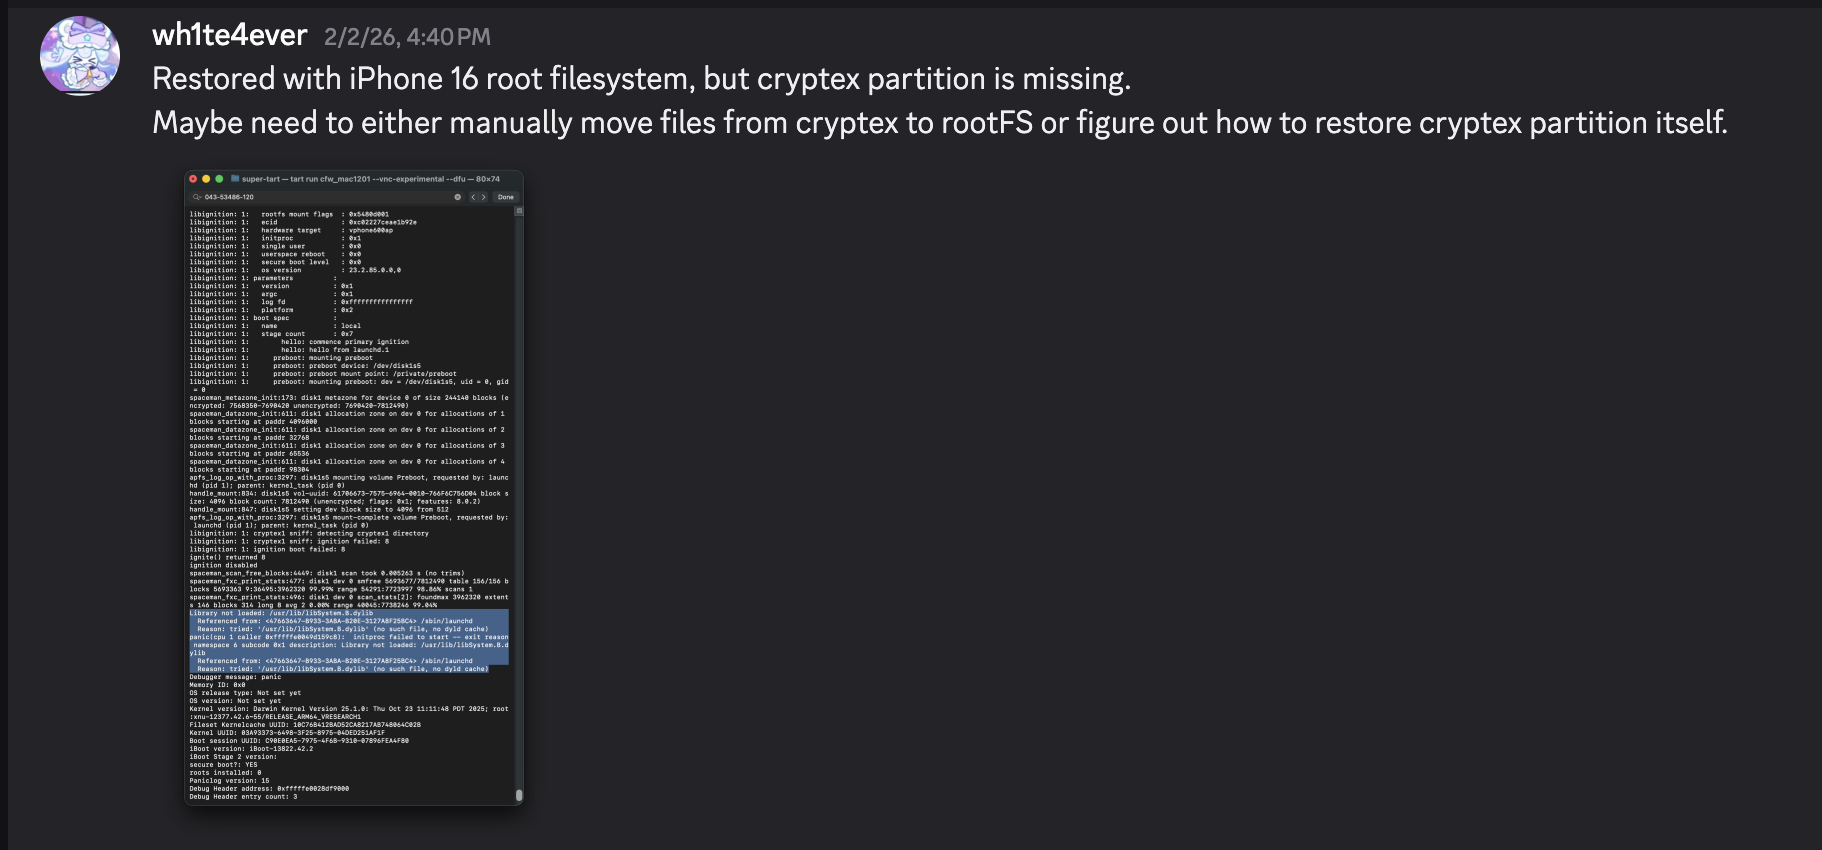 wh1te4ever/super-tart-vphone-writeup
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 danielw98/zero-click-exploit-analysis
CVE-2025-55177 + CVE-2025-43300: reverse-engineering the WhatsApp-ImageIO zero-click iOS chain, with interactive labs.
 ldebug/extra_recipe
Ian Beer's exploit for CVE-2017-2370 (kernel memory r/w on iOS 10.2)
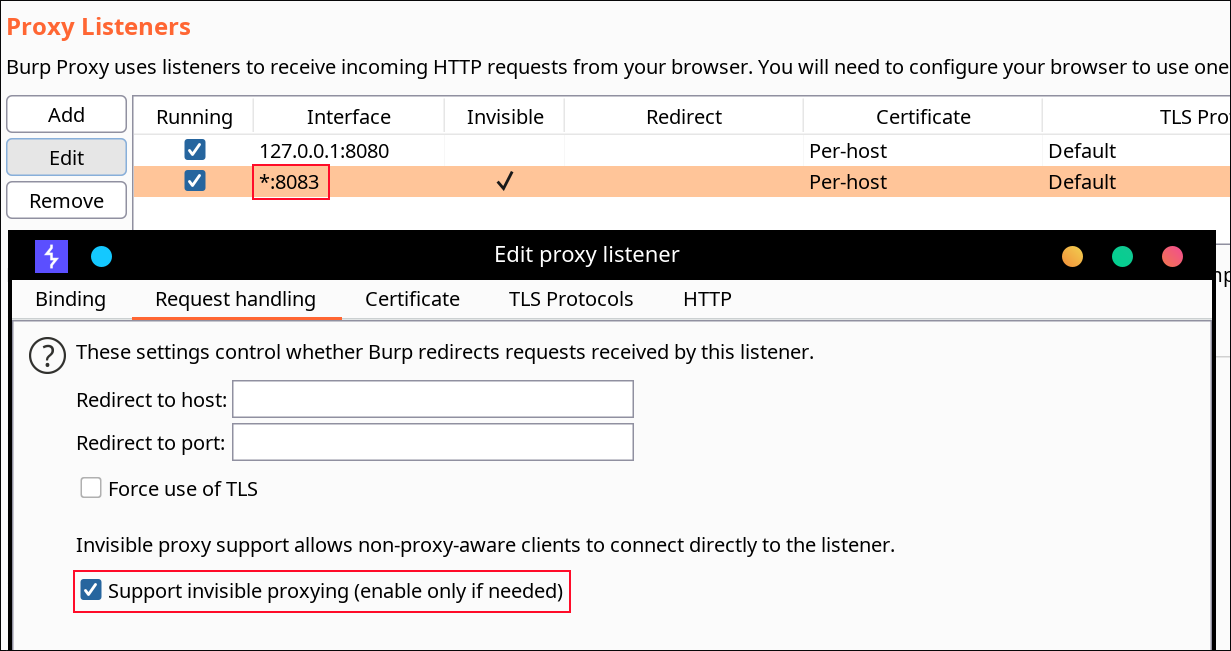 ptswarm/reflutter
Flutter Reverse Engineering Framework
 reverseclabs/needle
The iOS Security Testing Framework
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 peterpan0927/cve-2017-2370
on Mac 10.12.2