
CVE-2025-43300
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
binary-exploitationeducationembedded-systems-security+7
118
hunters-sec/cve-2025-43300This is POC for IOS 0click CVE-2025-43300
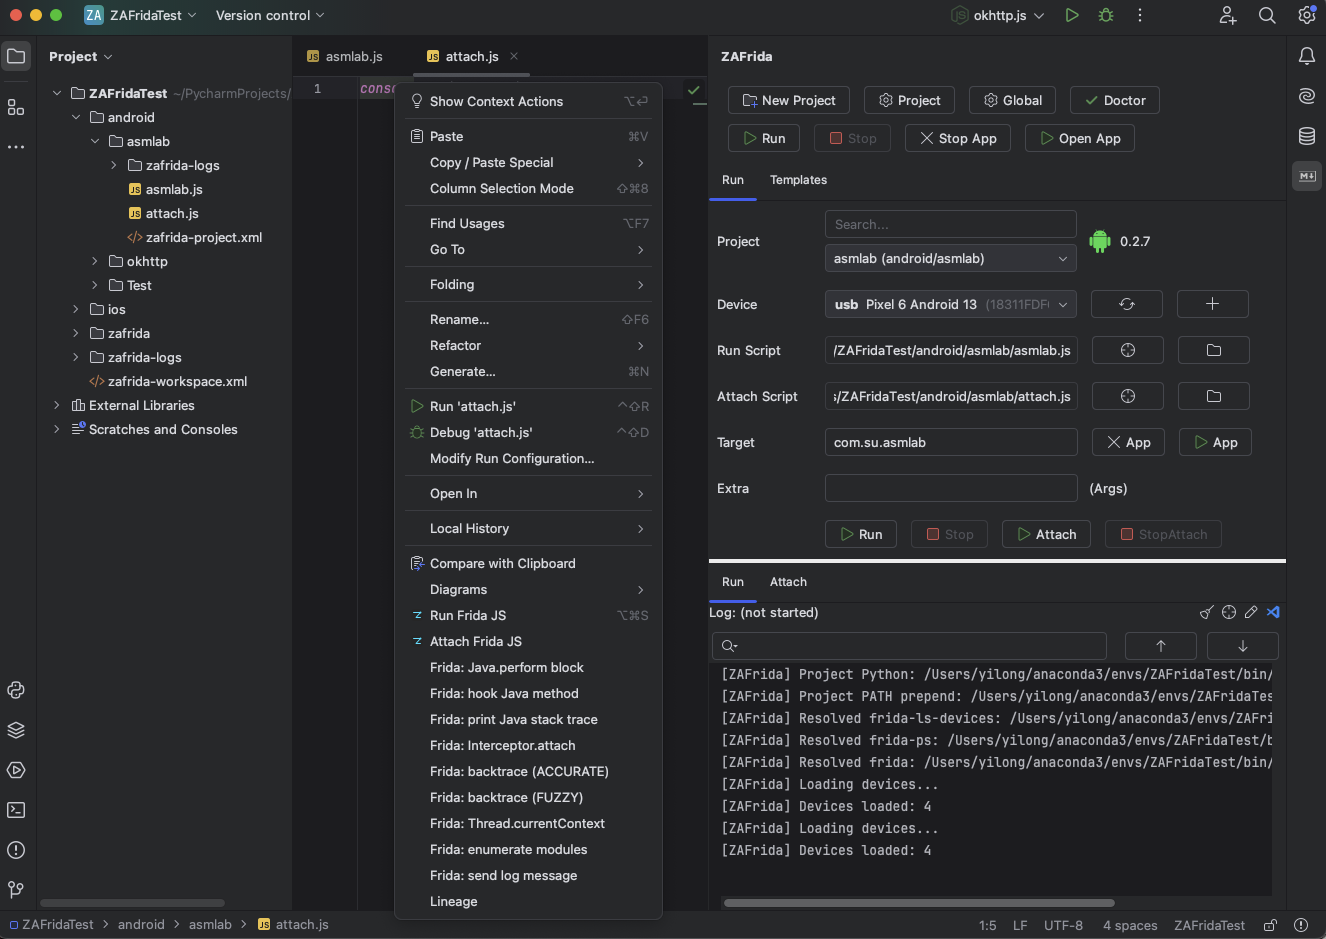 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 zteeed/cve-2018-4407-ios
POC: Heap buffer overflow in the networking code in the XNU operating system kernel
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 danielw98/zero-click-exploit-analysis
CVE-2025-55177 + CVE-2025-43300: reverse-engineering the WhatsApp-ImageIO zero-click iOS chain, with interactive labs.
 george0papasotiriou/cve-2026-6666-xpc-service-nskeyedunarchiver-deserialization-attack-macos-ios-simulation-
Simulated macOS/iOS XPC service vulnerable to NSKeyedUnarchiver deserialization, plus exploit demonstration and crafted plist payload for RCE via…
 ashishsecdev/mobsf_ai
AI powered security analysis extension for Mobile Security Framework MobSF