
mobsfscan
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
android-securitycode-analysisios-security+3
787
mobsf/mobsfscanmobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 dmayer/idb
idb is a tool to simplify some common tasks for iOS pentesting and research
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
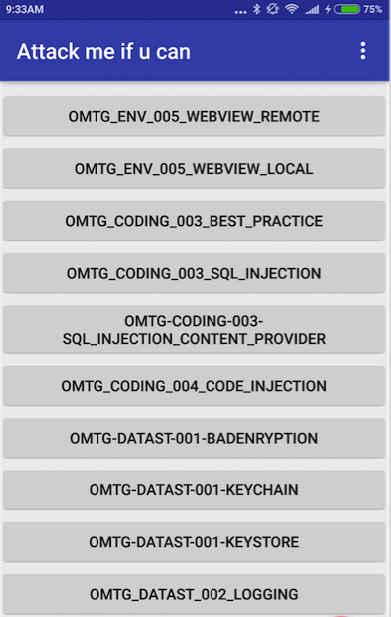 owasp/mastg-hacking-playground
Collection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…
 b1n4r1b01/n-days
Curated collection of iOS kernel and userland exploit PoCs and writeups for in-the-wild and researched CVEs, including binary-diffed vulnerability…
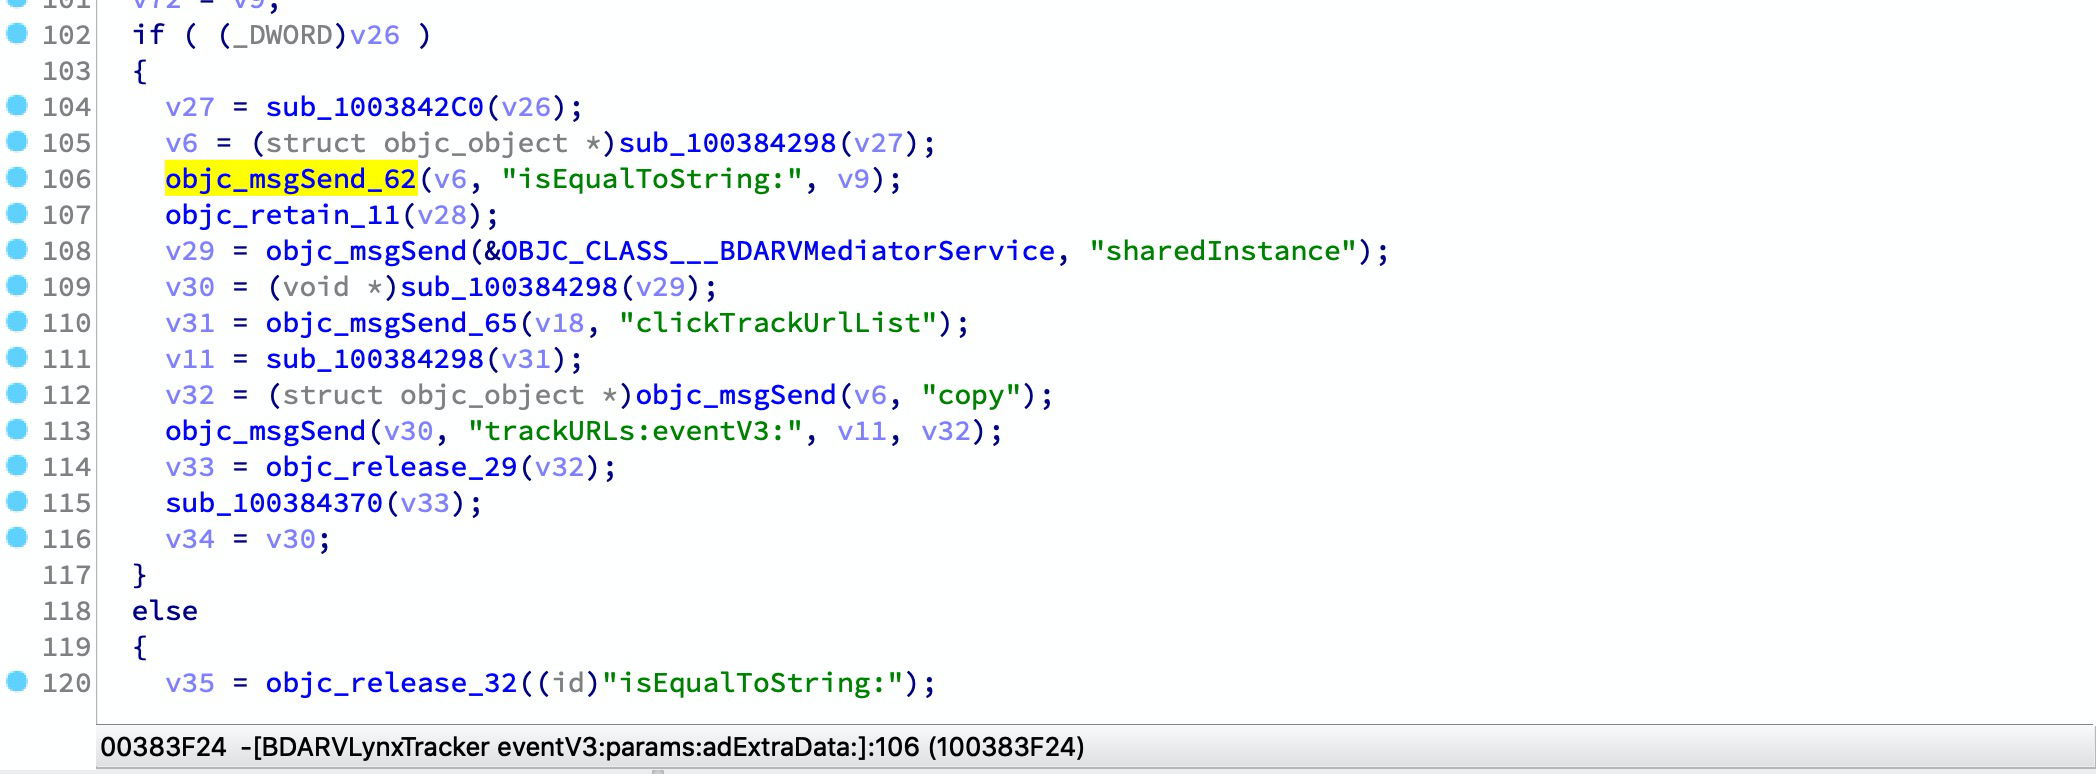 soulghost/iblessing
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
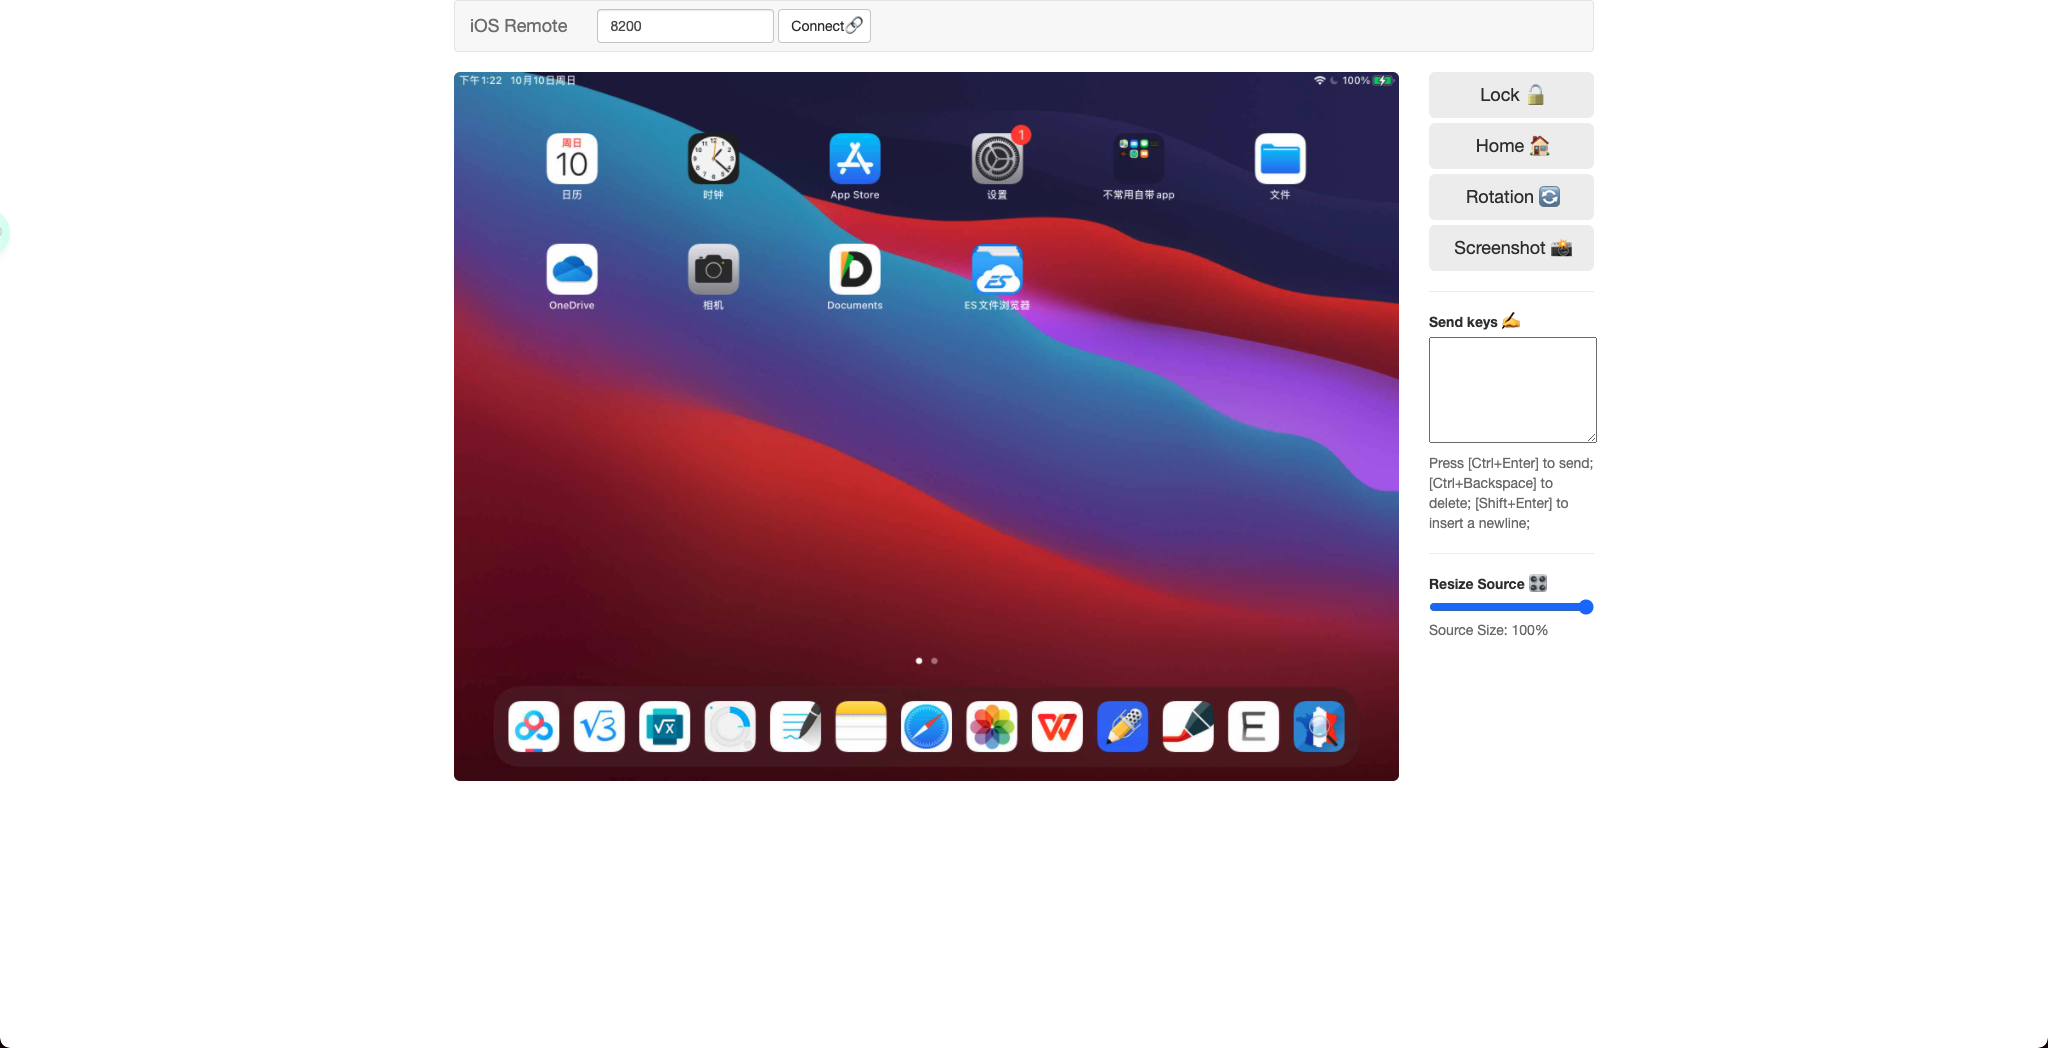 dimcyan/ios-remote
Display and control your iOS device
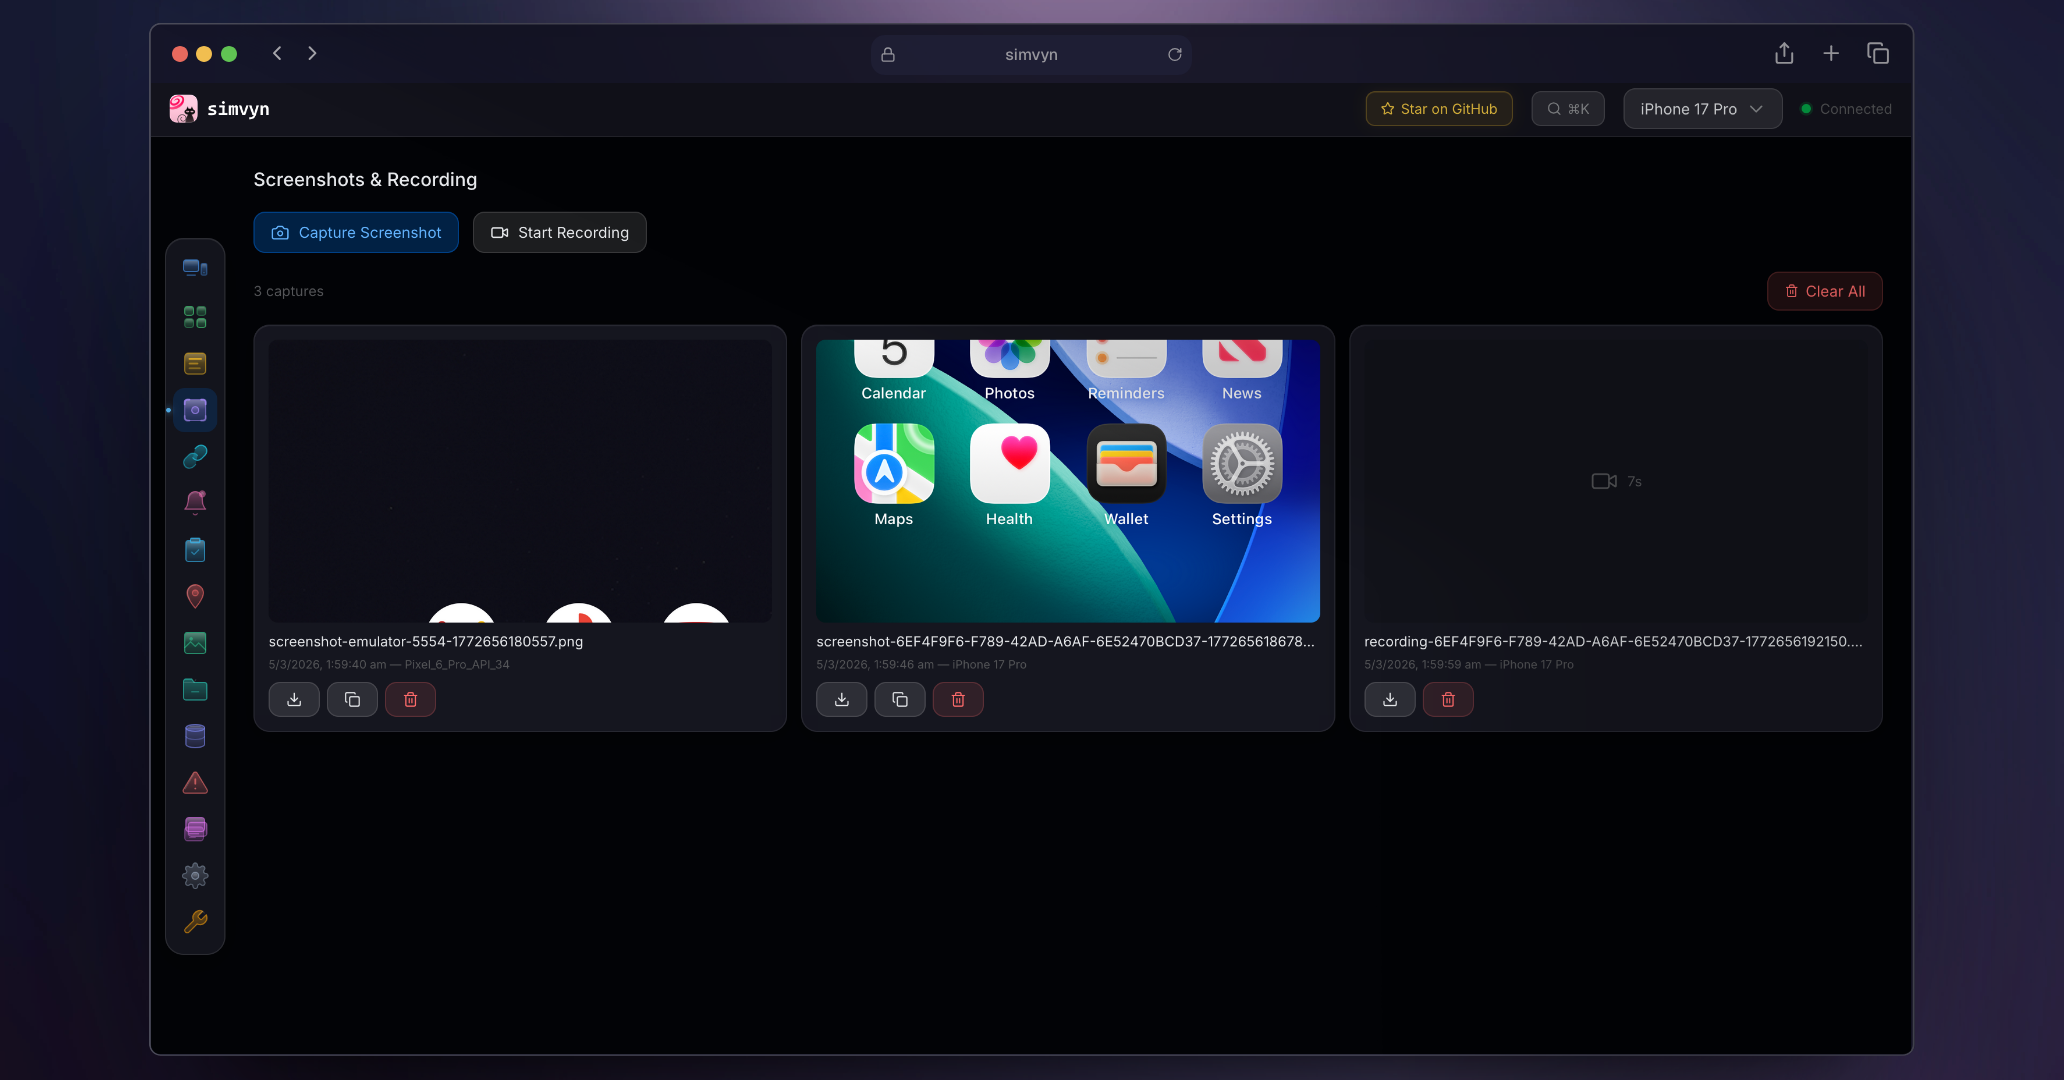 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 xorrior/macostools
macOS offensive security toolkit featuring dylib injection, HID keylogger, and in-memory JXA/Python payload runners for red team operations and…
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 bazad/blanket
CVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
 droid-ash/finalrun-agent
AI-driven CLI for testing Android and iOS apps using natural language. Generates, runs, and fixes end-to-end tests on emulators/simulators with…
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 0x36/weightbufs
ANE kernel r/w exploit for iOS 15 and macOS 12
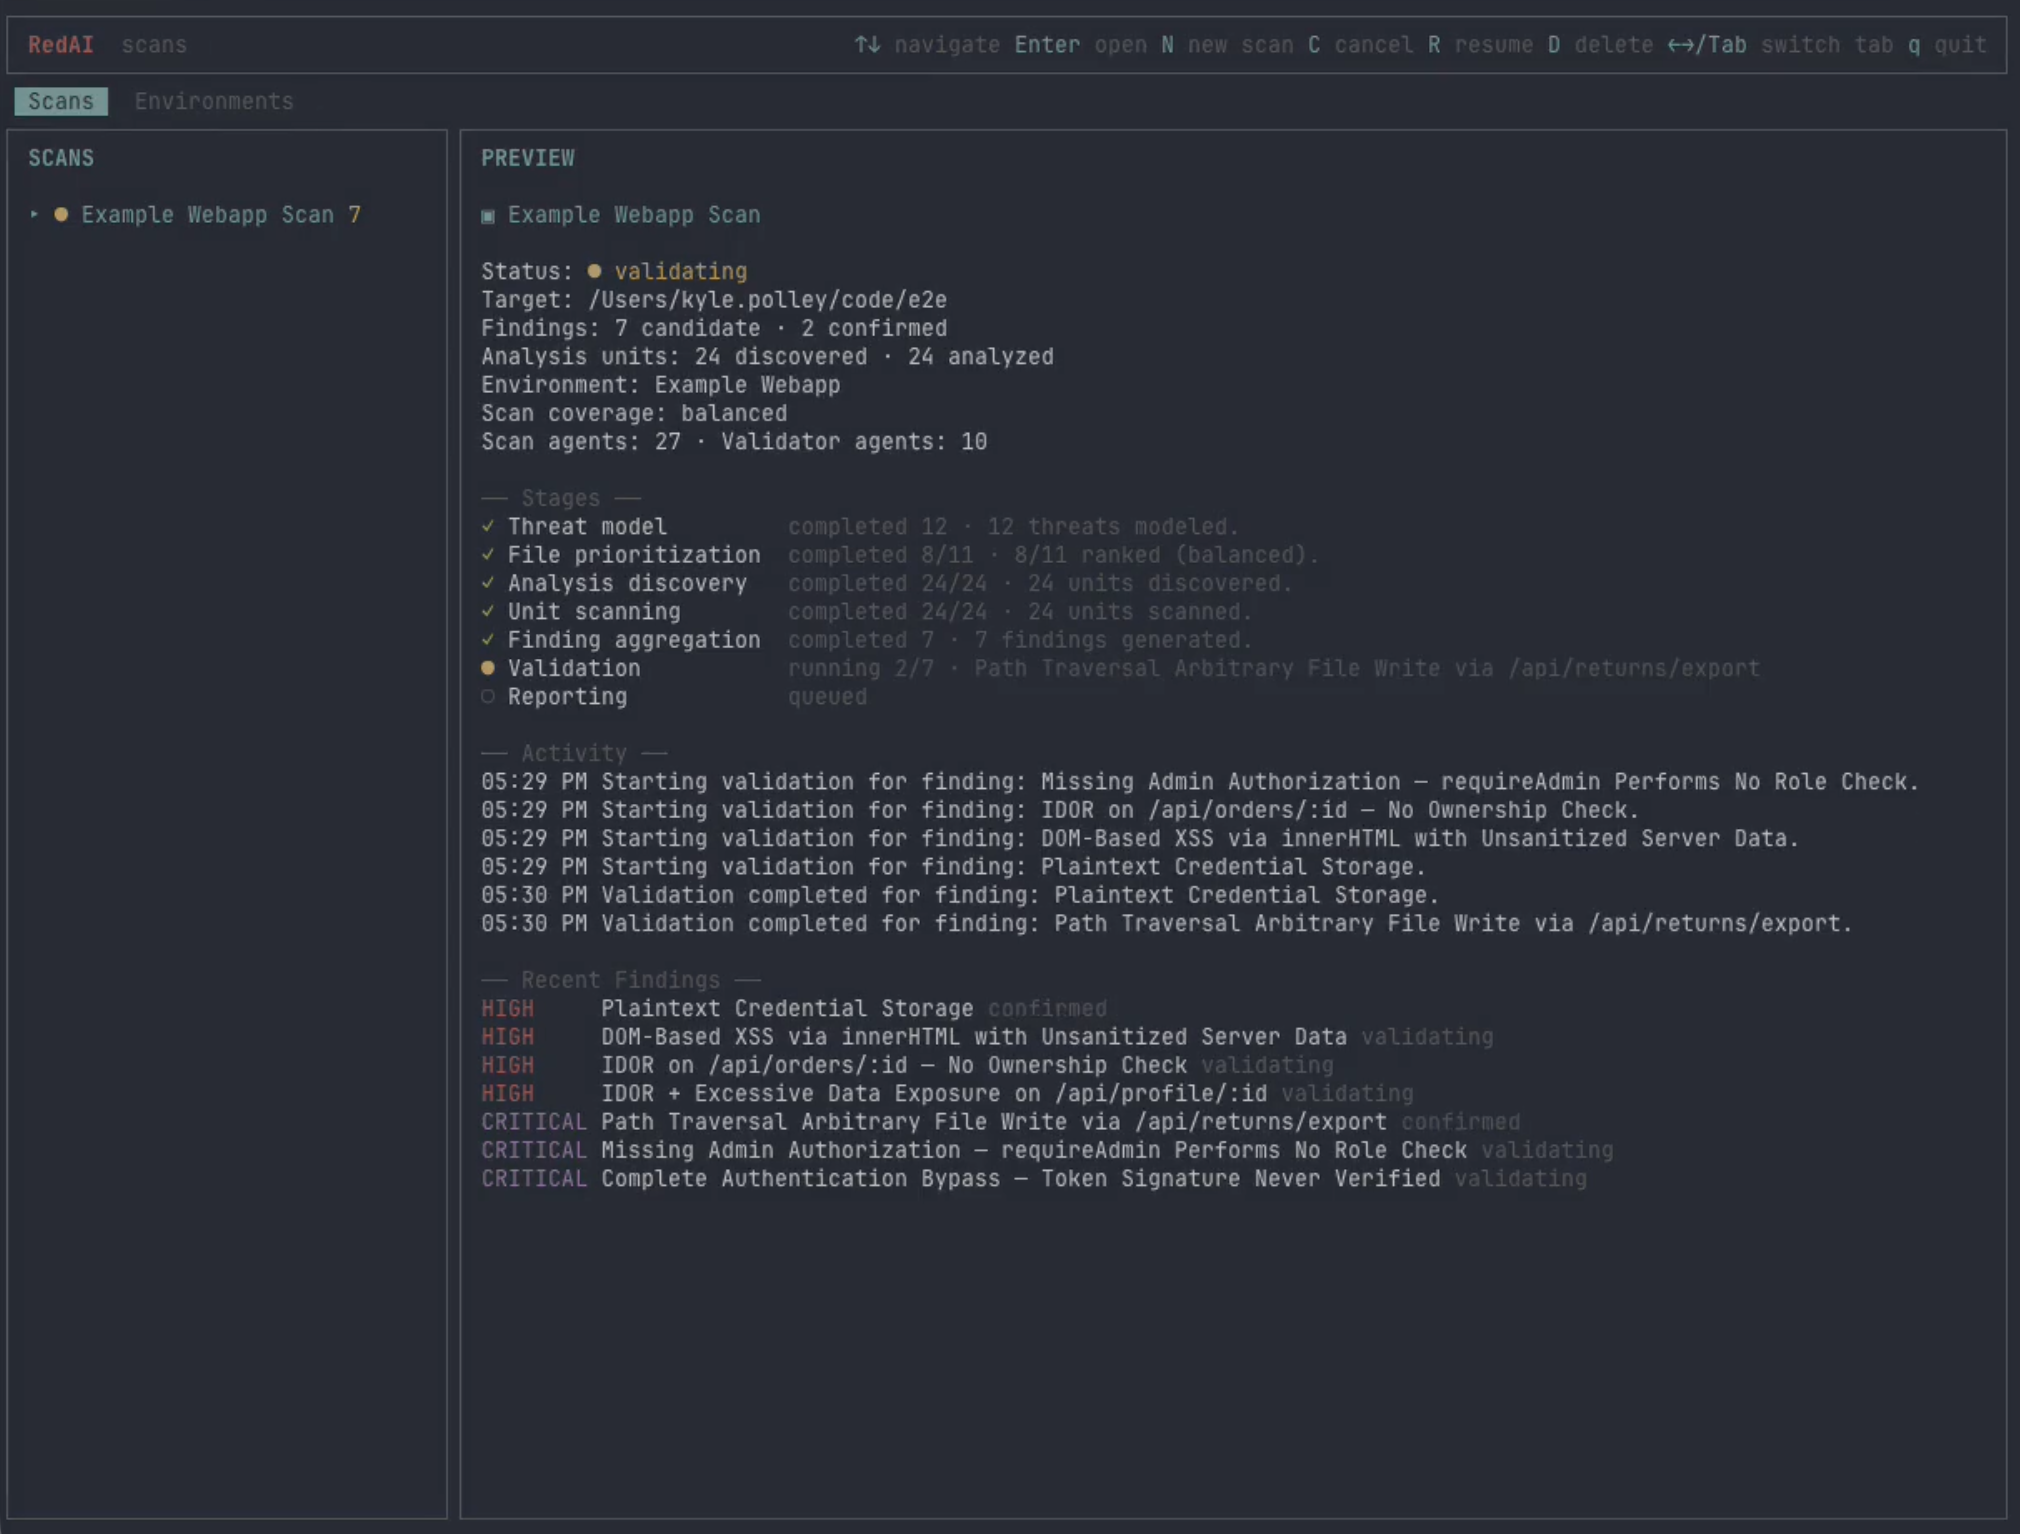 kpolley/redai
AI-driven vulnerability discovery and live validation
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…