iPhoneRestrictionsPasscodeBF

Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.

Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.

Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…

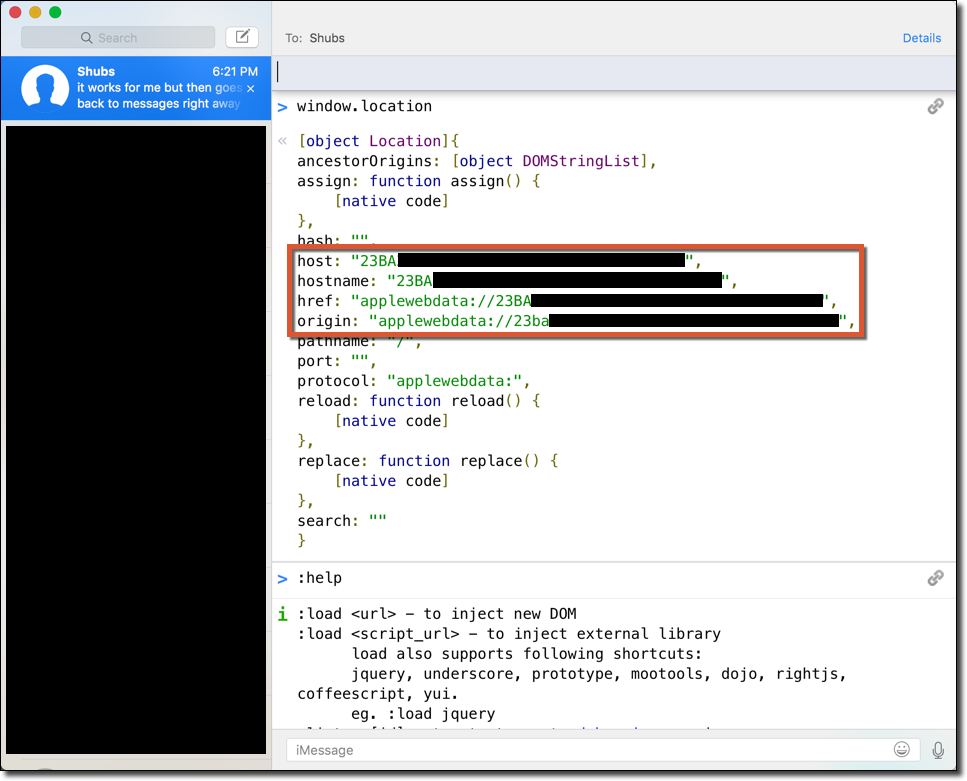
Extraction of iMessage Data via XSS

Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…

Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices

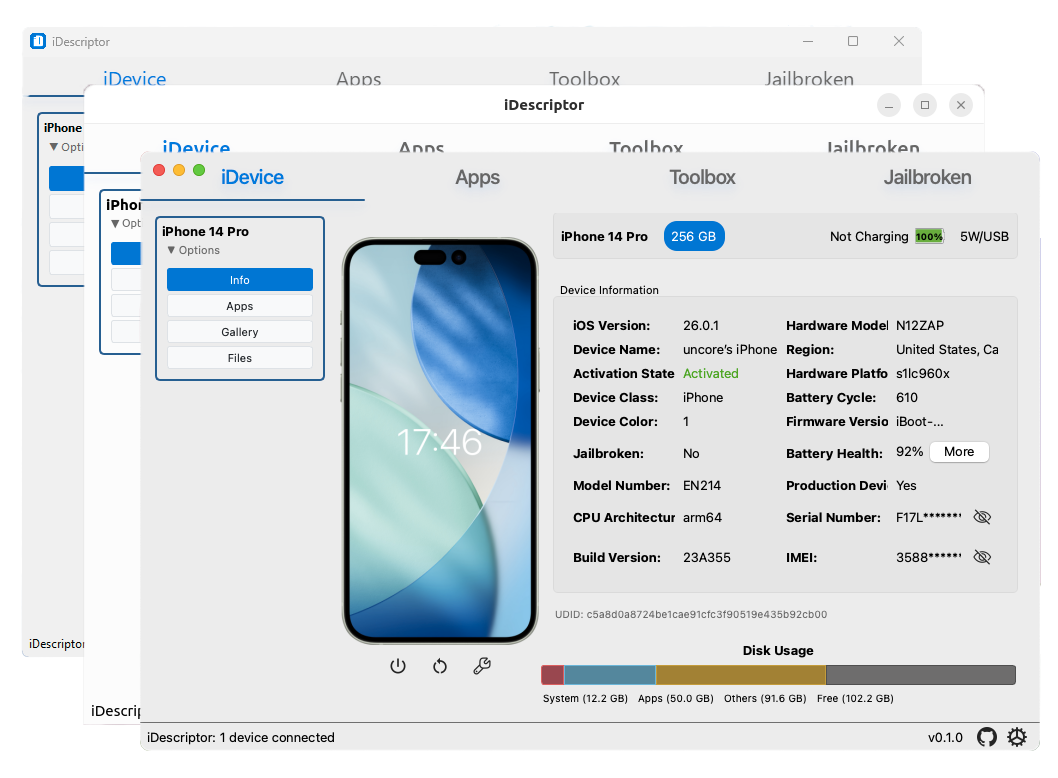
privacy-first, open-source and free idevice management tool written in Rust and Qt

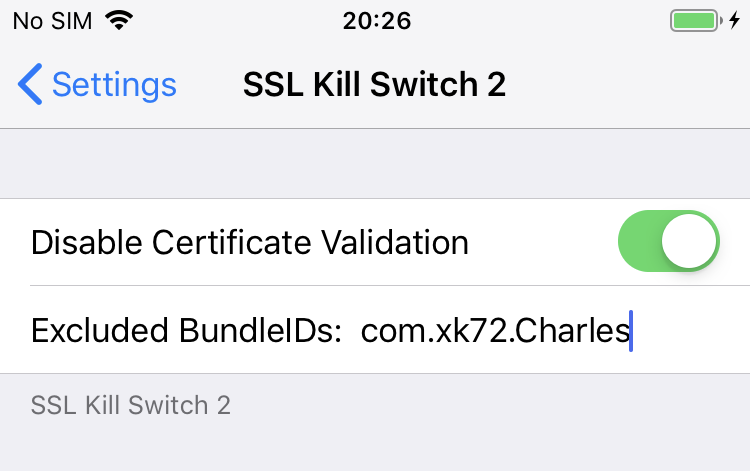
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.

idb is a tool to simplify some common tasks for iOS pentesting and research

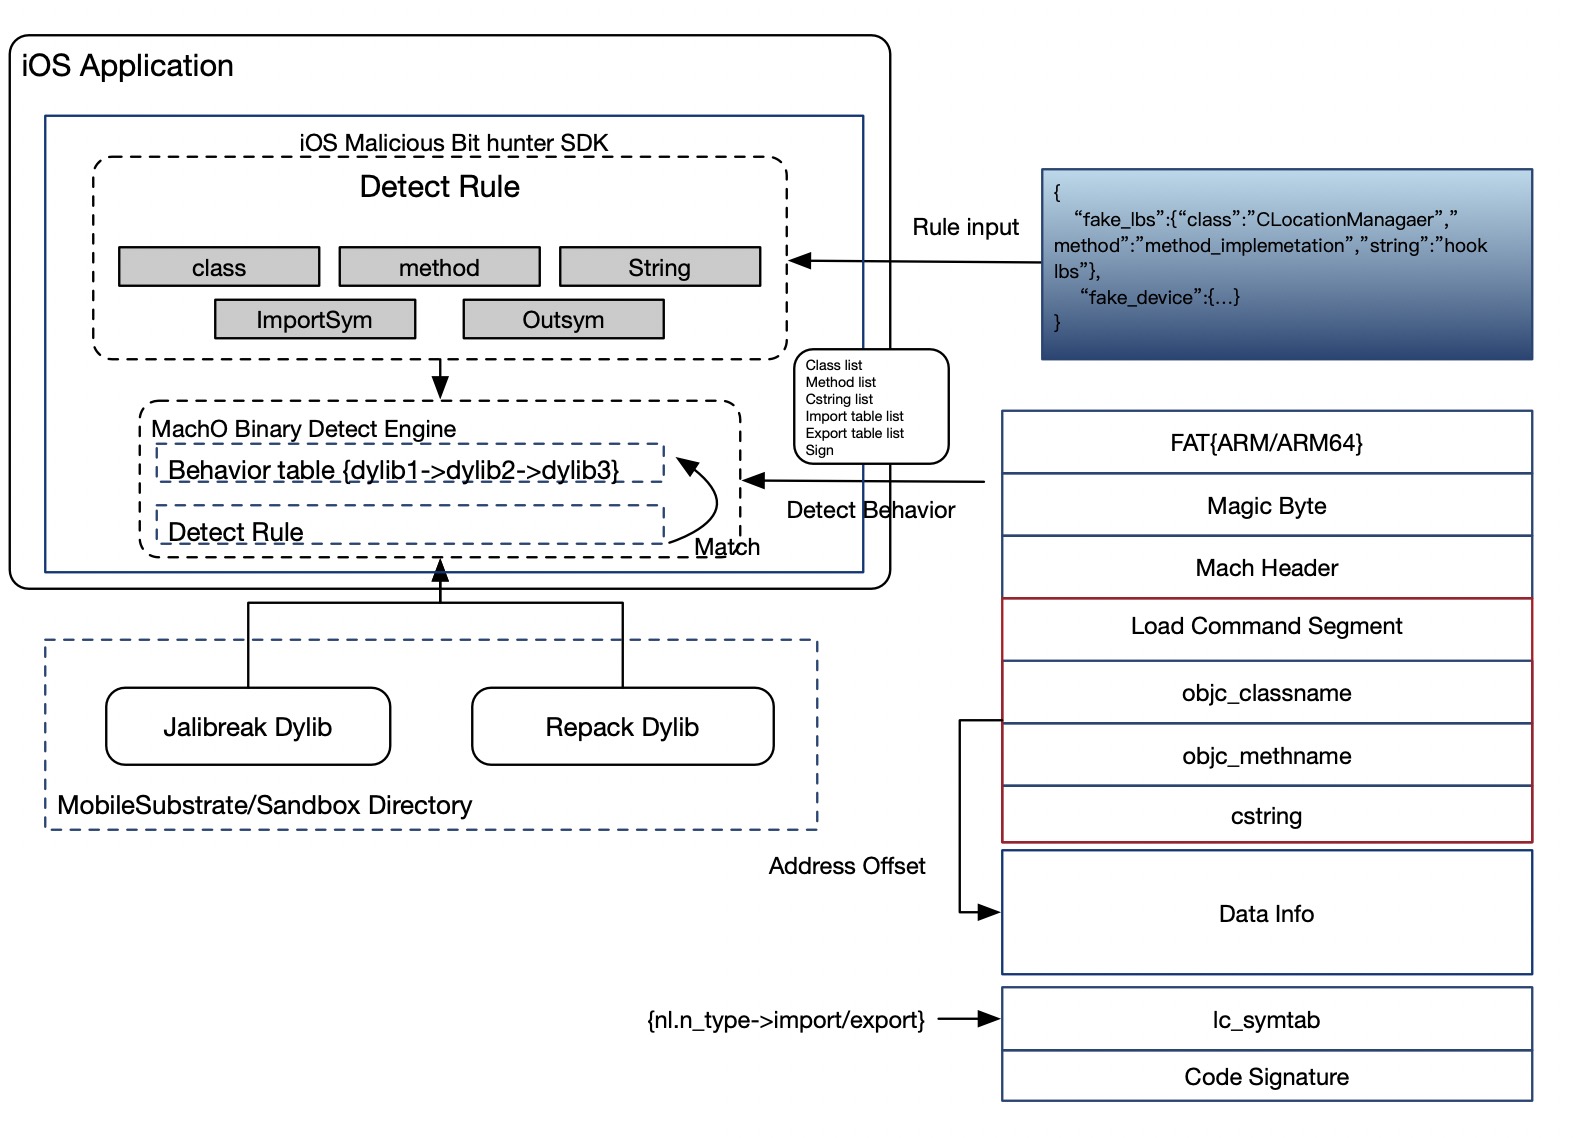
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…

Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero

Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…

CVE-2026-43813: CloudAttestation enforceEnvironment bypass

Ian Beer's exploit for CVE-2017-2370 (kernel memory r/w on iOS 10.2)

A Framework meant for the exploitation of iOS devices.