

masvs
 owasp/masvs
The OWASP MASVS (Mobile Application Security Verification Standard) is the industry standard for mobile app security.
android-securitycurated-resourceseducation+3
owasp/masvsThe OWASP MASVS (Mobile Application Security Verification Standard) is the industry standard for mobile app security.
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 tegal1337/cilocks
Crack Interface lockscreen, Metasploit and More Android/IOS Hacking
 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 mysk-research/loupe
A privacy-focused iOS app that raises awareness about what native apps can see
 illusionofchaos/ios-gamed-0day
iOS gamed exploit (fixed in 15.0.2)
 illusionofchaos/ios-nehelper-enum-apps-0day
iOS 15 0-day exploit (still works in 15.0.2)
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 bazad/x18-leak
CVE-2018-4185: iOS 11.2-11.2.6 kernel pointer disclosure introduced by Apple's Meltdown mitigation.
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 elevenpaths/dirtytooth-raspberrypi
Exploit the hack for IOS 11.1.2 and earlier to collect leaked information.
 owasp/mas-website
The OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
 biscuitehh/cve-2022-46718-leaky-location
CVE-2022-46718: an app may be able to read sensitive location information.
 feliam/cve-2014-4378
Exploit analysis for CVE-2014-4378: information disclosure in Apple CoreGraphics via crafted PDF, enabling memory layout leak and bypass of ASLR,…
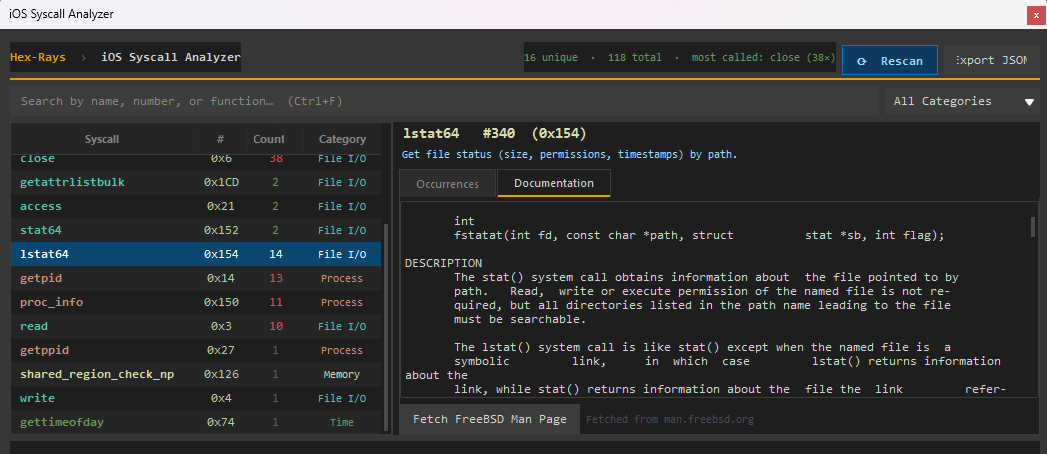 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 peterpan0927/cve-2017-2370
on Mac 10.12.2
 kolbicz/appenumguard
CVE-2025-31207 mitigation and sandboxed tester for rootless and rootHide jailbreaks on iOS 15–18.4.1