
DirtyTooth-RaspberryPi
 elevenpaths/dirtytooth-raspberrypi
Exploit the hack for IOS 11.1.2 and earlier to collect leaked information.
bluetooth-securityexploitationinformation-gathering+3
87
elevenpaths/dirtytooth-raspberrypiExploit the hack for IOS 11.1.2 and earlier to collect leaked information.
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
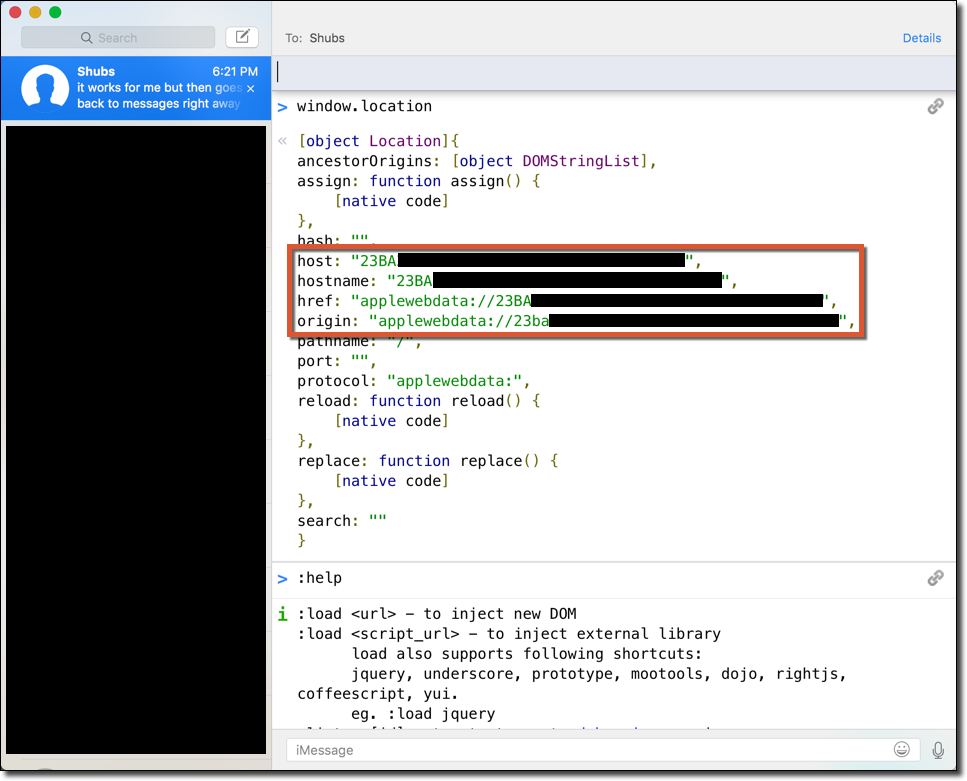 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 biscuitehh/cve-2022-46718-leaky-location
CVE-2022-46718: an app may be able to read sensitive location information.
 feliam/cve-2014-4378
Exploit analysis for CVE-2014-4378: information disclosure in Apple CoreGraphics via crafted PDF, enabling memory layout leak and bypass of ASLR,…
 xcodeon1/ipa-scope
Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…
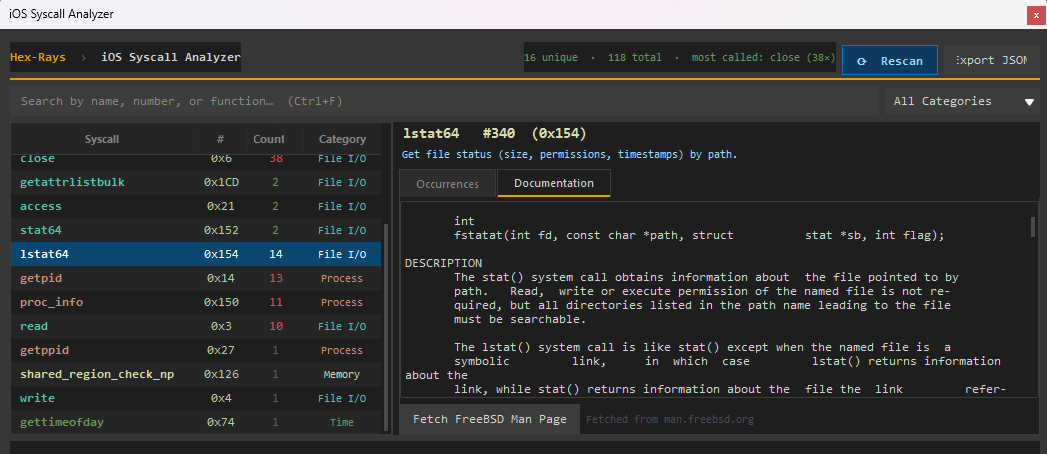 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 wyatu/cve-2018-4407
CVE-2018-4407 IOS/macOS kernel crash
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 peterpan0927/cve-2017-2370
on Mac 10.12.2
 xcodeon1/ssh-killv2
SSH brute-force tool targeting jailbroken iPhones with default 'alpine' password, featuring network scanning, wordlist-based cracking, and file…
 speedyfriend433/cve-2026-28867-poc
Kernel info leak Proof of Concept patched in iOS 26.4 / macOS 26.4
 zteeed/cve-2018-4407-ios
POC: Heap buffer overflow in the networking code in the XNU operating system kernel
 biscuitehh/cve-2023-40429-ez-device-name
CVE-2023-40429: An app may be able to access sensitive user data.
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 tihmstar/freepw_tc7200eploit
Technicolor TC7200 - Credentials Disclosure CVE : CVE-2014-1677
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)