
cve-2025-5915
 r3n3r0/cve-2025-5915
Proof-of-concept exploit for a heap over-read in libarchive RAR v4 filter (CVE-2025-5915) with ASan reproduction, encoder, and on-device iOS 18.5…
binary-exploitationexploitationios-security+3
r3n3r0/cve-2025-5915Proof-of-concept exploit for a heap over-read in libarchive RAR v4 filter (CVE-2025-5915) with ASan reproduction, encoder, and on-device iOS 18.5…
 ktiosz/poc_ios12
PoC Exploit iOS 12 to iOS 12.1 (CVE-2018-4431)
 enfilade-labs/cve-2026-20687-applejpegdriver-uaf
CVE-2026-20687: AppleJPEGDriver startDecoder Timeout UAF — iOS/macOS kernel vulnerability leading to deferred panic (A19 Pro, iOS 26.3 RC)
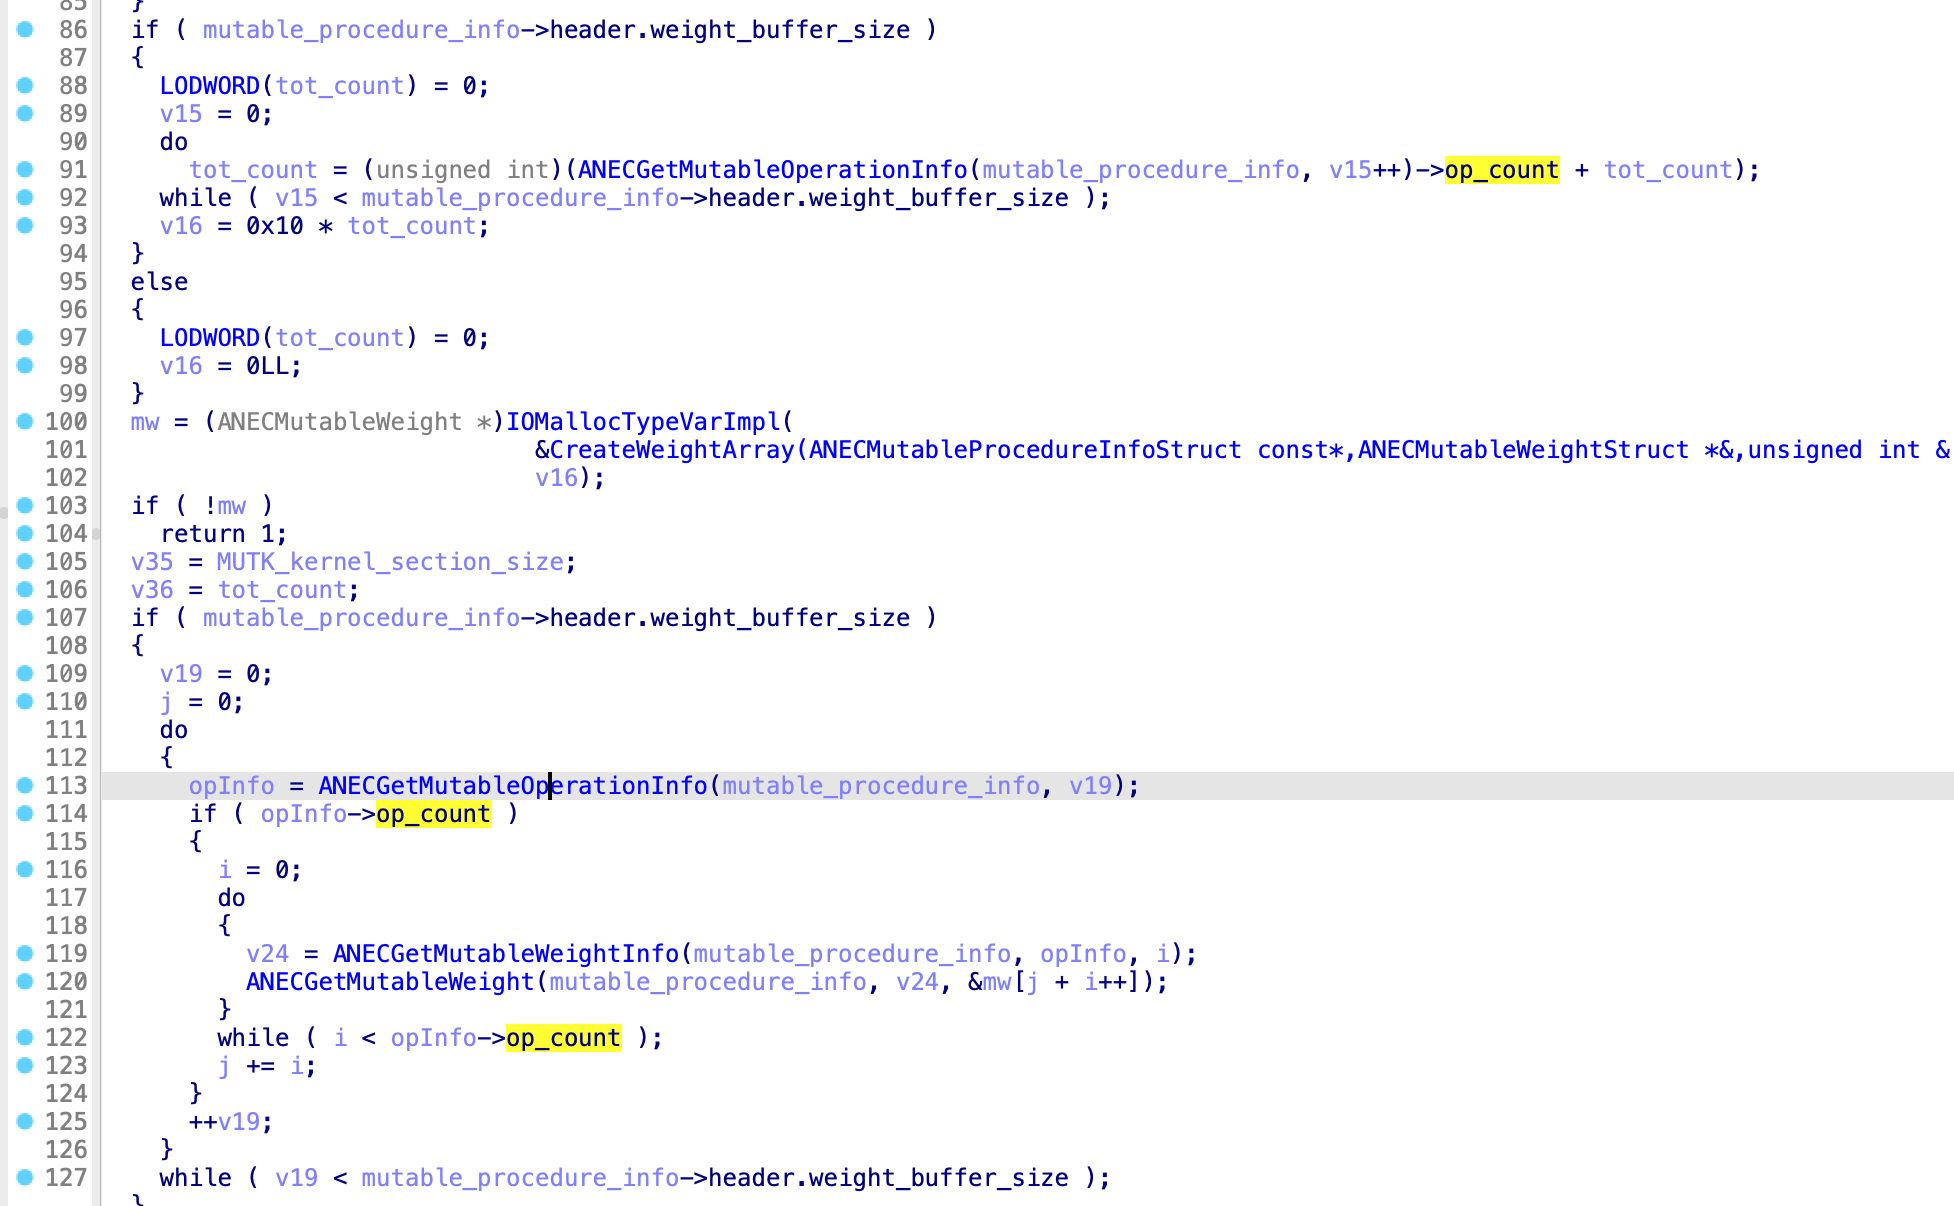 ox1111/cve-2022-32932
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…
 simoesctt/ctt-apple-silicon-refraction
webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…
 nomnomheapnom/cve-2024-27815
Proof-of-concept trigger for CVE-2024-27815, an XNU kernel heap buffer overflow in sbconcat_mbufs() reachable via AF_UNIX datagram sockets, causing…
 opa334/darksword-kexploit
iOS <=26.0.1 DarkSword Kernel Exploit reimplemented in Objective-C
 b1n4r1b01/desc_race
iOS 15.1 kernel exploit POC for CVE-2021-30955
 bazad/x18-leak
CVE-2018-4185: iOS 11.2-11.2.6 kernel pointer disclosure introduced by Apple's Meltdown mitigation.
 0xjohnnydev/cve-2026-20637-applesepkeystore-uaf
CVE-2026-20637: AppleSEPKeyStore Use-After-Free — iOS/macOS kernel vulnerability (patched in 26.4)
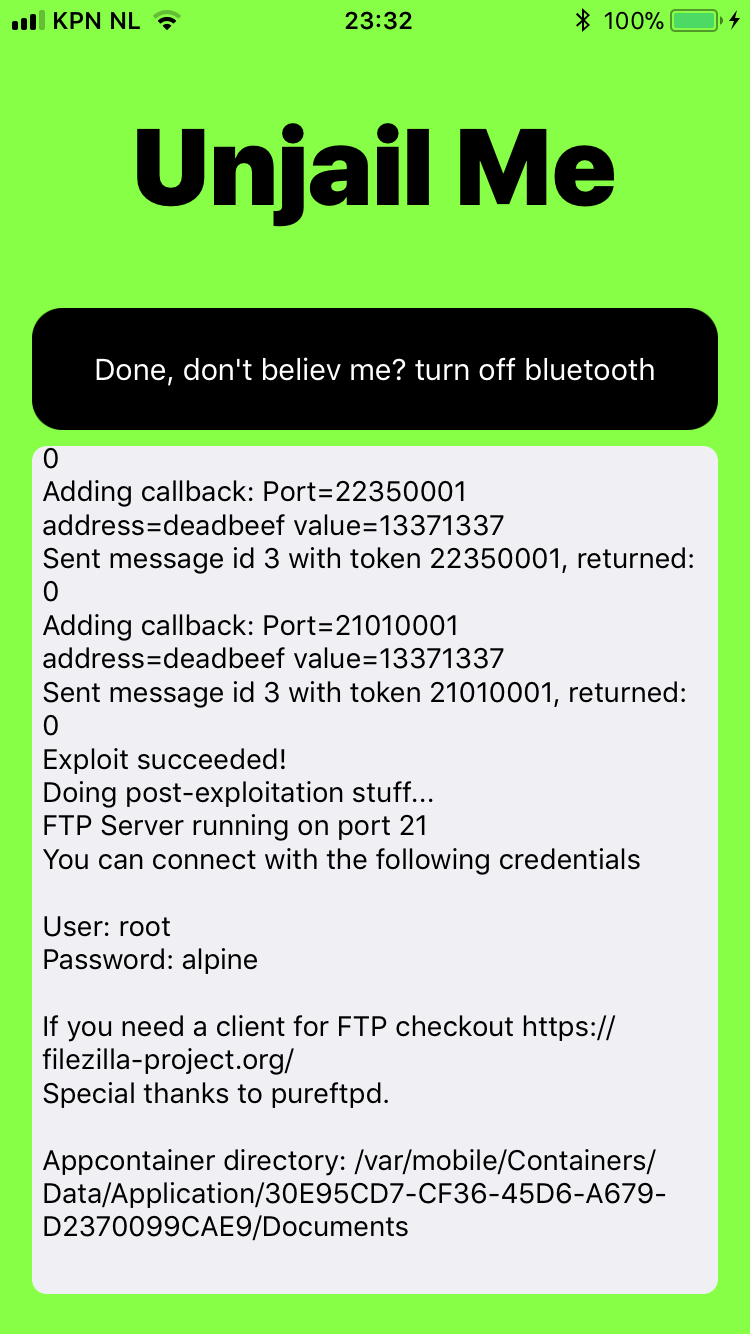 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 0xjohnnydev/cve-2026-28992-iohidfamily-fastpathuserclient-race-conditions
UAF and AOP coprocessor panic in IOHIDEventServiceFastPathUserClient. No entitlements, reachable from app sandbox.
 bazad/gsscred-move-uaf
CVE-2018-4343: Proof-of-concept for a use-after-free in the GSSCred daemon on macOS and iOS.
 viai957/webkit-vulnerability
CVE-2016-4657 web-kit vulnerability for ios 9.3, nintendo switch browser vulnerability
 pwnhacker0x18/ios-kernel-crash
Exploit for CVE-2018-4407-Memory Corruption
 spotlightishere/inputcontrol
proof-of-concept for CVE-2023-28197
 nickorlow/cve-2021-30955-poc
Jake Jame's proof of concept wrapped into an iOS app for CVE-2021-30955