


 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
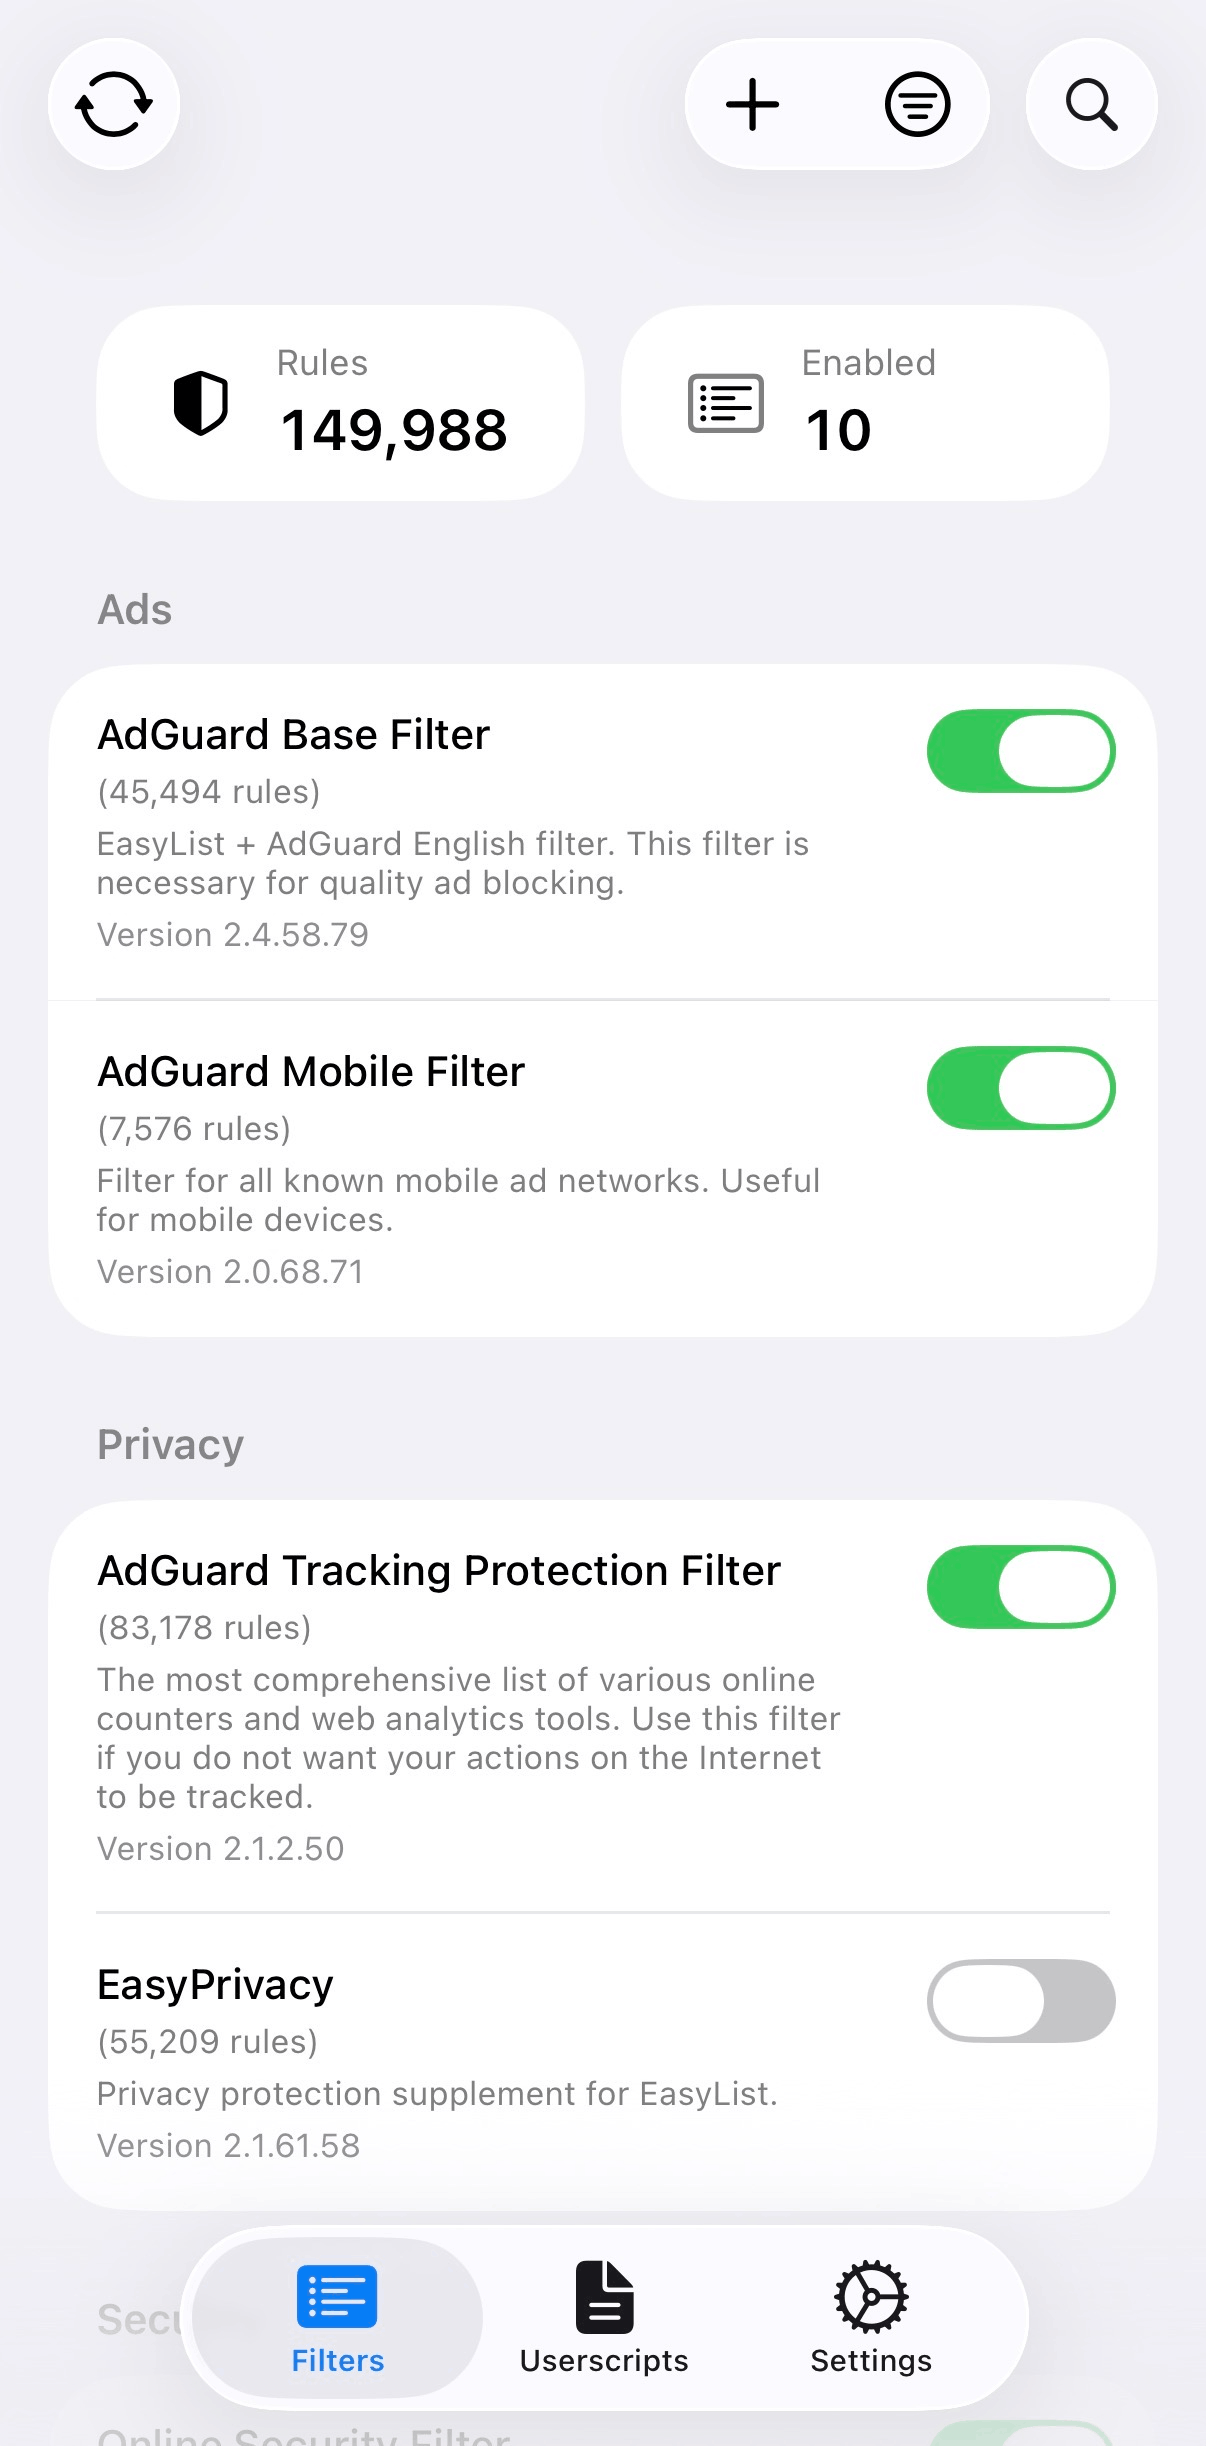 0xcub3/wblock
Free, open-source Safari ad blocker for macOS, iOS, iPadOS and visionOS. Up to 750,000 rules, custom filter lists, userscripts and userstyles. No…
 hahwul/mobilehackersweapons
Mobile Hacker's Weapons / A collection of cool tools used by Mobile hackers. Happy hacking , Happy bug-hunting
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
 xorrior/macostools
macOS offensive security toolkit featuring dylib injection, HID keylogger, and in-memory JXA/Python payload runners for red team operations and…
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
 azw413/glass
Glass - a fast and free IDA Pro alternative
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300