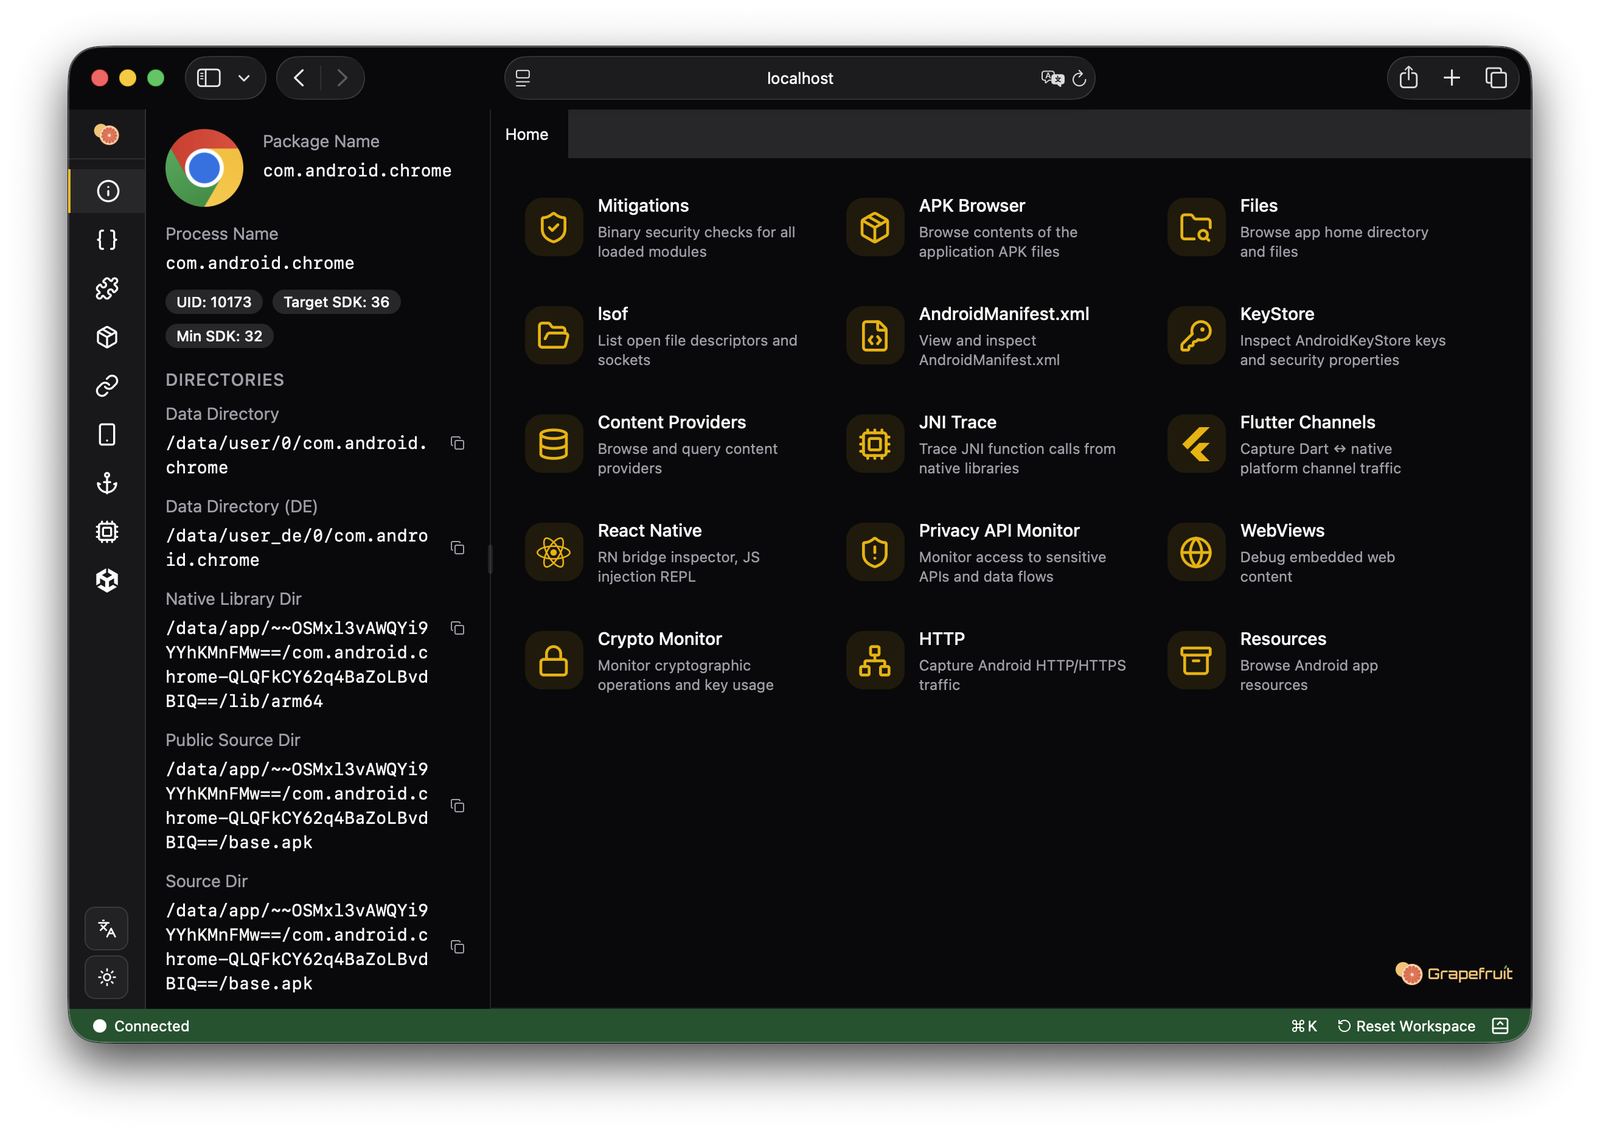
grapefruit
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
android-securitybinary-analysisdynamic-code-analysis+5
1.4k
chichou/grapefruitOpen-source mobile security testing suite for iOS and Android. Previously Passionfruit
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 ch0pin/medusa
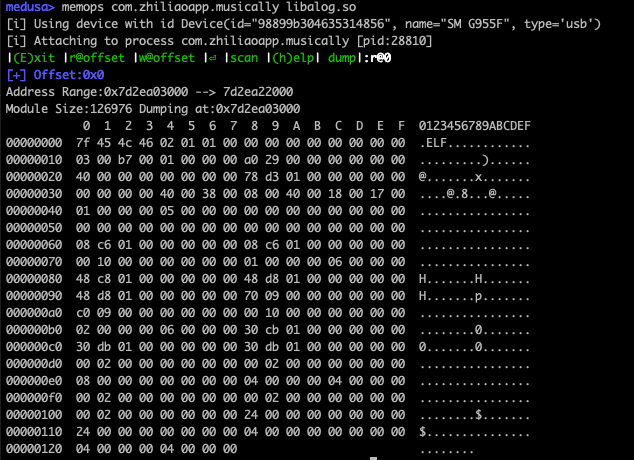
Mobile Edge-Dynamic Unified Security Analysis
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 msuiche/hotcell
Runtime exploit monitor for Apple document/image pipelines (iOS/macOS) — EXPMON concept: Frida agent + behavioral rules. First target: the…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 billy-ellis/exr-imageio-poc
PoC for CVE-2026-28990, an ImageIO bug patched in iOS/macOS 26.5
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
 googleprojectzero/sockfuzzer
Coverage-guided kernel fuzzing framework that runs XNU as a userspace library and discovers vulnerabilities across BSD, Mach, virtual memory, and…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…