

frida-ios-dump
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
encryption-decryption-toolsios-securitymobile-app-pentesting+4
4.0k
alonemonkey/frida-ios-dumpExtracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
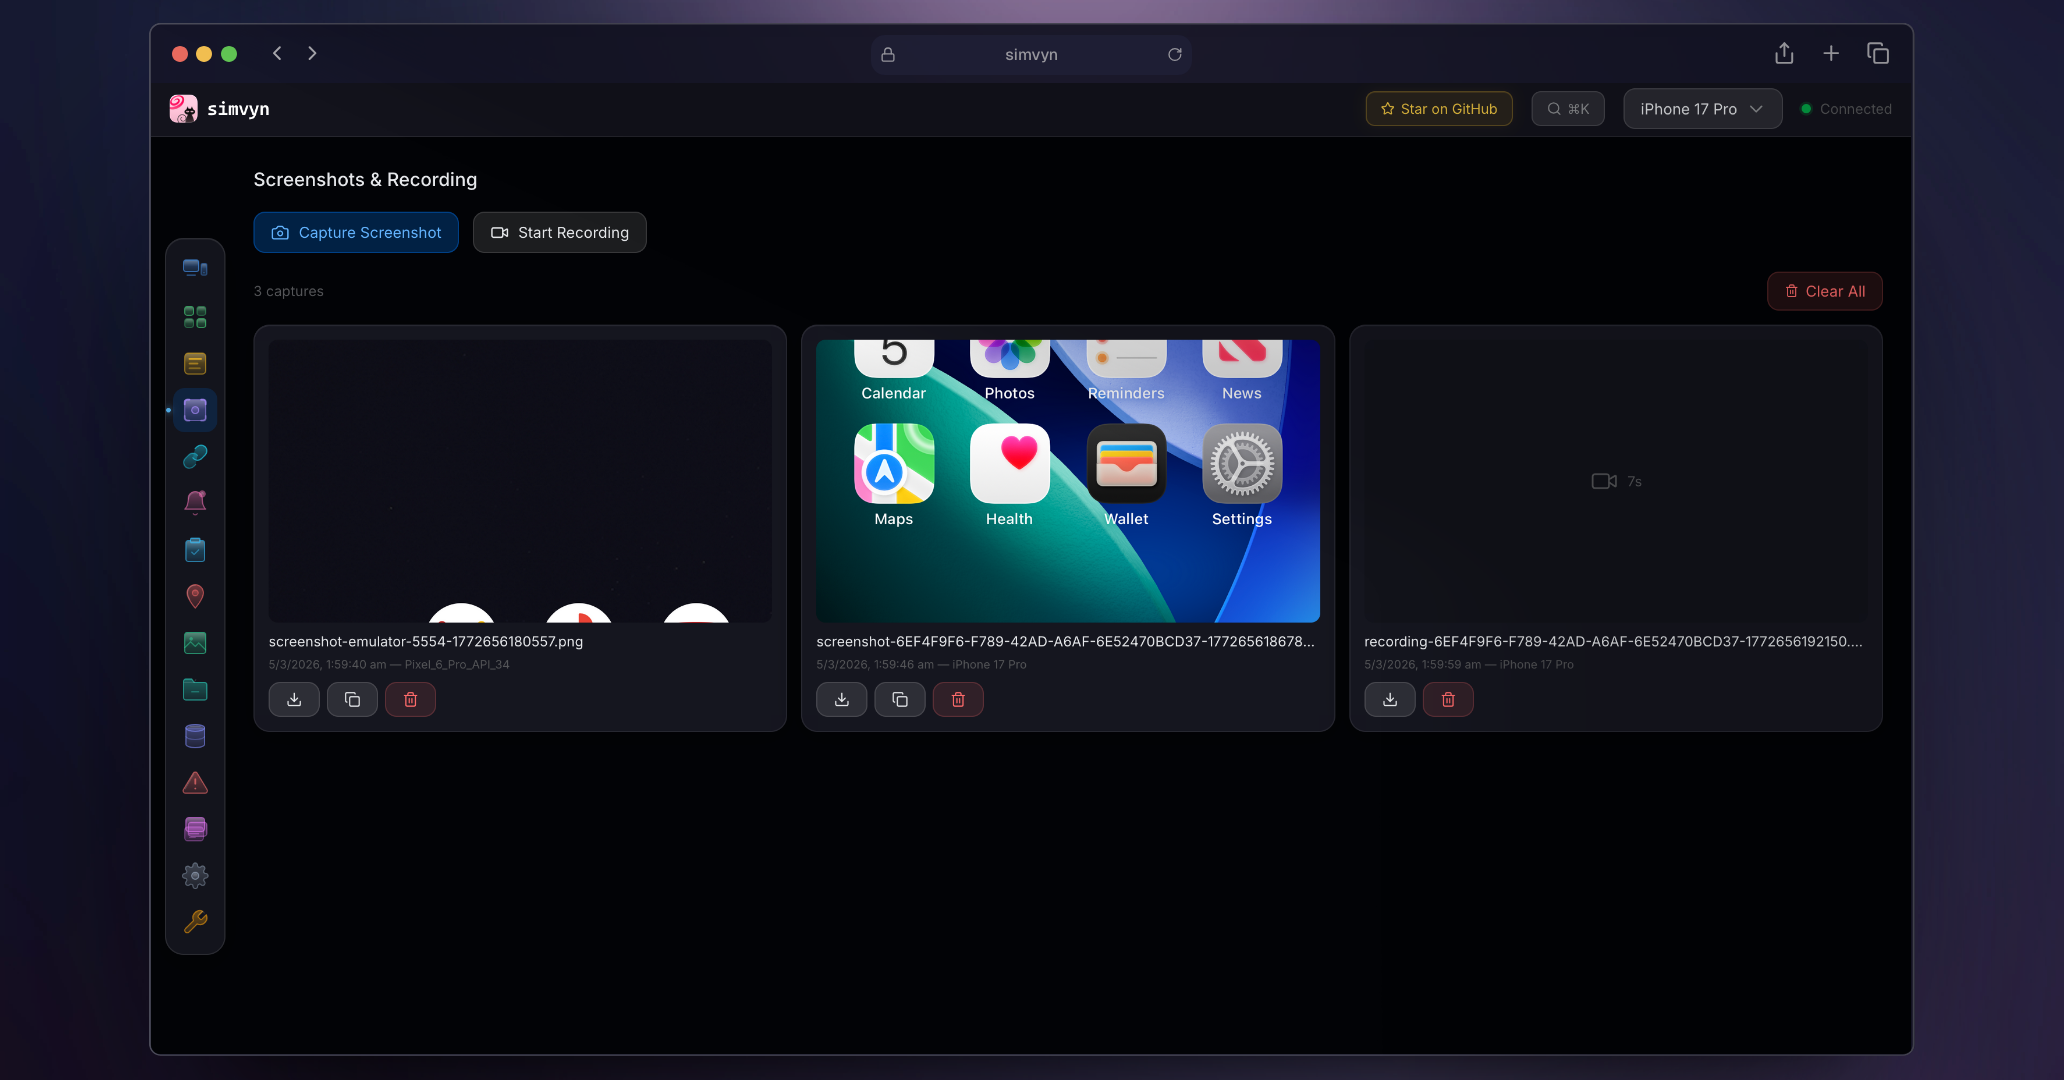 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 bytev0rtex/cve-2026-65330
Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…
 0xjohnnydev/cve-2026-28992-iohidfamily-fastpathuserclient-race-conditions
UAF and AOP coprocessor panic in IOHIDEventServiceFastPathUserClient. No entitlements, reachable from app sandbox.
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 r3n3r0/cve-2025-5915
Proof-of-concept exploit for a heap over-read in libarchive RAR v4 filter (CVE-2025-5915) with ASan reproduction, encoder, and on-device iOS 18.5…
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 somisomair/cve-2026-43655-applem2scalercscdriver-uaf
Public disclosure for CVE-2026-43655 AppleM2ScalerCSCDriver use-after-free
 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
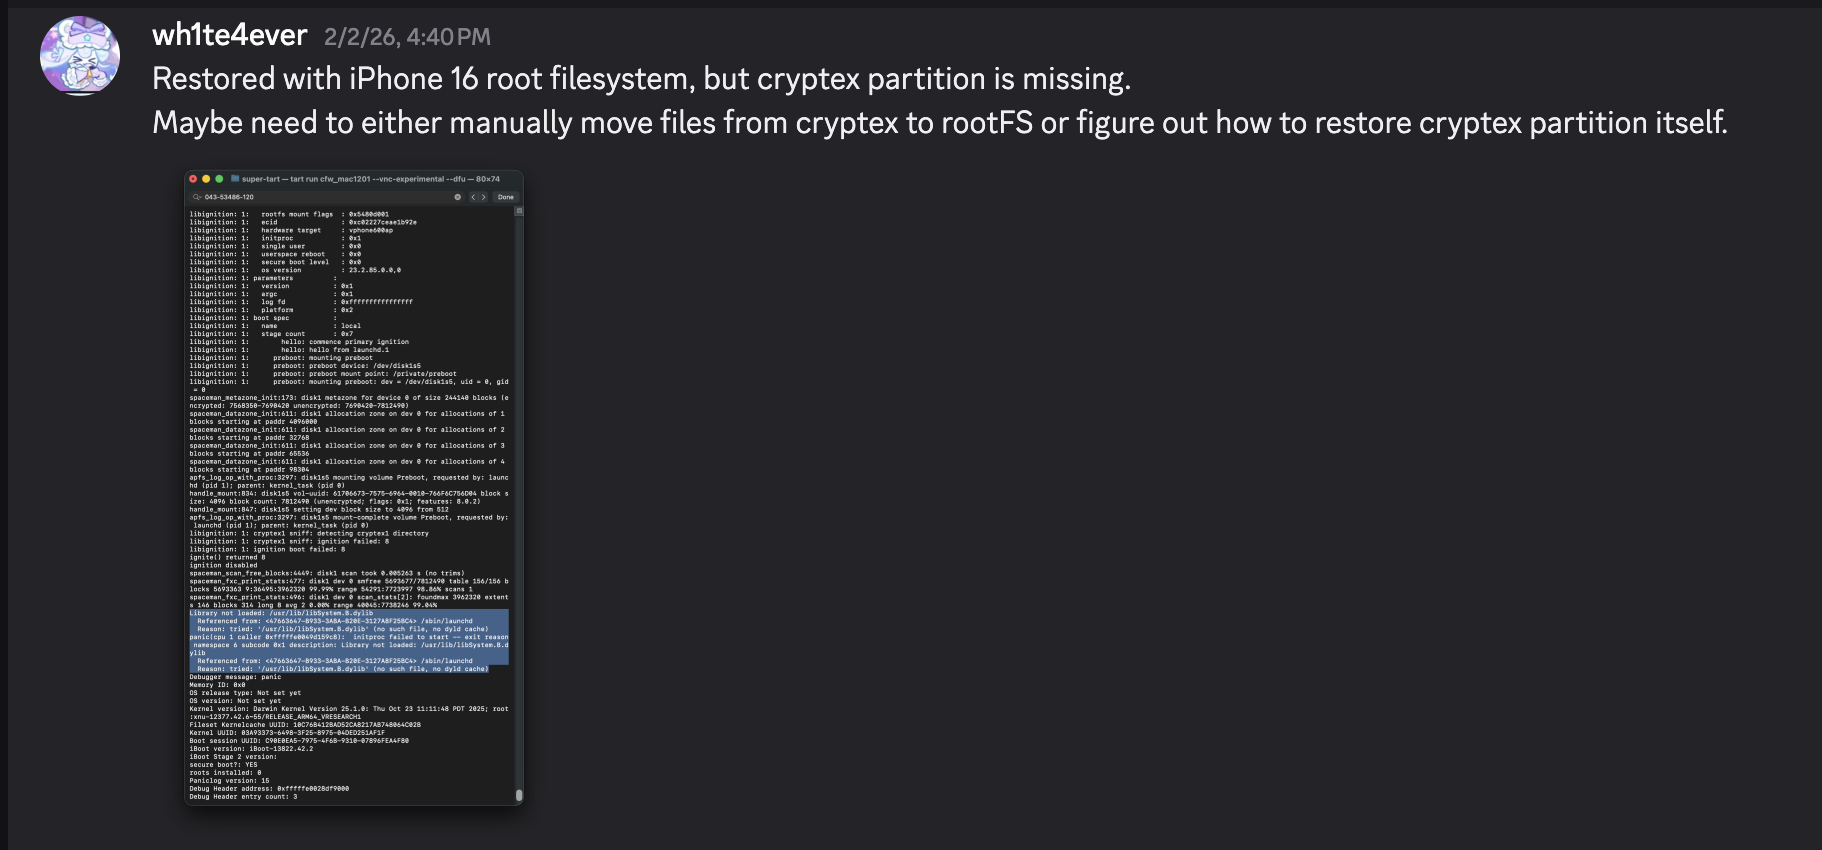 wh1te4ever/super-tart-vphone-writeup
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…
 simoesctt/ctt-apple-silicon-refraction
webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…
 b1n4r1b01/n-days
Curated collection of iOS kernel and userland exploit PoCs and writeups for in-the-wild and researched CVEs, including binary-diffed vulnerability…
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 darknavysecurity/poc
Curated proof-of-concept exploits for real-world CVEs affecting iOS, macOS, Chrome Renderer, and Steam clients, with version-specific targets and…