
palera1n
 palera1n/palera1n
Jailbreak for A8 through A11, T2 devices, on iOS/iPadOS/tvOS 15.0, bridgeOS 5.0 and higher.
embedded-systems-securityexploitationhardware-security+2
6.5k
palera1n/palera1nJailbreak for A8 through A11, T2 devices, on iOS/iPadOS/tvOS 15.0, bridgeOS 5.0 and higher.
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
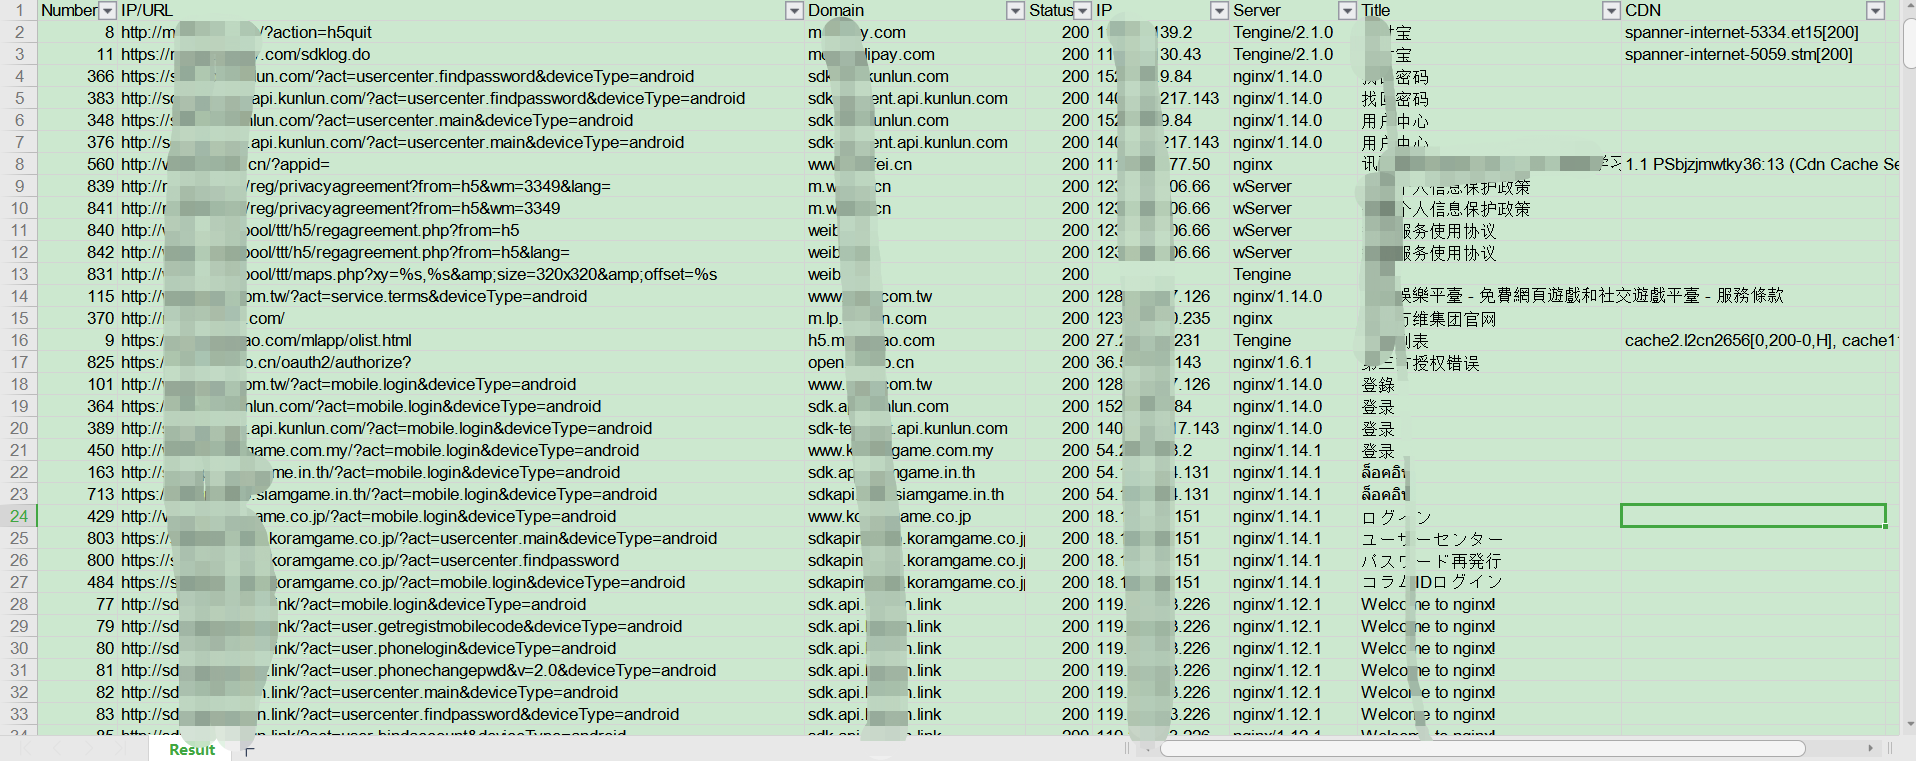 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 amorcool/ios26.6-cve-2026-65343
CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)
 amorcool/ios26.6-cve-2026-64788
CVE-2026-64788 PoC — IOGPUFamily Use-After-Free (iOS 26.6 / 23G71)
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 genericcoding/pois0nsword
A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
 chefkissinc/inferno
Apple Silicon device emulator.
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 dgh05t/zer0con_2026_attacking_apple_dcp
Research repository detailing exploitation techniques against Apple's Display Co-Processor (DCP), including firmware analysis and hardware-level…
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 hahwul/mobilehackersweapons
Mobile Hacker's Weapons / A collection of cool tools used by Mobile hackers. Happy hacking , Happy bug-hunting
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 jclarkcom/ble_proxy
BLE-based HTTP proxy system routing browser traffic through an iOS device. Supports HTTP/HTTPS, data compression, and mock mode for testing without…
 geosn0w/cve-2025-24203-ios-exploit-with-error-logging
Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero
 straight-tamago/nocamerasound
CVE-2022-46689