
ioscpy
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
information-gatheringios-securitymobile-security+3
lautarovculic/ioscpyNow you can mirror and control your jailbroken iPhone over USB
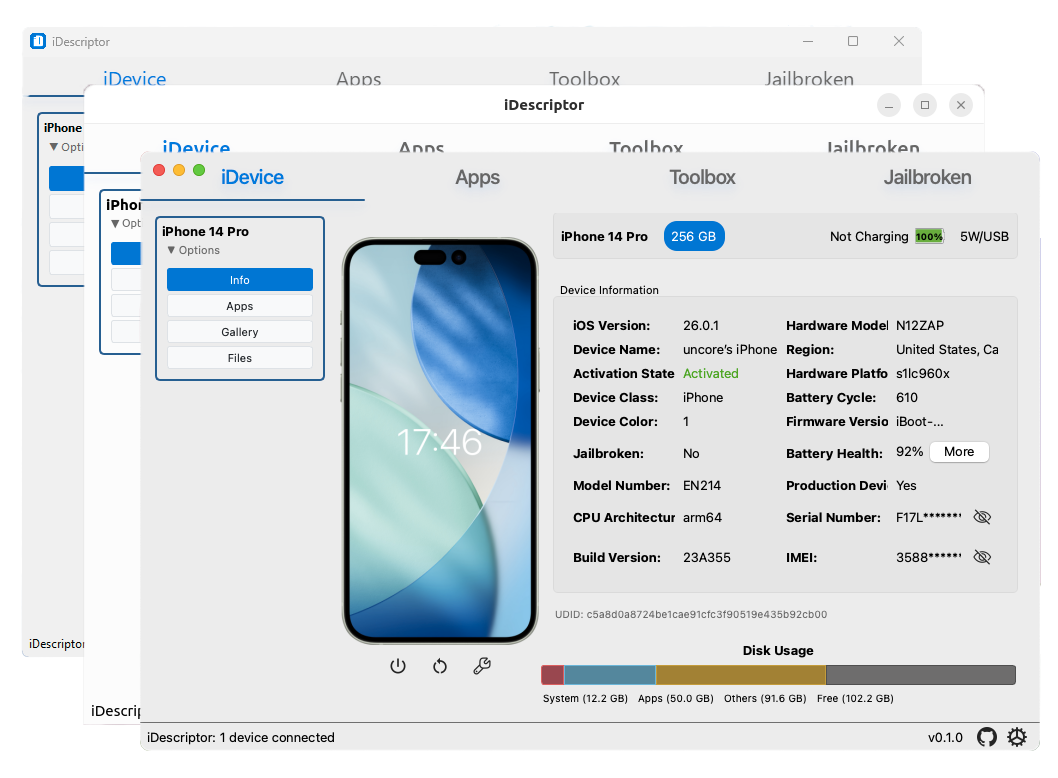 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
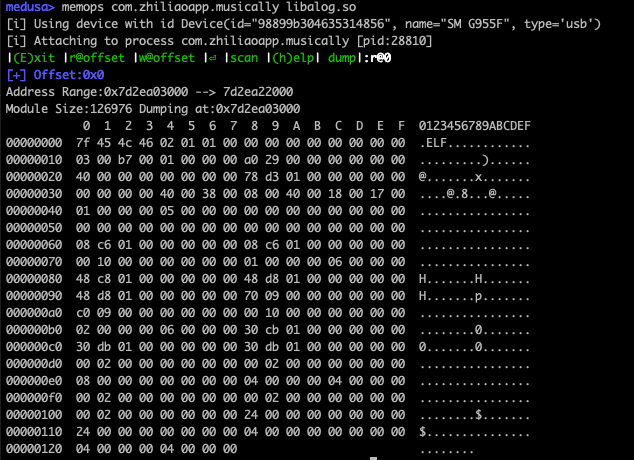 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 owenpawl/cve-2026-84600
Information on the security content of Apple software updates
 ping-2o/ios.cve-2026-84616-84607
research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 speedyfriend433/cve-2026-28867-poc
Kernel info leak Proof of Concept patched in iOS 26.4 / macOS 26.4
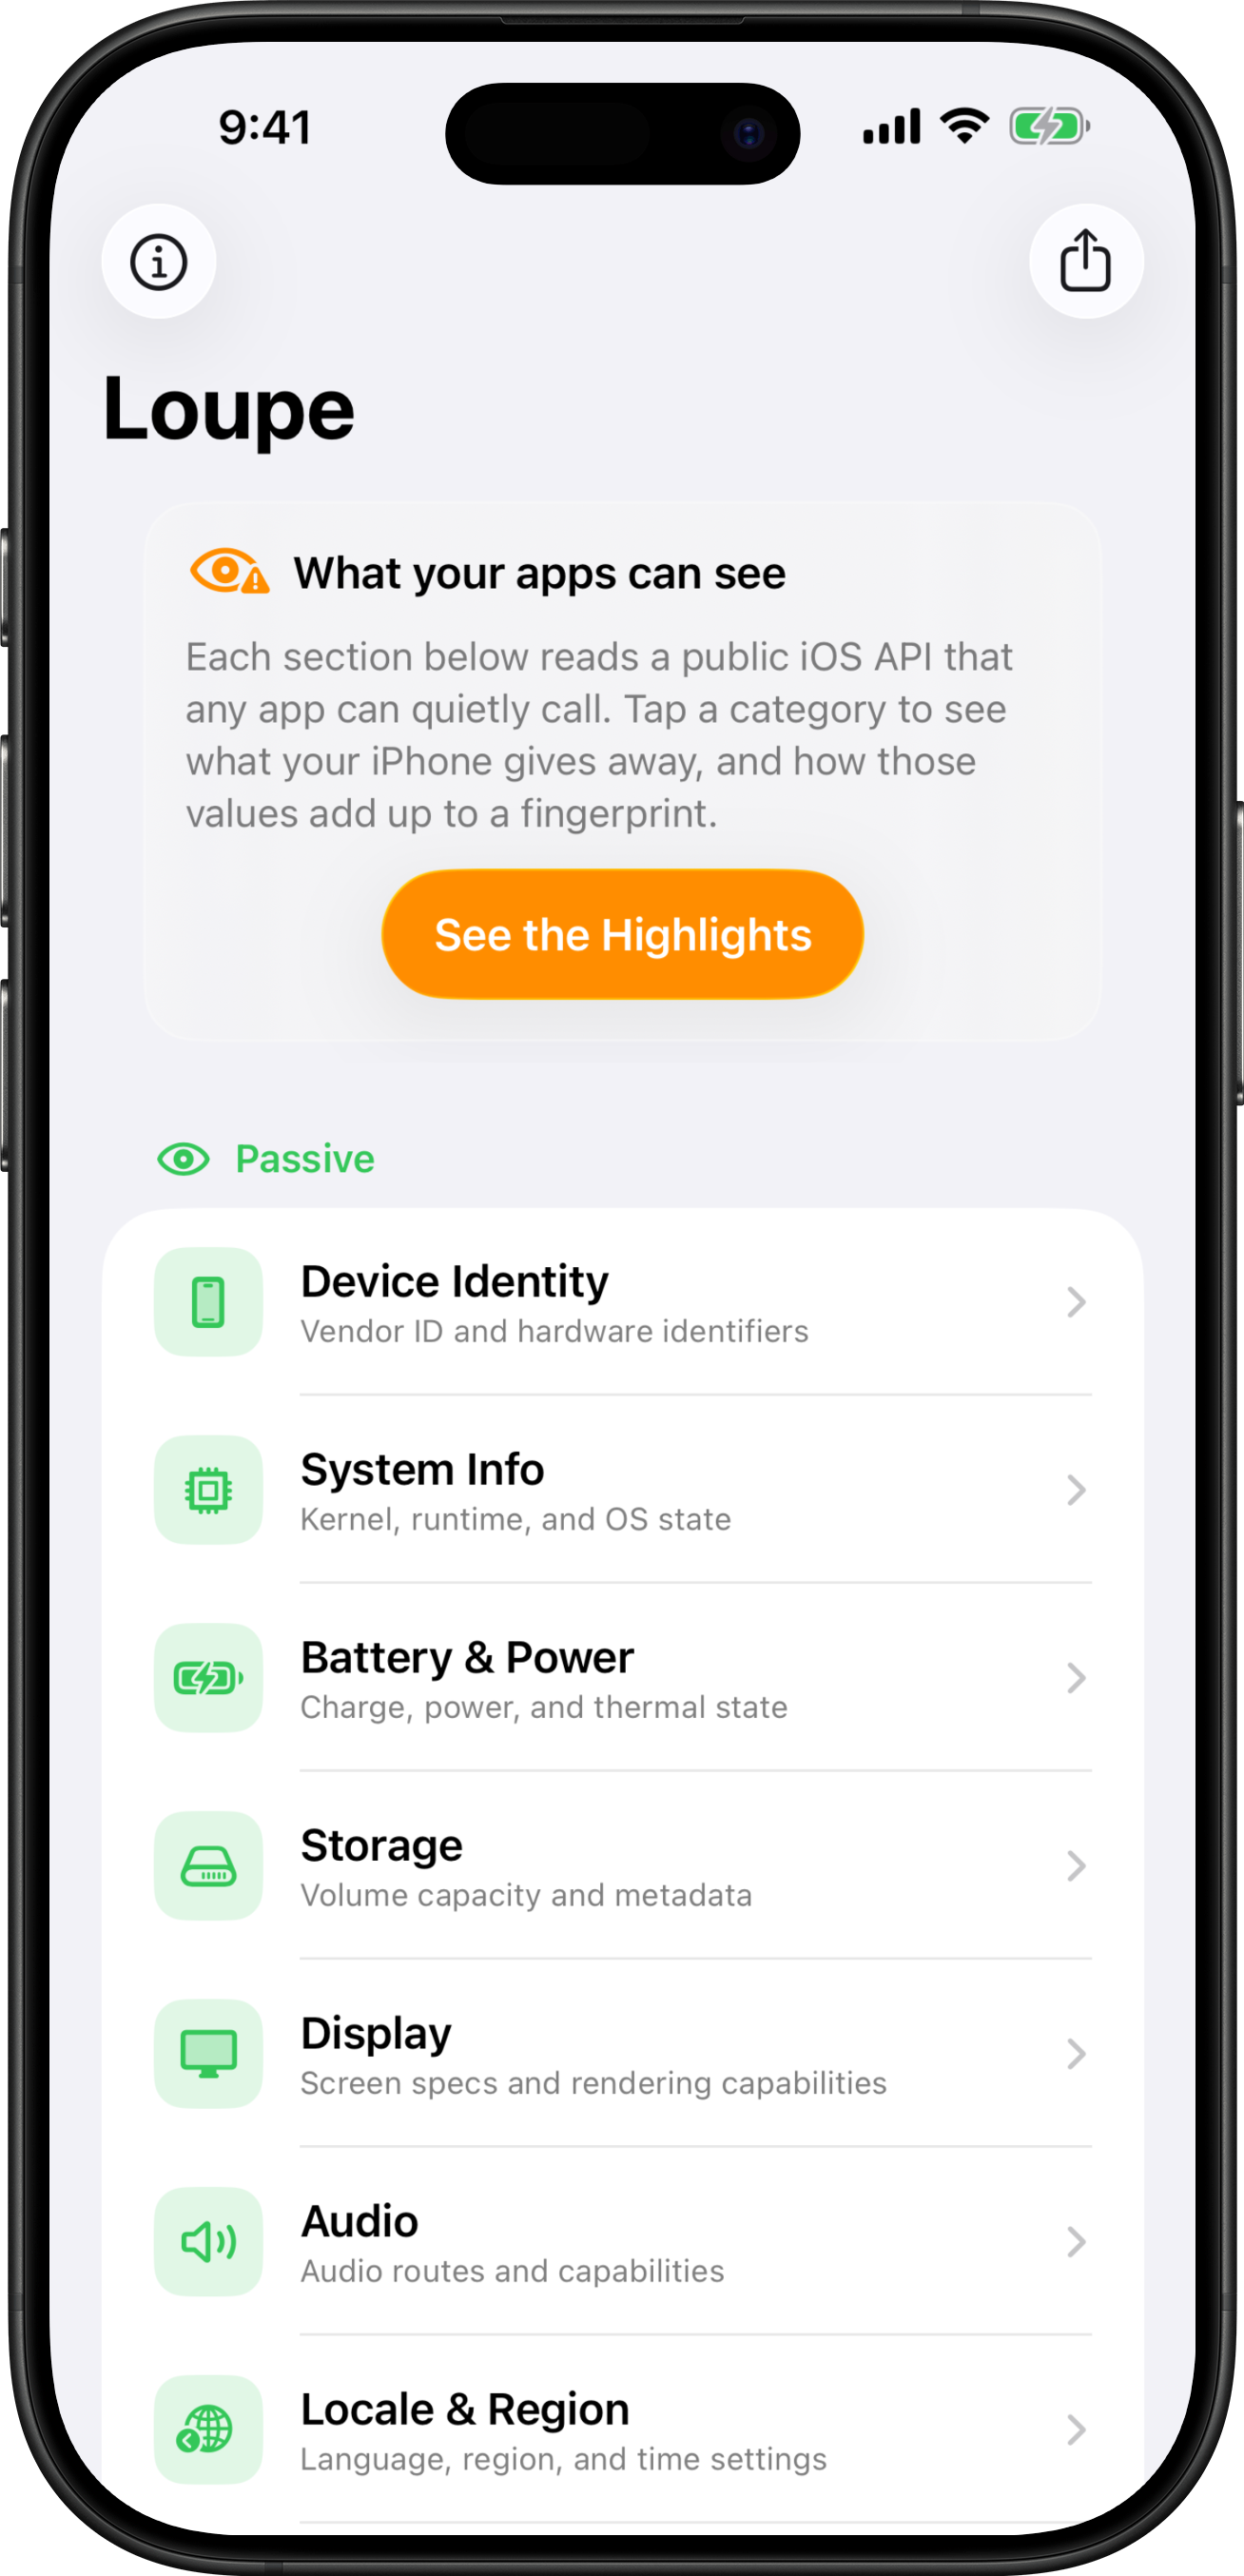 mysk-research/loupe
A privacy-focused iOS app that raises awareness about what native apps can see
 nst/spyphone
This project shows the kind of data a rogue iPhone application can collect.
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 whw0x455/cve-2023-41992
Proof-of-concept for CVE-2023-41992, a macOS kernel vulnerability, demonstrating exploitation techniques and providing a patch analysis.
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…