

unidbg
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
ai-assisted-reversingandroid-securitybinary-analysis+5
5.3k12h 38m ago
zhkl0228/unidbgAllows you to emulate an Android native library, and an experimental iOS emulation

 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 ping-2o/ios.cve-2026-84616-84607
research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
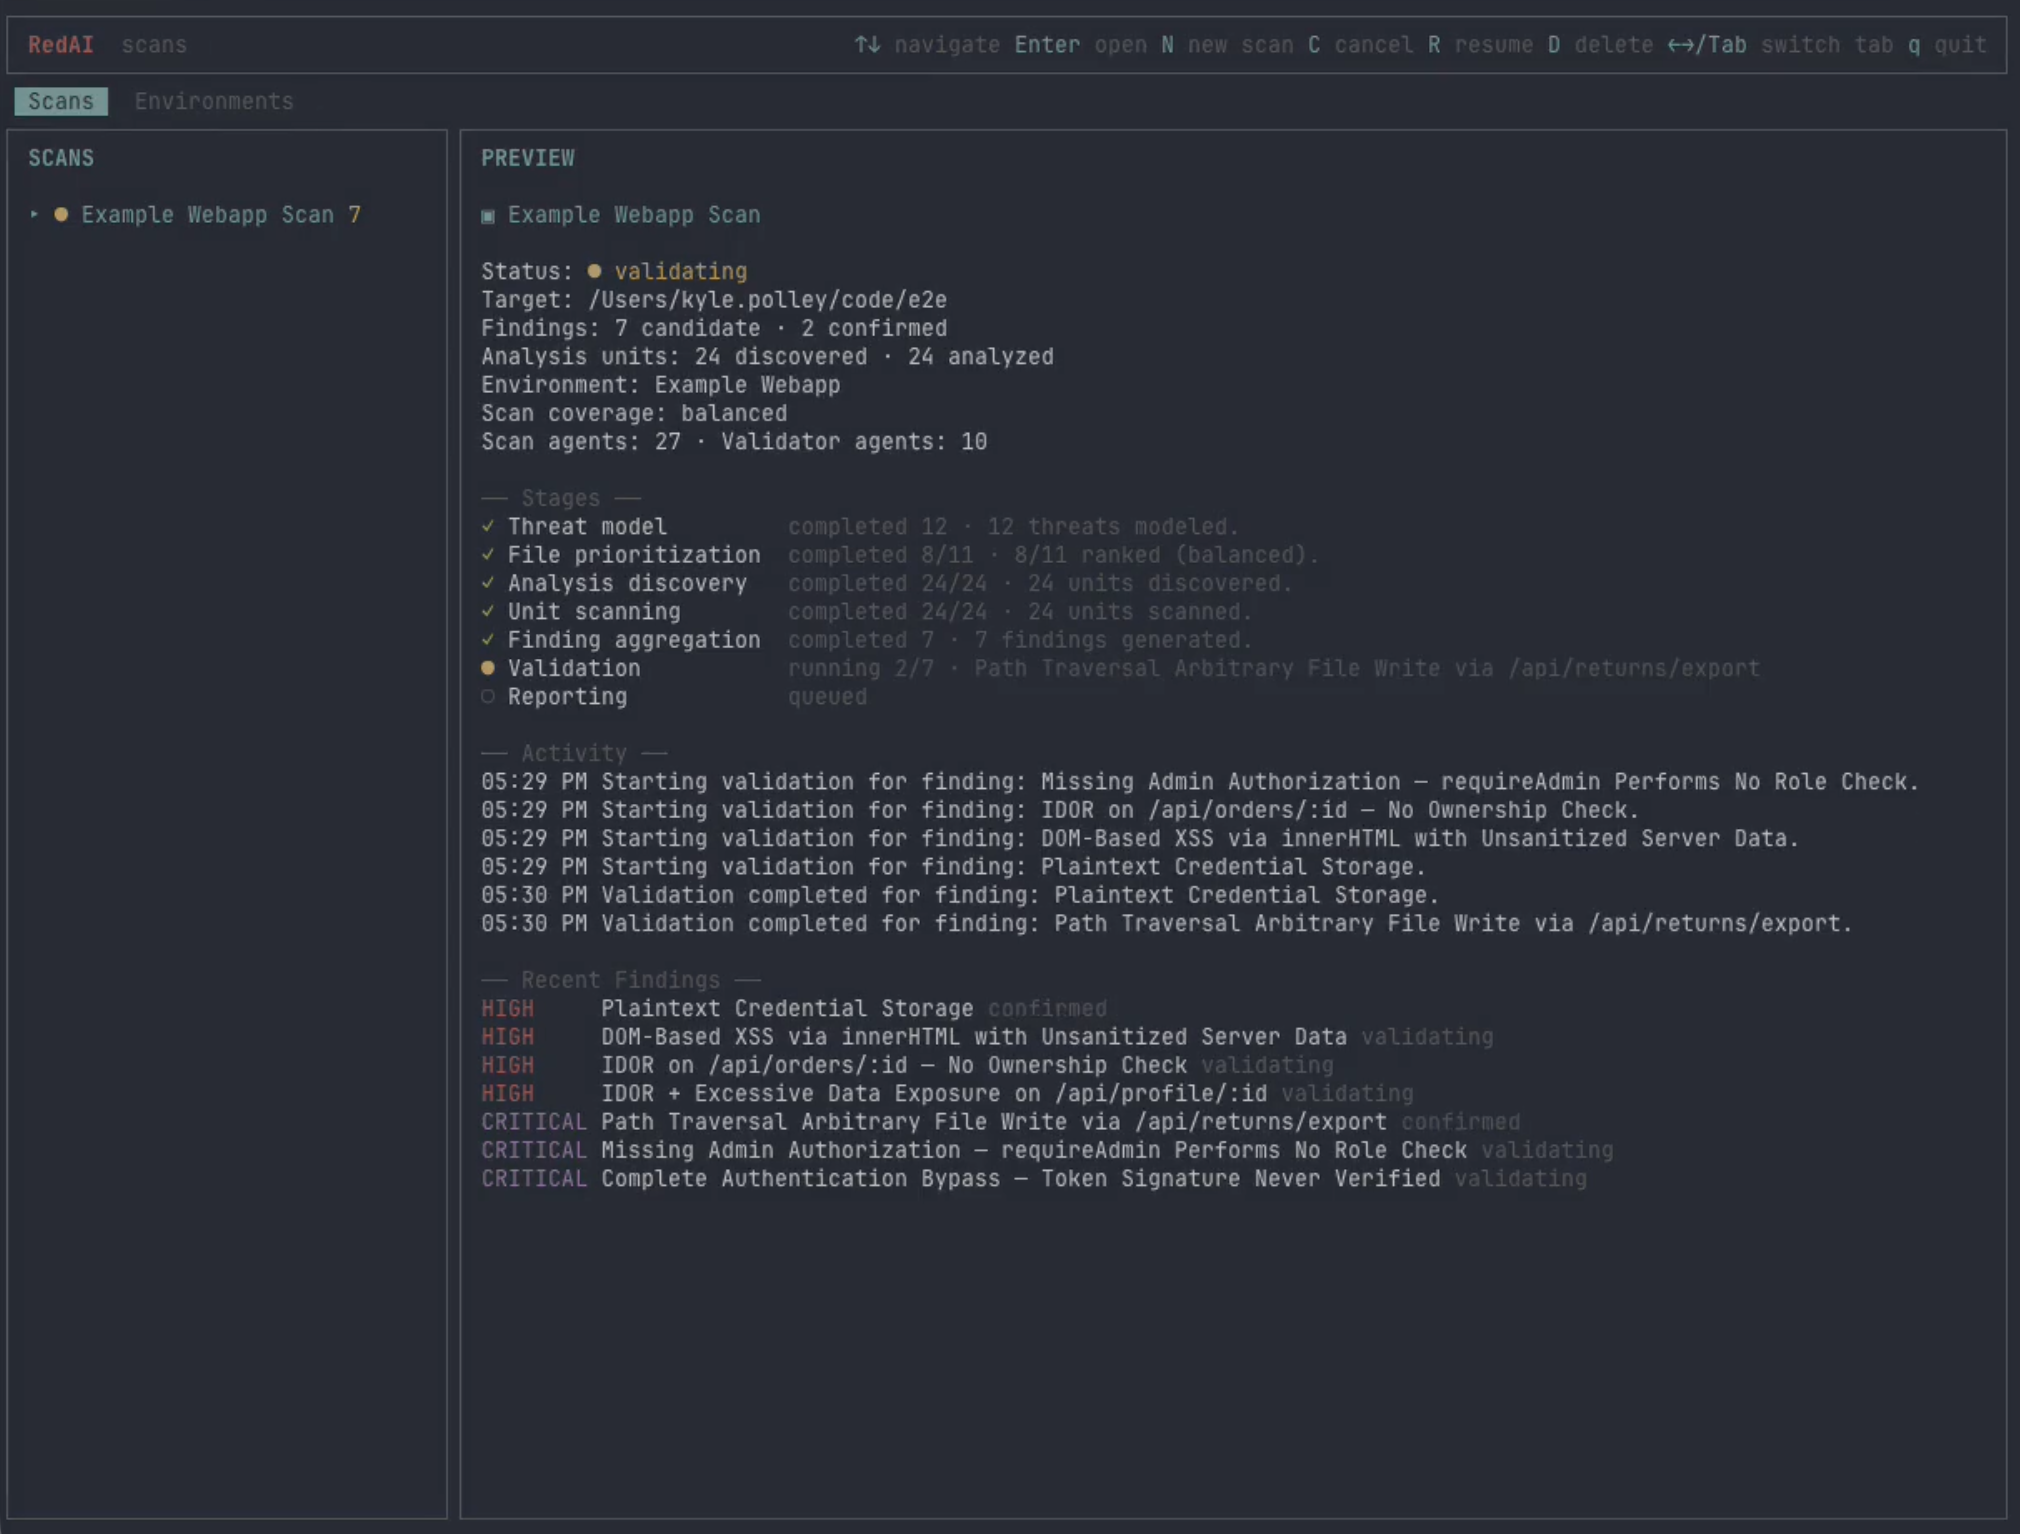 kpolley/redai
AI-driven vulnerability discovery and live validation
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
 calysteon/cve-2025-43504
Technical deep-dive into CVE-2025-43504, a remote pre-authentication global buffer overflow in LLDB's debugserver for iOS, with PoC code and…
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 lauriewired/malimite
iOS and macOS Decompiler
 serundengsapi/cve-2025-31200-ios-audioconverter-rce
Public disclosure of CVE-2025-31200 – Zero-click RCE in iOS 18.X via AudioConverterService and malicious audio file.
 asdfugil/haxx
Untethered + Unsandboxed code execution haxx as root on iOS 14 - iOS 14.8.1.
 xorrior/macostools
macOS offensive security toolkit featuring dylib injection, HID keylogger, and in-memory JXA/Python payload runners for red team operations and…
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 potmdehex/multicast_bytecopy
kernel r/w exploit for iOS 15.0 - 15.1.1