
oob_entry
 rkrakesh524/oob_entry
oob_entry tfp0 kernel exploit for armv7 iOS (iOS 3.0–10.3.4), using CVE-2023-32434. We will publish a write-up detailing the methods in the coming…
binary-exploitationeducationexploitation+4
rkrakesh524/oob_entryoob_entry tfp0 kernel exploit for armv7 iOS (iOS 3.0–10.3.4), using CVE-2023-32434. We will publish a write-up detailing the methods in the coming…
 idescriptor/idescriptor
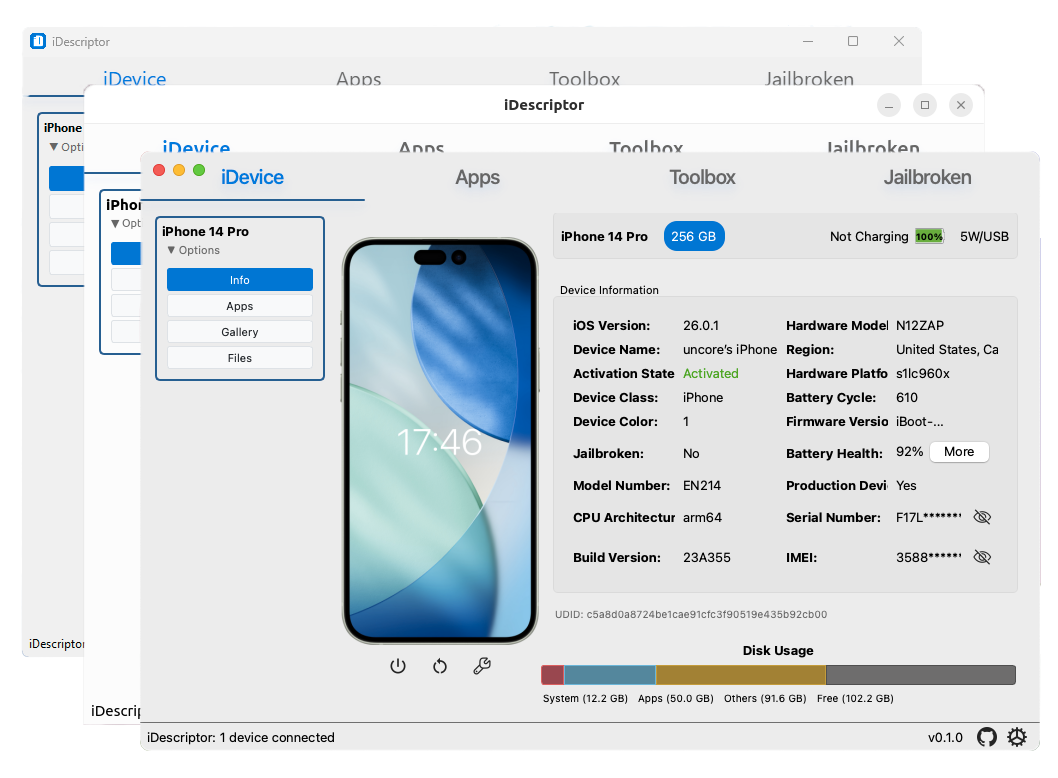
privacy-first, open-source and free idevice management tool written in Rust and Qt
 techupdate24/capacitor-flaw-cve-2026-103922
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 pranshuchittora/simvyn
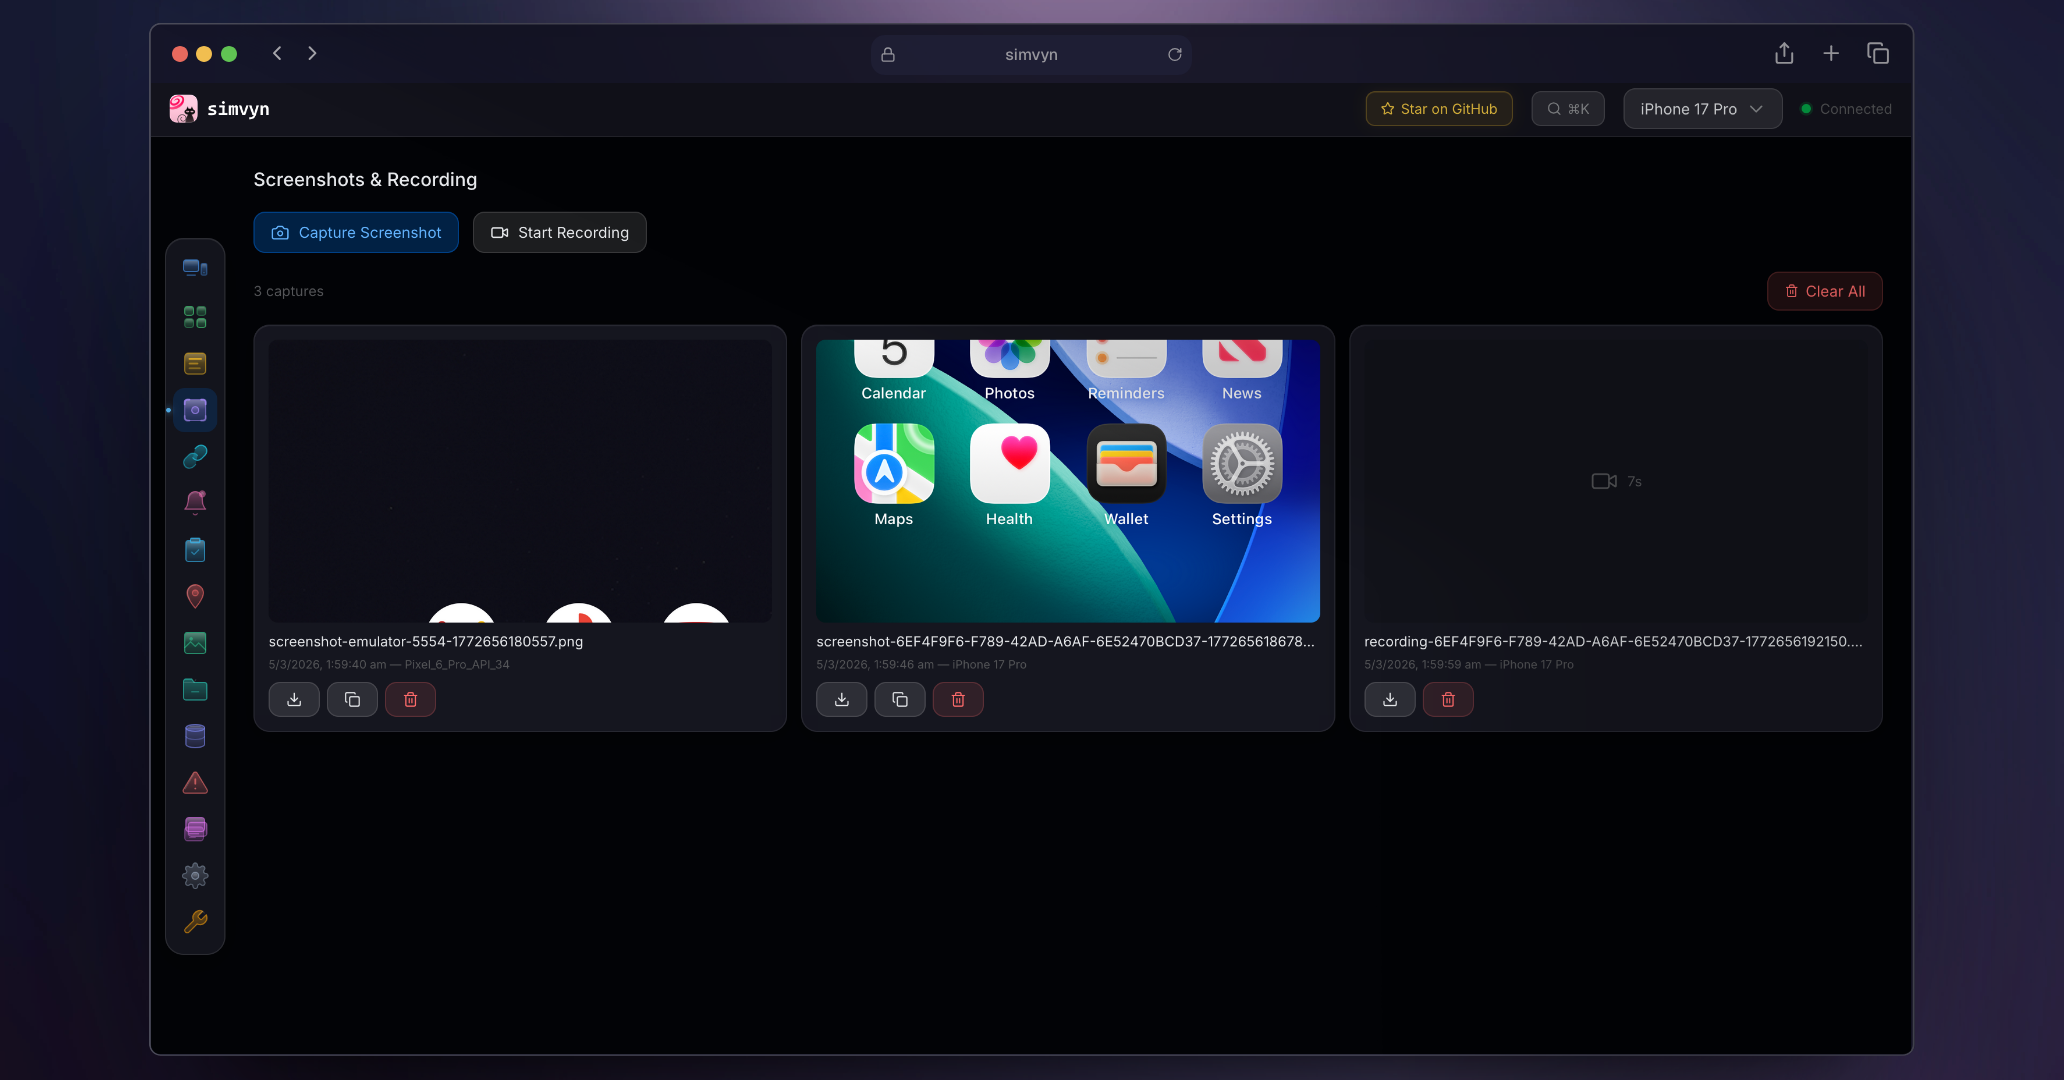
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 robertmak2014-sudow/cve-2026-28995
# CVE-2026-28995 Proof of Concept for CVE-2026-28995 — Path Traversal vulnerability in App Intents on iOS 26.4.2 and below.
 owasp/masvs
The OWASP MASVS (Mobile Application Security Verification Standard) is the industry standard for mobile app security.
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 nomnomheapnom/cve-2024-27815
Proof-of-concept trigger for CVE-2024-27815, an XNU kernel heap buffer overflow in sbconcat_mbufs() reachable via AF_UNIX datagram sockets, causing…
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 hidayat-tanjung/cve-2026-65343-e7eb2ed
PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
 bytev0rtex/cve-2026-65330
Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…
 bytev0rtex/cve-2026-65349
Proof-of-concept for an out-of-bounds write in XNU's vfs_attr_pack_internal (getattrlist) on iOS 26.6, demonstrating kernel heap corruption and…
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…