awesome-game-security

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

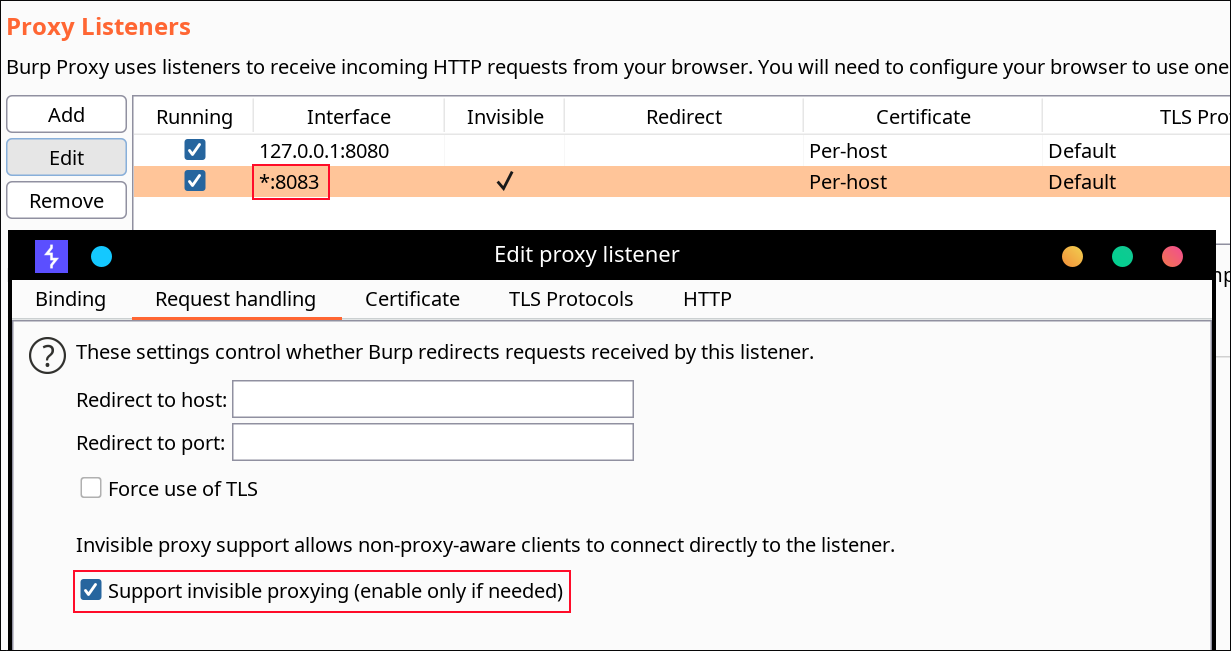
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic

Now you can mirror and control your jailbroken iPhone over USB

Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…

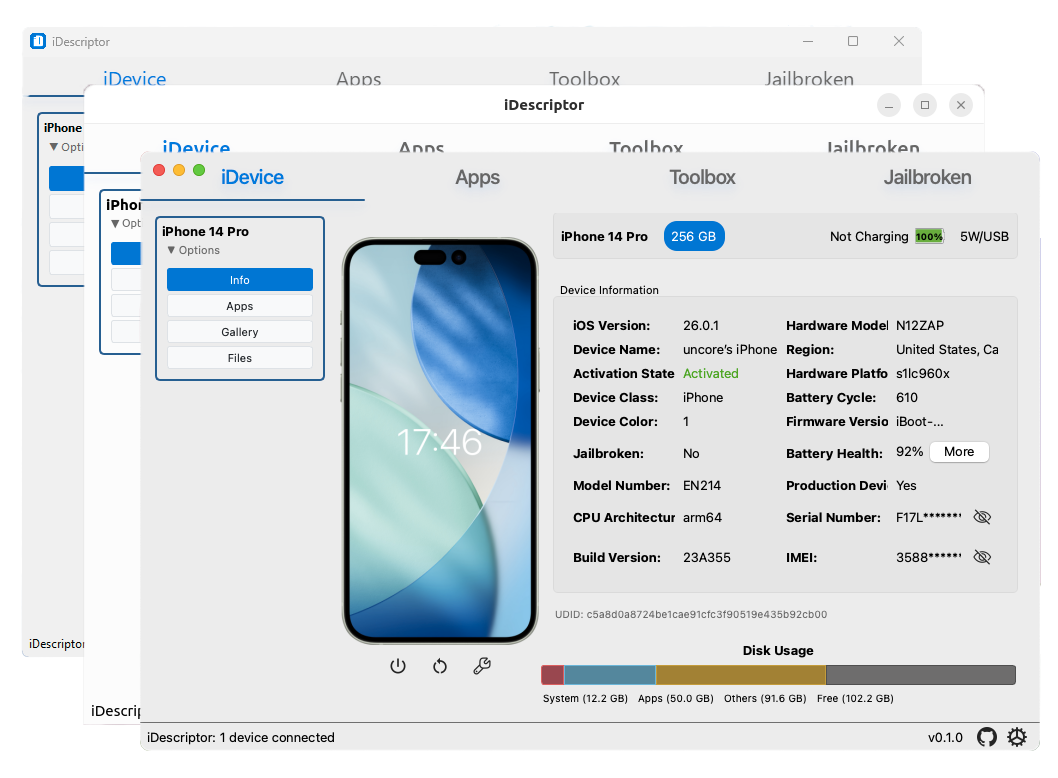
privacy-first, open-source and free idevice management tool written in Rust and Qt

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…

Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…

Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…

A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.

Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…

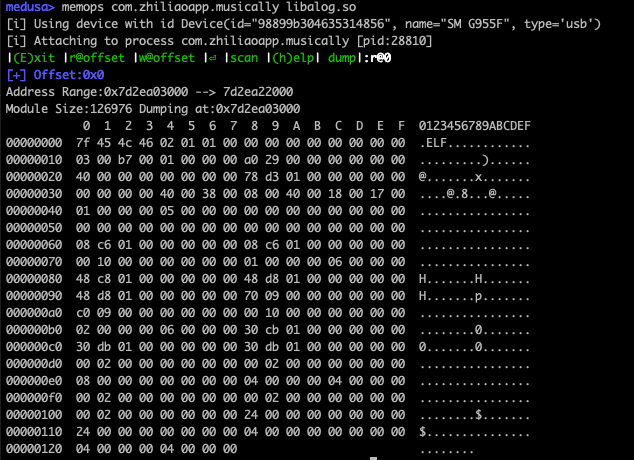
Mobile Edge-Dynamic Unified Security Analysis

OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…

Information on the security content of Apple software updates

Proof-of-concept trigger for CVE-2024-27815, an XNU kernel heap buffer overflow in sbconcat_mbufs() reachable via AF_UNIX datagram sockets, causing…

research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607