

mastg
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
android-securitycryptographydynamic-analysis-sandboxing+9
owasp/mastgComprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
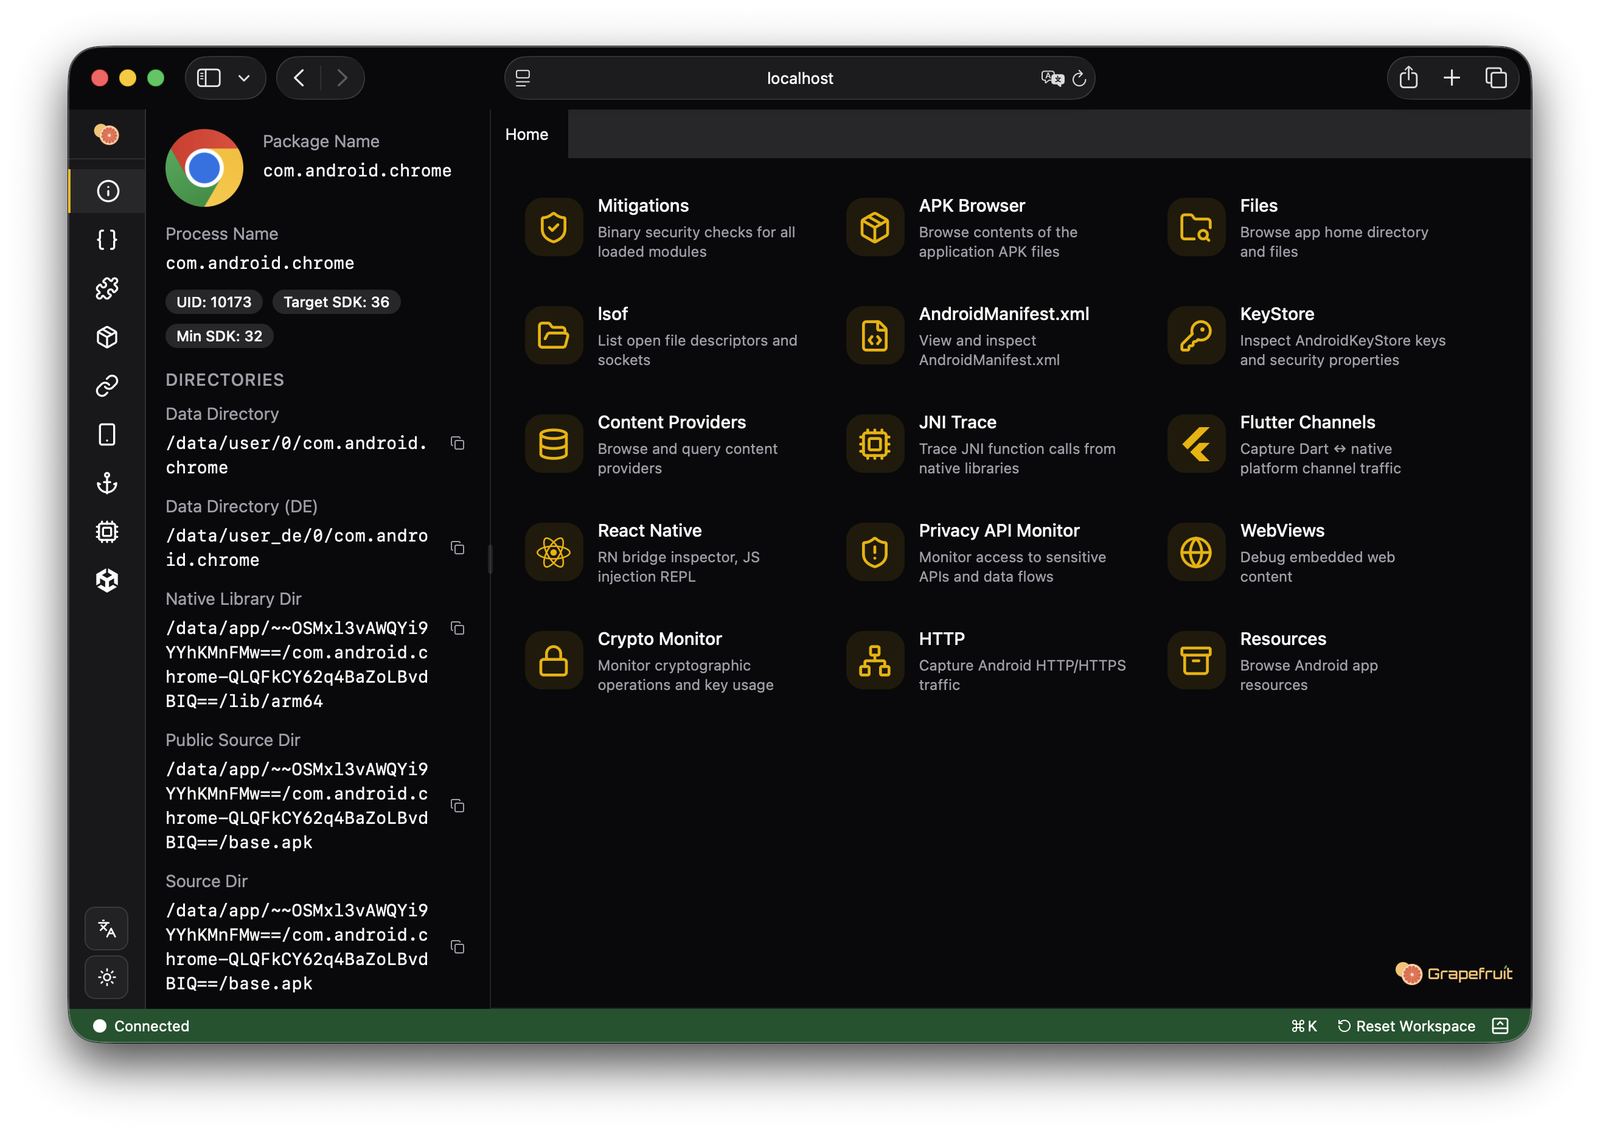 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 nst/spyphone
This project shows the kind of data a rogue iPhone application can collect.
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 soulghost/iblessing
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 d0gukank/cve-2019-1218
Proof-of-concept exploit for a cross-site scripting (XSS) vulnerability in Microsoft Outlook for iOS, enabling email-based spoofing attacks and…
 shawarkhanethicalhacker/cve-2019-8389
[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application
 isecpartners/introspy-ios
Security profiling for blackbox iOS
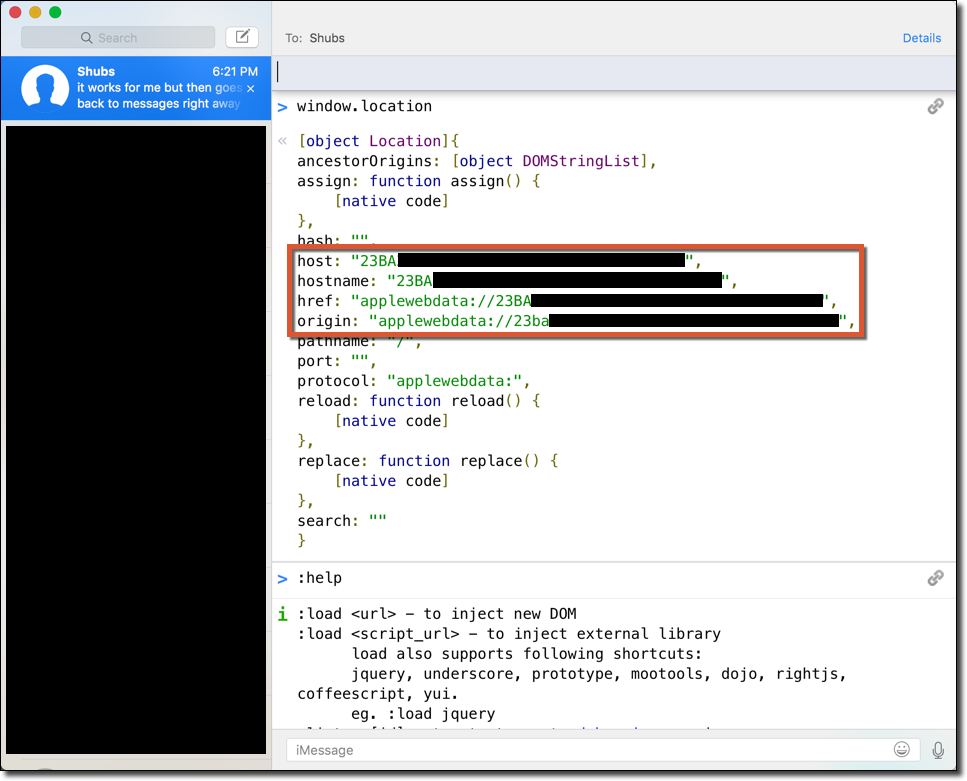 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS