

hermit
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
android-securitybinary-analysiscode-analysis+7
6
xv4l3x/hermitInspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 bytev0rtex/cve-2026-65330
Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 darknavysecurity/poc
Curated proof-of-concept exploits for real-world CVEs affecting iOS, macOS, Chrome Renderer, and Steam clients, with version-specific targets and…
 b1n4r1b01/n-days
Curated collection of iOS kernel and userland exploit PoCs and writeups for in-the-wild and researched CVEs, including binary-diffed vulnerability…
 spiralbl0ck/learning-history-of-cff-bug-in-iphone
Dive into CFF font and coincidently learn about a bof in cff parsing from some jailbreak. just for fun
 spiralbl0ck/mallicious-ios-shortcut-keylogger-
iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.
 0xjohnnydev/cve-2026-28992-iohidfamily-fastpathuserclient-race-conditions
UAF and AOP coprocessor panic in IOHIDEventServiceFastPathUserClient. No entitlements, reachable from app sandbox.
 r3n3r0/cve-2025-5915
Proof-of-concept exploit for a heap over-read in libarchive RAR v4 filter (CVE-2025-5915) with ASan reproduction, encoder, and on-device iOS 18.5…
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
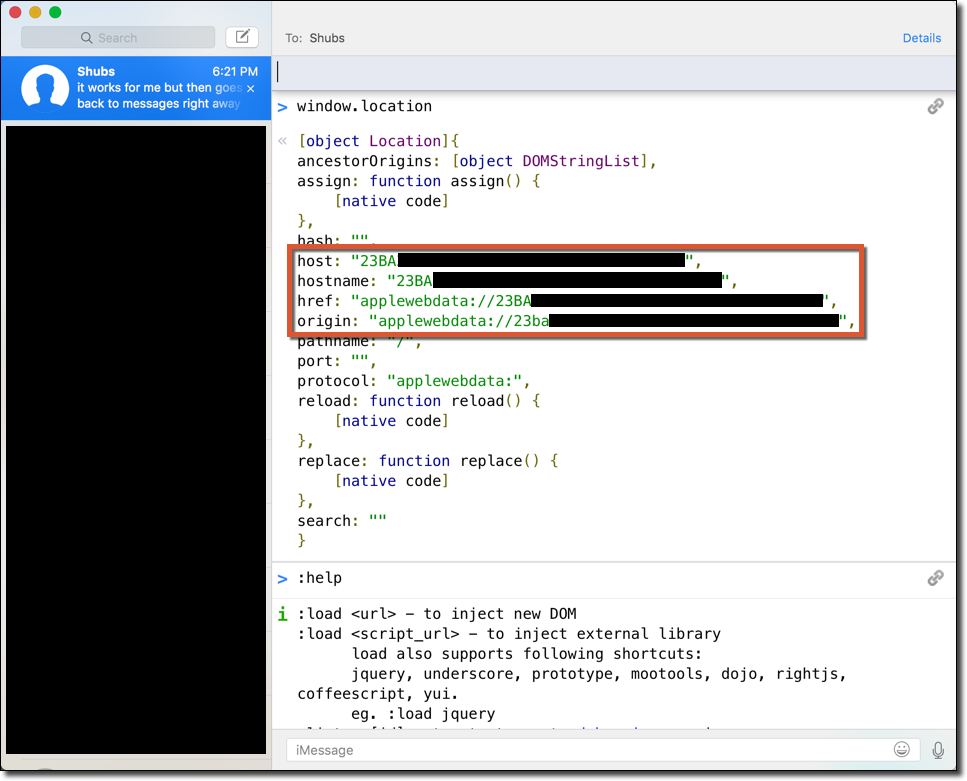 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
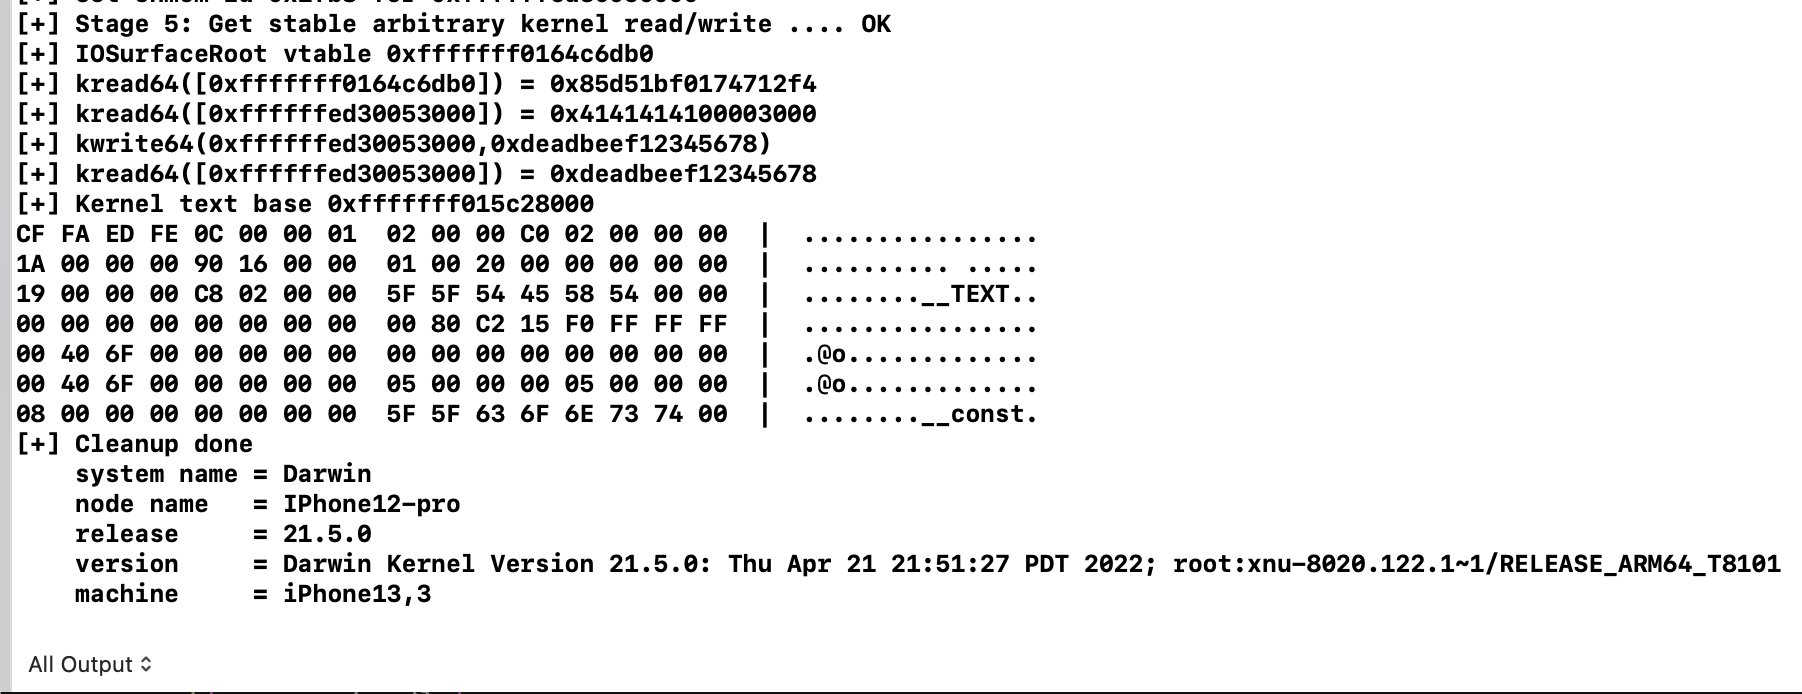 ox1111/cve-2022-32898
Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…
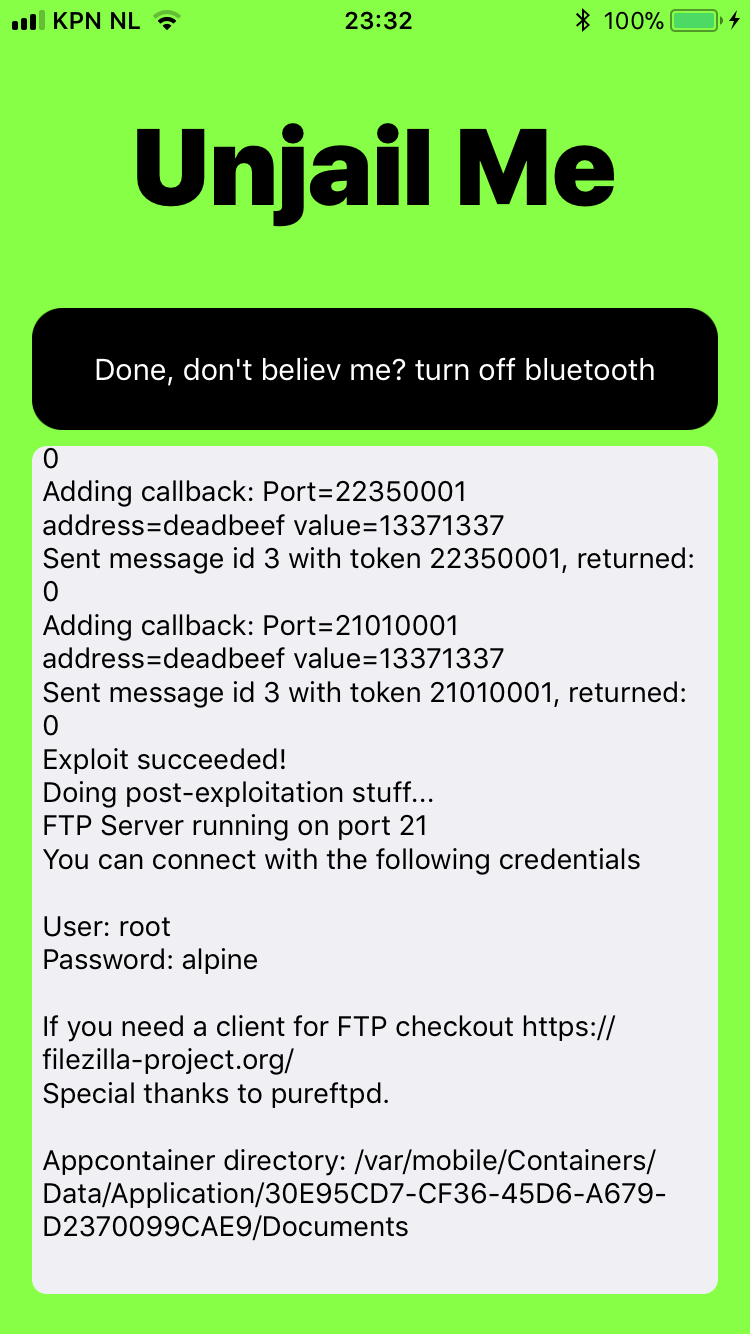 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 josephshenton/triple_fetch-kernel-creds
Attempt to steal kernelcredentials from launchd + task_t pointer (Based on: CVE-2017-7047)
 missaels235/poc-cve-2025-24104-py
Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…