
CVE-2026-84600
 owenpawl/cve-2026-84600
Information on the security content of Apple software updates
ios-securitymobile-securityvulnerability-analysis
owenpawl/cve-2026-84600Information on the security content of Apple software updates
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 ping-2o/ios.cve-2026-84616-84607
research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 eddinos2/cve-2026-28956-jxl-messages-surface
iOS Messages JPEG XL delivery-surface probe and patch-diff notes for CVE-2026-28956.
 realrodri/exploiteameesta
iOS app to check device compatibility with CVE-2021-30937 vulnerability, displaying alerts and popups during the process.
 verygenericname/cve-2021-30955-poc-ipa
Proof-of-concept IPA for CVE-2021-30955, targeting iOS 15.0-15.2b1, demonstrating a local privilege escalation vulnerability.
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
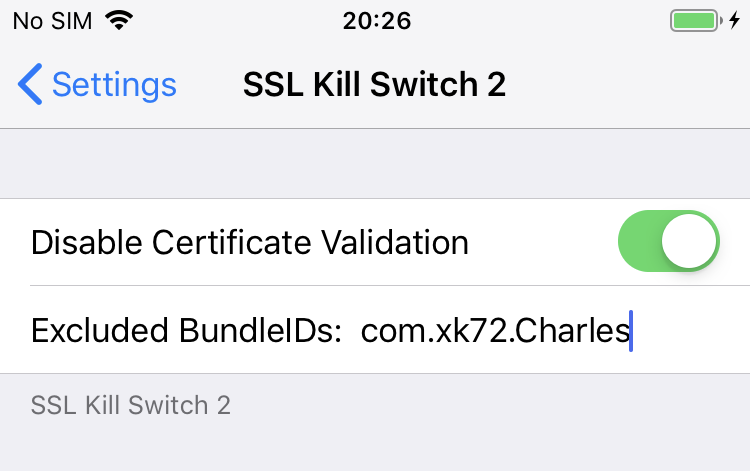 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
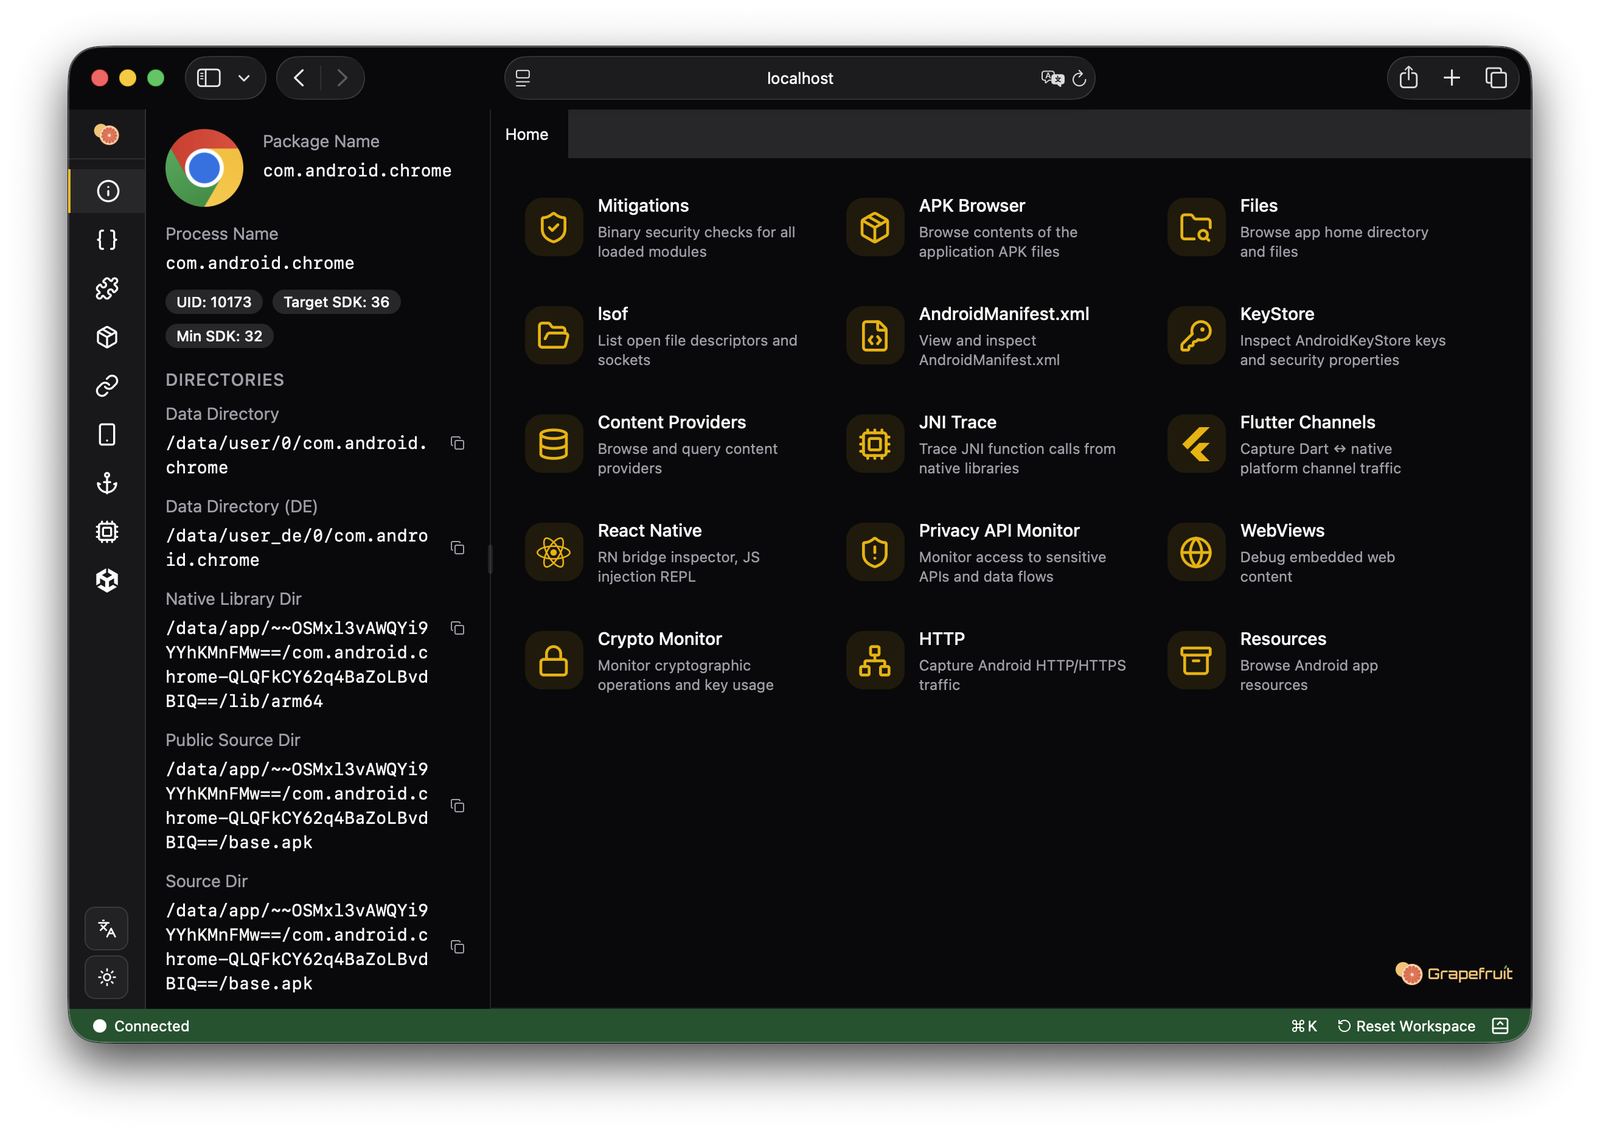 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic