frida-il2cpp-datacollector

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.

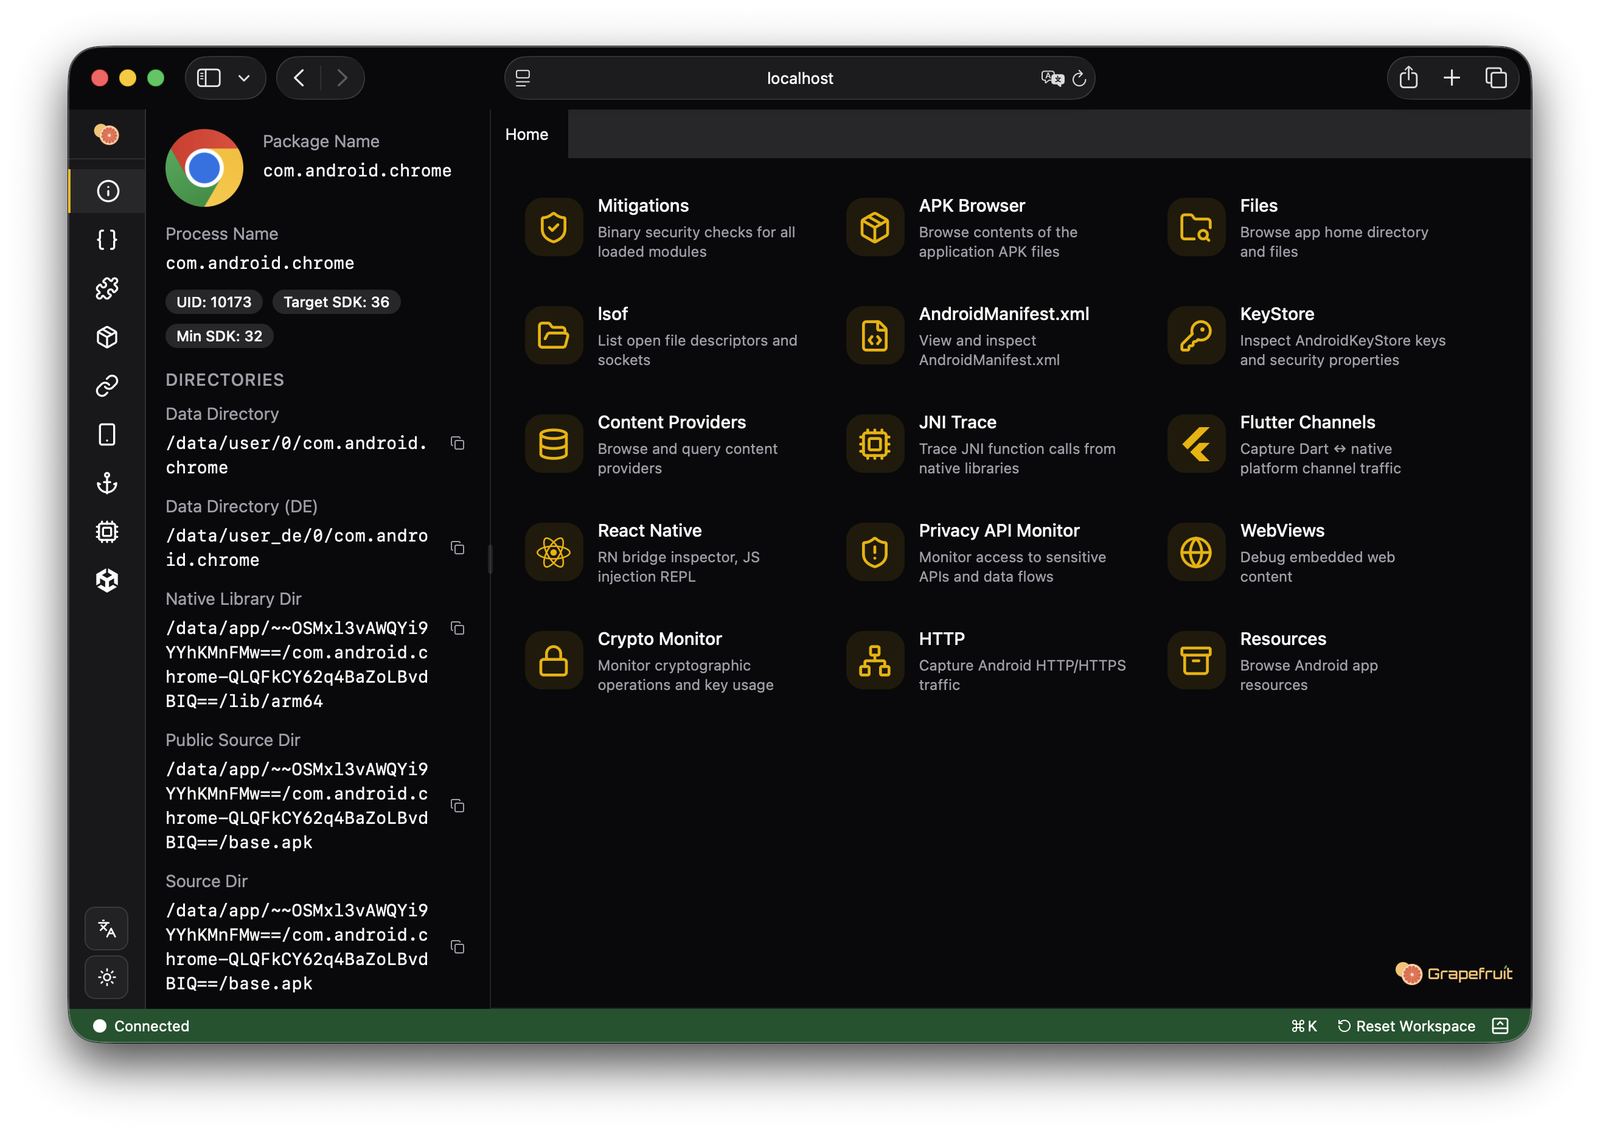
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic

Security profiling for blackbox iOS

CydiaSubstrate-based patch for CVE-2014-4377, a CoreGraphics memory corruption vulnerability on iOS, providing a runtime fix for affected devices.

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS

Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

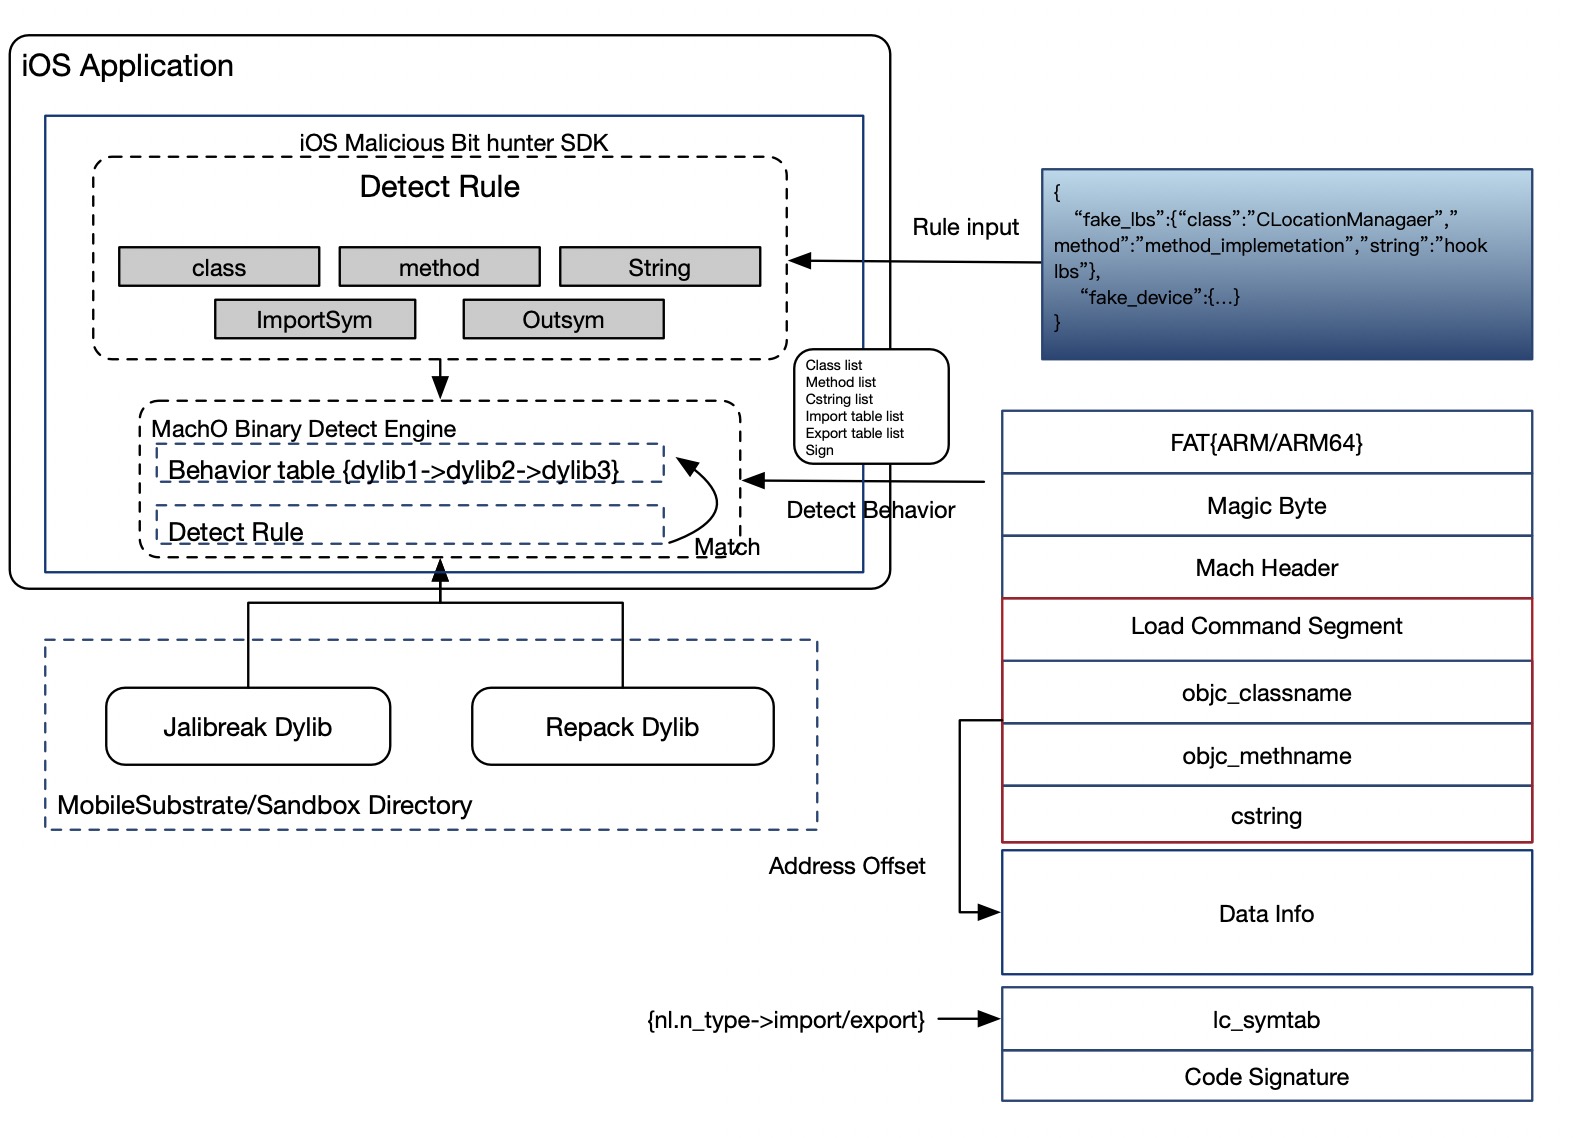
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…

Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

Rust-based Tor library for Android and iOS, providing a standard API to integrate the Arti Tor runtime into mobile apps for private,…