
rinhit
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
bluetooth-securitydigital-forensicsinformation-gathering+6
toxy4ny/rinhitCollects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 kolbicz/appenumguard
CVE-2025-31207 mitigation and sandboxed tester for rootless and rootHide jailbreaks on iOS 15–18.4.1
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 illusionofchaos/ios-gamed-0day
iOS gamed exploit (fixed in 15.0.2)
 illusionofchaos/ios-nehelper-enum-apps-0day
iOS 15 0-day exploit (still works in 15.0.2)
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
 peterpan0927/cve-2017-2370
on Mac 10.12.2
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 nst/spyphone
This project shows the kind of data a rogue iPhone application can collect.
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 owasp/masvs
The OWASP MASVS (Mobile Application Security Verification Standard) is the industry standard for mobile app security.
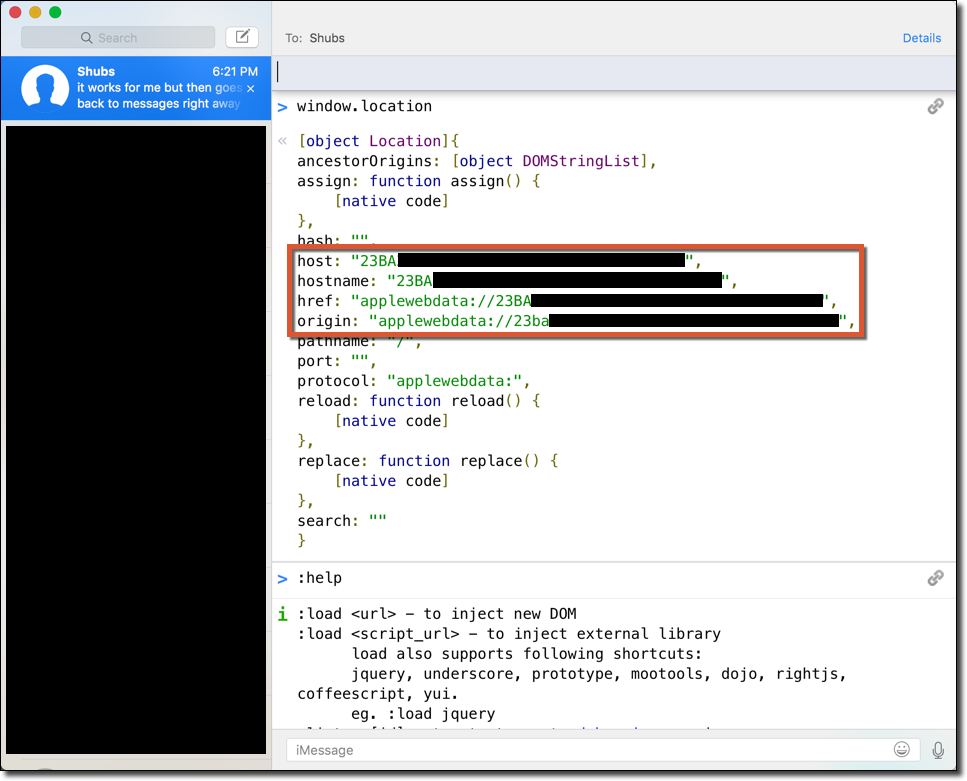 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 tihmstar/freepw_tc7200eploit
Technicolor TC7200 - Credentials Disclosure CVE : CVE-2014-1677
 speedyfriend433/cve-2026-28867-poc
Kernel info leak Proof of Concept patched in iOS 26.4 / macOS 26.4
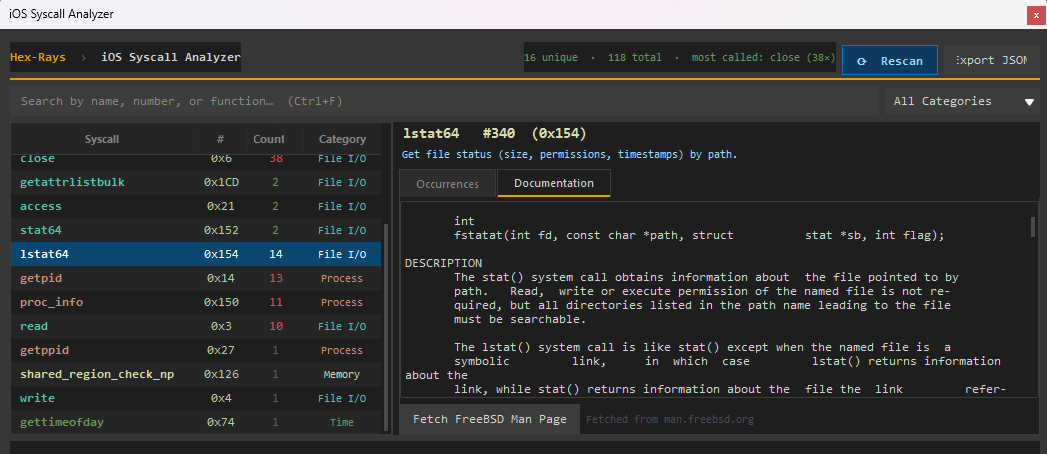 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 owasp/mas-website
The OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…