frida-il2cpp-datacollector

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…

Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.

Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.

Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…

An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs

Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…

A jailbreak tool for all arm64 devices on iOS 16.0 to iOS 16.6.1


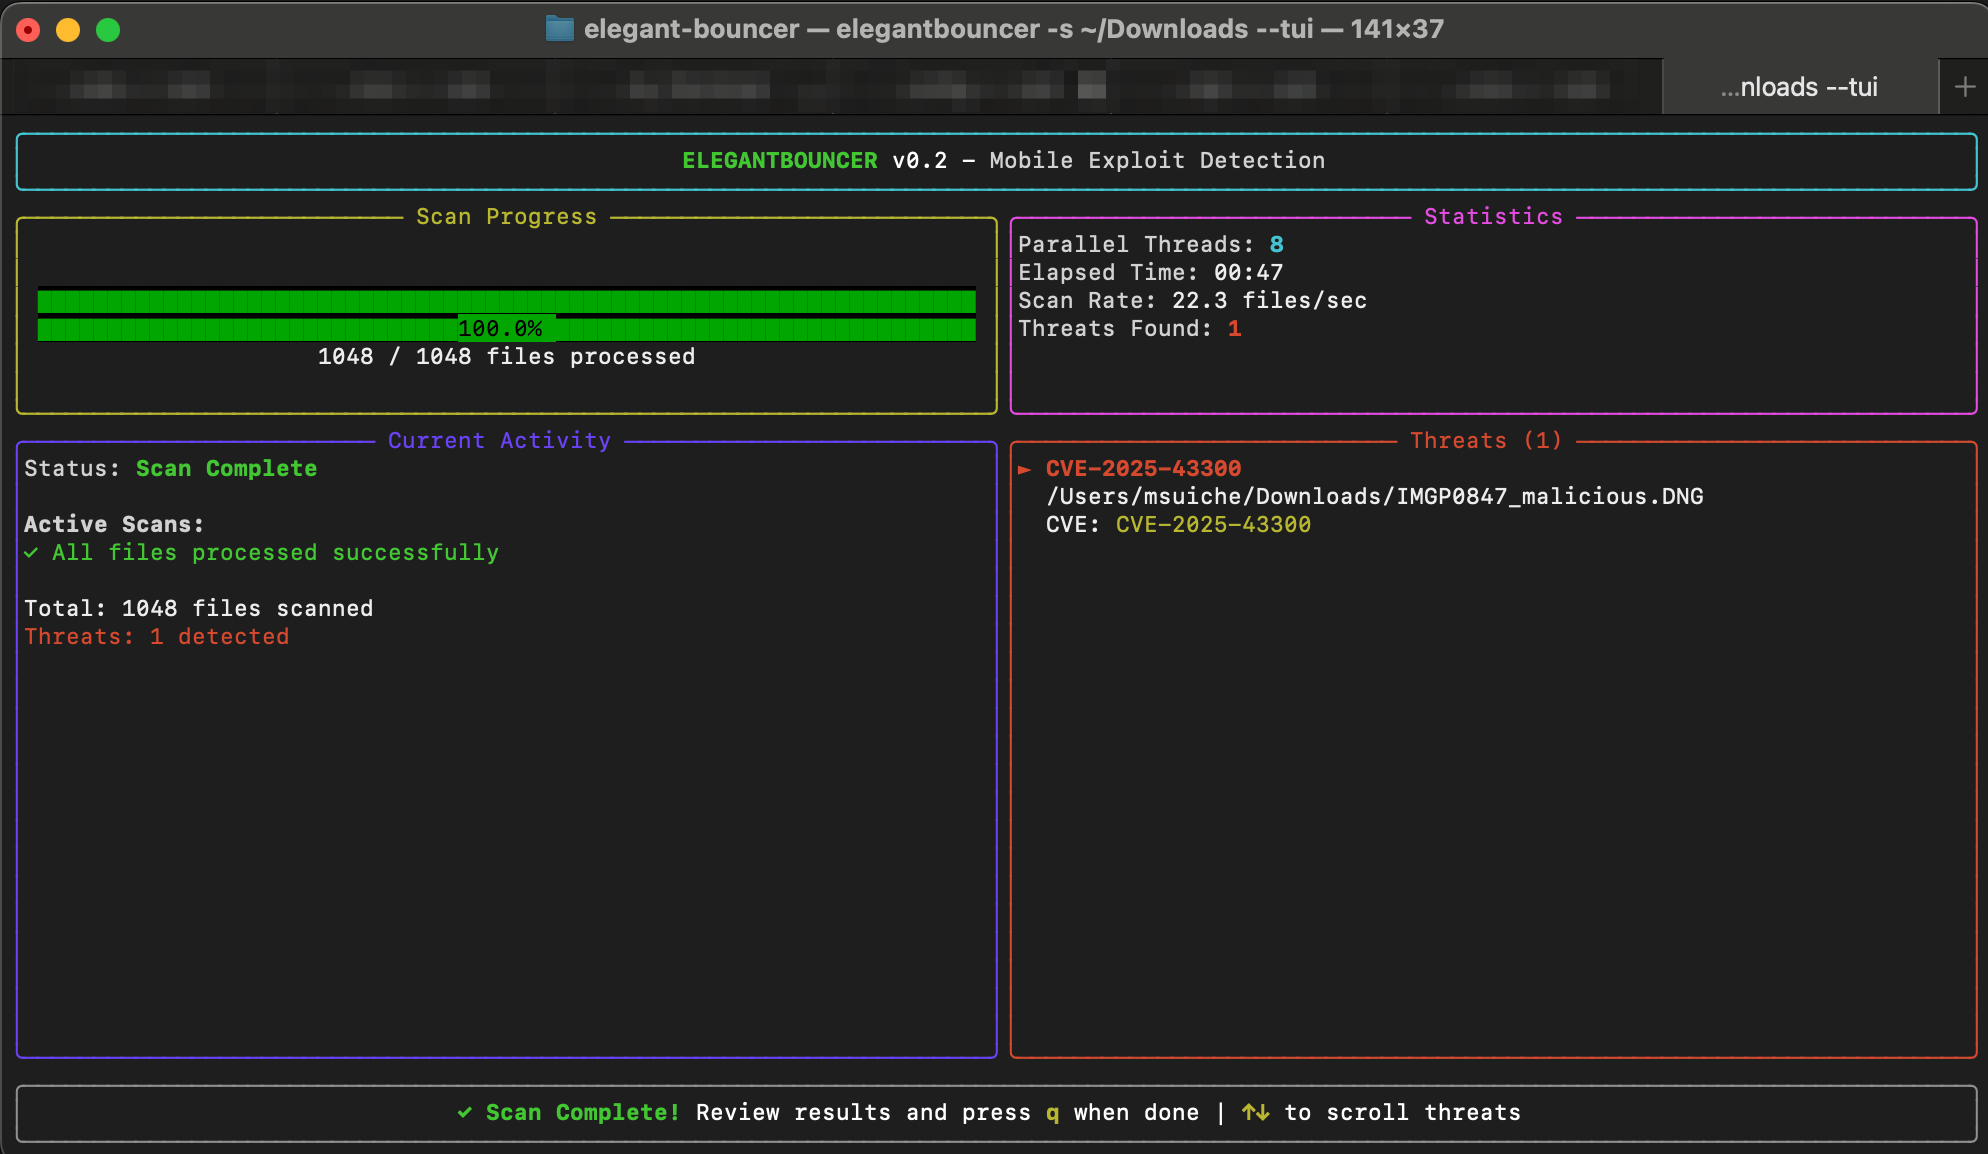
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

Utility to decrypt App Store apps on jailbroken iOS 11.x

open-source jailbreaking tool for many iOS devices

CVE-2026-43813: CloudAttestation enforceEnvironment bypass

Security profiling for blackbox iOS

Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.

This uses CVE-2025-43407 as exploit and still testing working not gauranteed.