

Charles-Proxy-Mobile-Guide
 thyrlian/charles-proxy-mobile-guide
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…
android-securityeducationios-security+6
thyrlian/charles-proxy-mobile-guideStep-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
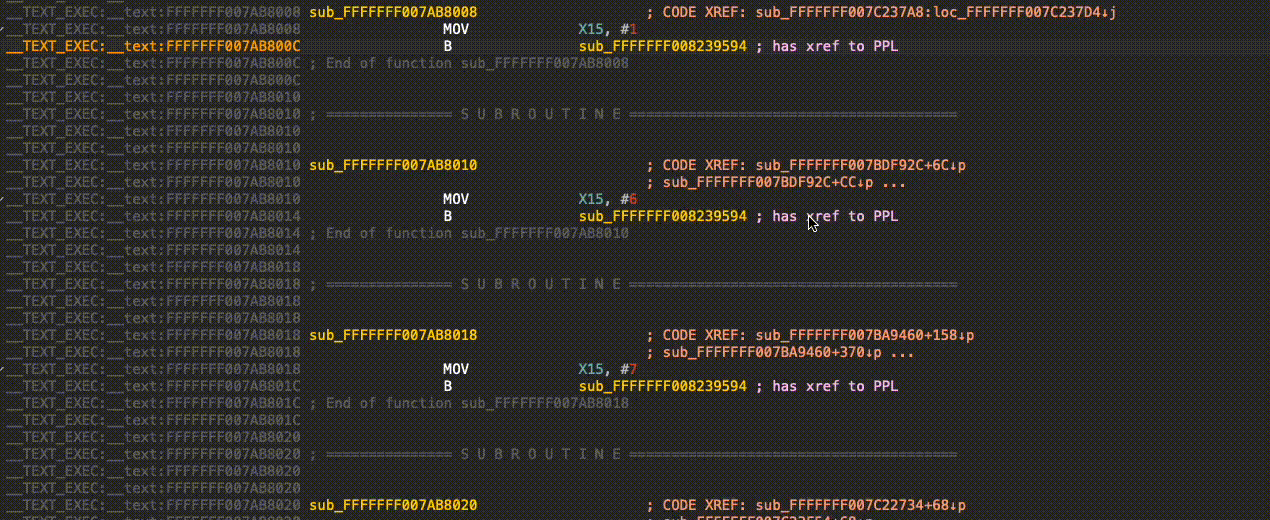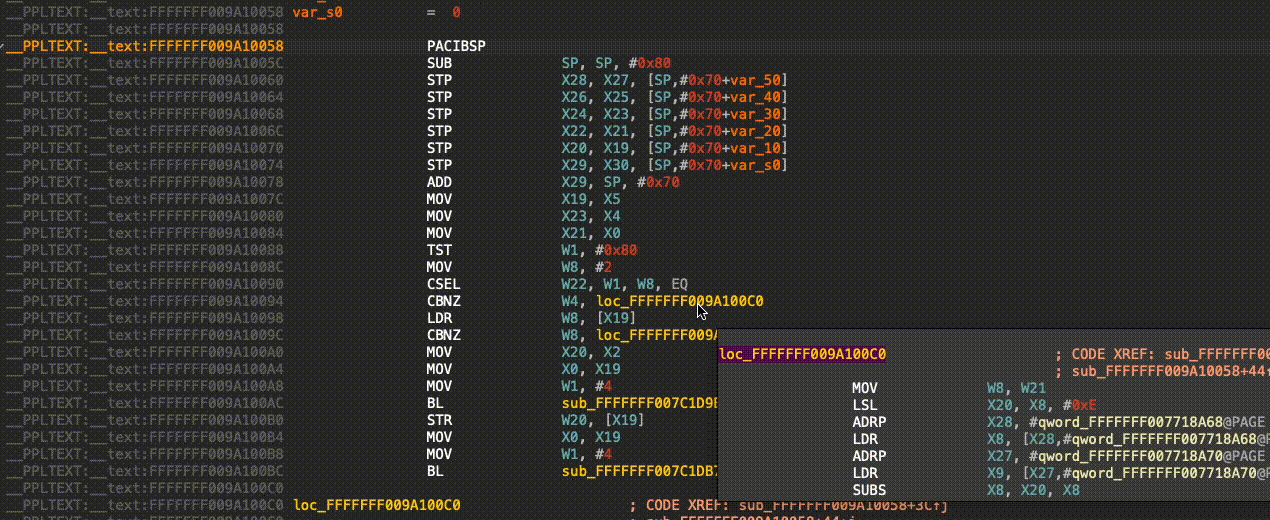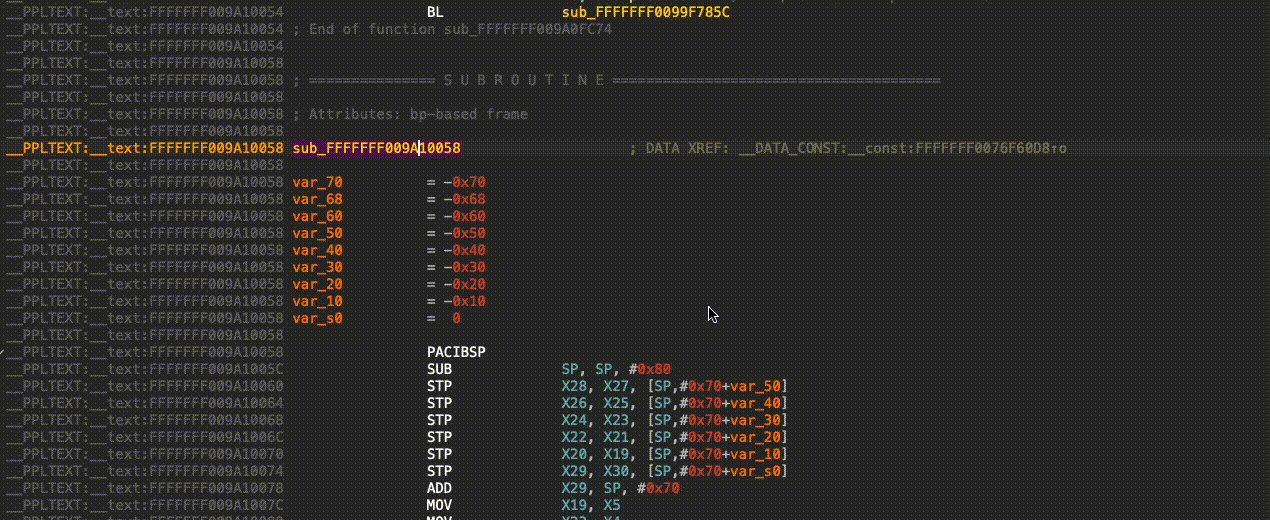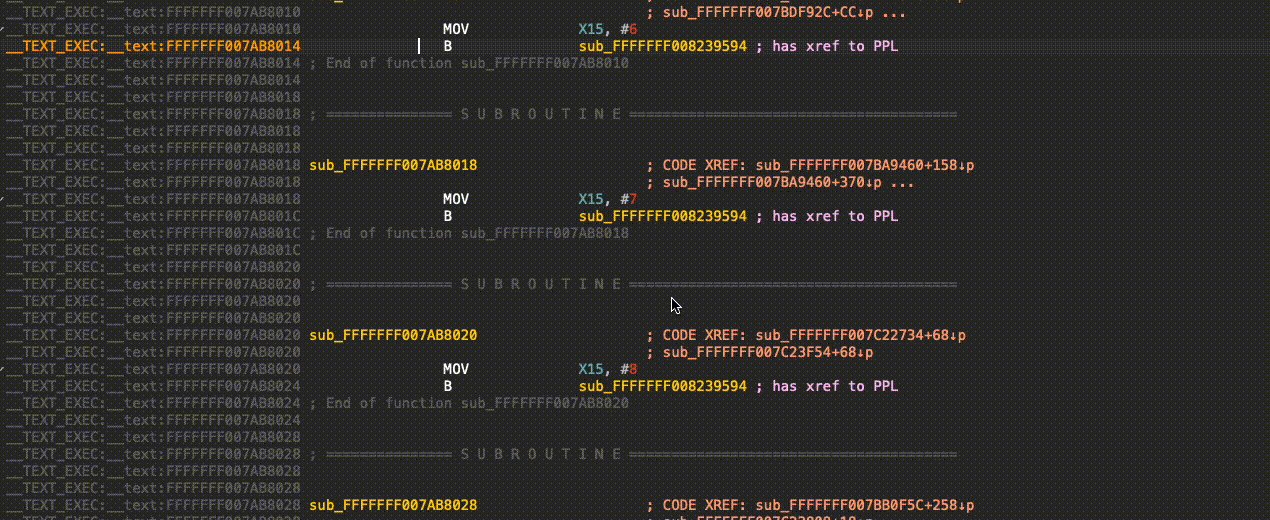 cellebrite-labs/pplorer
IDA plugin that resolves PPL calls to the actual underlying PPL function.
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 george0papasotiriou/cve-2026-22011-ios-mdm-profile-delivery-over-http
PoC Flask server for CVE-2026-22011 that serves a malicious iOS MDM enrollment profile over HTTP, enabling man-in-the-middle interception and device…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 owasp/masvs
The OWASP MASVS (Mobile Application Security Verification Standard) is the industry standard for mobile app security.
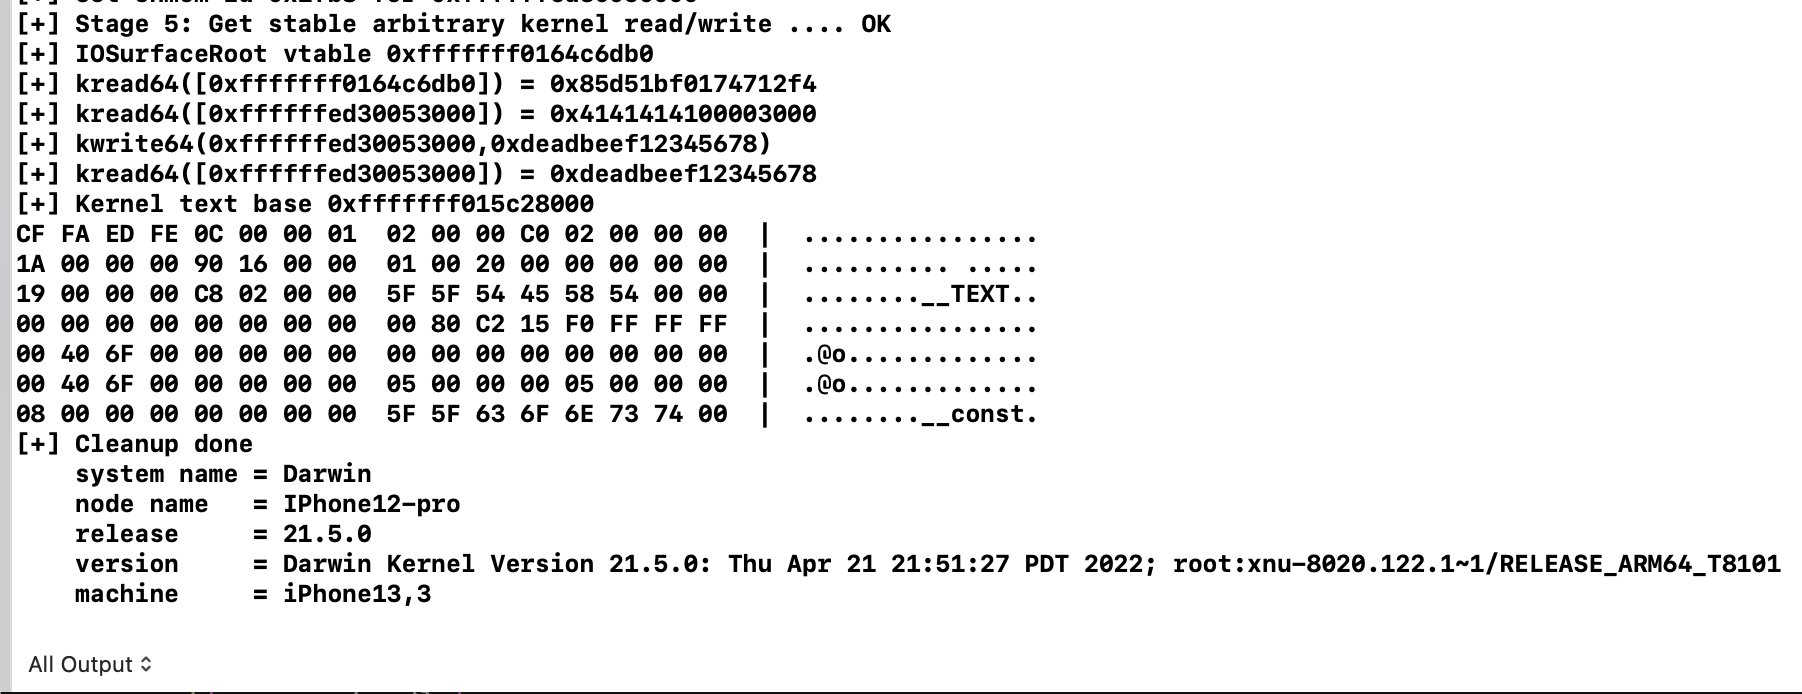 ox1111/cve-2022-32898
Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…
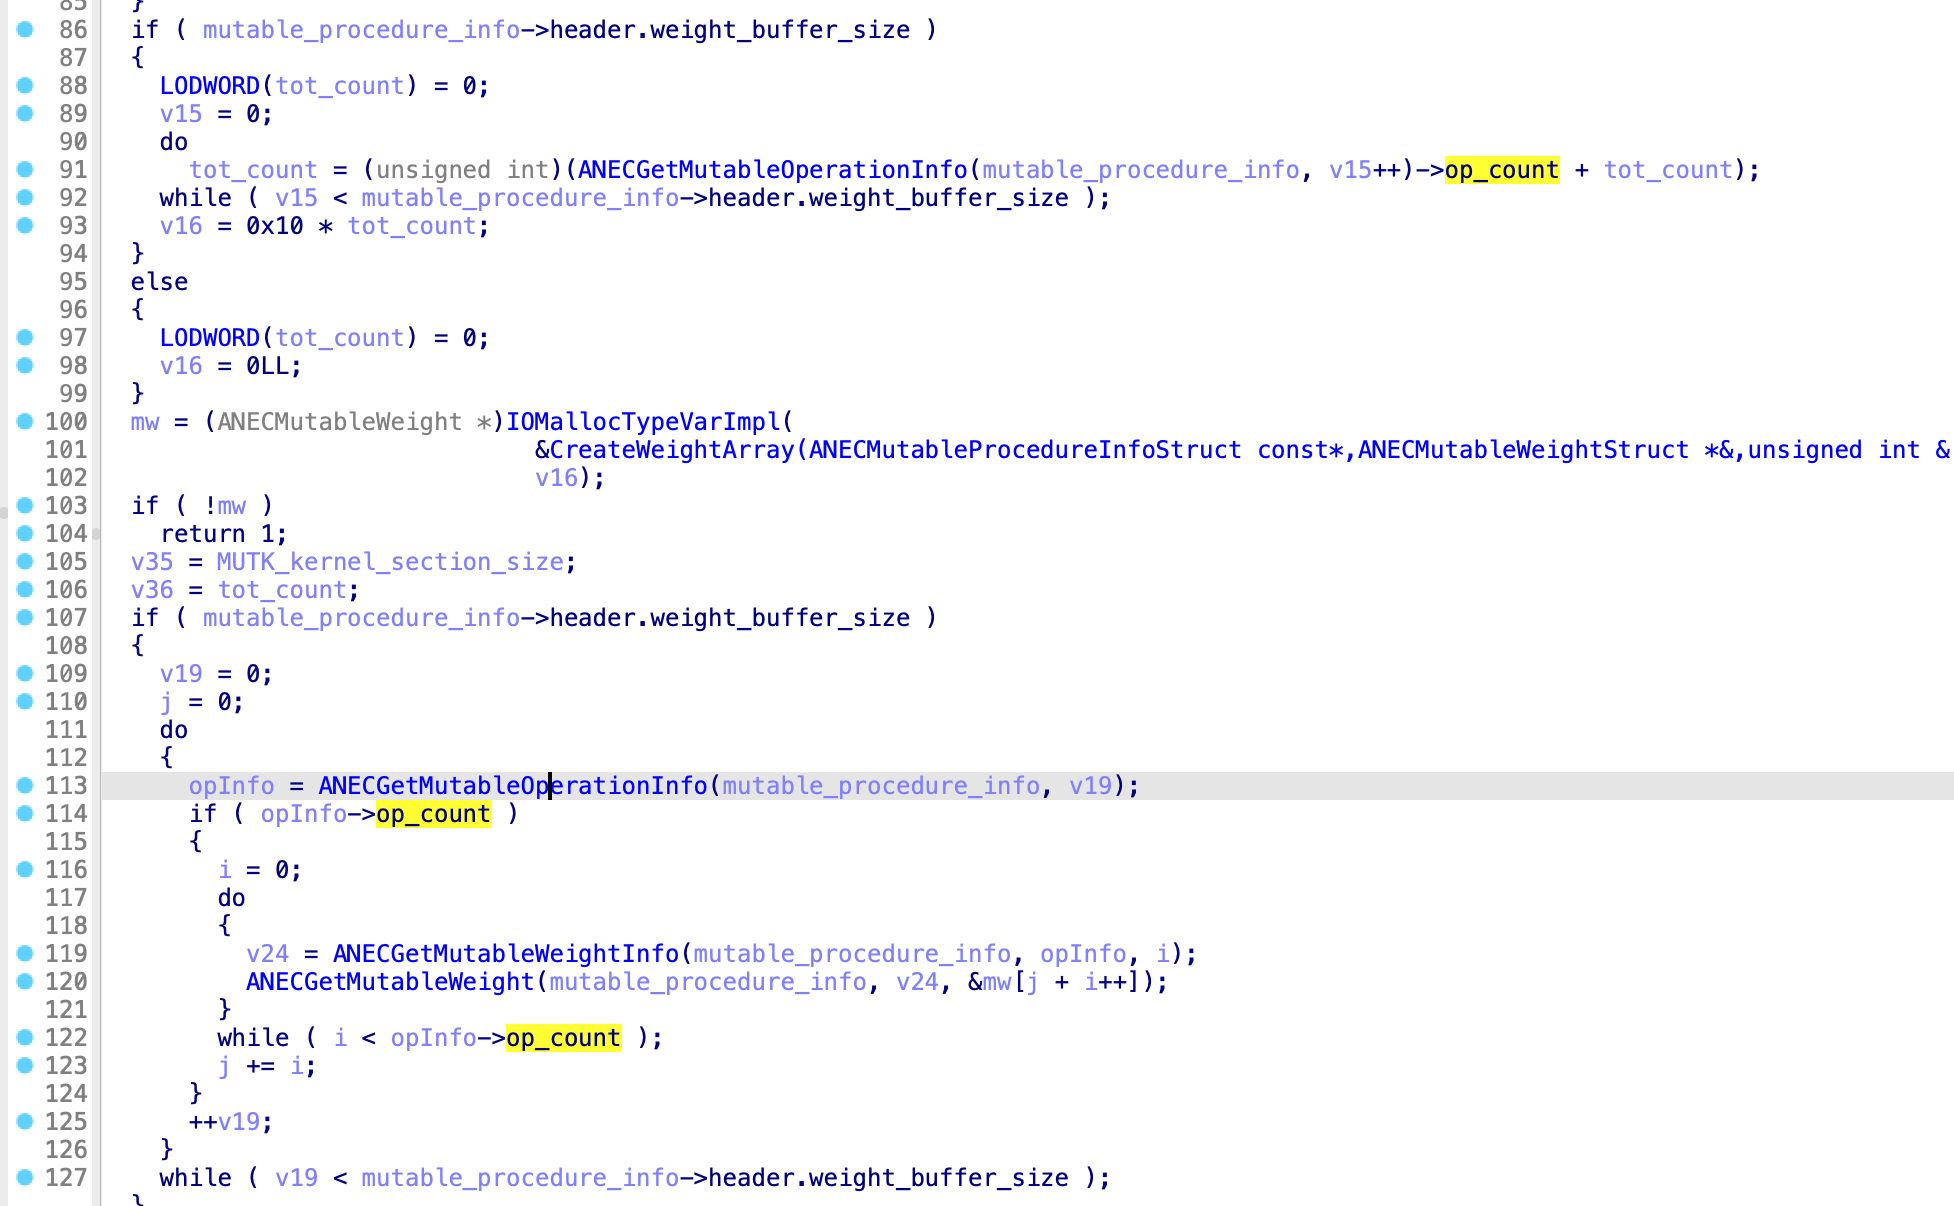 ox1111/cve-2022-32932
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…
 josephshenton/triple_fetch-kernel-creds
Attempt to steal kernelcredentials from launchd + task_t pointer (Based on: CVE-2017-7047)