frida-il2cpp-datacollector

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.

Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…

research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607

PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…

MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…

iOS Messages JPEG XL delivery-surface probe and patch-diff notes for CVE-2026-28956.

CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)

Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…

Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…

Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…

Proof-of-concept for an out-of-bounds write in XNU's vfs_attr_pack_internal (getattrlist) on iOS 26.6, demonstrating kernel heap corruption and…

Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…

CVE-2026-20687: AppleJPEGDriver startDecoder Timeout UAF — iOS/macOS kernel vulnerability leading to deferred panic (A19 Pro, iOS 26.3 RC)

Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.

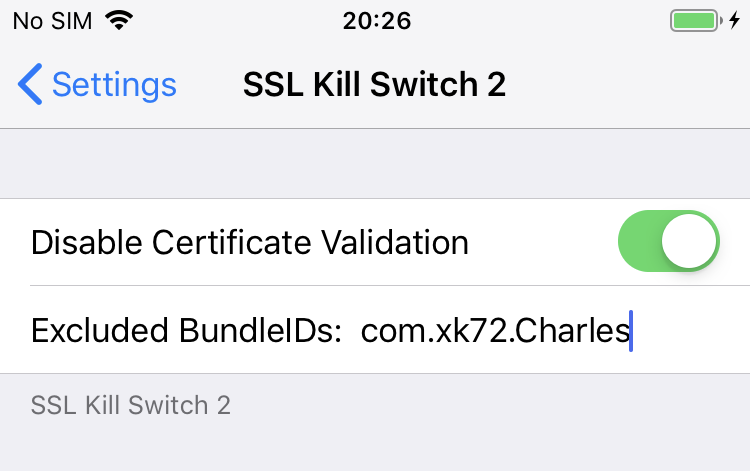
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.

Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…