moveit-transfer-cve-2023-34362

Curated vulnerability research repository with in-depth writeups, PoC scripts, and IOC detection tools for real-world security incidents like…

Curated vulnerability research repository with in-depth writeups, PoC scripts, and IOC detection tools for real-world security incidents like…

PoC & IOCs for critical HSM authentication bypass (CVE-2025-99999). Threat intelligence for financial sector.

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

CVE-2026-48907 – Joomla JCE Unauthenticated Remote Code Execution (RCE)

🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…

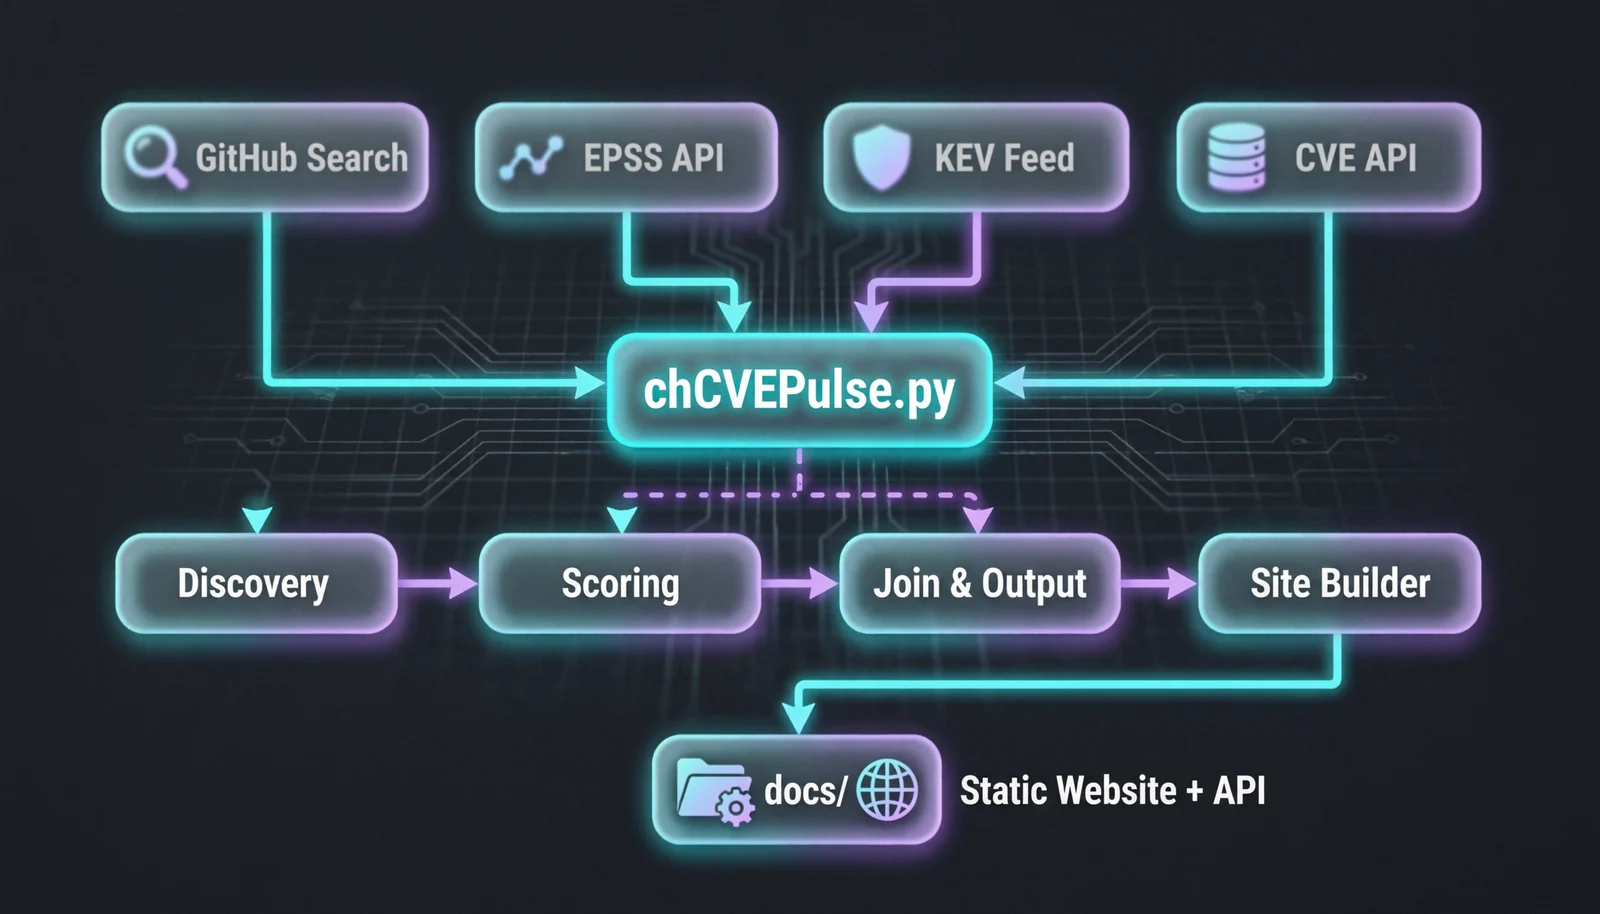
Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence

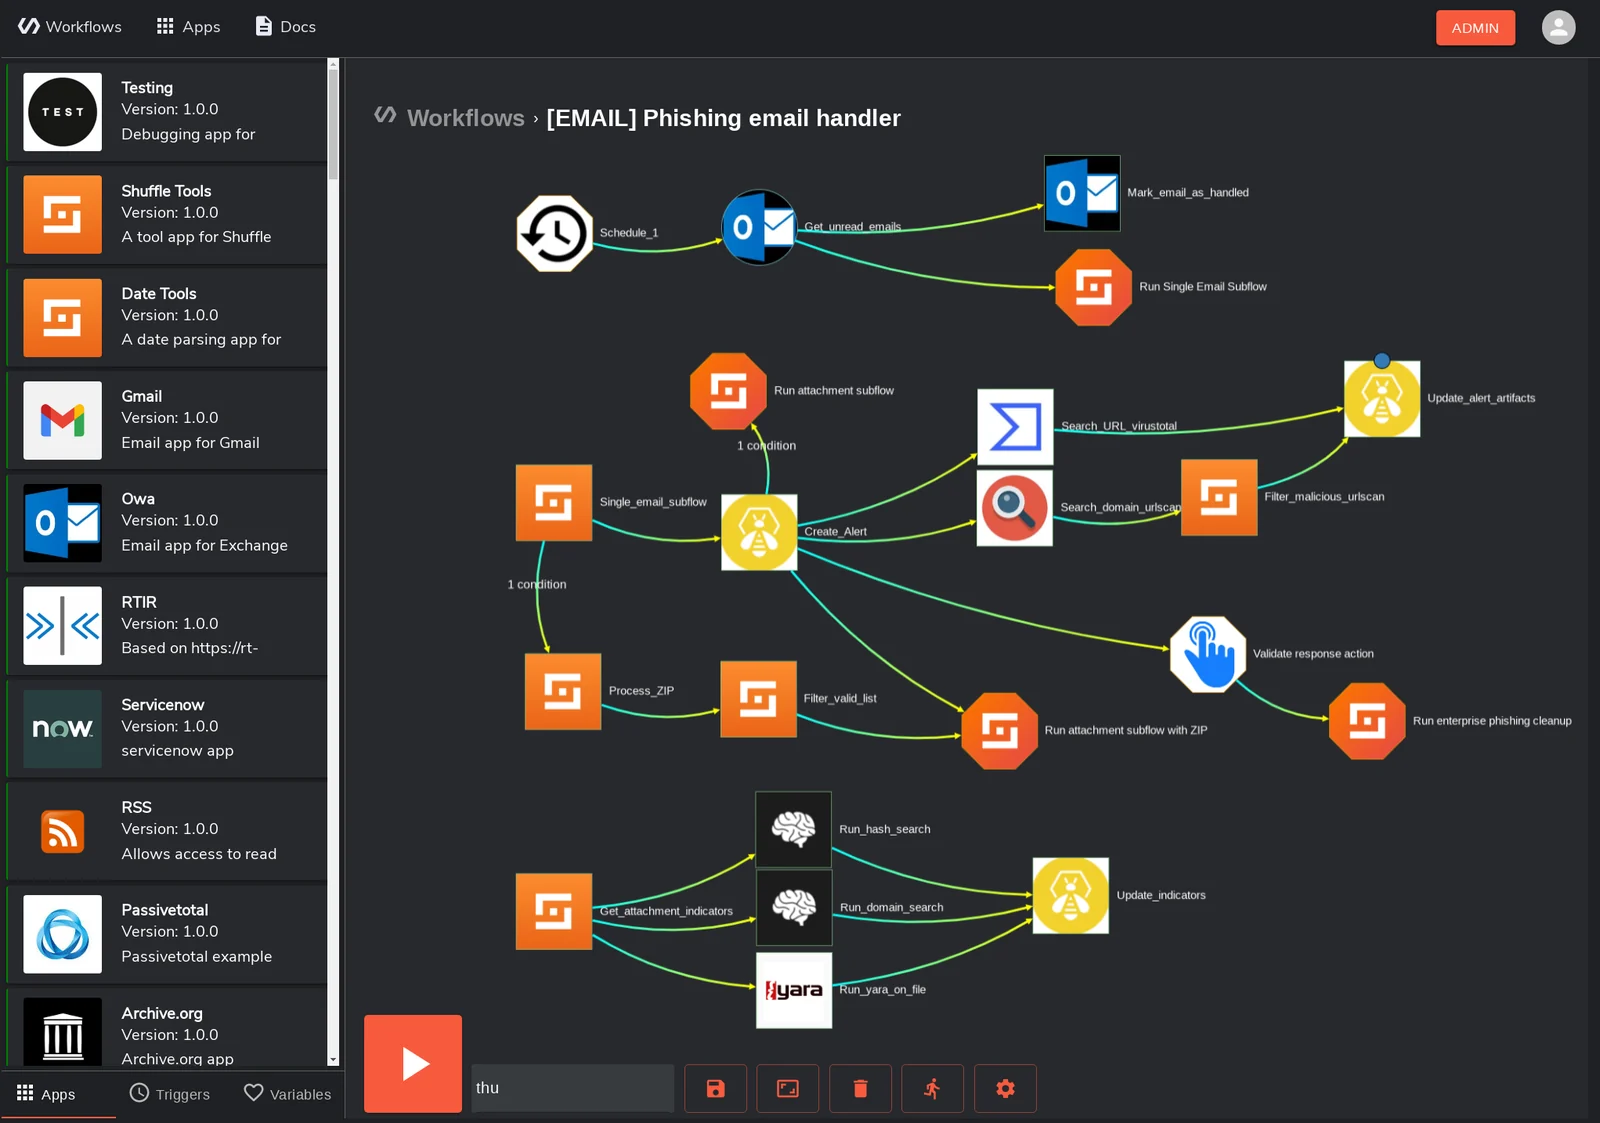
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…

A curated collection of DFIR skills and workflows for InfoSec practitioners.

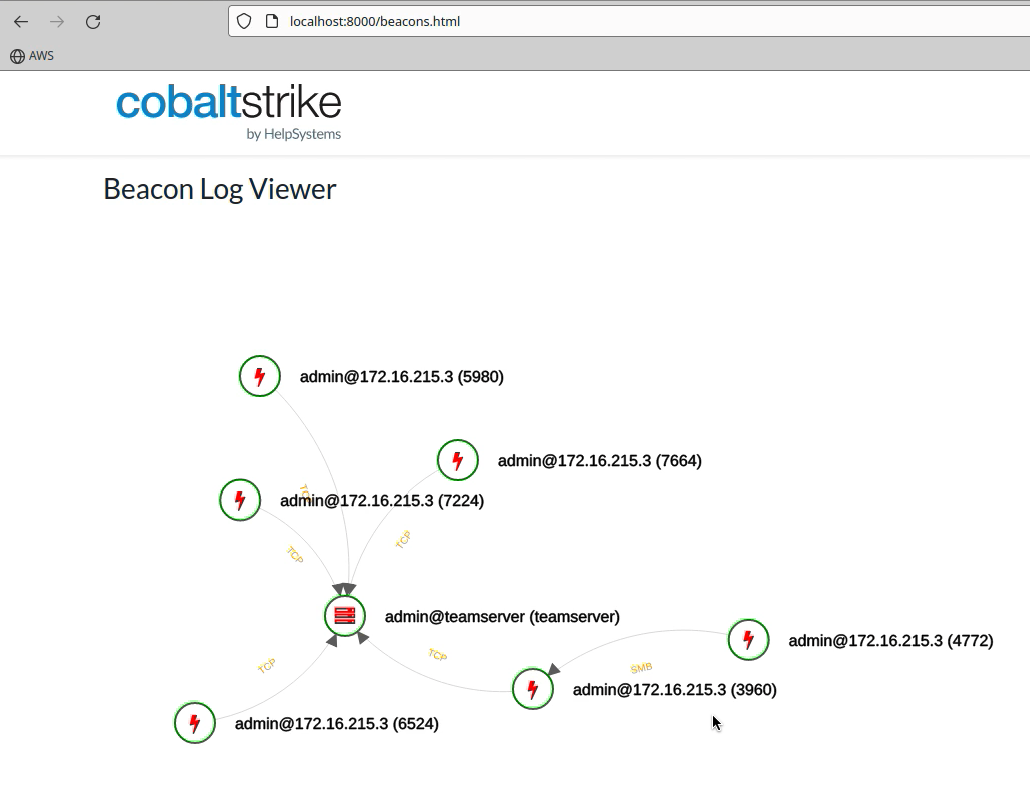
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…

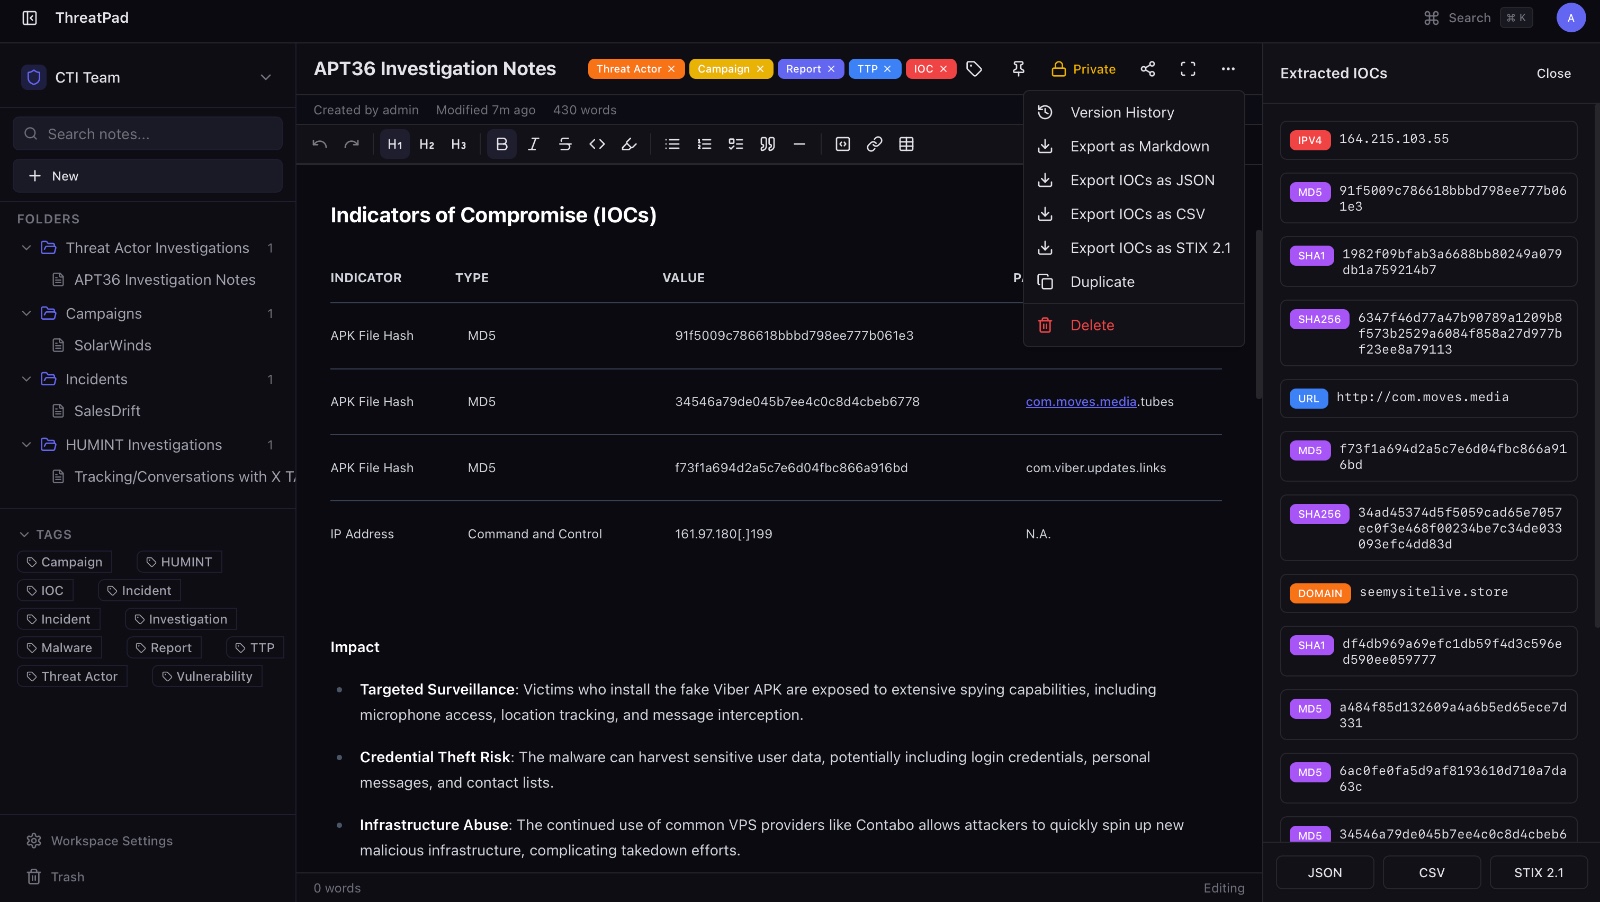
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…