
expel-intel
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
information-gatheringioc-managementosint+2
6
expel-io/expel-intelThis is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 niklasmato/fortileak-01-2025-be
This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…
 00gxd14g/misp-extractor
Extracts selected MISP attributes, including IP addresses, URLs, and hashes, into reusable output files.
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
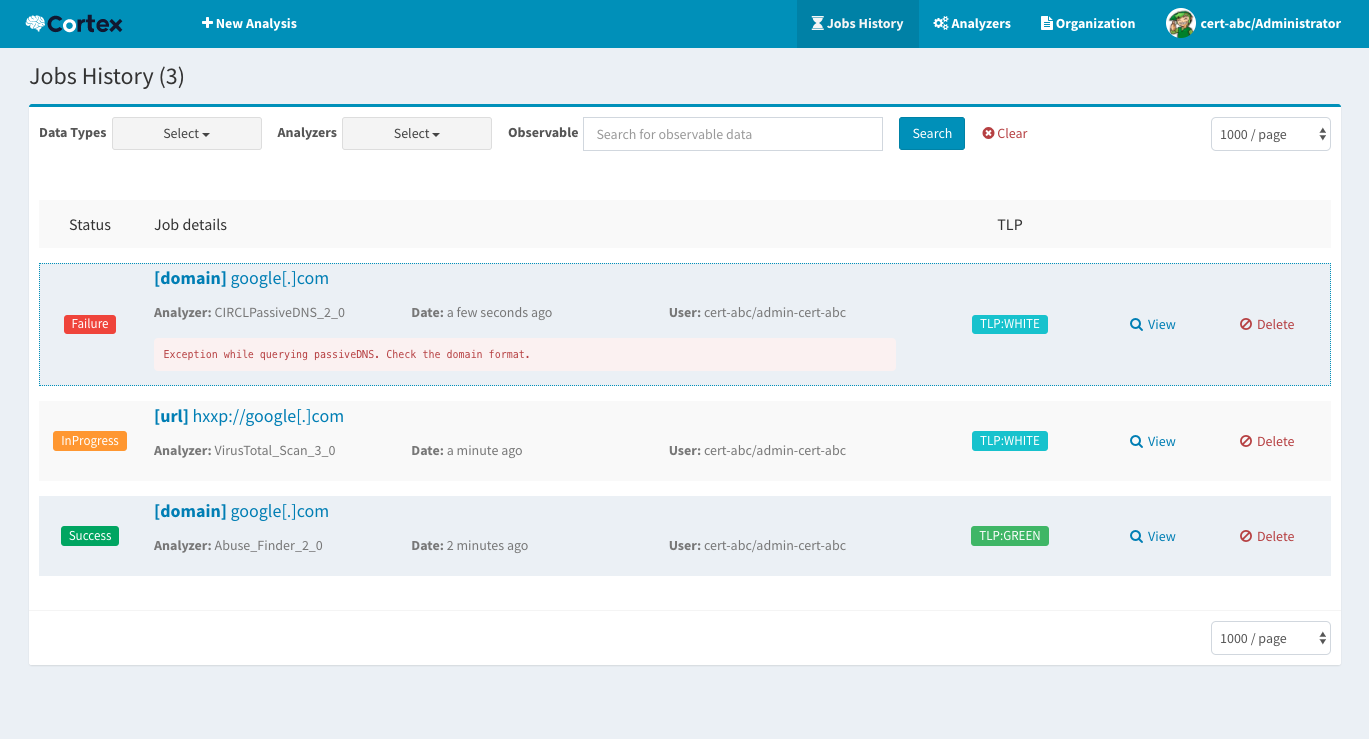 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 amnestytech/investigations
Indicators of Compromise from Amnesty International's cyber investigations
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…
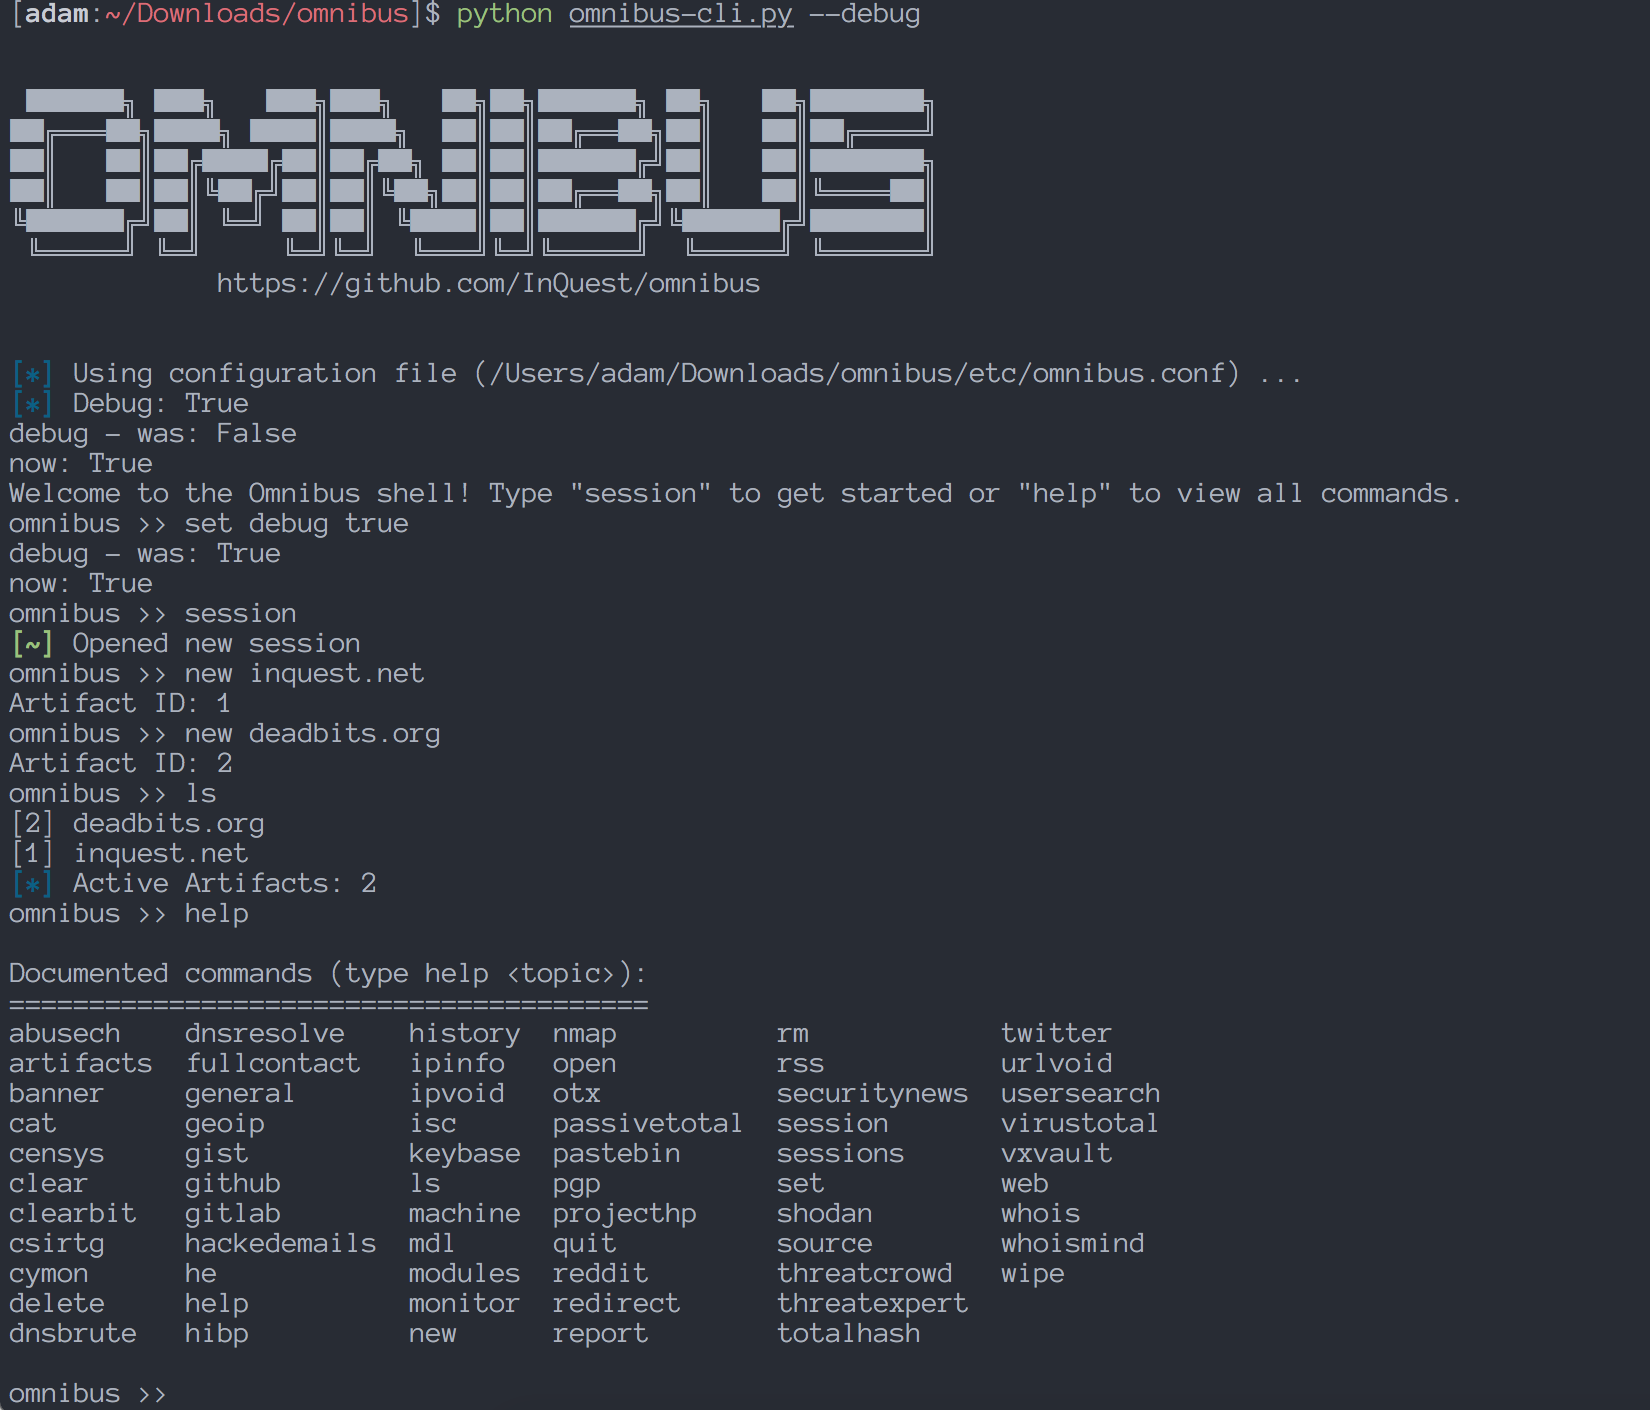
 emergingthreats/threatresearch
Proofpoint - Emerging Threats - Threat Research tools + publicly shared intel and documentation
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
 nomi-sec/nvd-database
📕NVD Database
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 silascutler/malpipe
Malware/IOC ingestion and processing engine
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.