
CVE-2026-0257
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
authenticationincident-responseinformation-gathering+6
1
grayxploit/cve-2026-0257Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
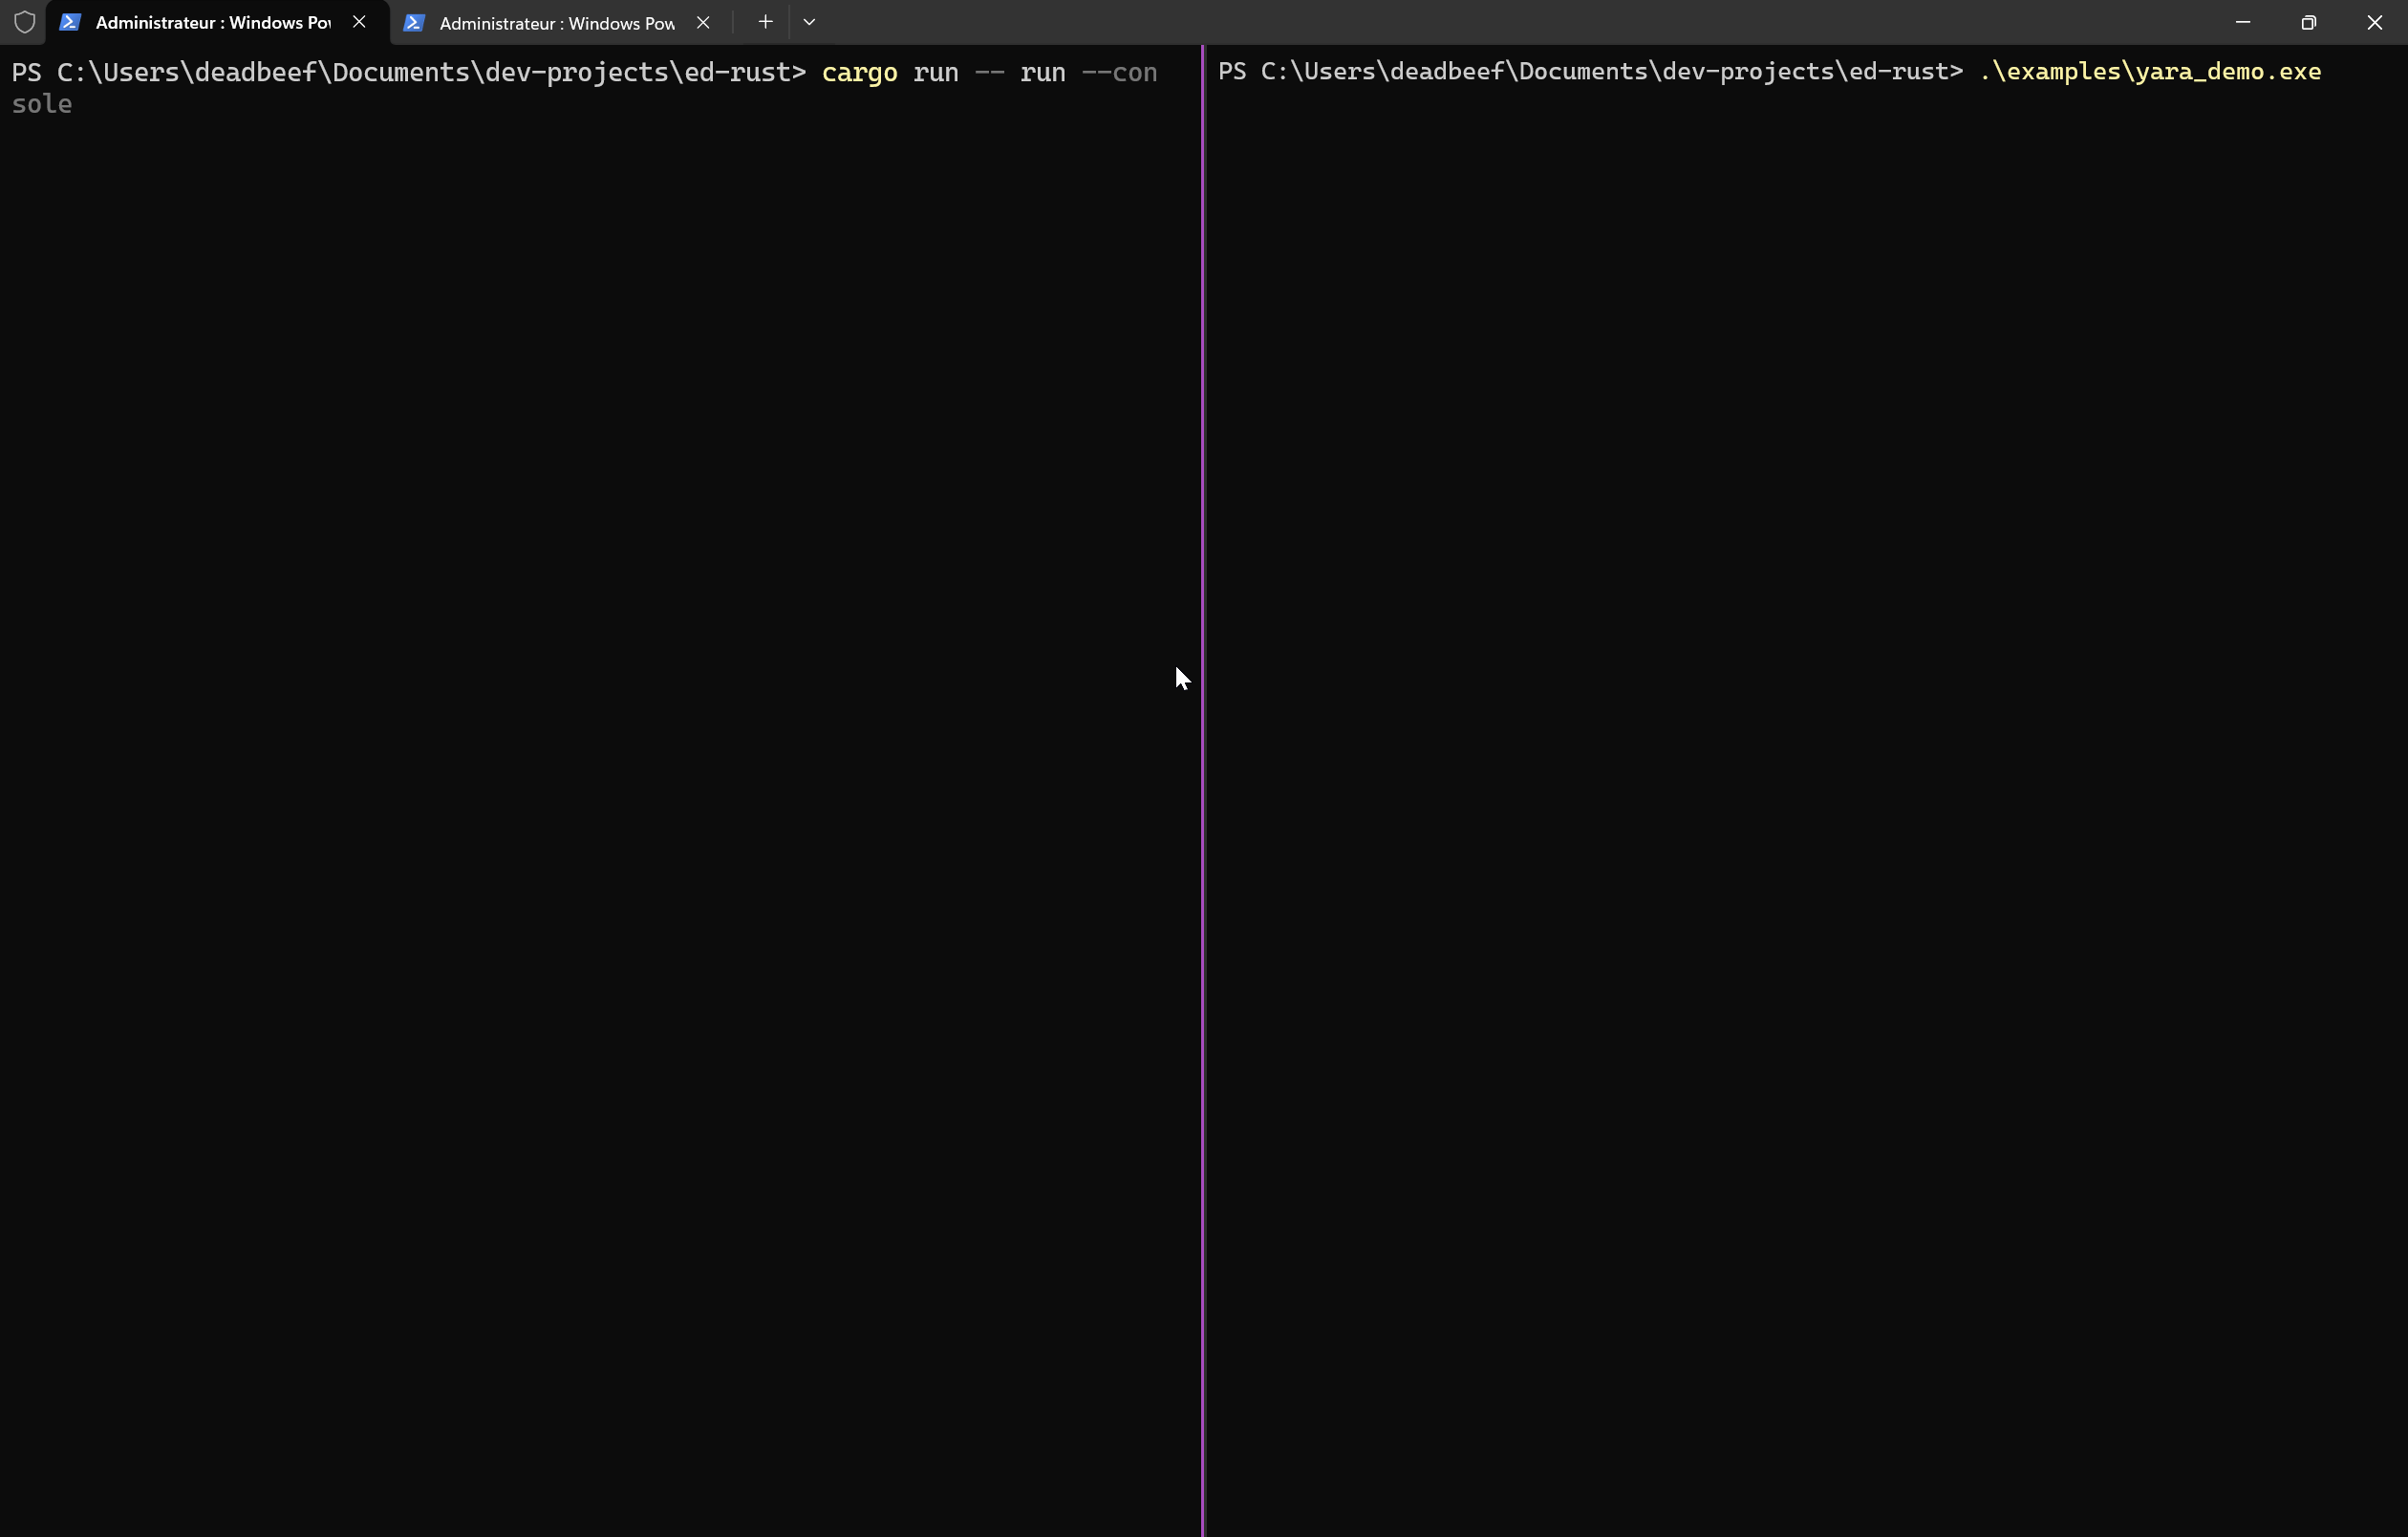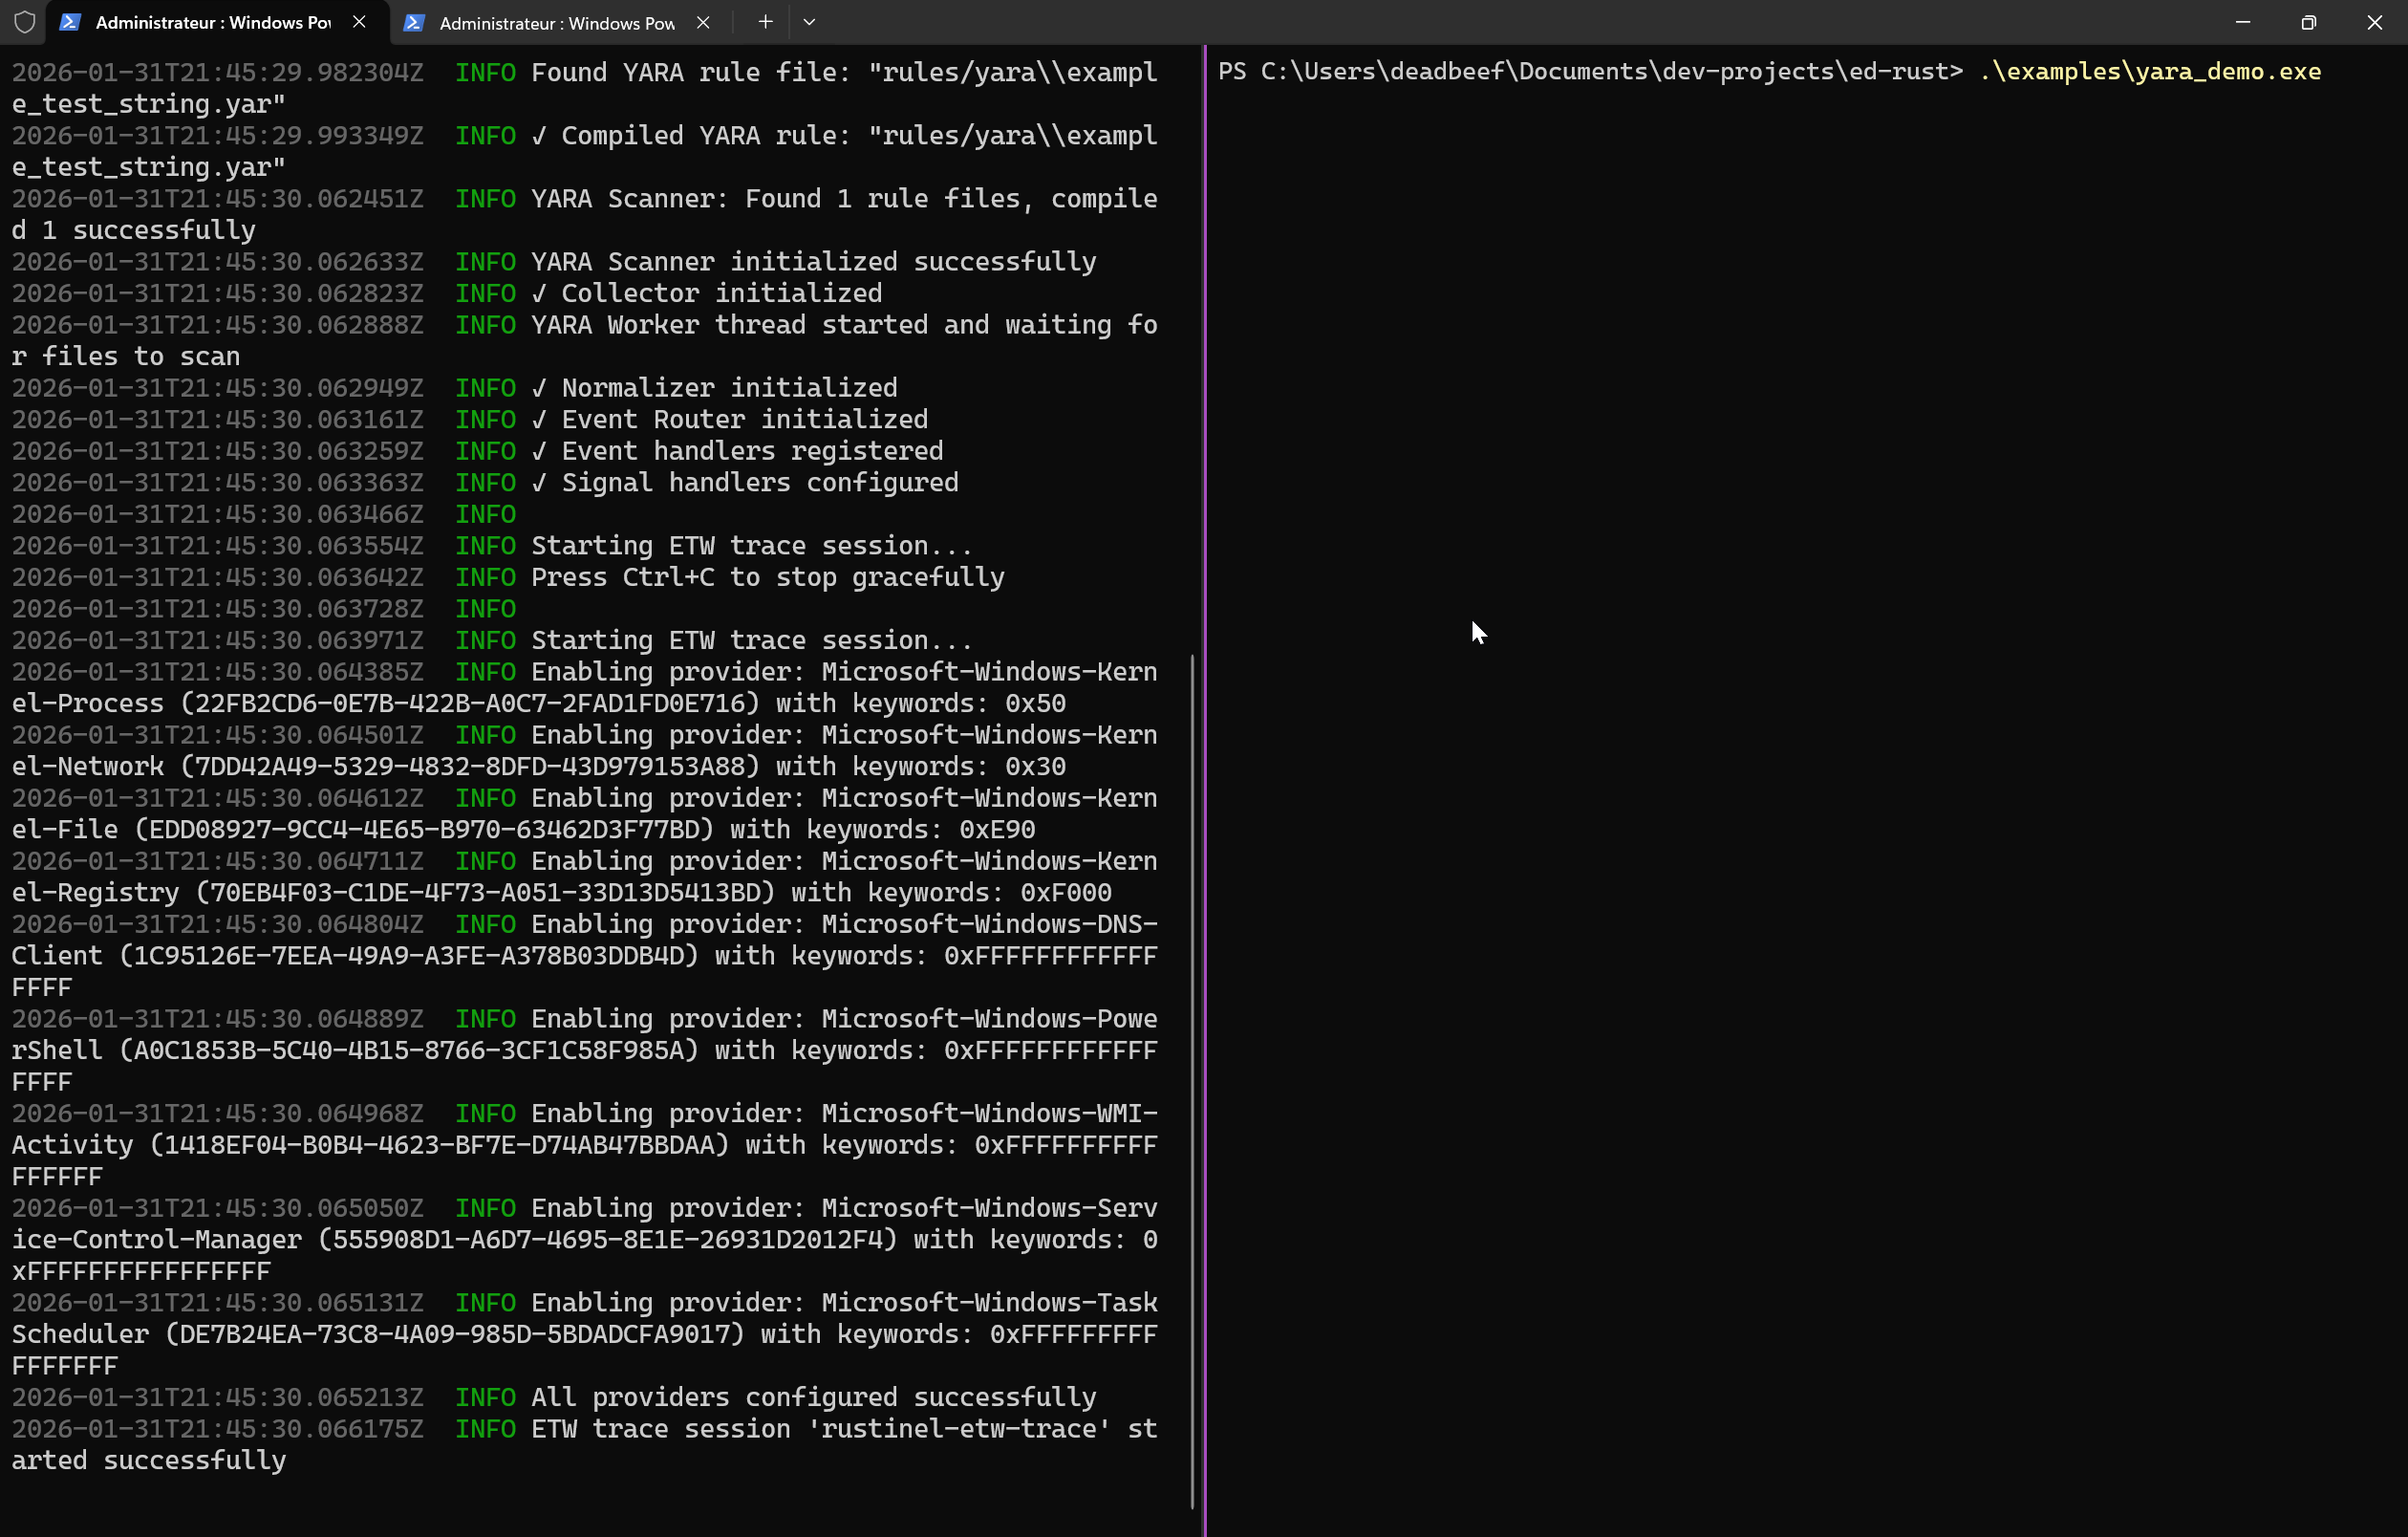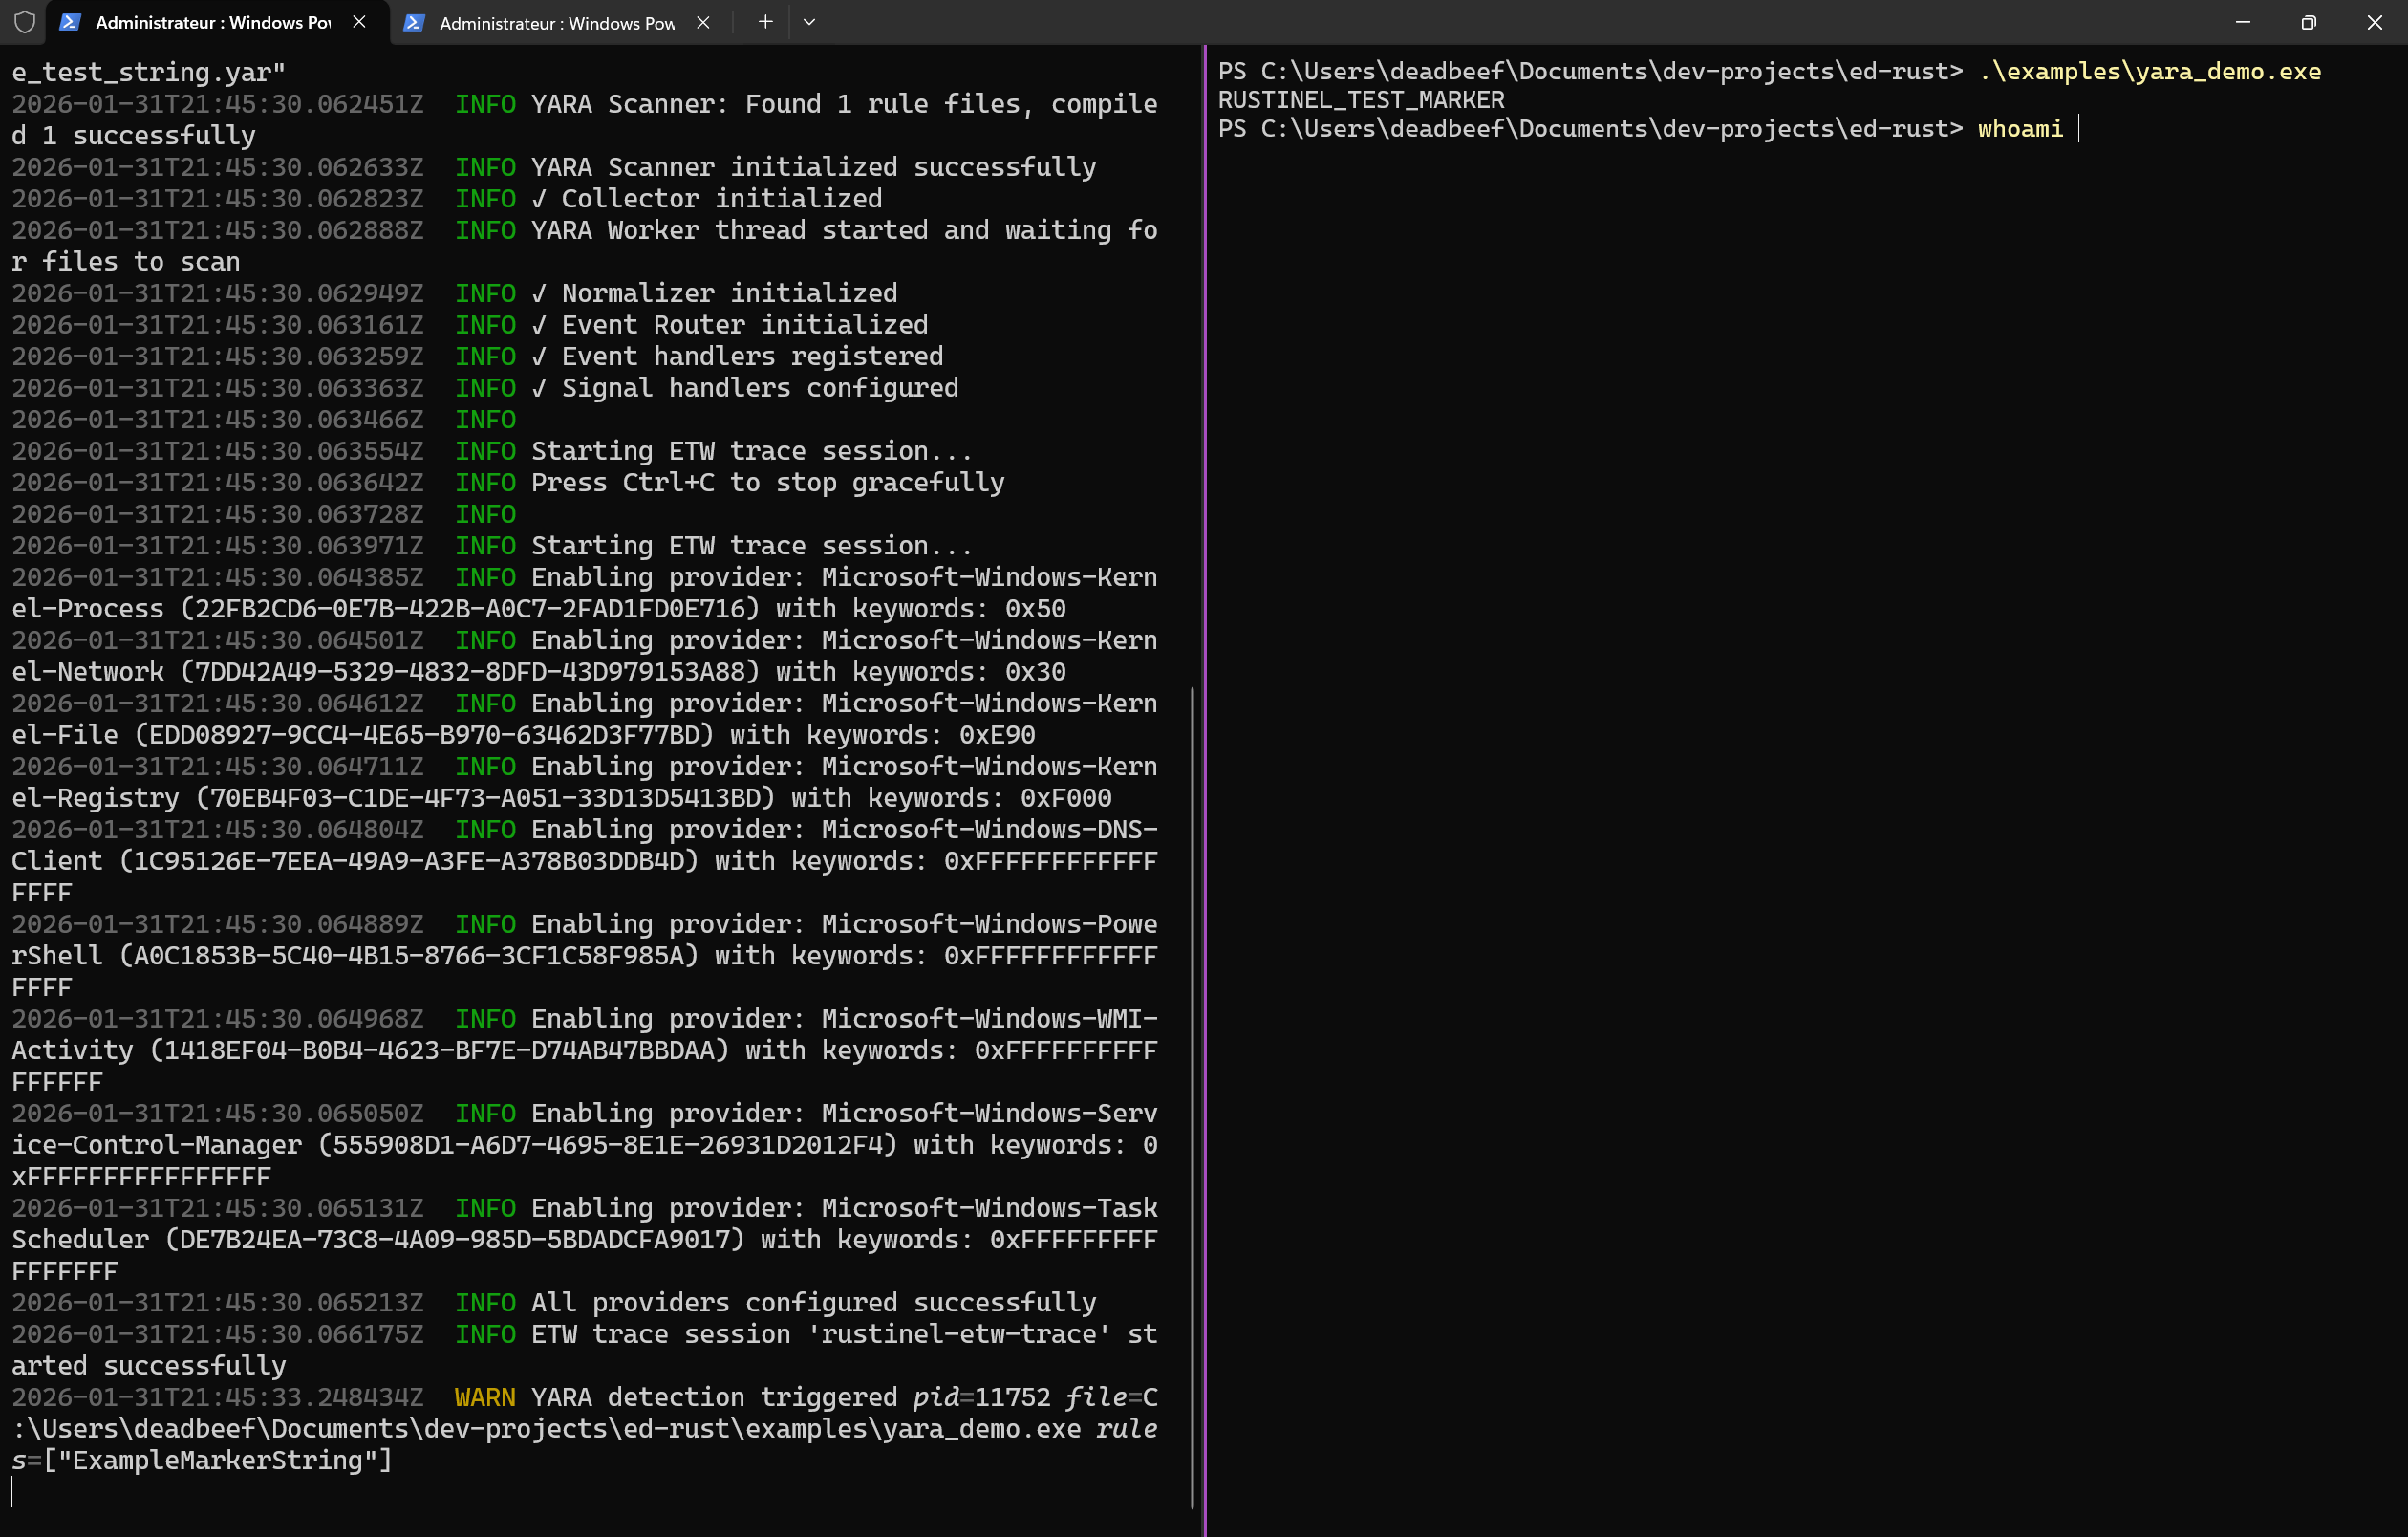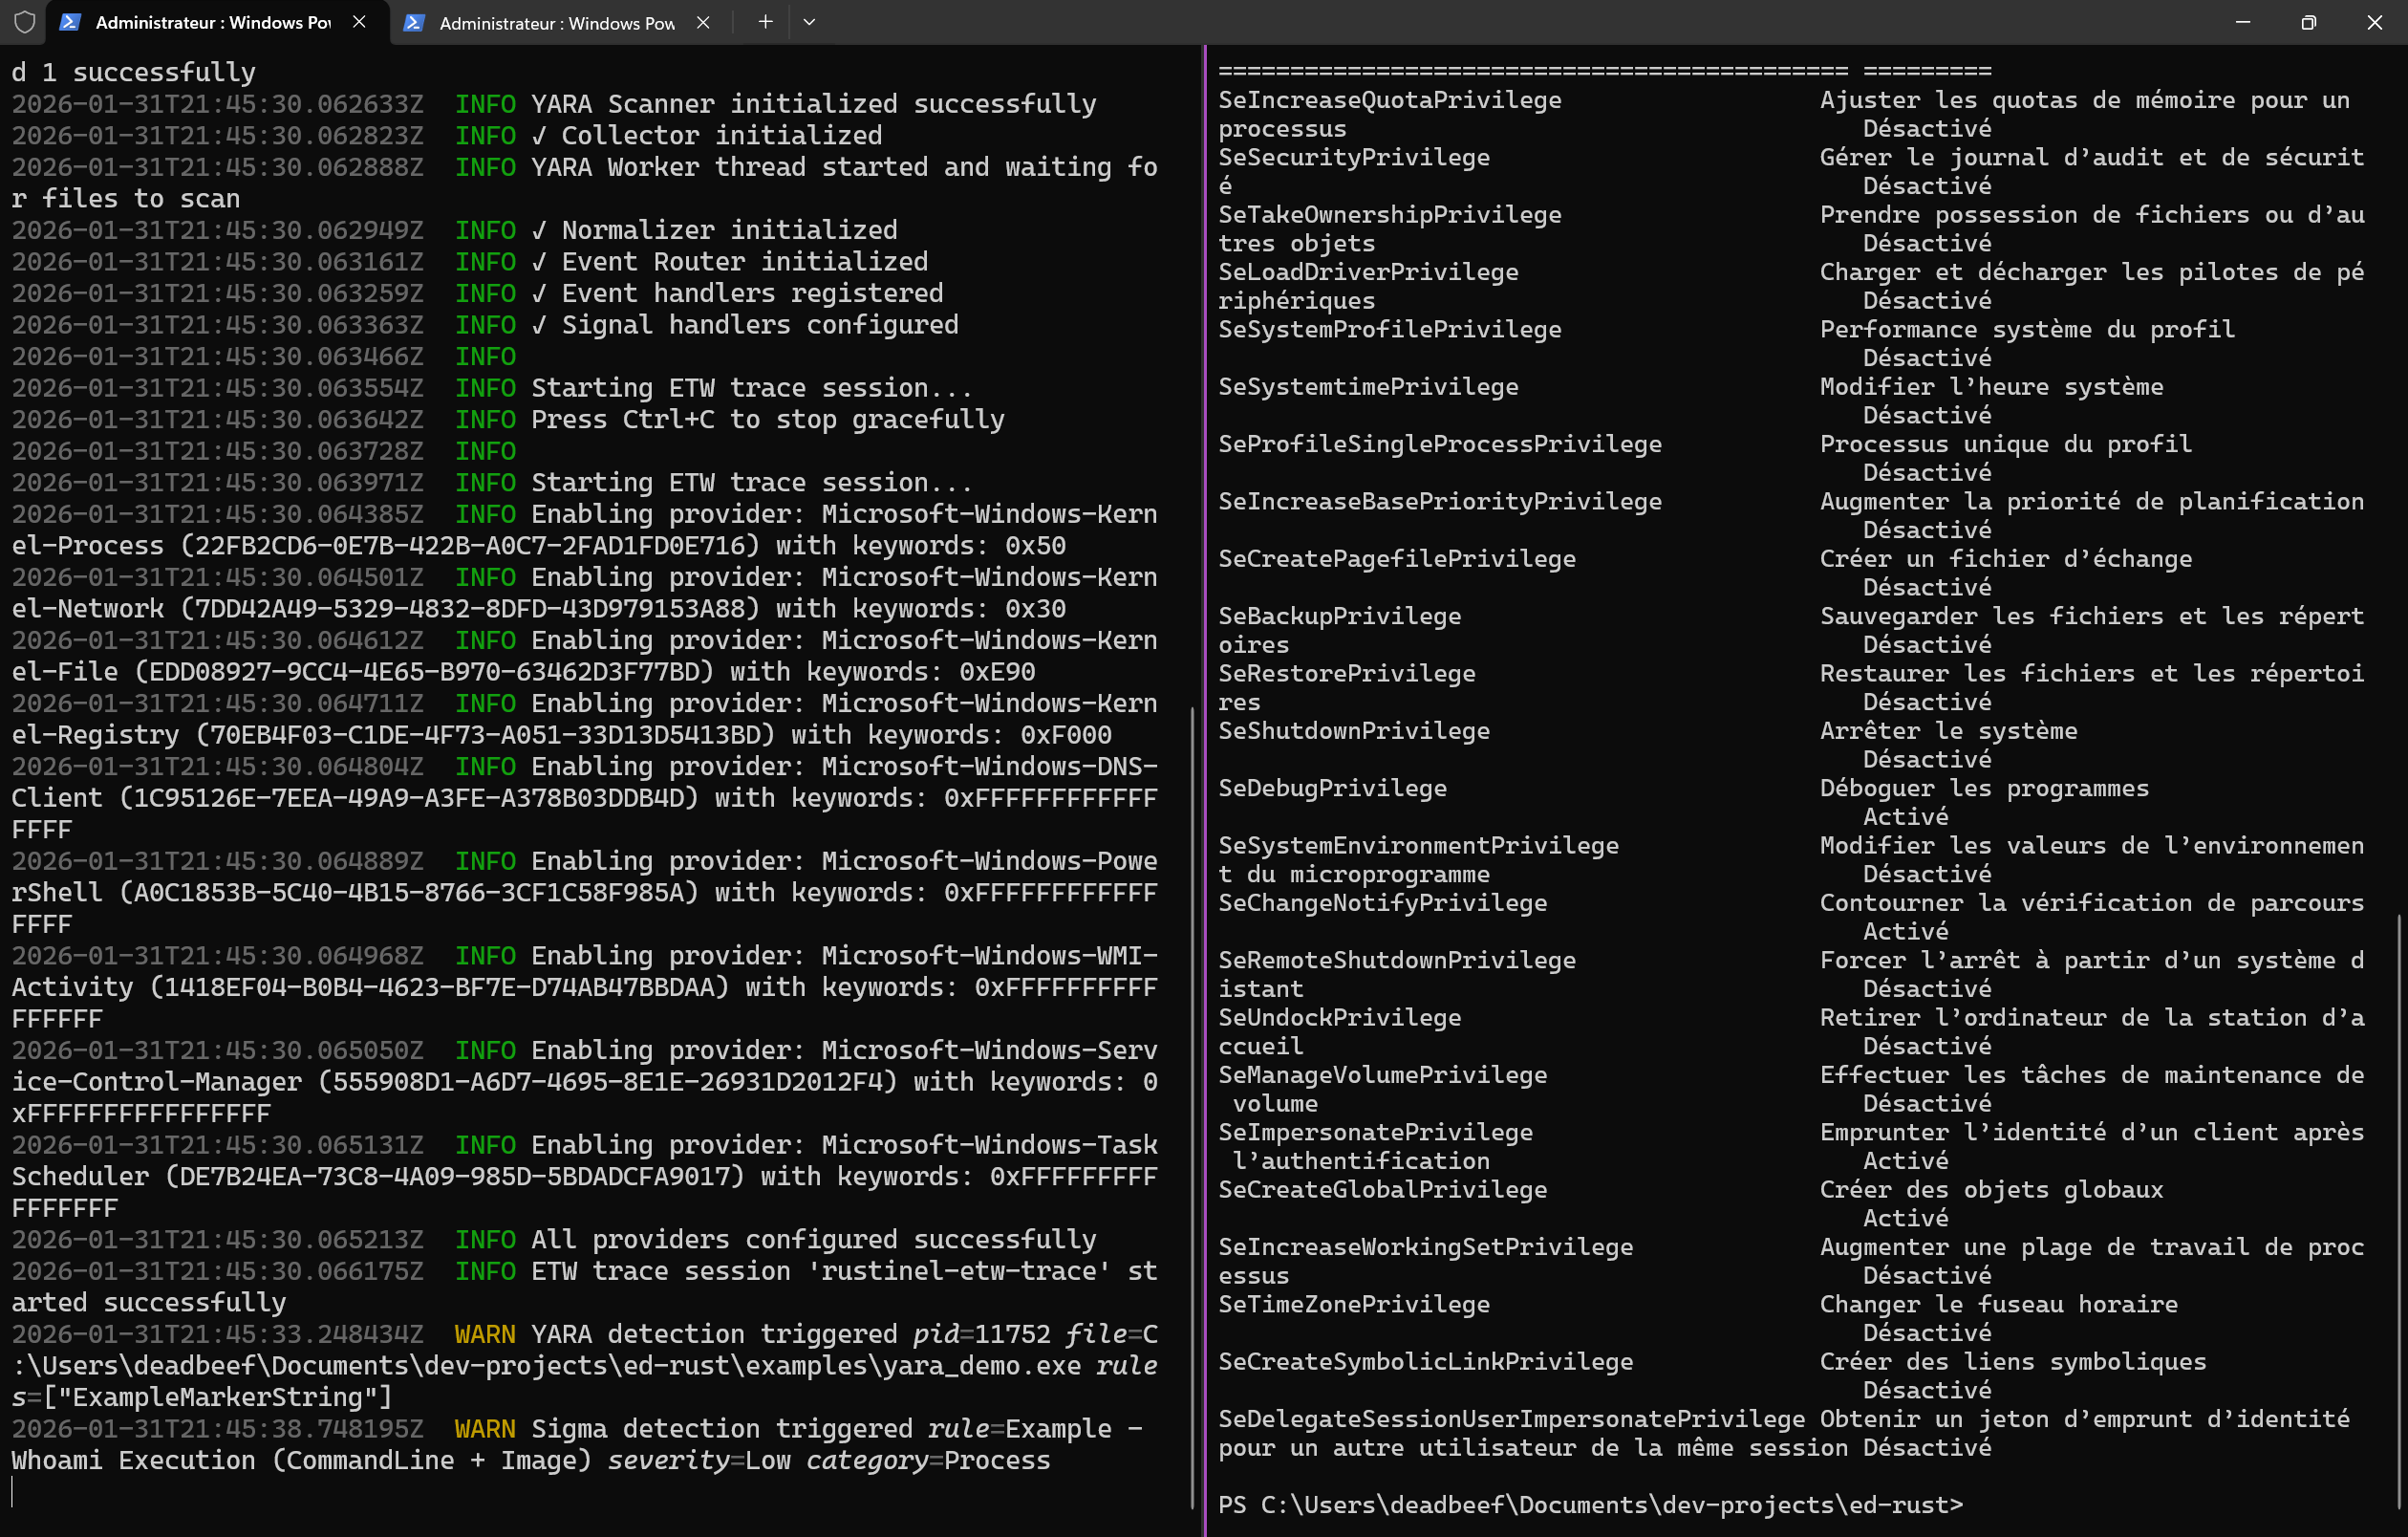 karib0u/rustinel
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 ma1am/cve-2022-26134-exploit-detection
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 santosomar/log4j-ioc-detector
A Simple Log4j Indicator of Compromise Linux Detector
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 lukeslp/redtail-ioc
IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…