CVE-2021-1675_CarbonBlack_HuntingQuery

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…

CVE-2023-34362-IOCs. More information on Deep Instinct's blog site.

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…

Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…

This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.

KrustyLoader Analysis

Public IoCs about log4j CVE-2021-44228

HexaLocker ransomware analysis

Honeypot for CVE-2025-53770 aka ToolShell

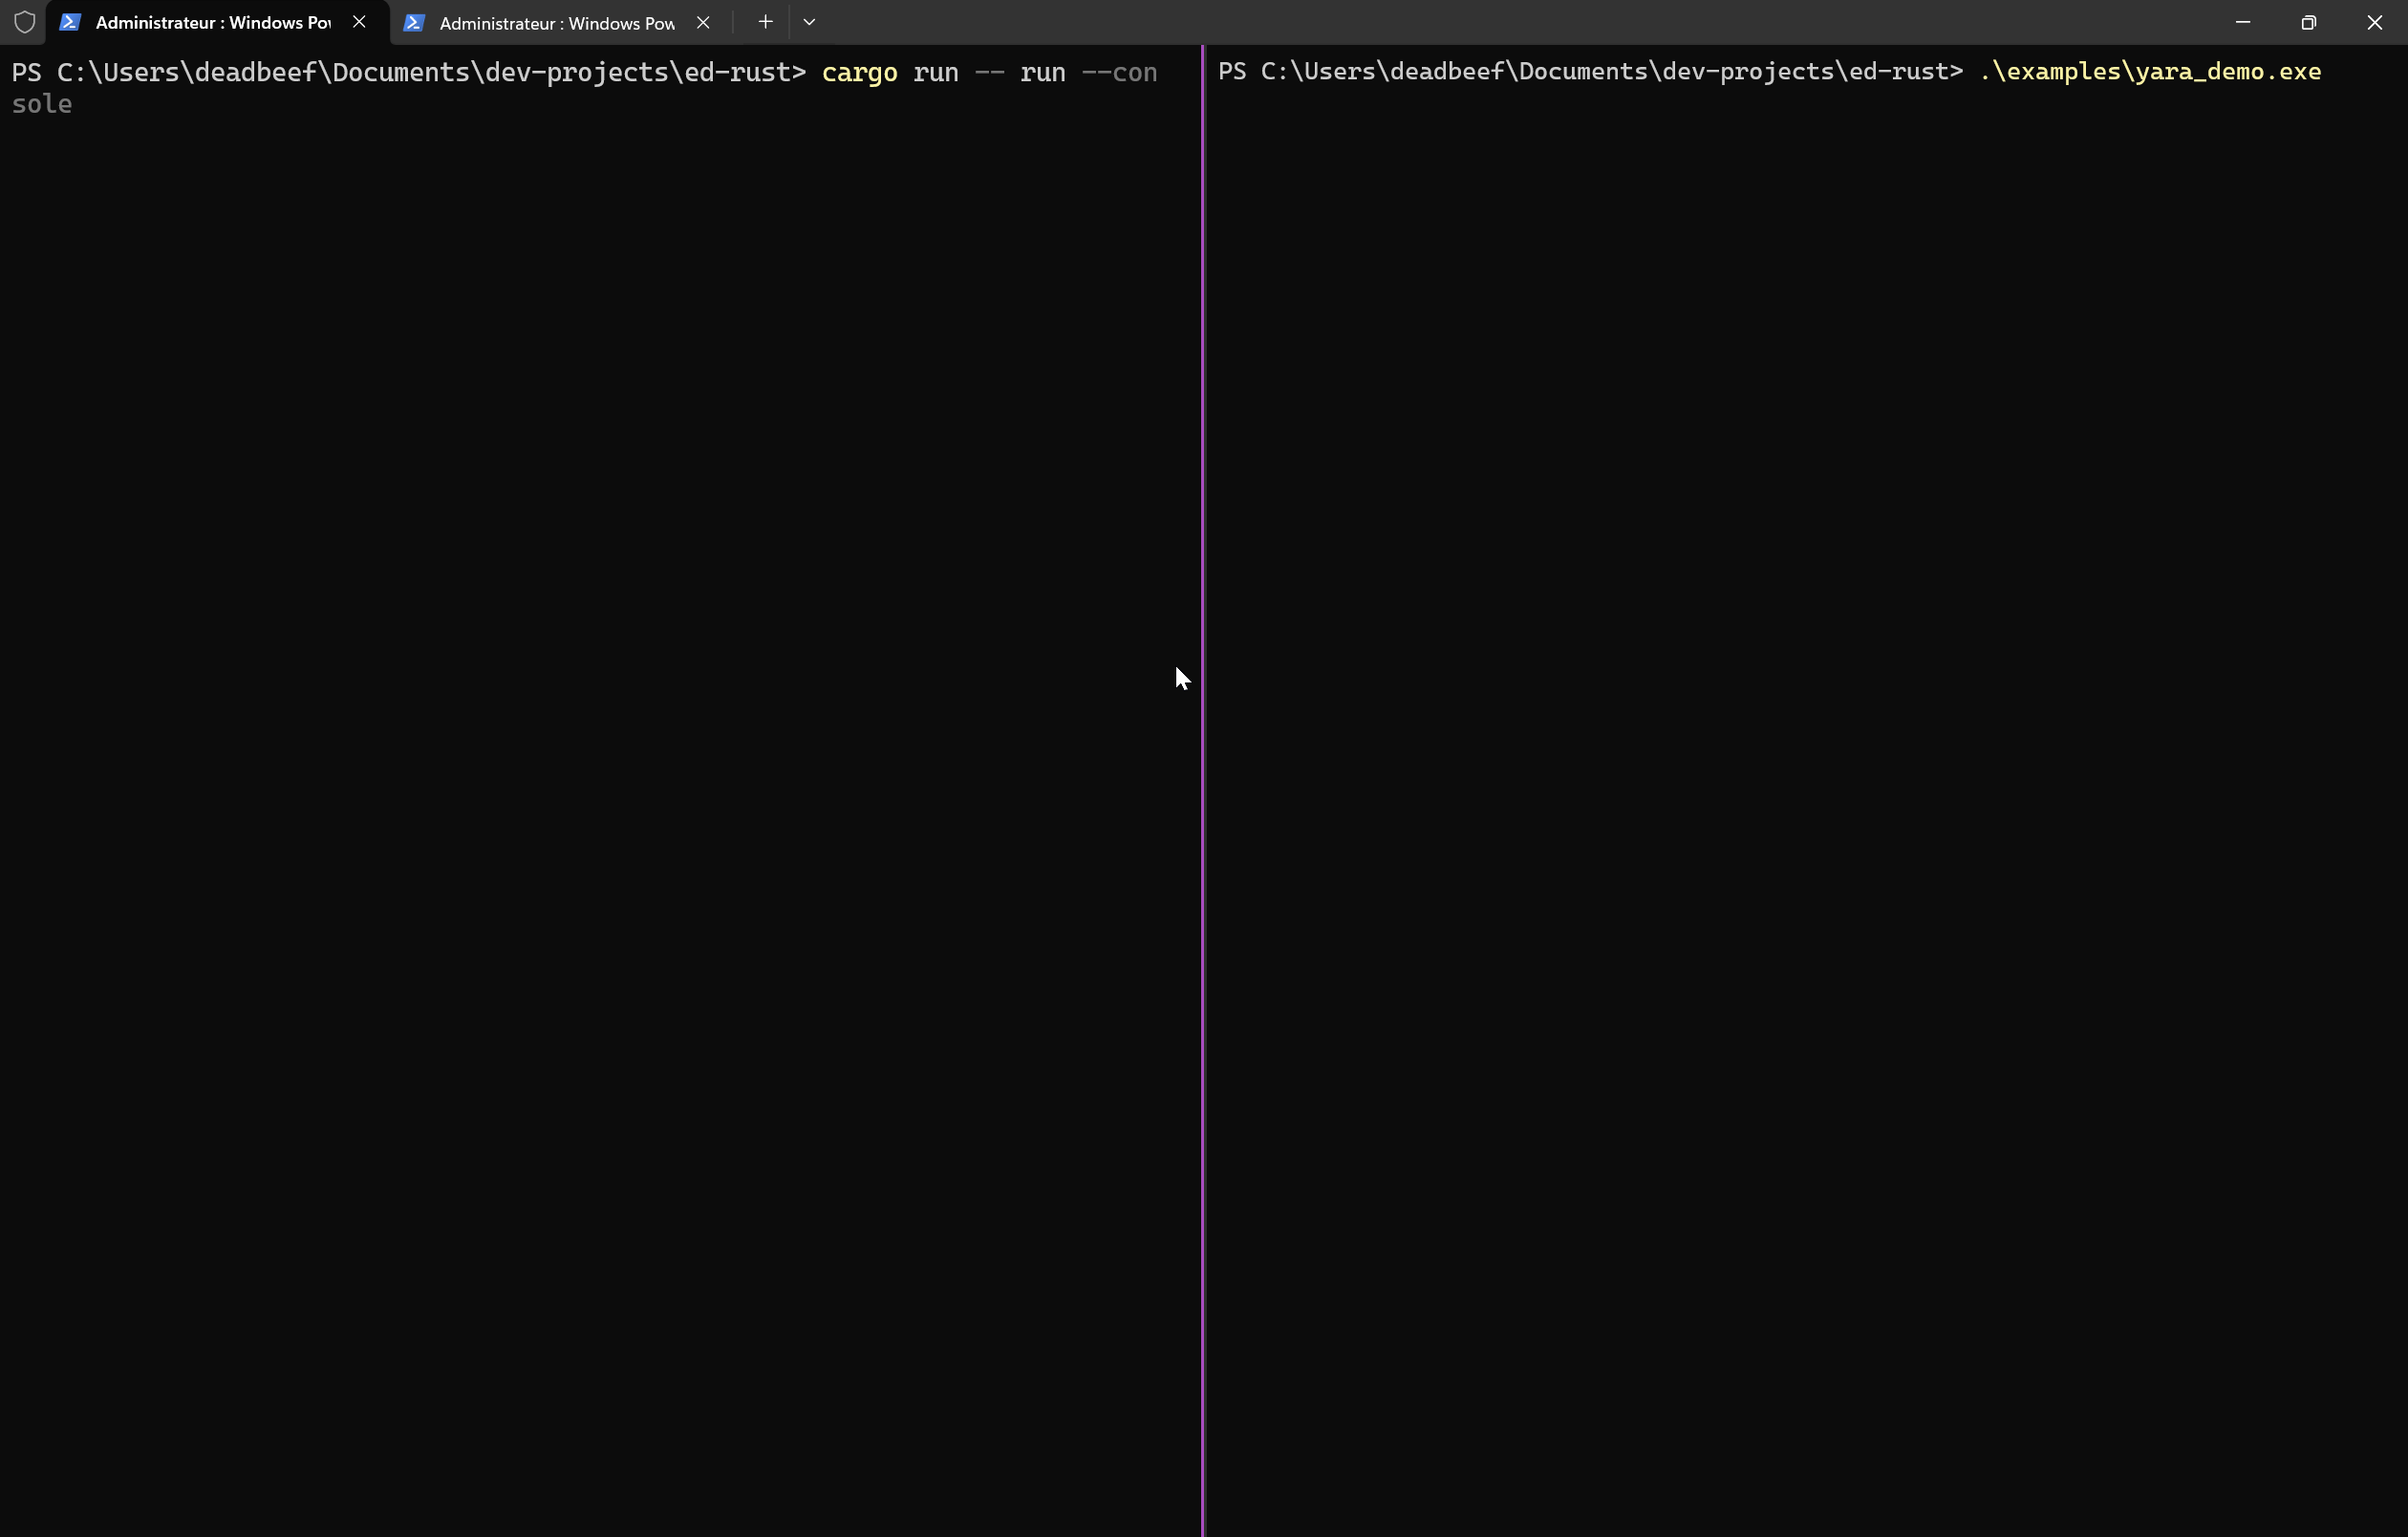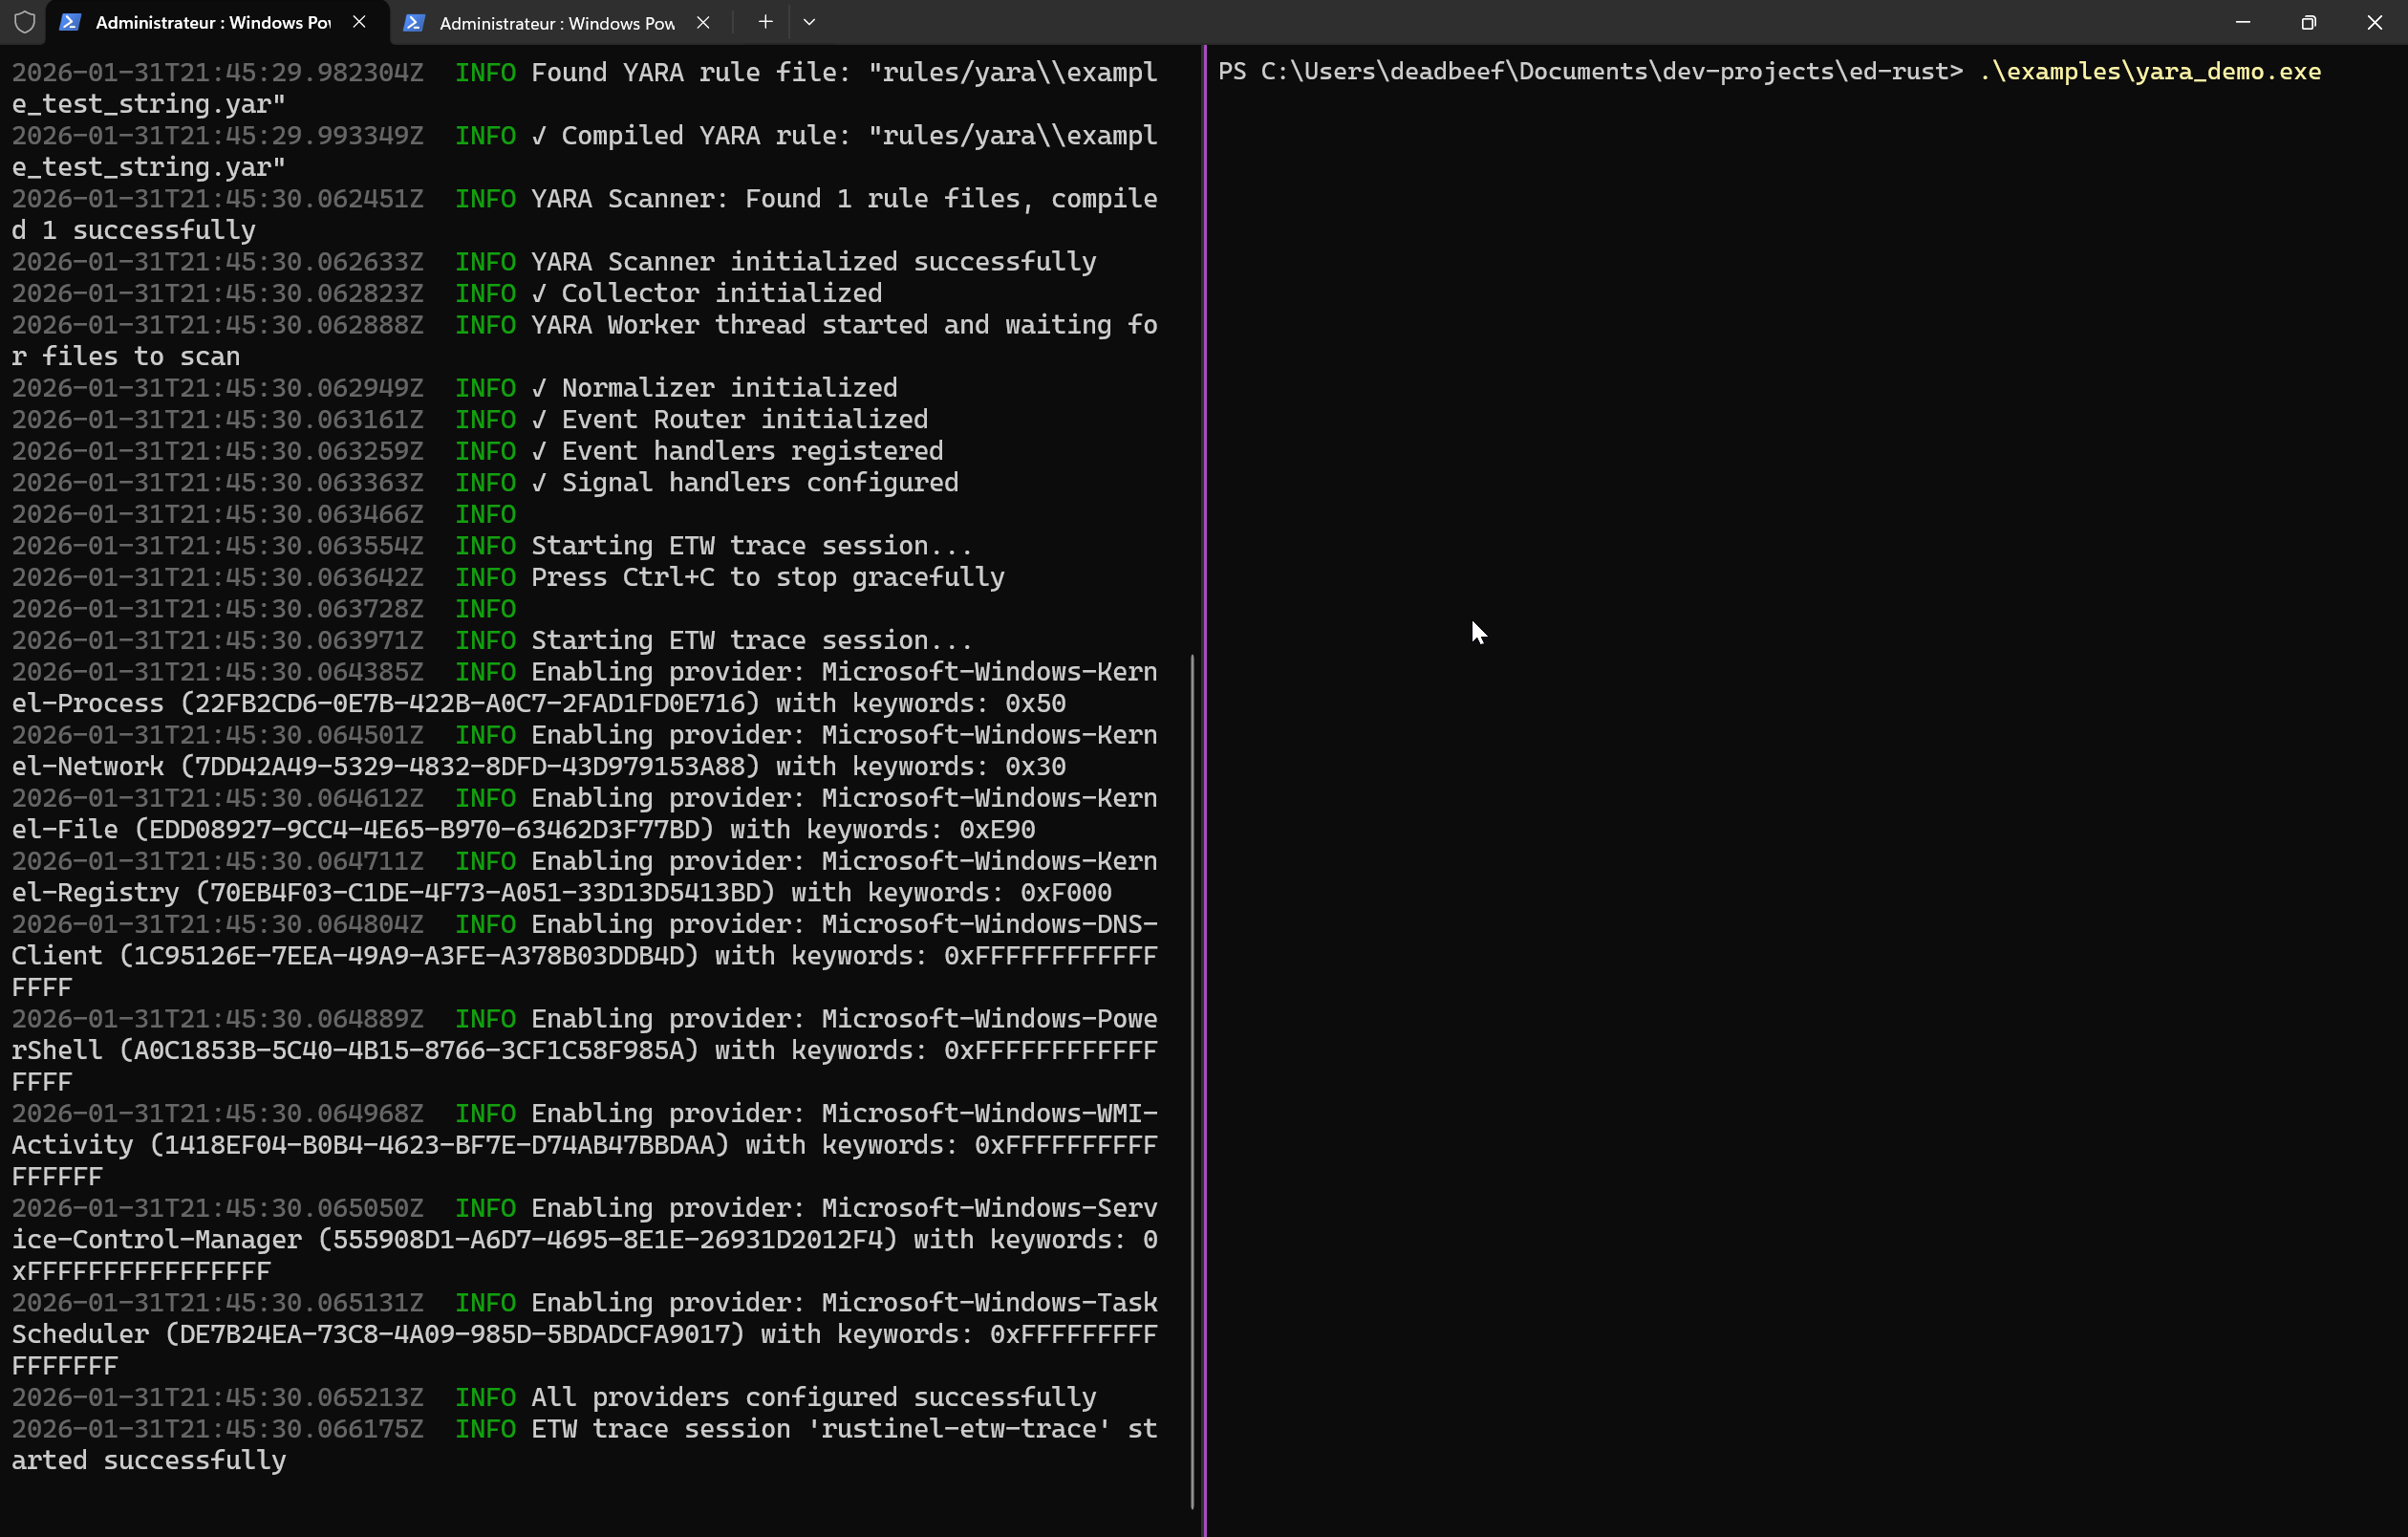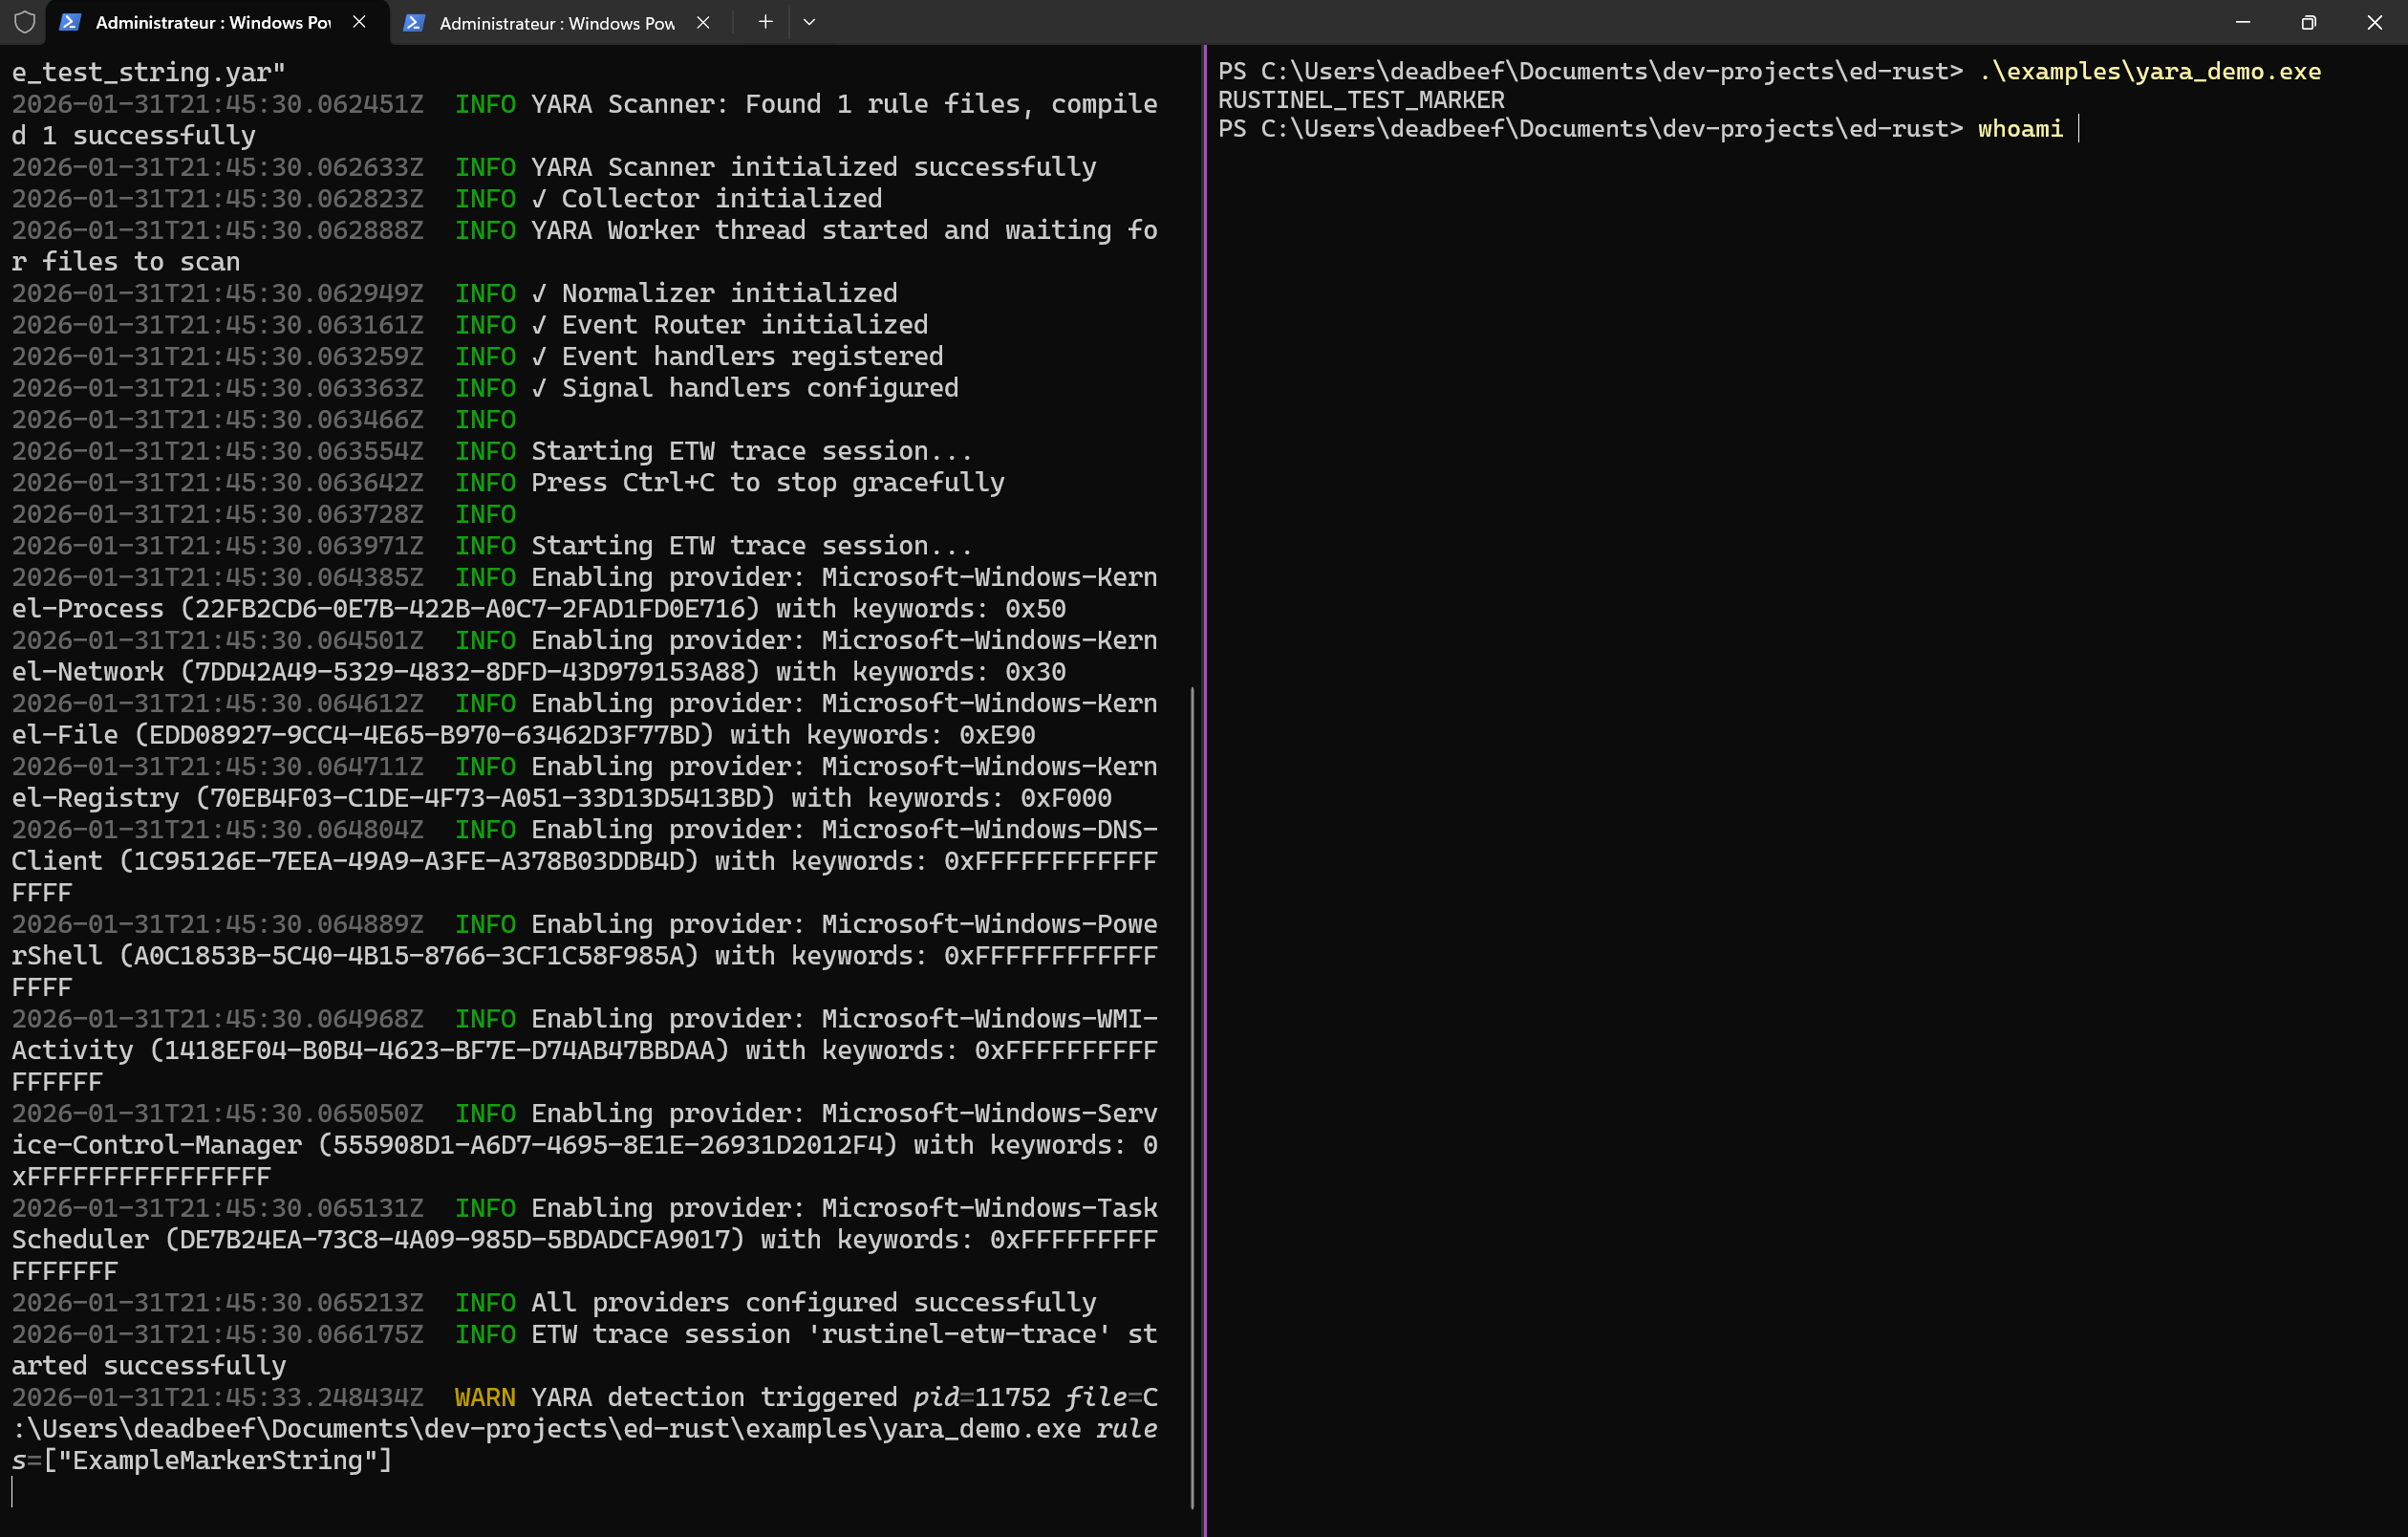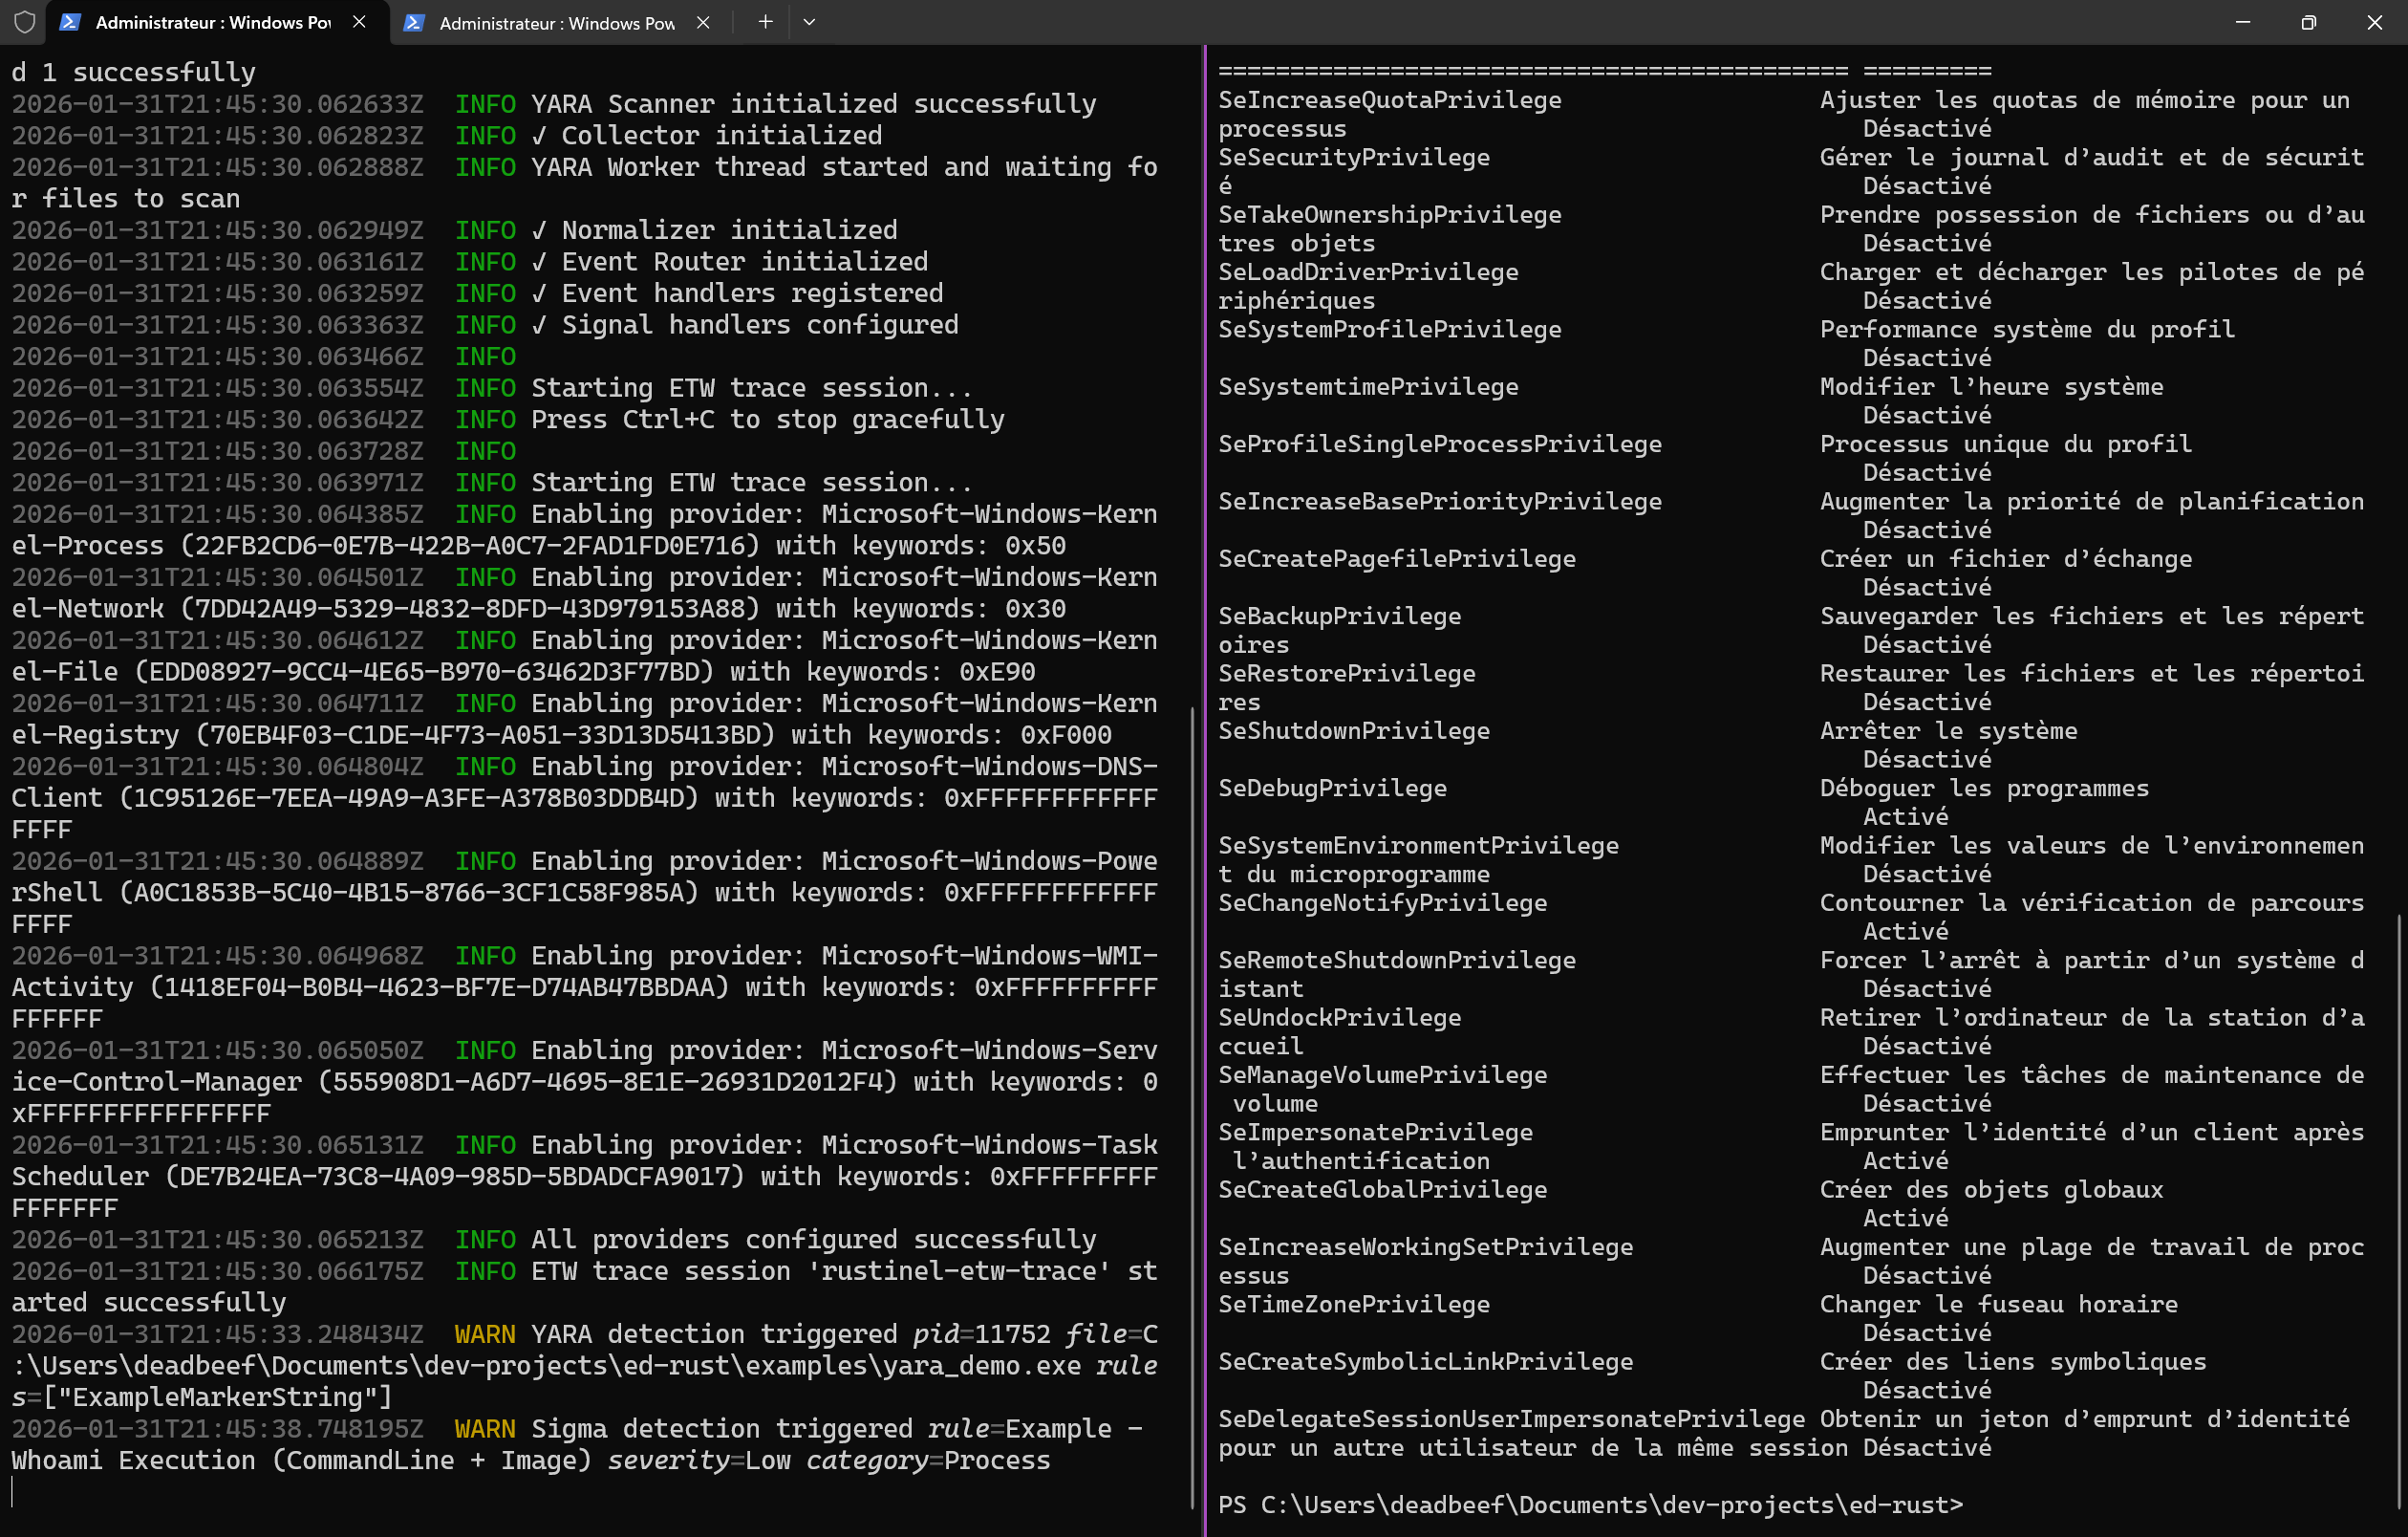
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.

STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…

DDoS botnet research and indicators of compromise from Nokia Deepfield ERT

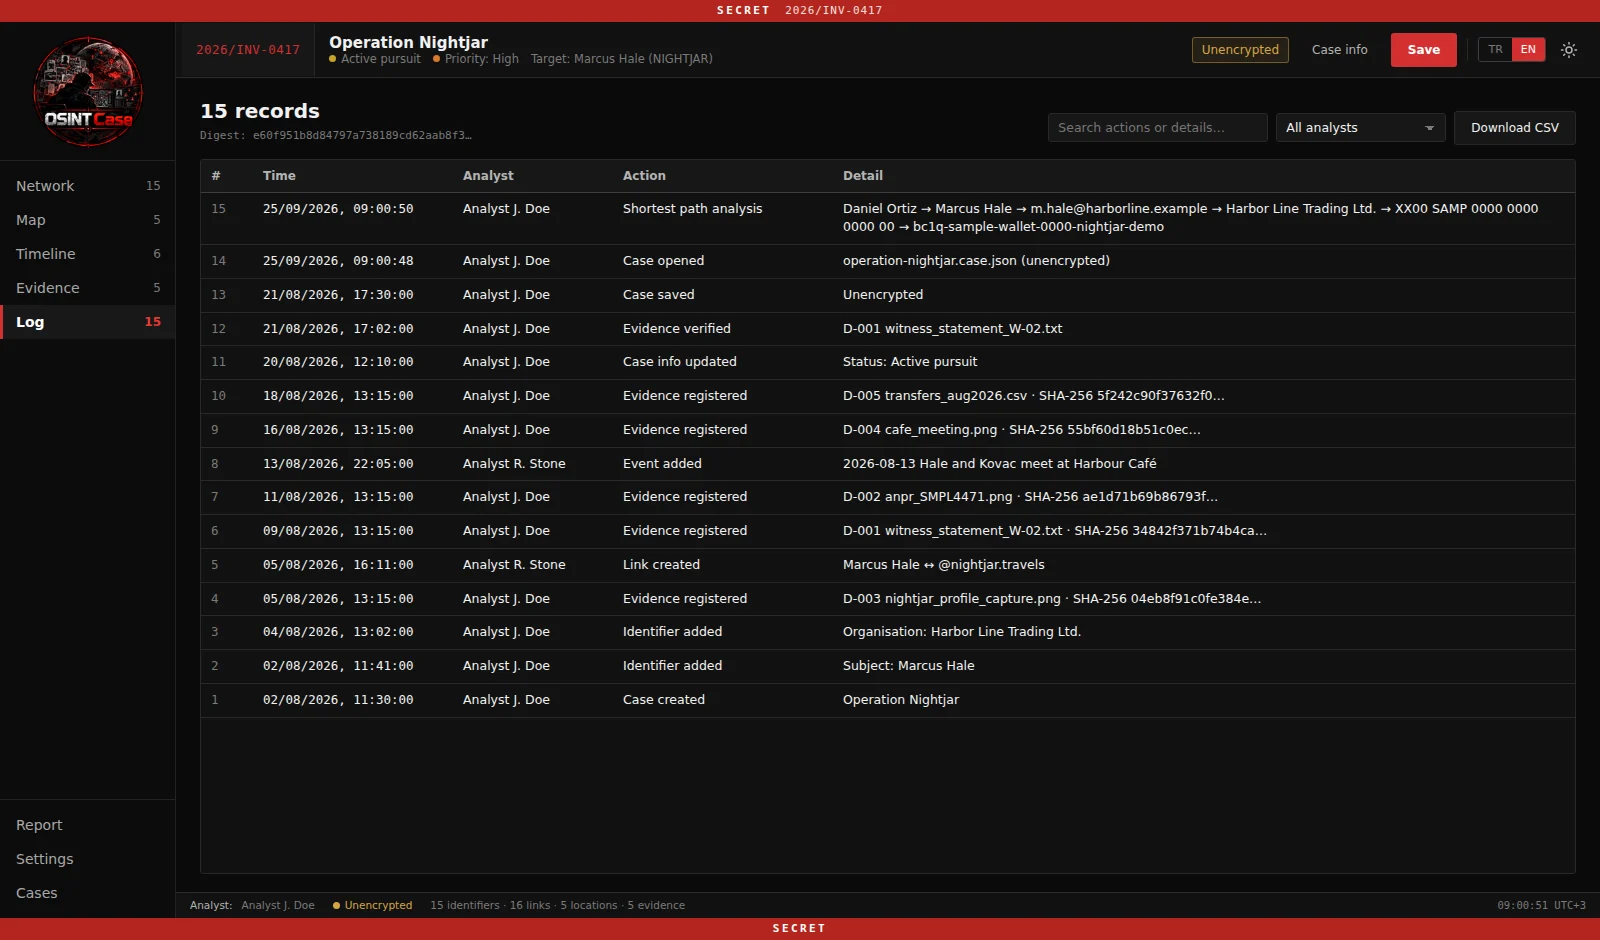
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.

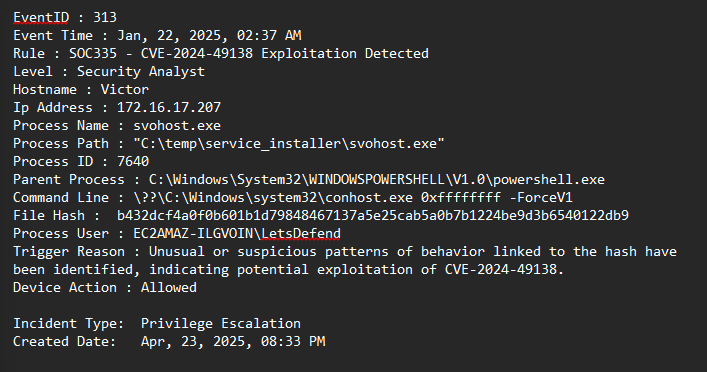
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.

ThePhish: an automated phishing email analysis tool

Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…