

Archived
C2-Tracker
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
command-and-controlinformation-gatheringioc-management+5
montysecurity/c2-trackerLive Feed of C2 servers, tools, and botnets
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 digitalshadows/cve-2019-19781_iocs
Curated indicators of compromise (IOCs) for CVE-2019-19781, including IP addresses and whois data from honeypot logs to aid threat detection and…
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 00gxd14g/misp-extractor
Extracts selected MISP attributes, including IP addresses, URLs, and hashes, into reusable output files.
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 hahasagined/cve-2024-3400
External Dynamic List (EDL) of IP addresses actively exploiting CVE-2024-3400, for use in firewall and SIEM blocklists to defend against ongoing…
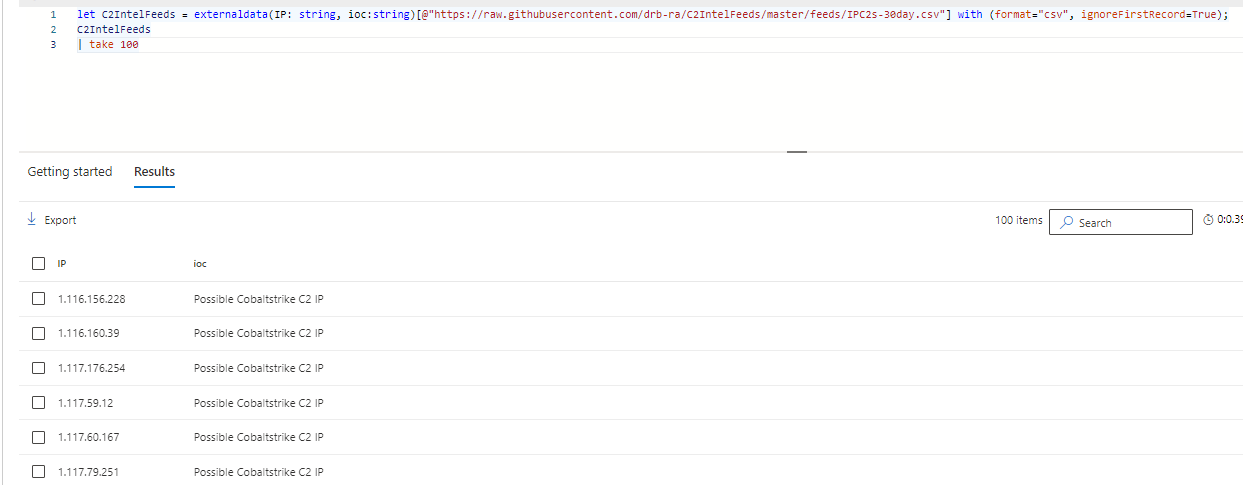 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 c3-h2/log4j_attacker_iplist
Curated list of attacker IP addresses targeting the Log4j vulnerability (CVE-2021-44228) for threat intelligence, incident response, and network…
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…