
Spip-Go
 honeylabshq/spip-go
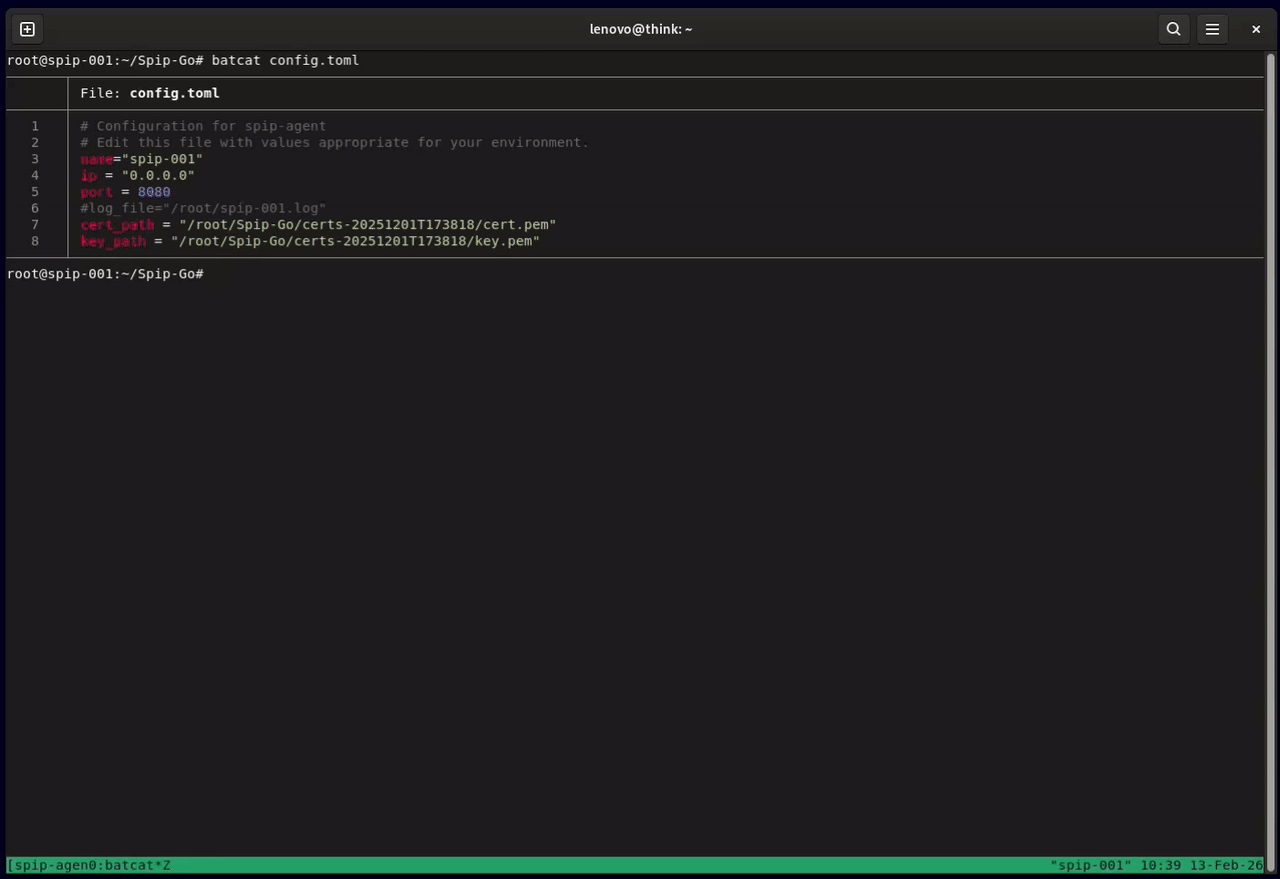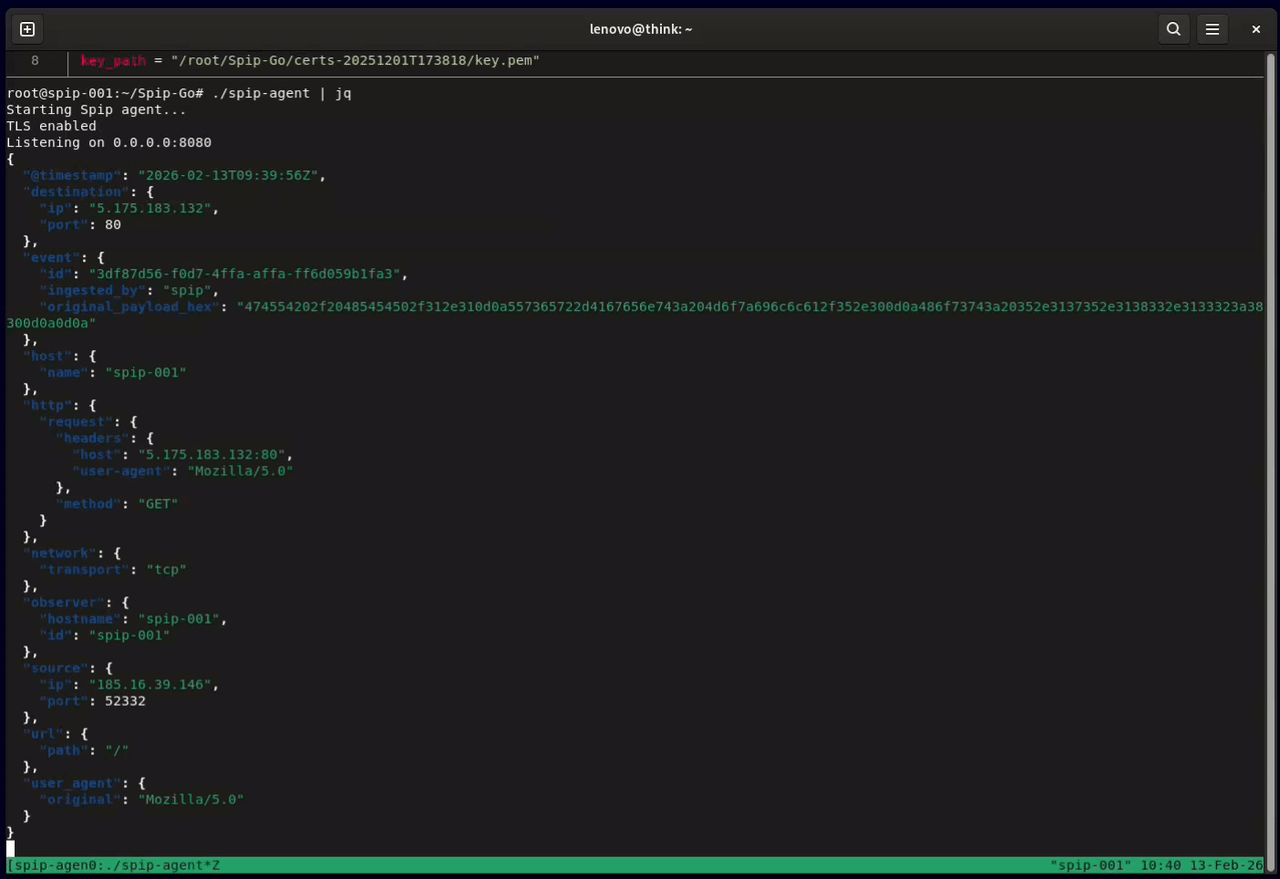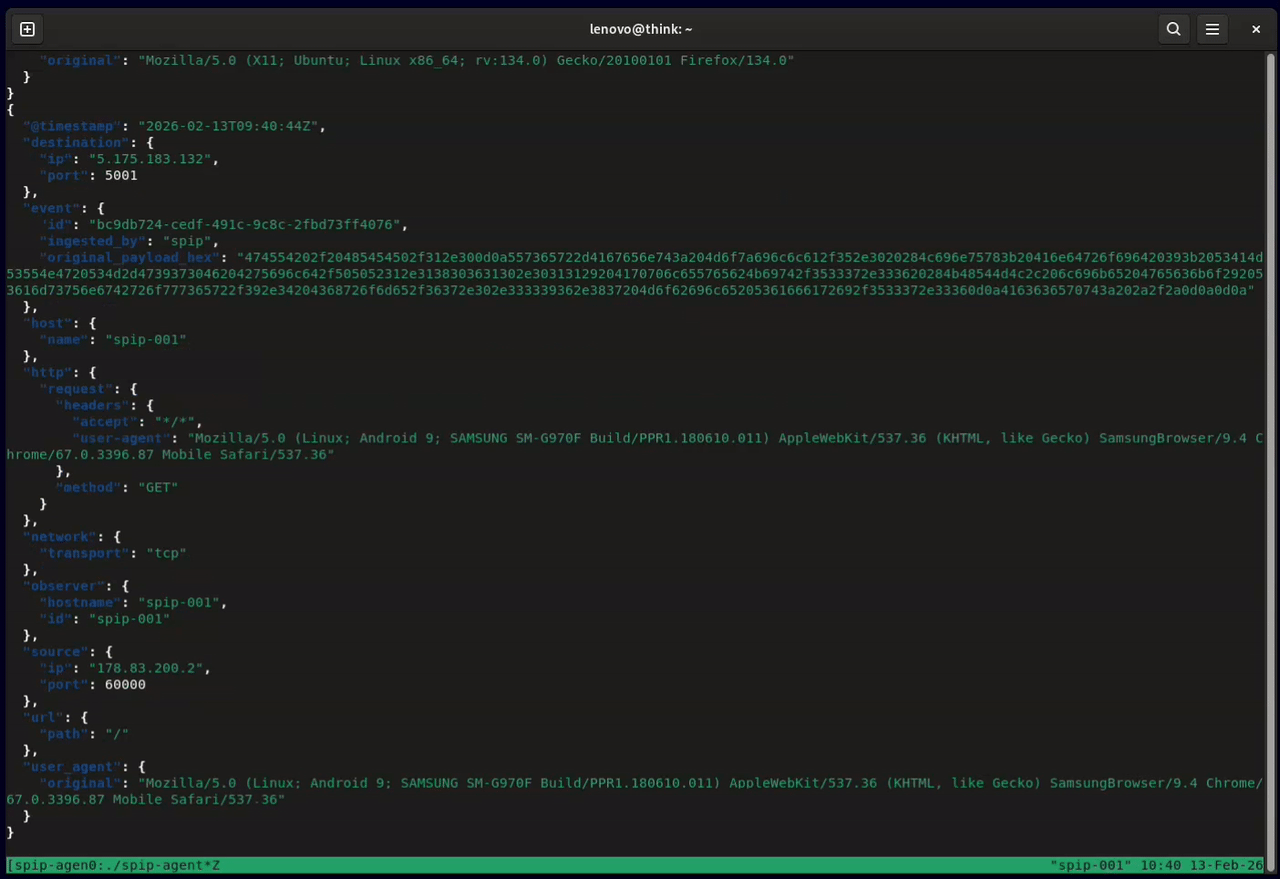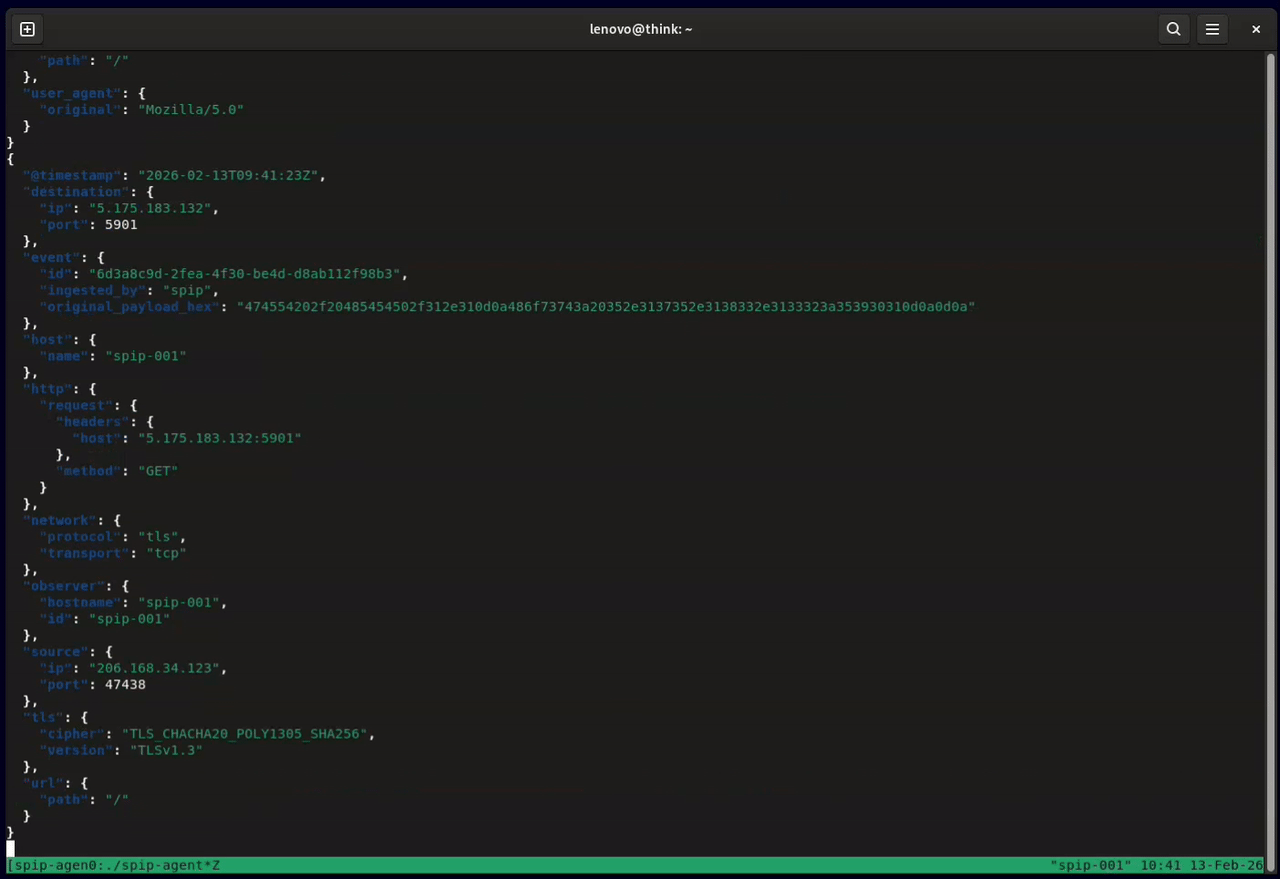
Spip network sensor written in Go
defensive-toolsincident-responseinformation-gathering+7
honeylabshq/spip-goSpip network sensor written in Go
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
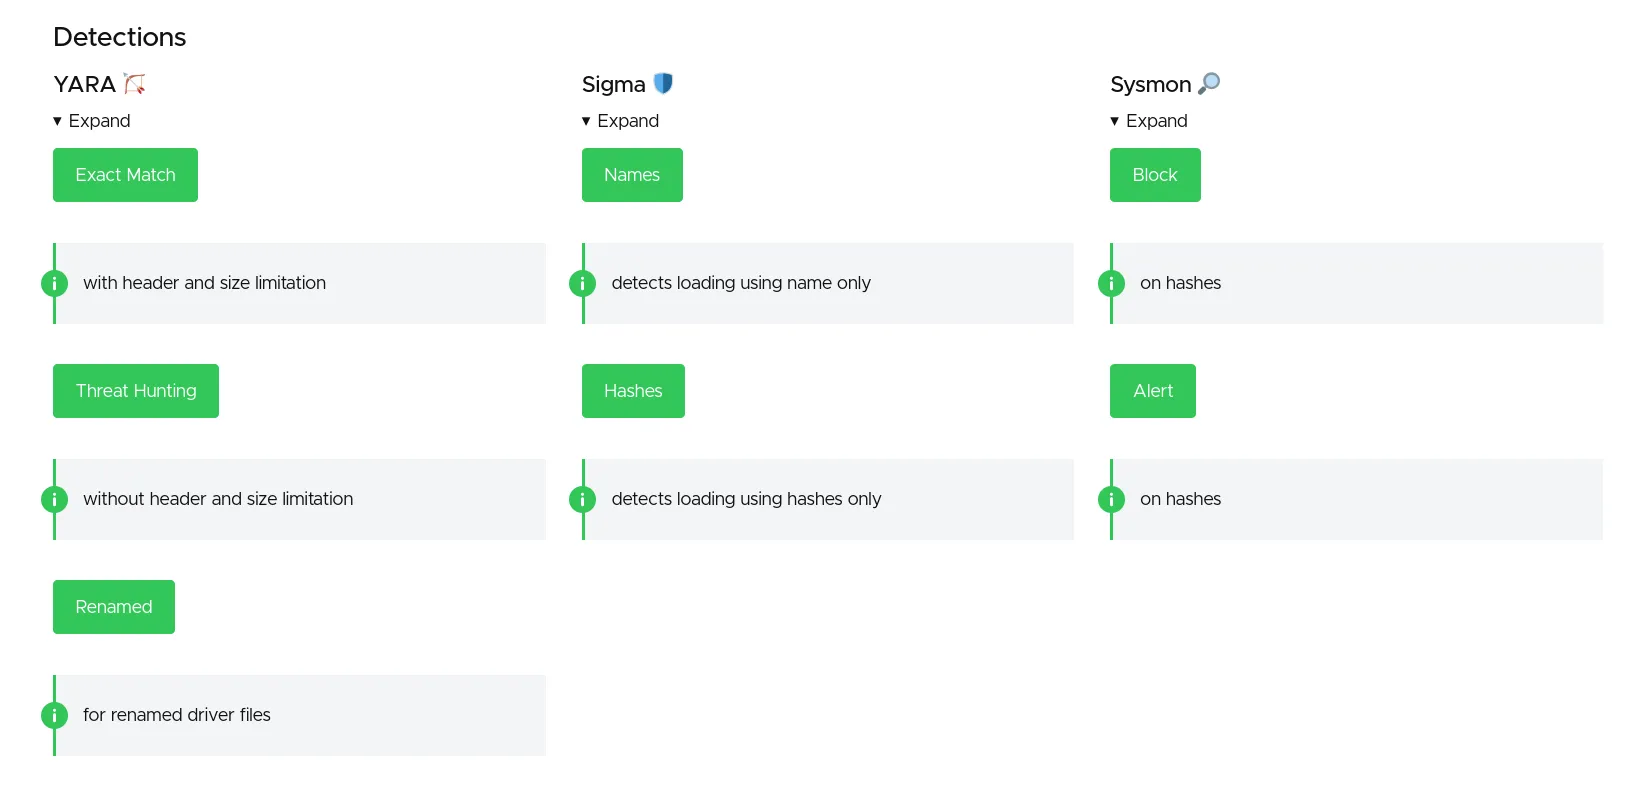 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
 eclecticiq/opentaxii
TAXII server implementation in Python from EclecticIQ
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 wortell/log4j
Repo containing all info, scripts, etc. related to CVE-2021-44228
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 vulncheck-oss/fetch-broker-conf
A go-exploit for fetching the RocketMQ broker configuration in order to discover indicators of compromise for CVE-2023-33246
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 iqx6889/cve-2026-52813-gogs-rce
CVE-2026-52813 (Gogs Path Traversal → Git Hooks RCE) defensive writeup: root-cause & patch analysis, Sigma/SIEM detection rules, IOCs, non-intrusive…
 techwithorgito/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…