

moneta
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
digital-forensicsforensicsioc-management+3
8492 years ago
forrest-orr/monetaMoneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
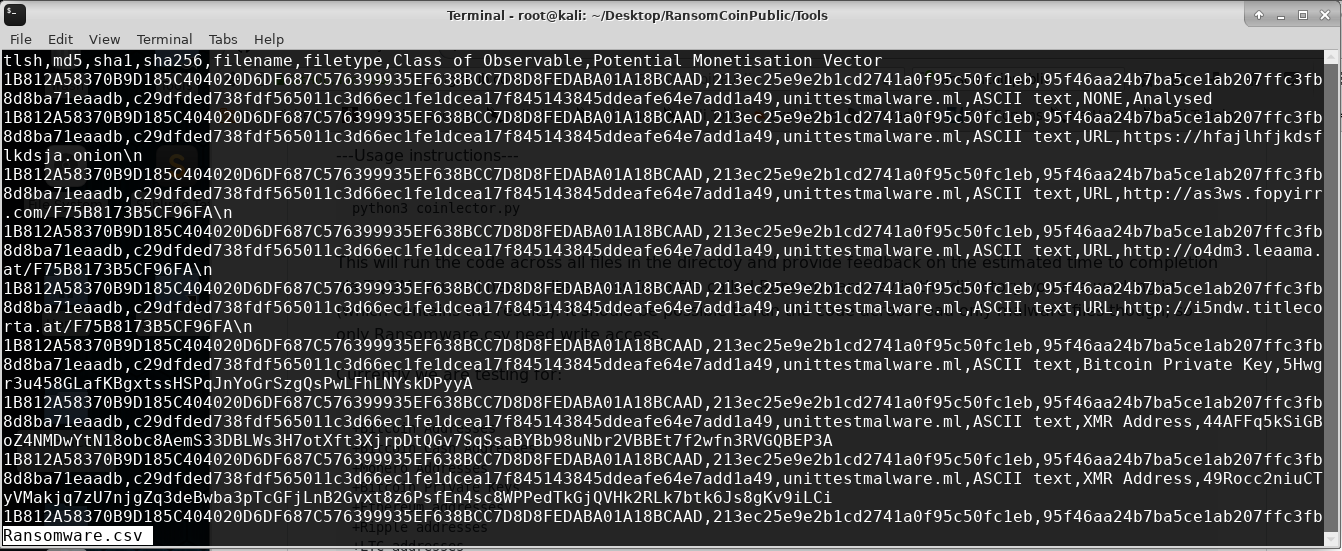 concinnity-risks/ransomcoinpublic
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 sucuri-labs/cve-2025-57819-ioc-check
This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 salaheldinfikri/kalim_backdoor
Kalim backdooe Malware Report