associated-threat-analyzer

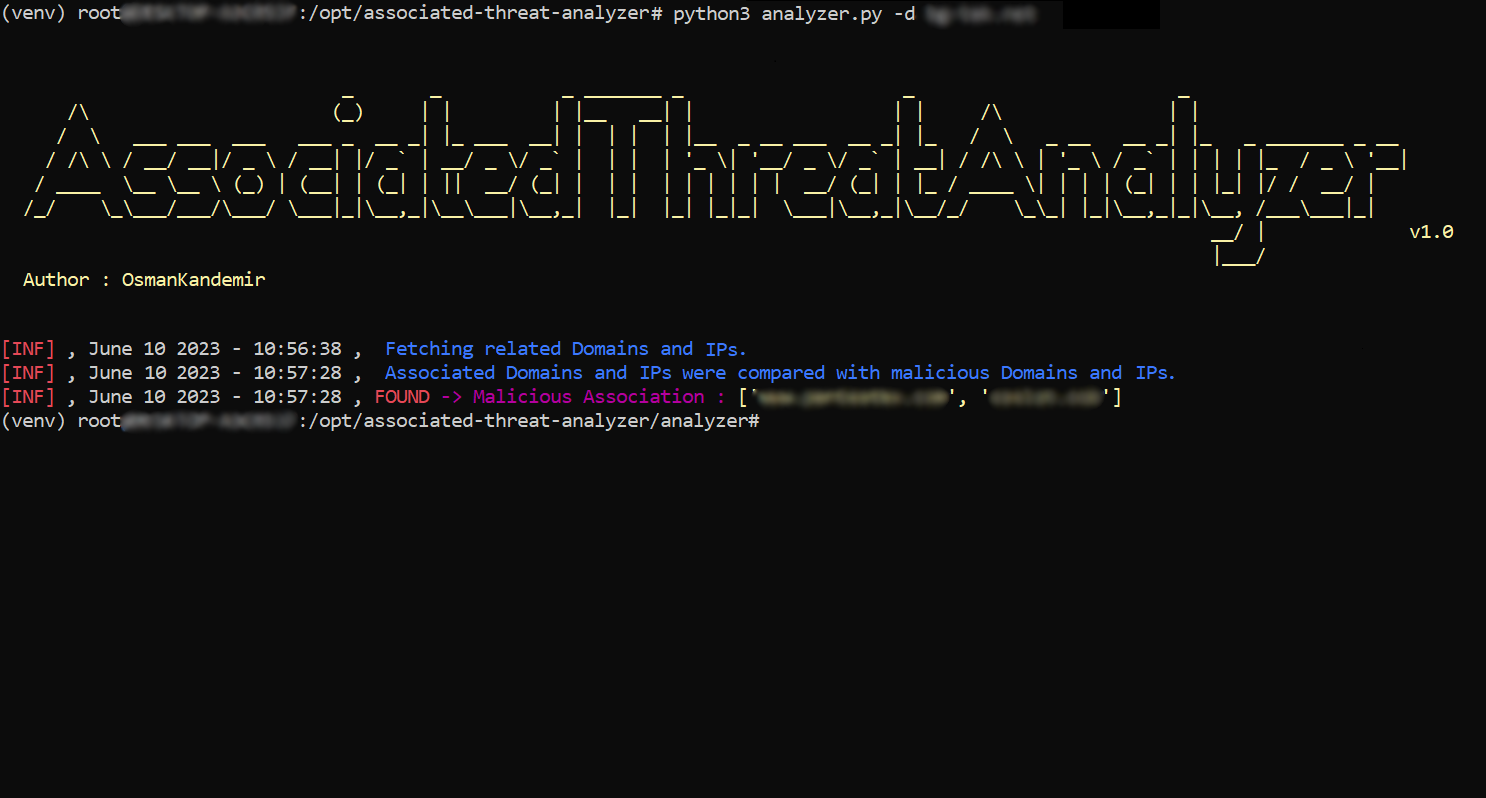
Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…

Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…

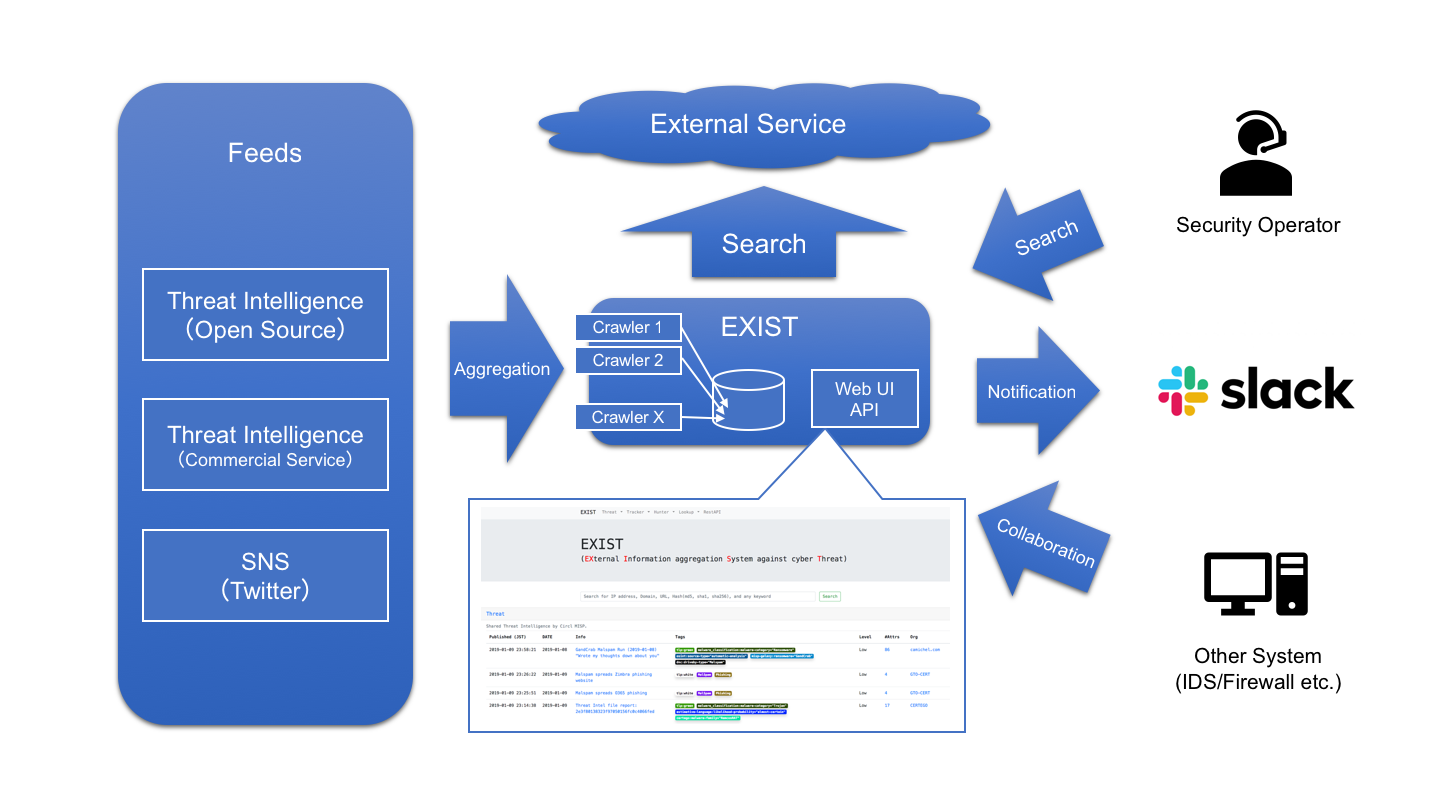
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

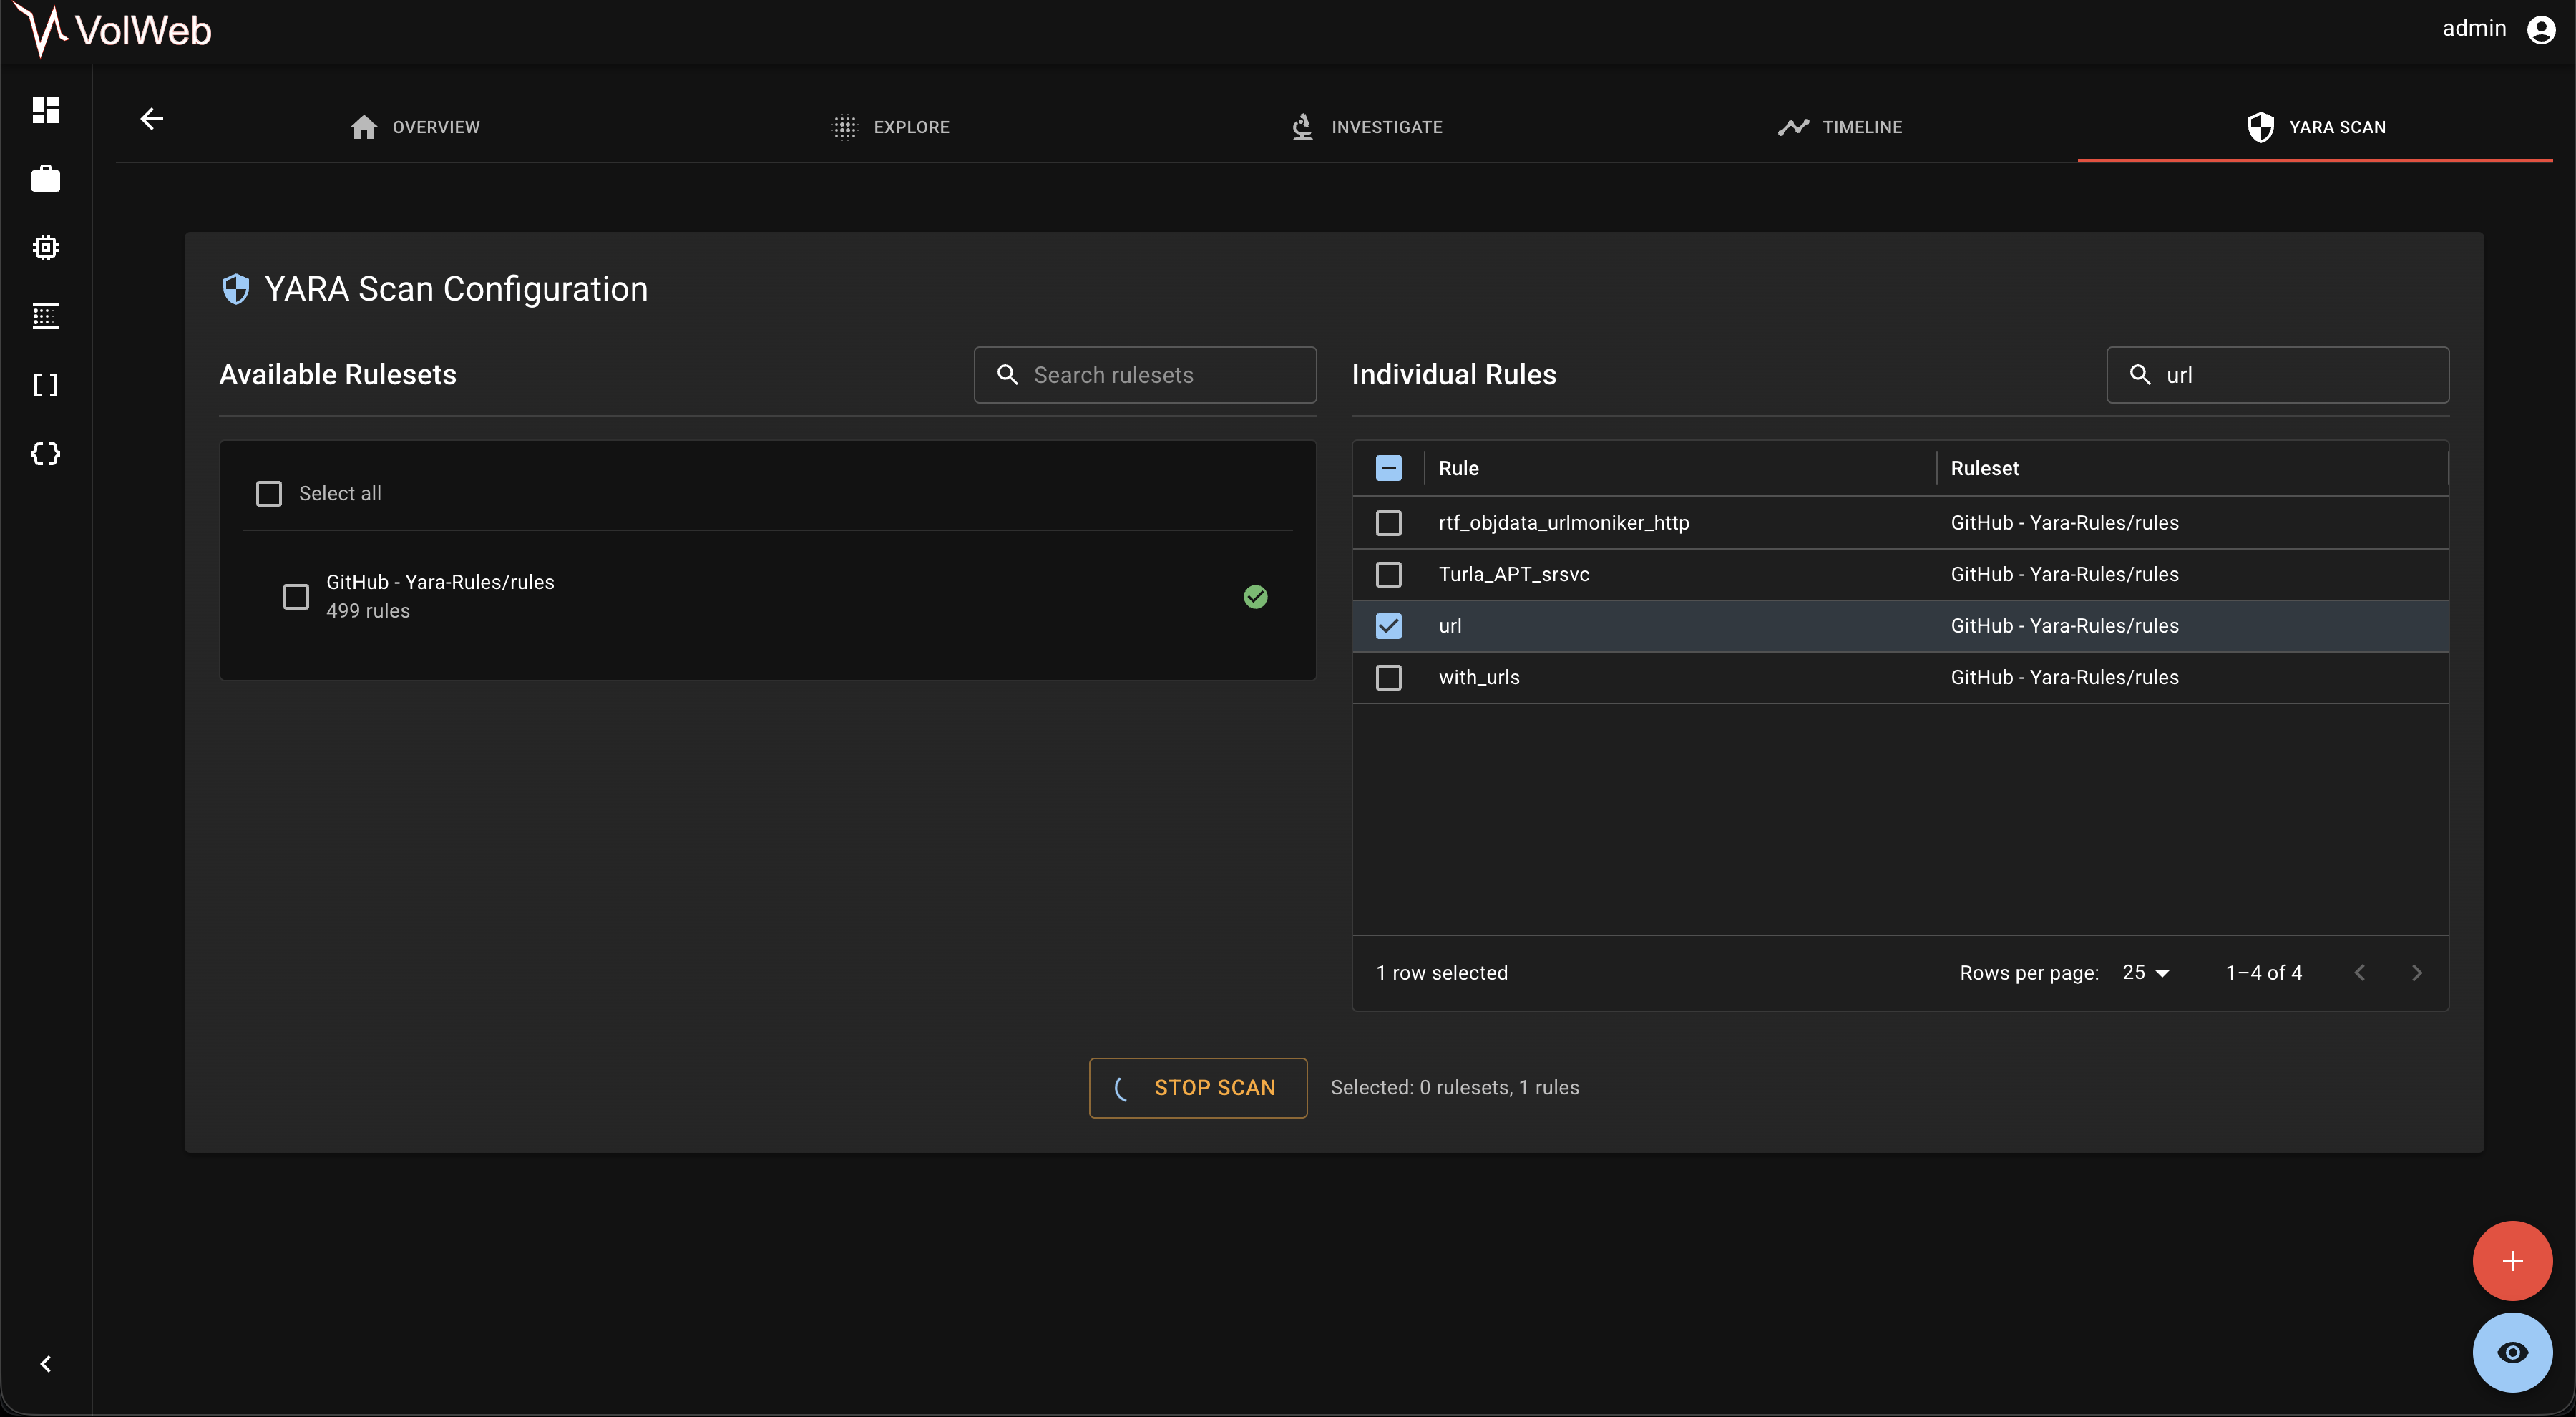
A centralized and enhanced memory analysis platform

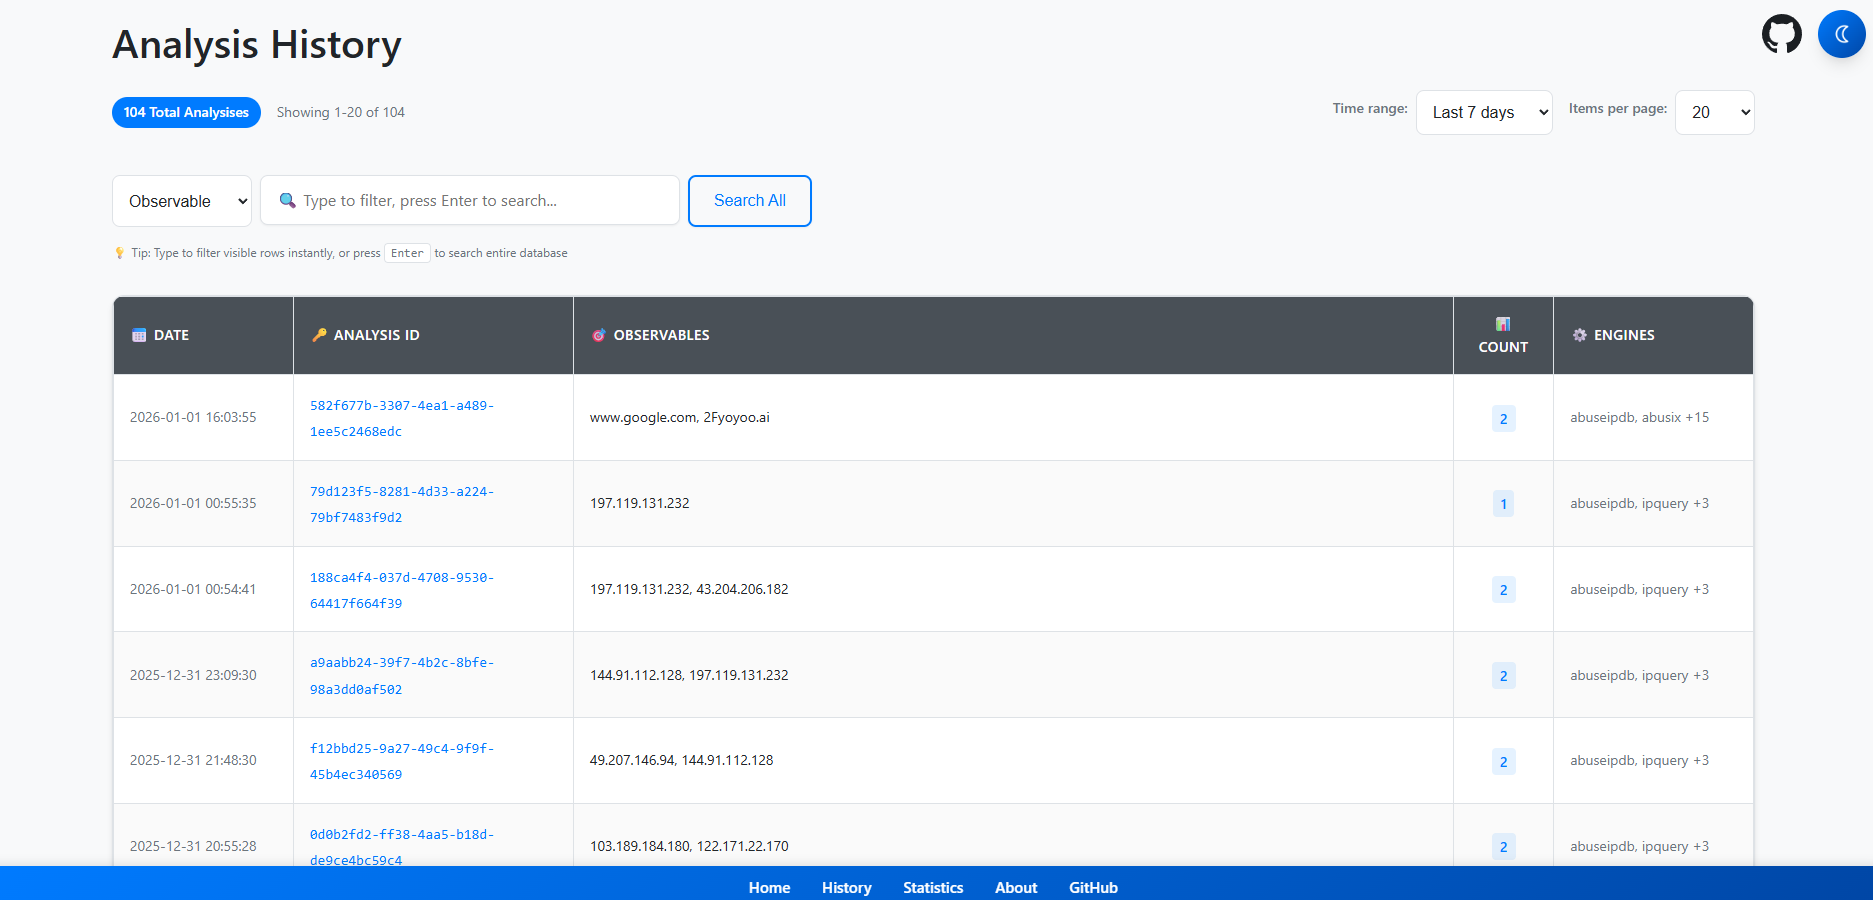
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.

StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…

Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…

Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…

Defensive remediation and auditing toolkit for CVE-2026-54420 in LiteSpeed cPanel Plugin. Automates patching, detects suspicious symlinks, hunts…

Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…

Defensive mitigation and auditing toolkit for CVE-2026-54420 in LiteSpeed cPanel plugin, providing symlink detection, IOC hunting, and remediation…

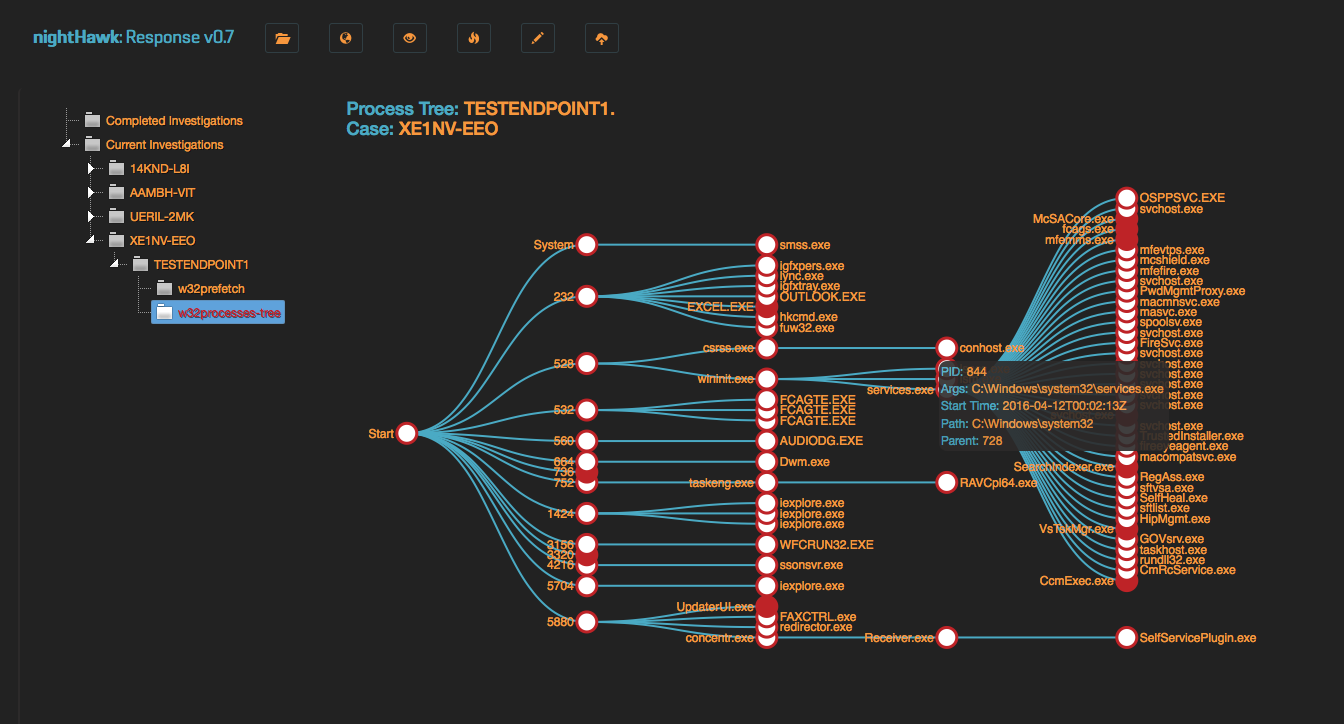
Incident Response Forensic Framework

TAXII server implementation in Python from EclecticIQ

Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Offline CISA KEV snapshot comparison for field-level change review. Free prototype, not a security assessment. AI-assisted development.

test for the ioc described for FG-IR-22-398