

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
26 results
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k1 day ago
BlackLotusDetection preview

BlackLotusDetection

GitHubbakedmuffinman/blacklotusdetection

Created to help detect IOCs for CVE-2022-21894: The BlackLotus campaign
forensicsincident-responseioc-management+2
3 years ago
log4shell_ioc_ips preview

log4shell_ioc_ips

GitHubhackinghippo/log4shell_ioc_ips

log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
incident-responseinformation-gatheringioc-management+3
374 years ago
CVE-2025-68645-Exploiting-Zimbra-Webmail-LFI-Vulnerability preview

CVE-2025-68645-Exploiting-Zimbra-Webmail-LFI-Vulnerability

GitHubfaysalferdous/cve-2025-68645-exploiting-zimbra-webmail-lfi-vulnerability

Defender-focused reference pack for CVE-2025-68645 Zimbra LFI, including Sigma/Splunk detection rules, WAF mitigation snippets, IOC patterns, and…
educationincident-responseioc-management+3
7 months ago
panrapidcheck preview

panrapidcheck

GitHubhackinglz/panrapidcheck

Extract useful information from PANOS support file for CVE-2024-3400

forensicsincident-responseioc-management+3
21 year ago
CVE-2025-60787-Detection-motionEye-RCE-via-Config-Injection preview

CVE-2025-60787-Detection-motionEye-RCE-via-Config-Injection

GitHubgarethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection

Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…

container-securityexploitationintrusion-detection+5
6 months ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
database-securitydigital-forensicsdisk-forensics+8
855 months ago
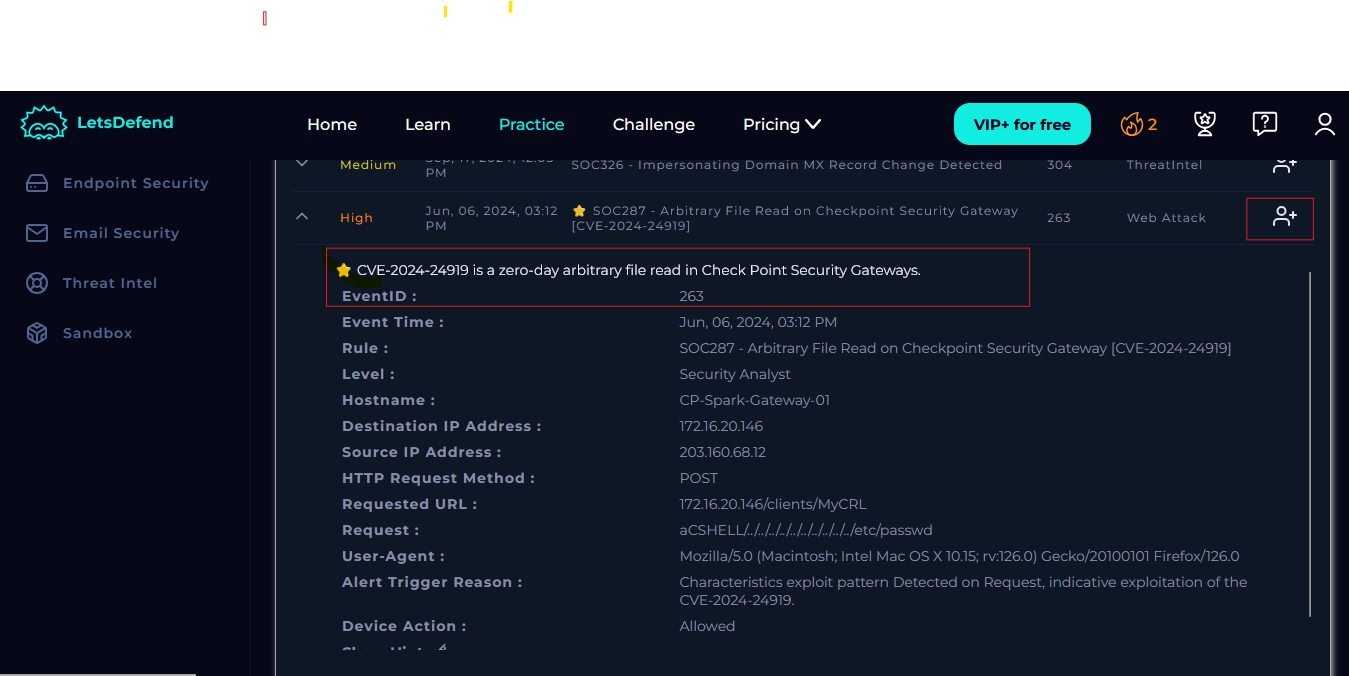
Event-ID-263-Arbitrary-File-Read-on-Checkpoint-Security-Gateway-CVE-2024-24919- preview

Event-ID-263-Arbitrary-File-Read-on-Checkpoint-Security-Gateway-CVE-2024-24919-

GitHubcyberbibs/event-id-263-arbitrary-file-read-on-checkpoint-security-gateway-cve-2024-24919-

Step-by-step SOC incident response walkthrough for CVE-2024-24919 arbitrary file read on Check Point gateways, covering detection, analysis,…

educationforensicsincident-response+3
1 year ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
3.0k1h 20m ago
Sandbox_Scryer preview

Sandbox_Scryer

GitHubpayloadsecurity/sandbox_scryer

Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
dynamic-analysis-sandboxingeducationinformation-gathering+6
2284 years ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
101 month ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k8 months ago
BlueBox preview

BlueBox

GitHubsvdwi/bluebox

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…

ioc-managementmachine-learningmalware-analysis+4
504 years ago
CVE-2021-1675_CarbonBlack_HuntingQuery preview

CVE-2021-1675_CarbonBlack_HuntingQuery

GitHubmrezqi/cve-2021-1675_carbonblack_huntingquery

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
defensive-toolsincident-responseioc-management+3
5 years ago
copy-fail-CVE-2026-31431-IOC preview

copy-fail-CVE-2026-31431-IOC

GitHubkadir/copy-fail-cve-2026-31431-ioc

Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
forensicsincident-responseintrusion-detection+2
314 months ago
ExtendIntel preview

ExtendIntel

GitHubcorelight/extendintel

This package extends the Intel package to log more fields
incident-responseioc-managementlog-analysis+2
32 months ago
CVE-2023-38831-KQL preview

CVE-2023-38831-KQL

GitHubpascalasch/cve-2023-38831-kql

KQL Hunting for WinRAR CVE-2023-38831
incident-responseinformation-gatheringioc-management+3
43 years ago
Detection-Tool-Kit-for-CVE-2026-31431 preview

Detection-Tool-Kit-for-CVE-2026-31431

GitHubvishvacyber/detection-tool-kit-for-cve-2026-31431

Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…

educationforensicsincident-response+4
4 months ago
Previous12Next