Wp2shell-ioc-scanner

Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…

Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…

Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign

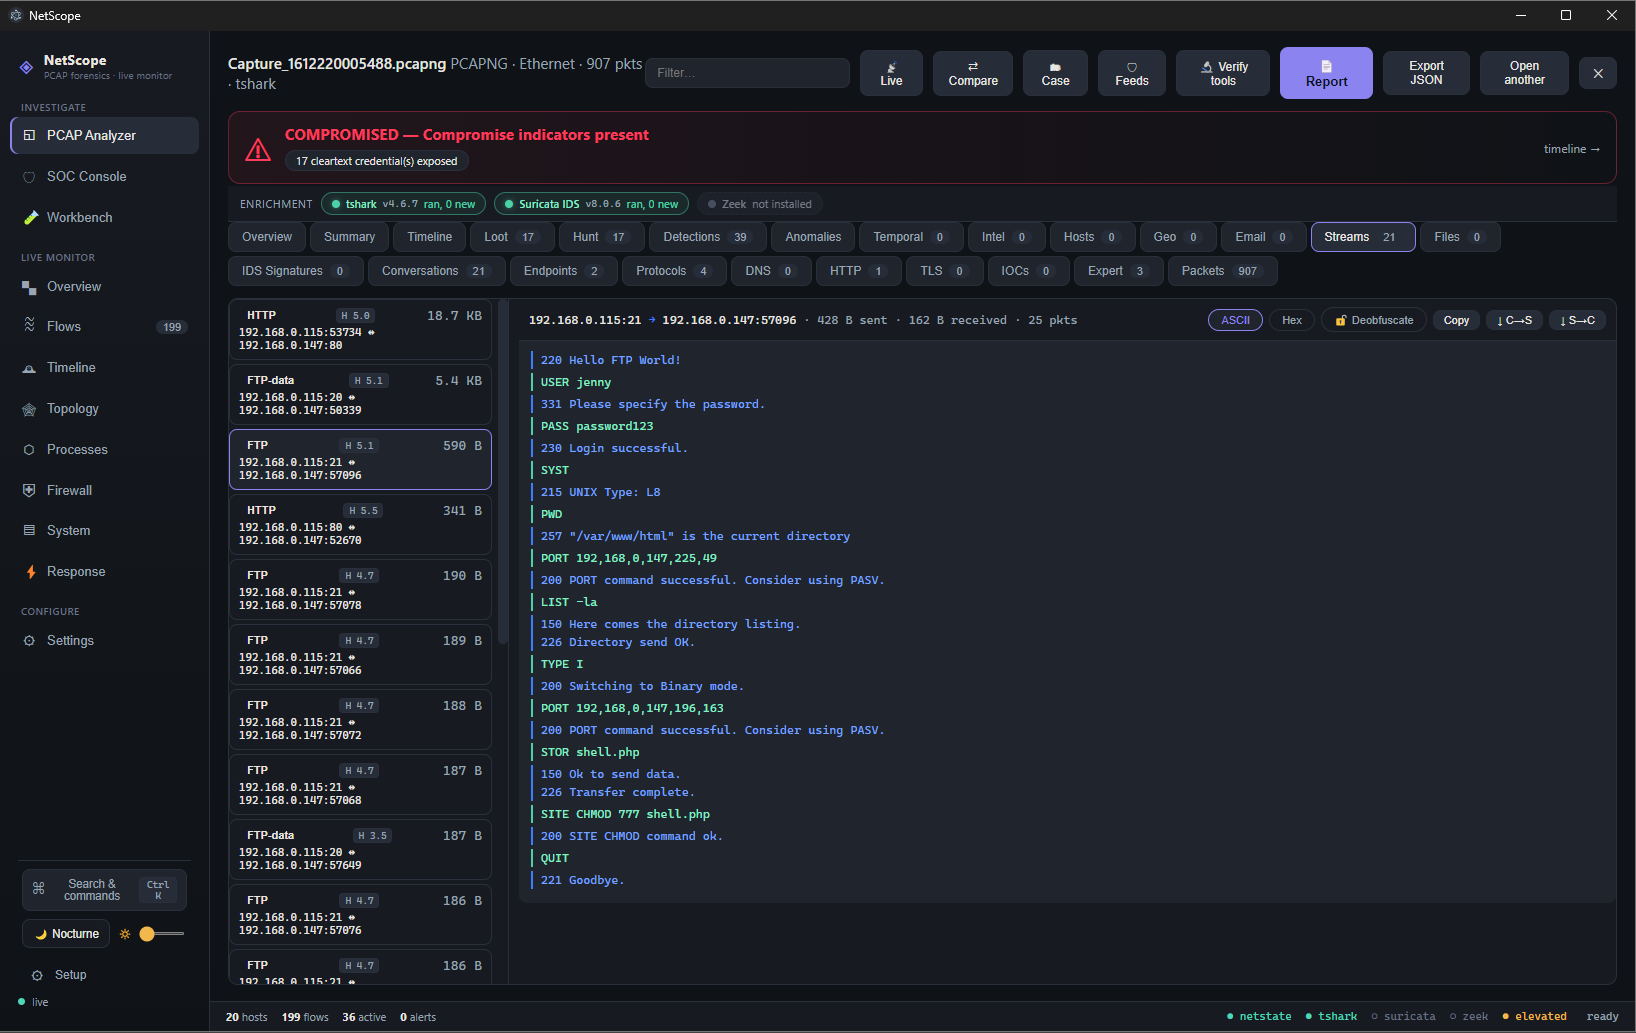
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

Detection-first incident-response toolkit for Zimbra administrators investigating CVE-2026-73570. Searches logs for exploit indicators, examines…

This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…

This repository talks about Zero-Day Exploitation of Atlassian Confluence, it's defense and analysis point of view from a SecOps or Blue Team…

IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…

Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…

Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)

Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.

Offline browser extension providing defensive analysis and detection guidance for CVE-2026-20127, with packet visualization, IOC extraction, and…

Read-only WordPress User Registration CVE-2026-1492 checker for hidden admins, plugin version, uploads PHP, cron, and compromise IOCs.

Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.

CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…