
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
348 results
iocx preview

iocx

GitHubiocx-dev/iocx

An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
binary-analysisdevsecopsforensics+6
29
11 days ago
threat-research preview

threat-research

GitHubthreatray/threat-research

IoCs and YARA rules from Threatray's Threat Research
forensicsincident-responseioc-management+2
223 days ago
muad-dib preview

muad-dib

GitHubdnszlsk/muad-dib

Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
code-analysisdevsecopsdynamic-analysis-sandboxing+8
1521 days ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…

binary-analysisdebuggersdigital-forensics+9
441 year ago
CVE-2020-6287_RECON-scanner preview

CVE-2020-6287_RECON-scanner

GitHubonapsis/cve-2020-6287_recon-scanner

Black-box vulnerability scanner and indicator-of-compromise analyzer for CVE-2020-6287 (RECON) in SAP NetWeaver Java applications, enabling rapid…
forensicsincident-responseioc-management+3
284 years ago
glassworm-hunter preview

glassworm-hunter

GitHubafine-com/glassworm-hunter

Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
code-analysisdevsecopseducation+9
303 months ago
Detection preview

Detection

GitHubsifalcon/detection

Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
curated-resourcesdigital-forensicsincident-response+4
243 years ago
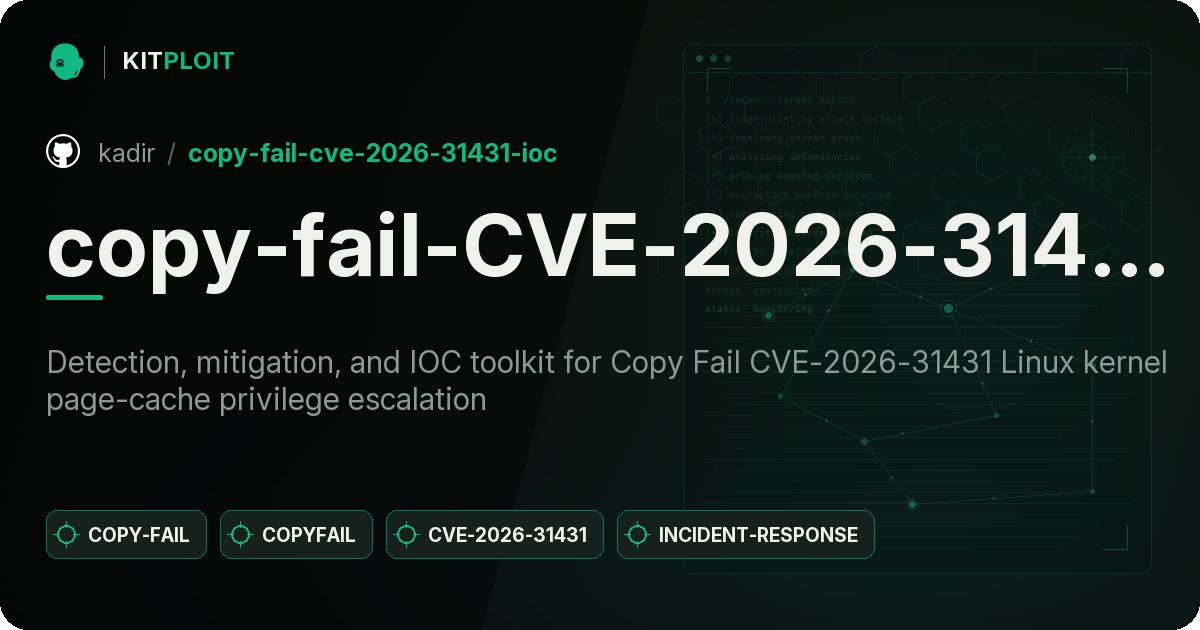
ThreatPad preview

ThreatPad

GitHubbhavikmalhotra/threatpad

Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
data-exfiltrationeducationincident-response+5
235 months ago
copy-fail-CVE-2026-31431-IOC preview

copy-fail-CVE-2026-31431-IOC

GitHubkadir/copy-fail-cve-2026-31431-ioc

Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation

forensicsincident-responseintrusion-detection+2
314 months ago
cve-2020-5902-ioc-bigip-checker preview

cve-2020-5902-ioc-bigip-checker

GitHubf5devcentral/cve-2020-5902-ioc-bigip-checker

Local F5 BIG-IP script that scans for Indicators of Compromise (IoCs) related to CVE-2020-5902, checking logs, files, and system integrity to detect…

forensicsincident-responseioc-management+3
176 years ago
Malware preview

Malware

GitHubpandare9x/malware

IOCs and notes related to malware
curated-resourcesioc-managementmalware-analysis+1
261 year ago
CVE-2025-53770-Scanner preview

CVE-2025-53770-Scanner

GitHubzephrfish/cve-2025-53770-scanner

ToolShell scanner - CVE-2025-53770 and detection information
defensive-toolsexploitationincident-response+6
181 year ago
Veto preview

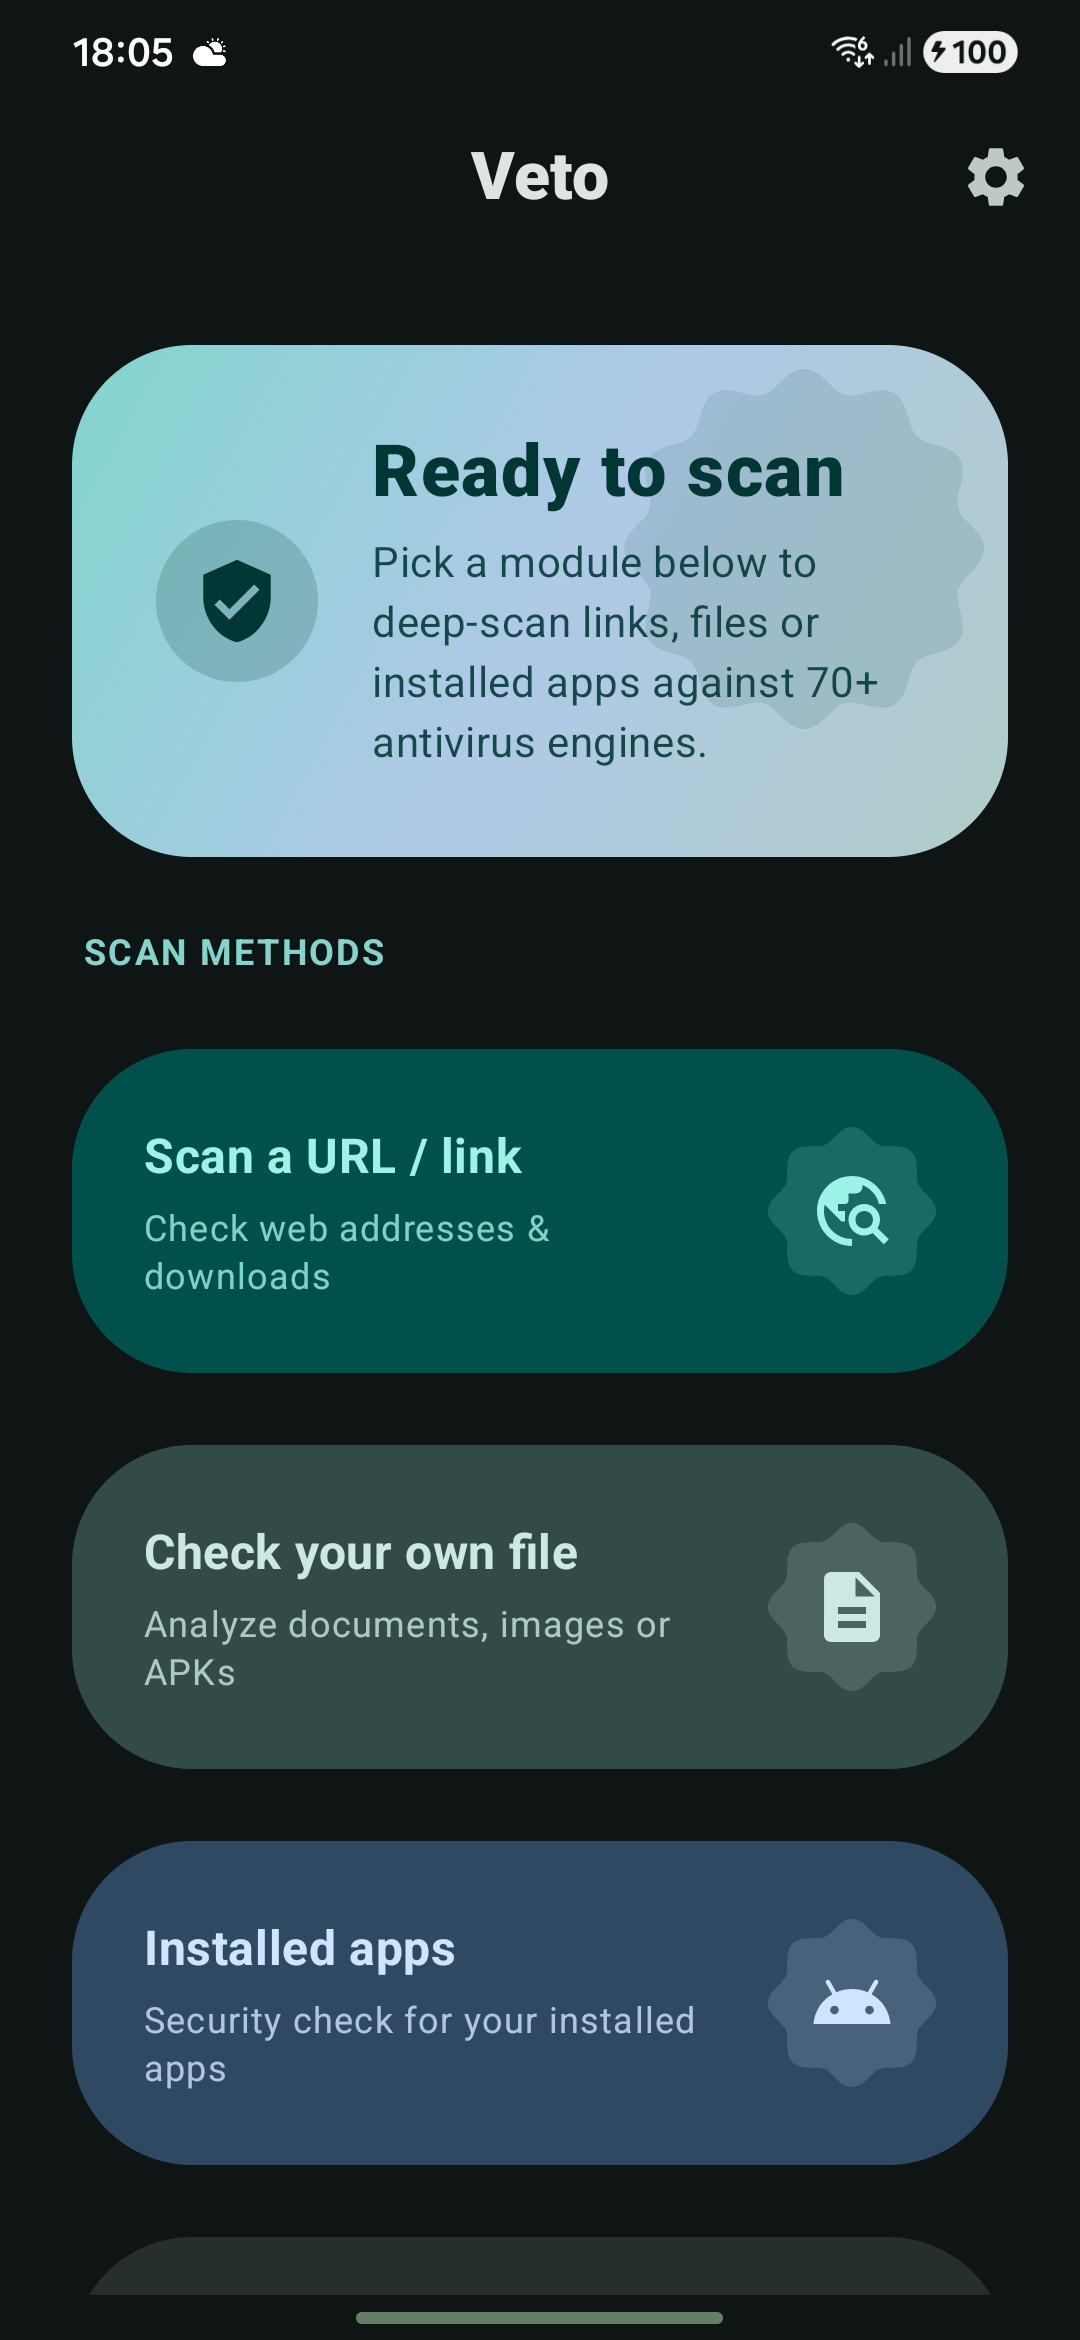
Veto

GitHubprofessorquantumuniverse/veto

Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
android-securitydynamic-analysis-sandboxingforensics+8
1714 days ago
synacktiv-rules preview

synacktiv-rules

GitHubsynacktiv/synacktiv-rules

Public repository of Sigma and YARA rules created by Synacktiv
forensicsintrusion-detectionioc-management+3
2111 months ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
data-exfiltrationdigital-forensicsforensics+5
139 years ago
cpanel-sessionscribe preview

cpanel-sessionscribe

GitHubrfxn/cpanel-sessionscribe

Detection, mitigation, and reverse-engineering tooling for CVE-2026-41940 (SessionScribe): the cPanel/WHM unauthenticated session-forgery…
defensive-toolsexploitationforensics+7
144 months ago
odin preview

odin

GitHubhamza-megahed/odin

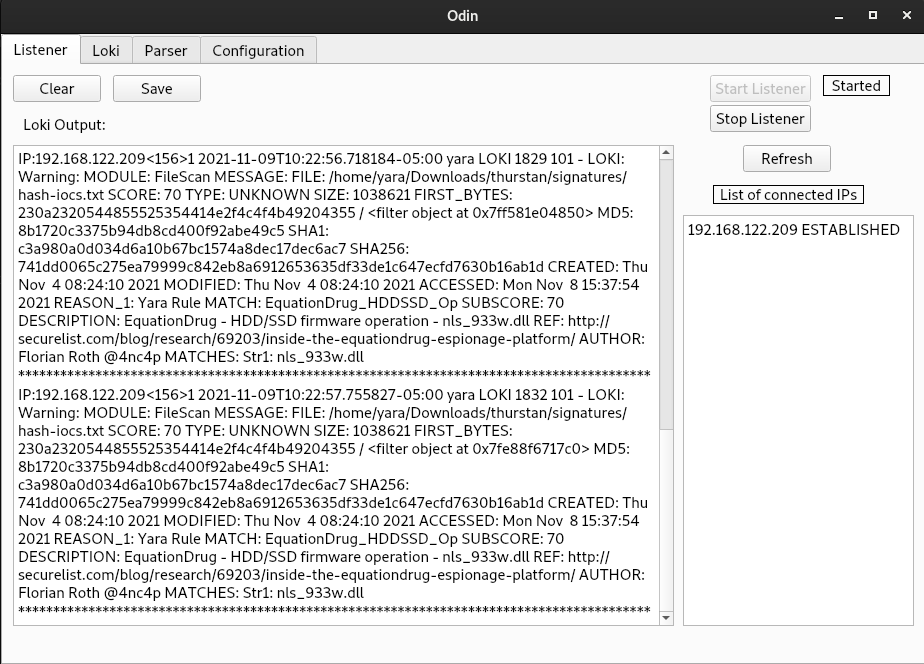
Centralized IoC scanner that deploys Loki across endpoints, collects detection results, and parses logs into CSV for incident response and forensic…

defensive-toolsforensicsincident-response+2
204 years ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

command-and-controlcryptographydigital-forensics+7
109 days ago
Previous1…456…20Next