
vuln-list-update
 aquasecurity/vuln-list-update
Automated vulnerability data aggregator that collects advisories from NVD, OSV, Alpine, Red Hat, and 20+ other sources into a unified parsable format…
cloud-securitydevsecopsioc-management+2
197
aquasecurity/vuln-list-updateAutomated vulnerability data aggregator that collects advisories from NVD, OSV, Alpine, Red Hat, and 20+ other sources into a unified parsable format…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 capacitorset/box-js
A tool for studying JavaScript malware.
 executemalware/malware-iocs
Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…
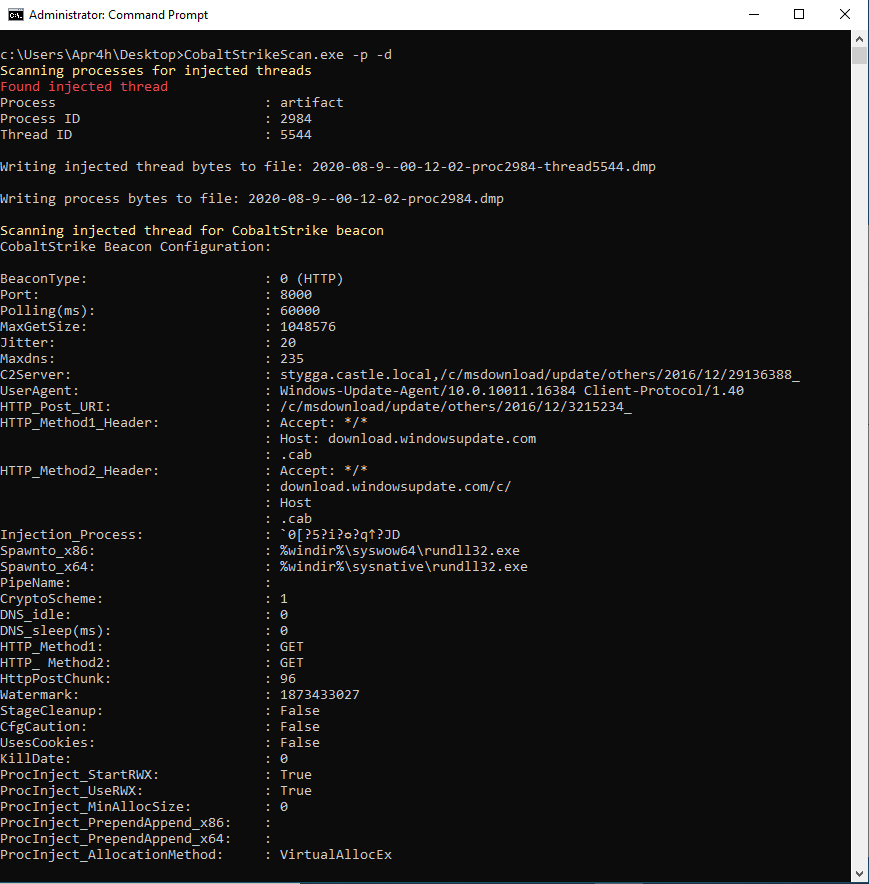 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 fhightower/ioc-finder
Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
 paloaltonetworks/unit42-threat-intelligence-article-information
This is the repository for indicators of compromise (IOCs) and other data for threat intelligence articles posted on the Palo Alto Networks Unit 42…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…
 wiz-sec-public/wiz-research-iocs
Curated public database of indicators of compromise aggregated by Wiz Research for threat detection, hunting, and incident response workflows.
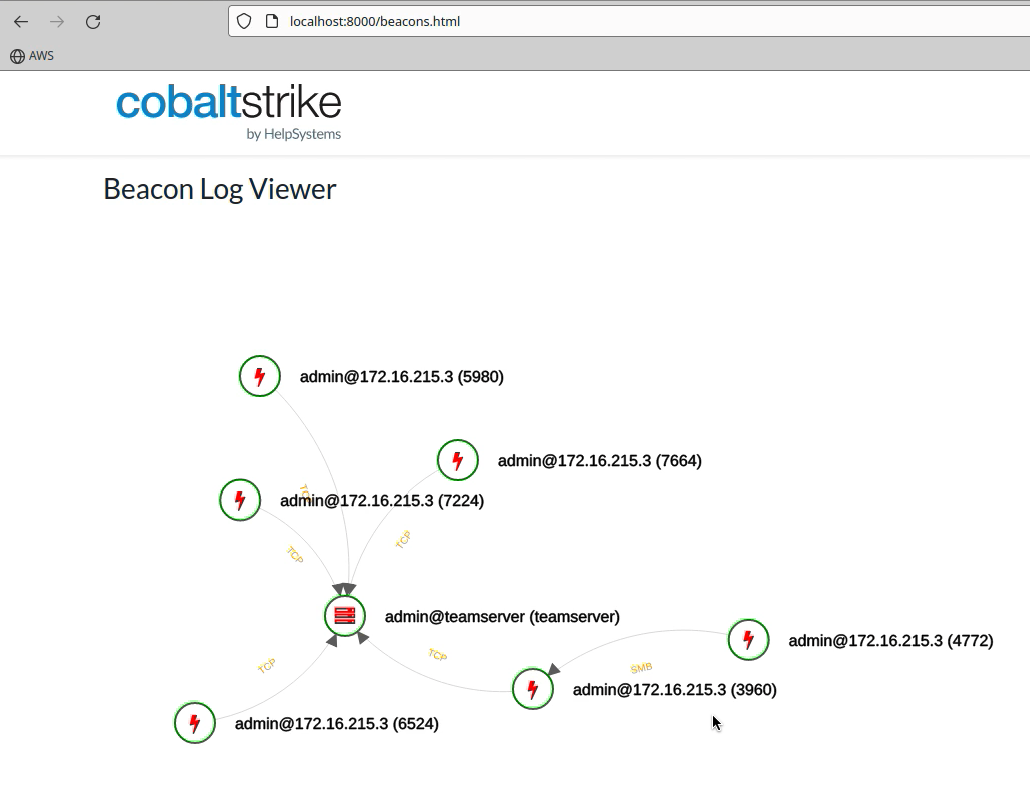 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 mubix/cve-2021-44228-log4shell-hashes
Hashes for vulnerable LOG4J versions
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)