
CAPEsolo
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
60
capesandbox/capesoloStandalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 chaitanyakrishna/iocscraper
IOCPARSER.COM is a Fast and Reliable service that enables you to extract IOCs and intelligence from different data sources.
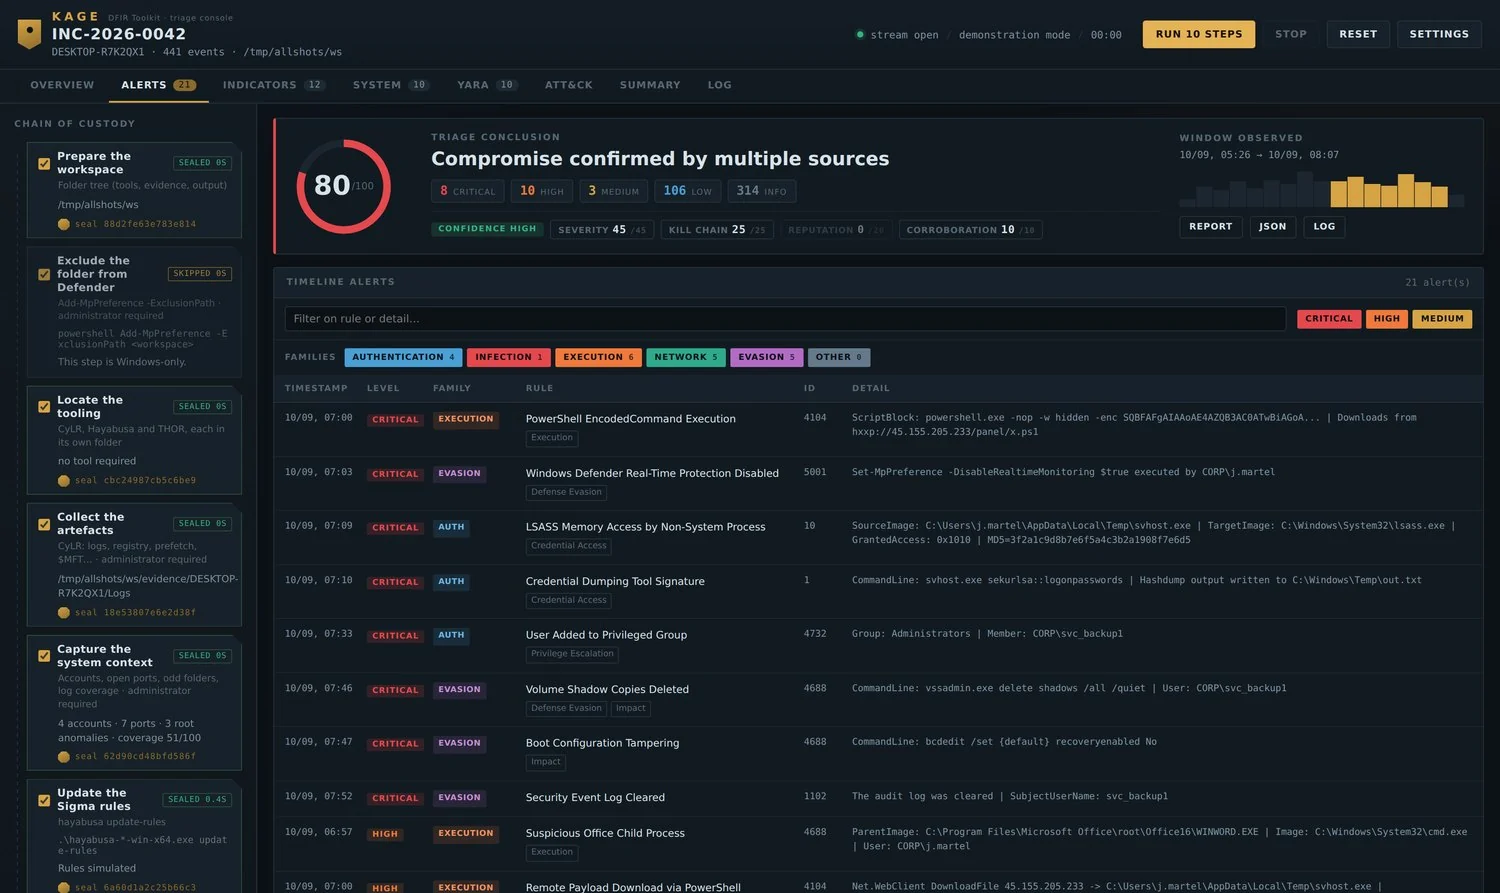 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
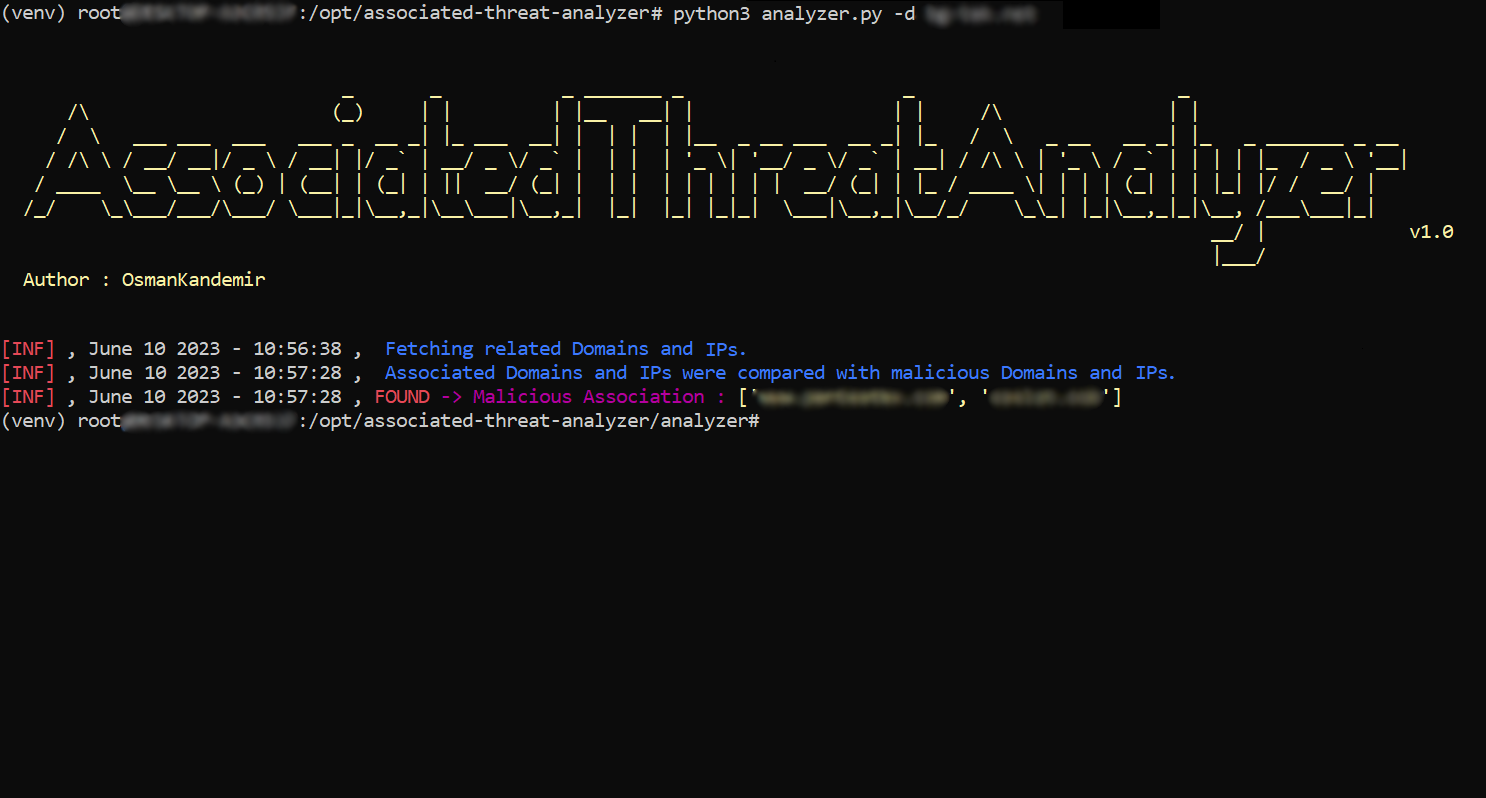 osmankandemir/associated-threat-analyzer
Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 shadow0ps/cve-2023-20198-scanner
This is a webshell fingerprinting scanner designed to identify implants on Cisco IOS XE WebUI's affected by CVE-2023-20198 and CVE-2023-20273
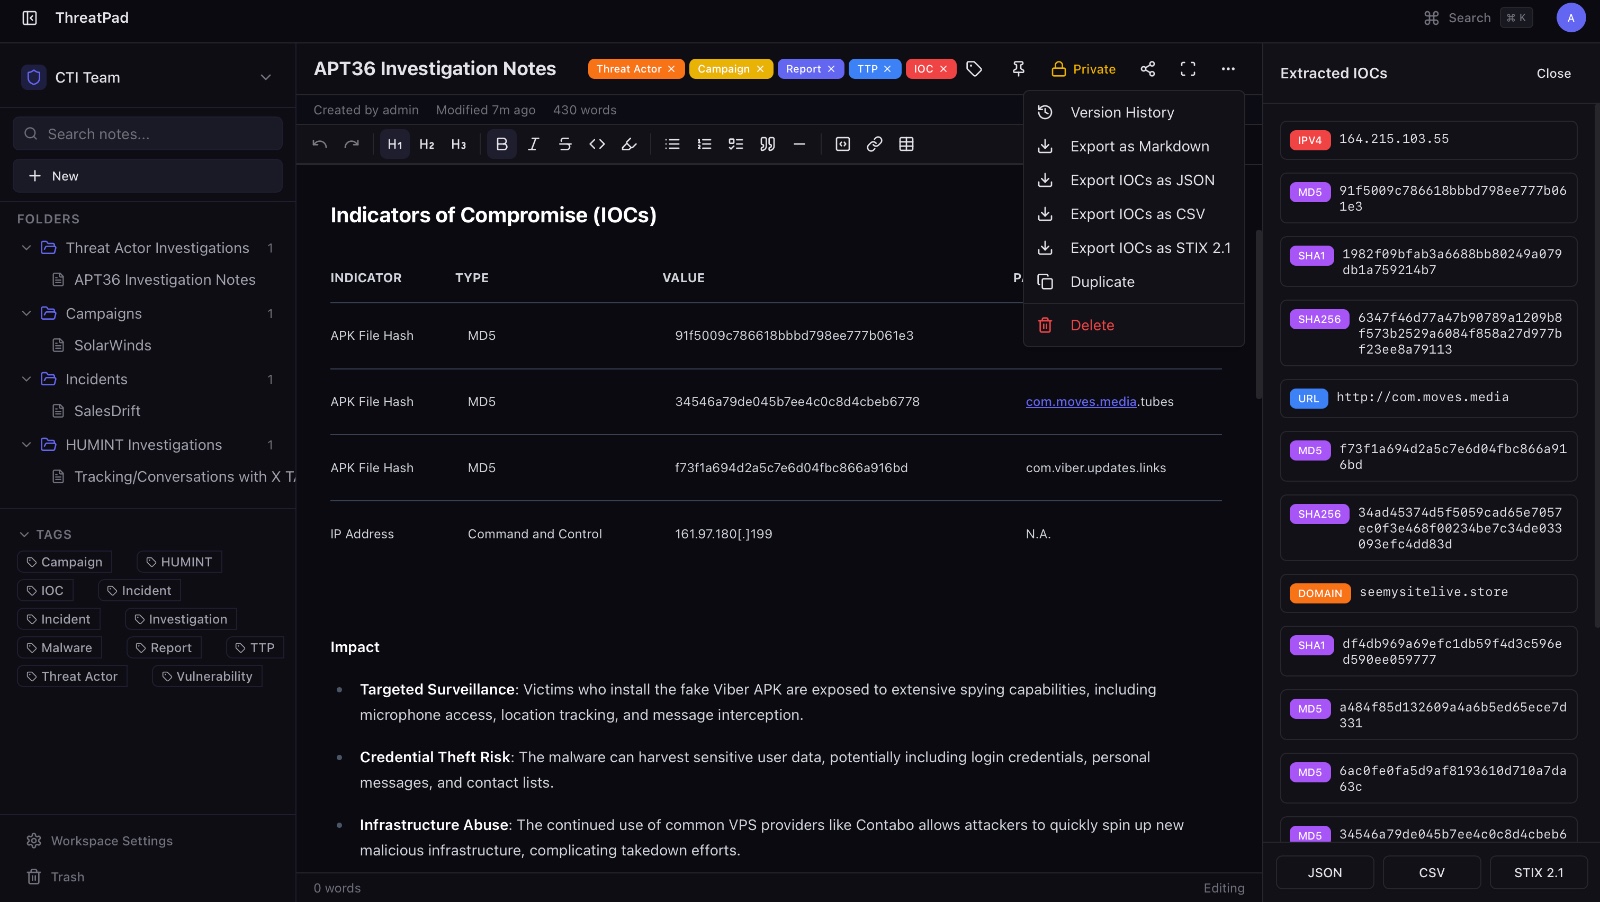 bhavikmalhotra/threatpad
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
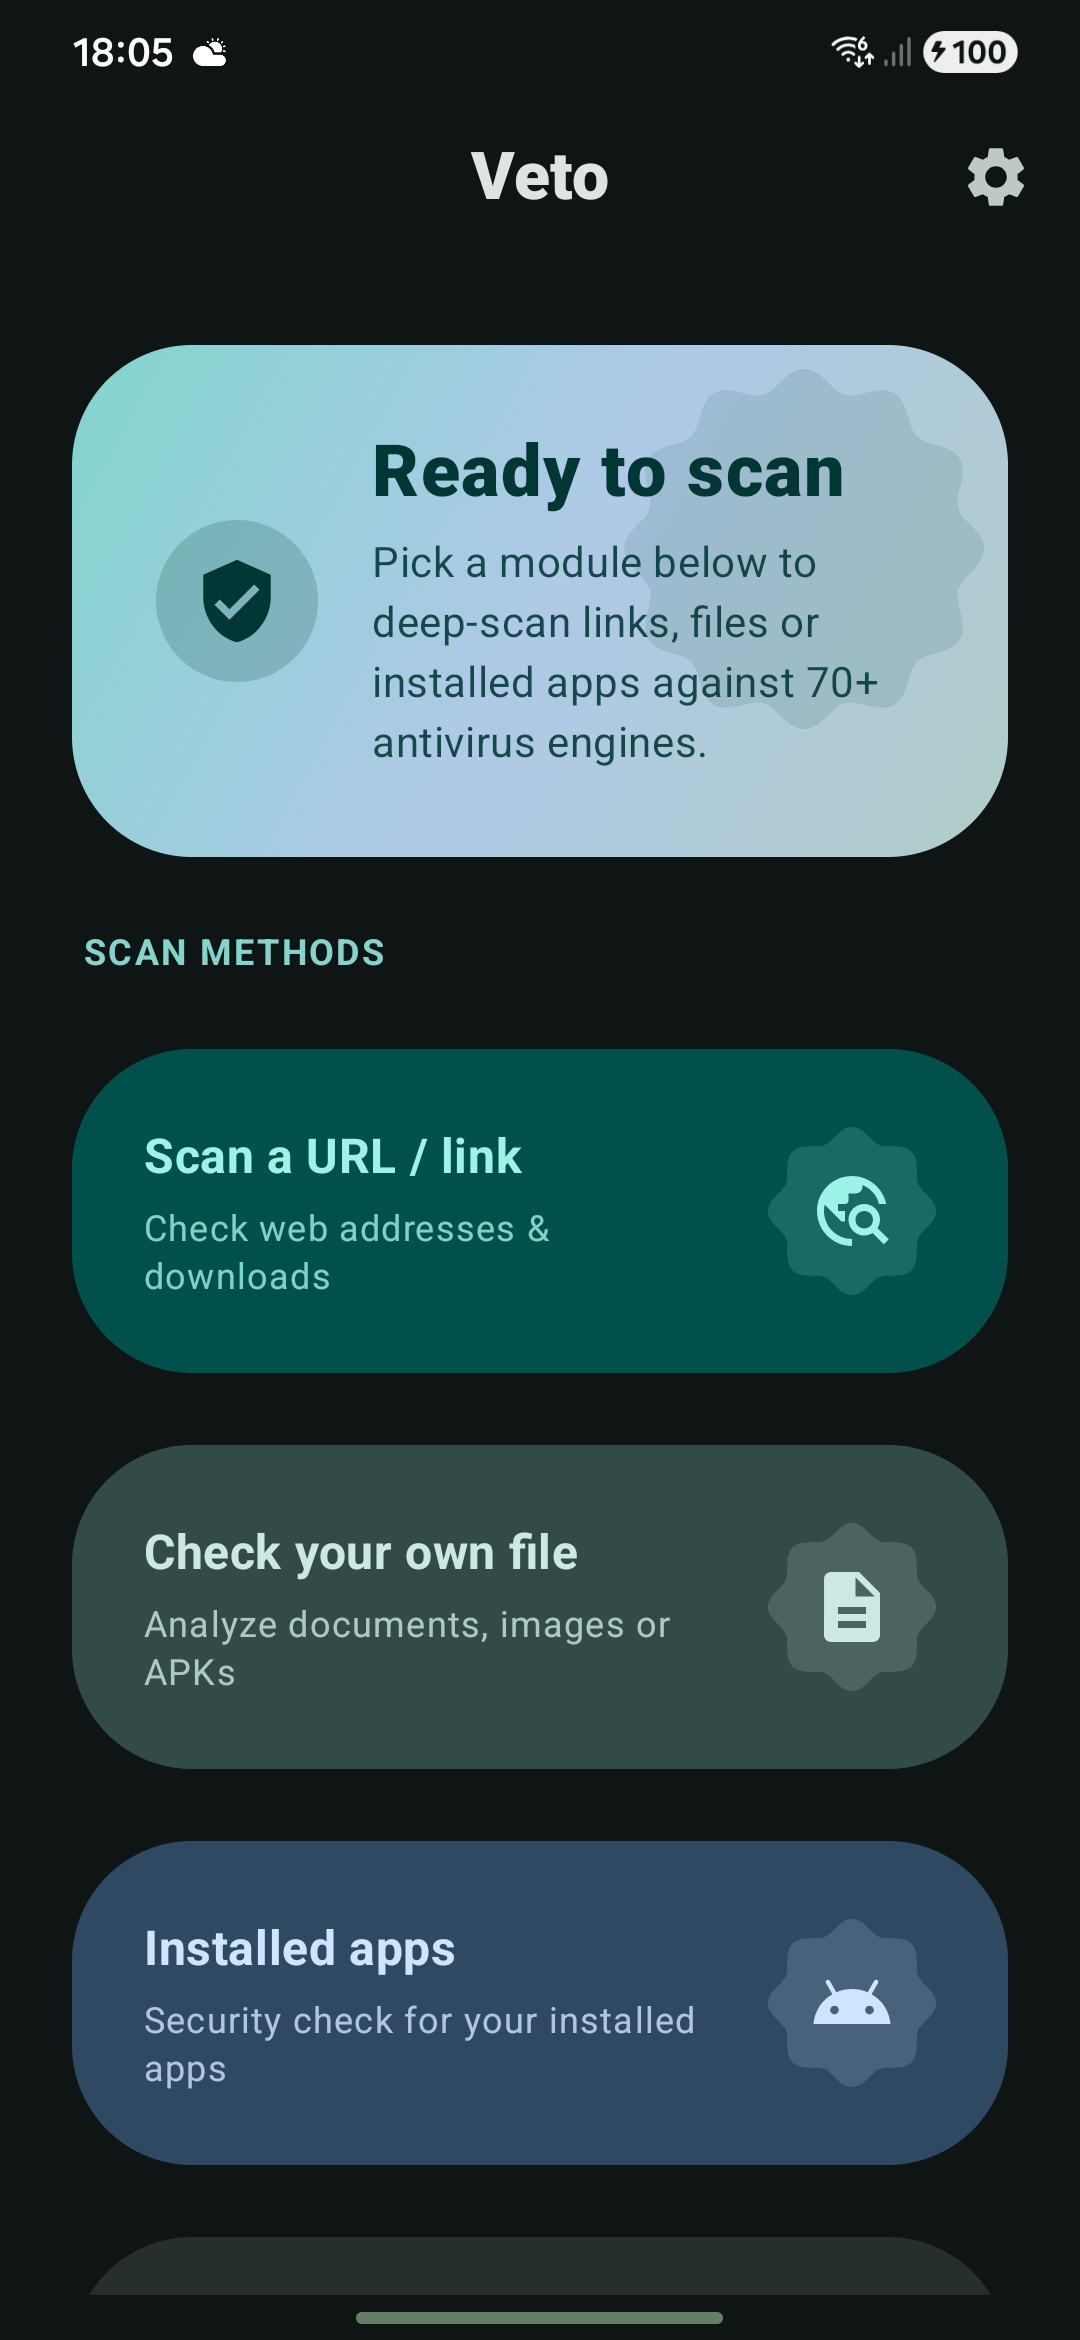 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
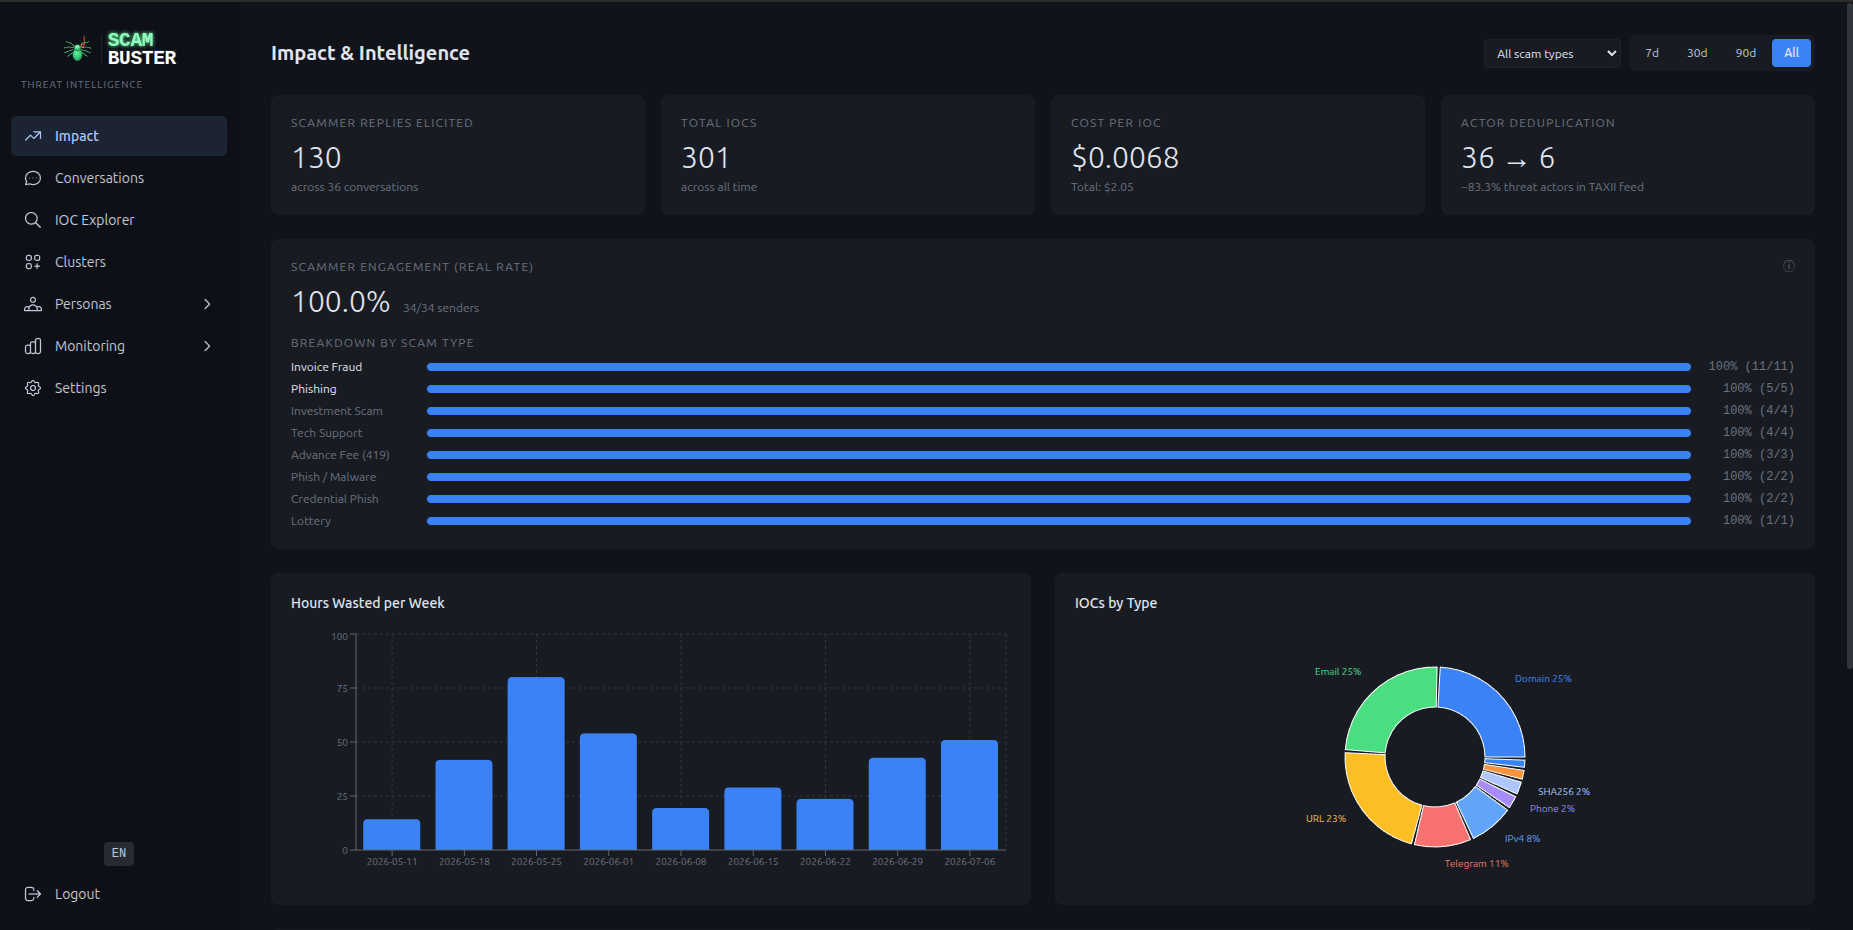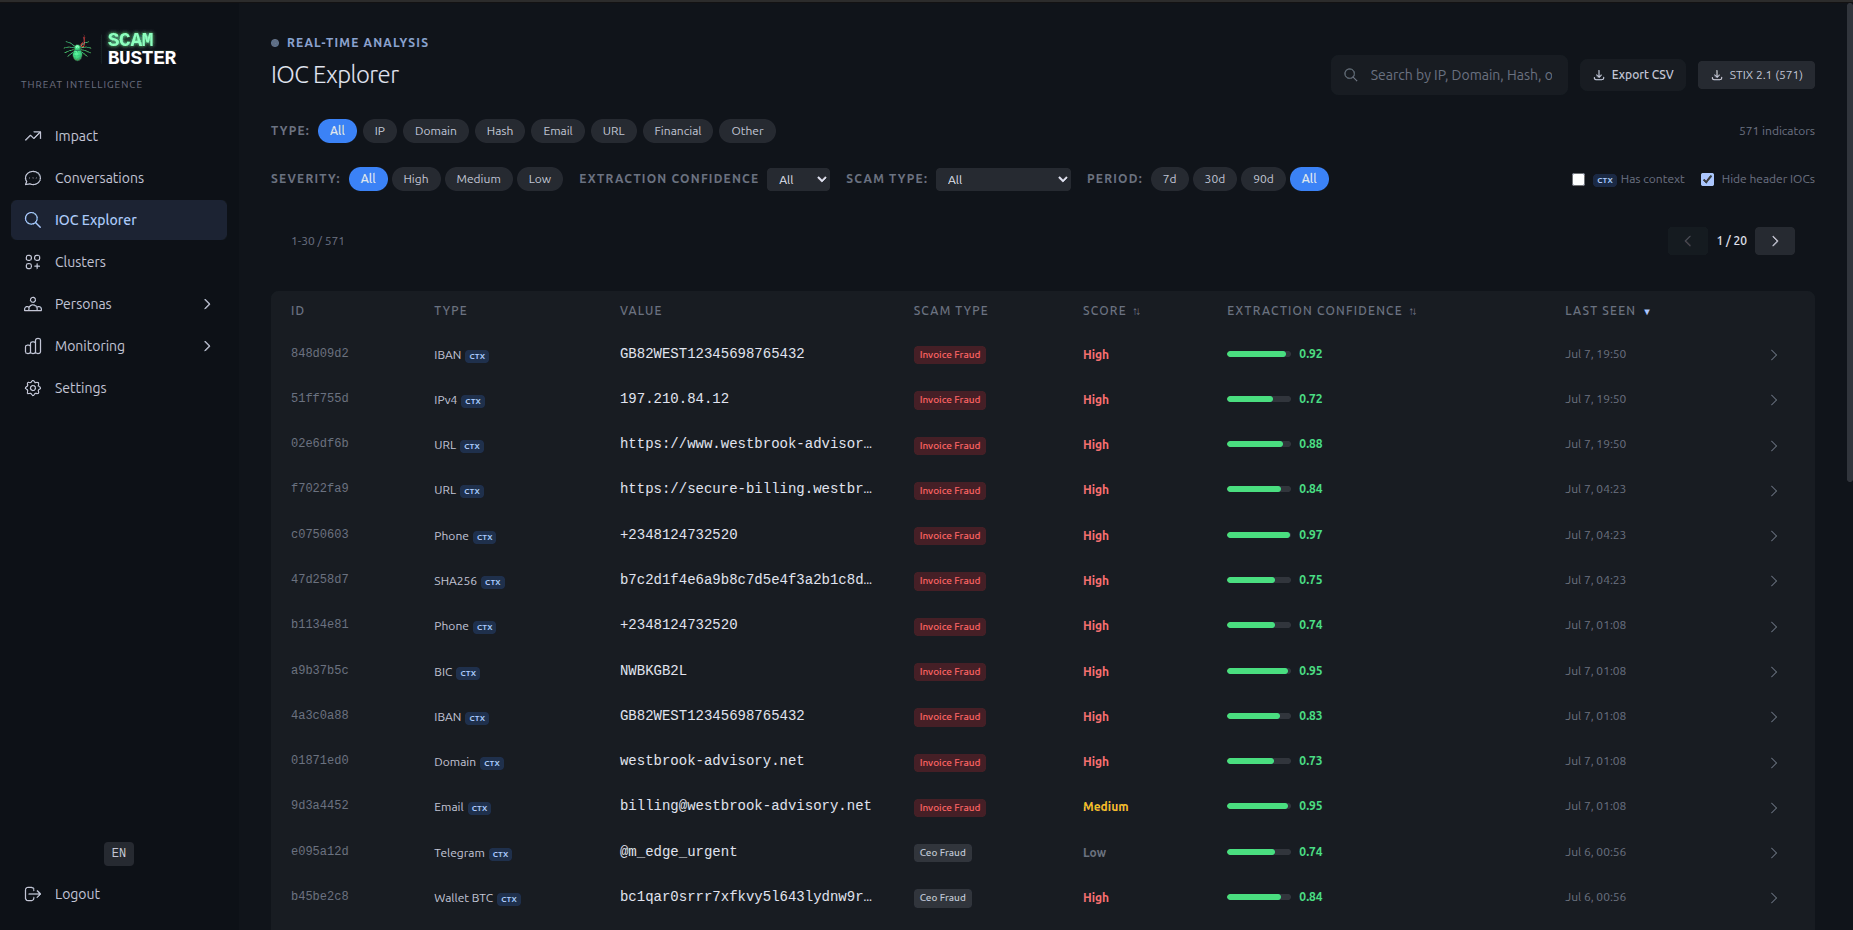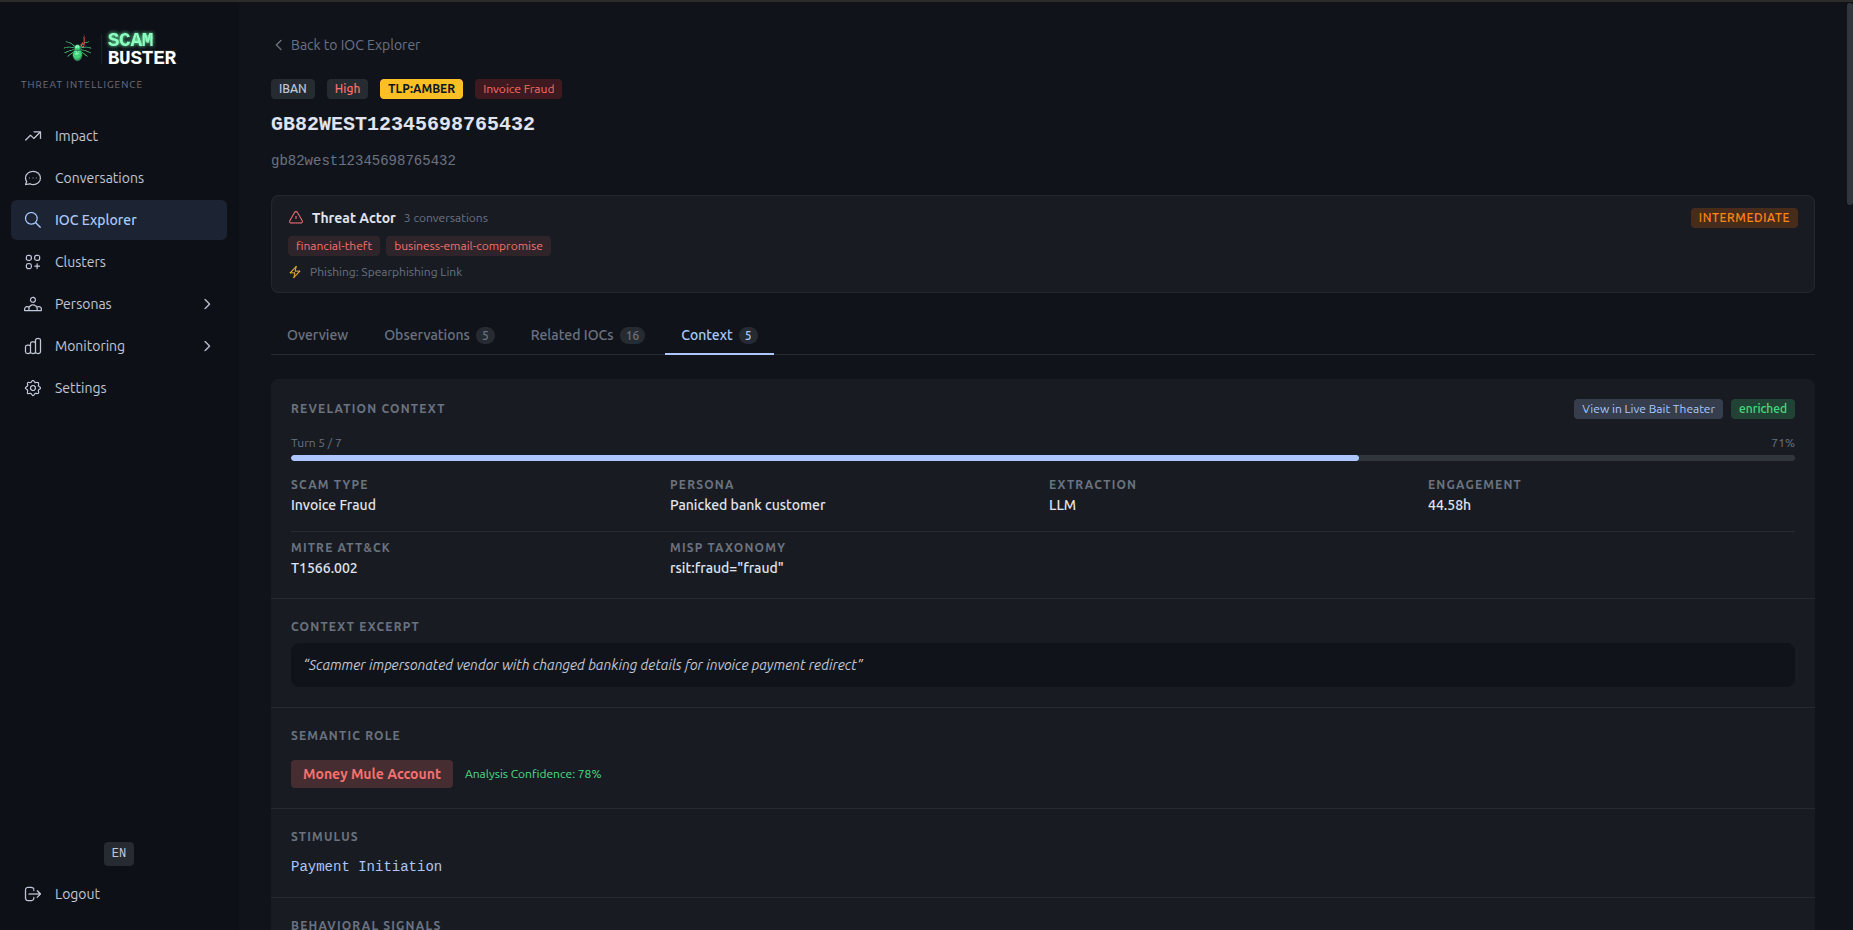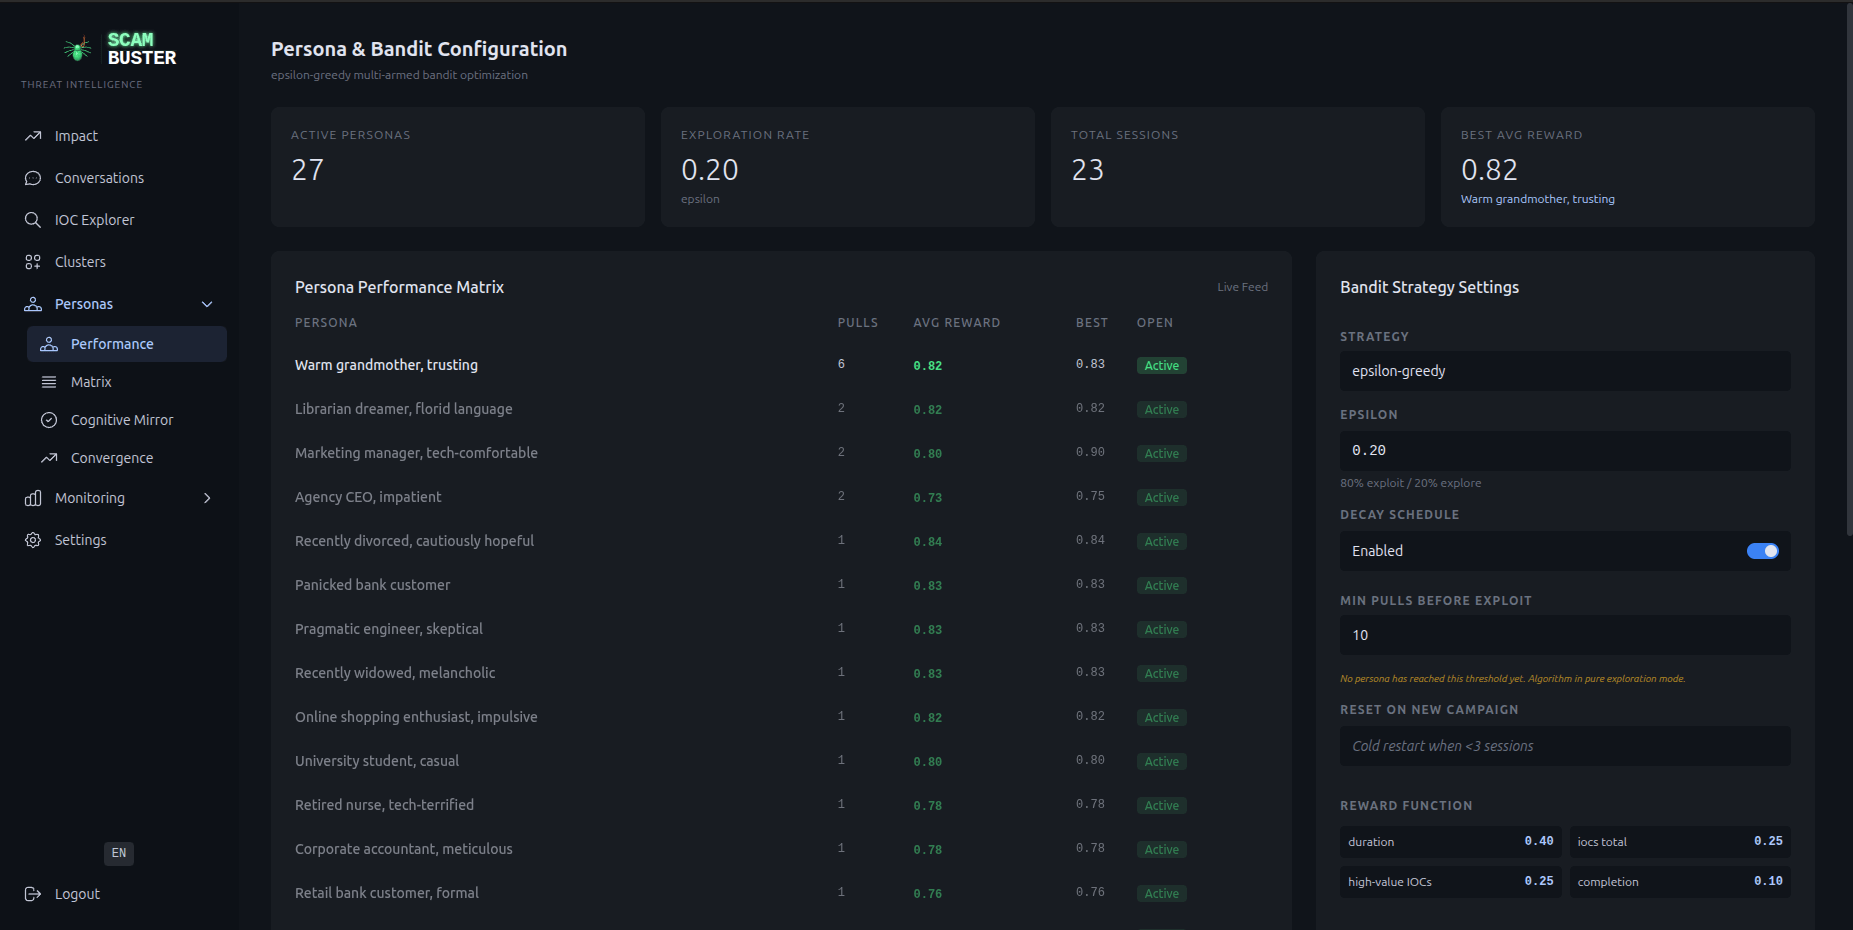 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…
 00gxd14g/misp-extractor
Extracts selected MISP attributes, including IP addresses, URLs, and hashes, into reusable output files.
 infostealers-stats/credential-and-breach-monitoring
This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
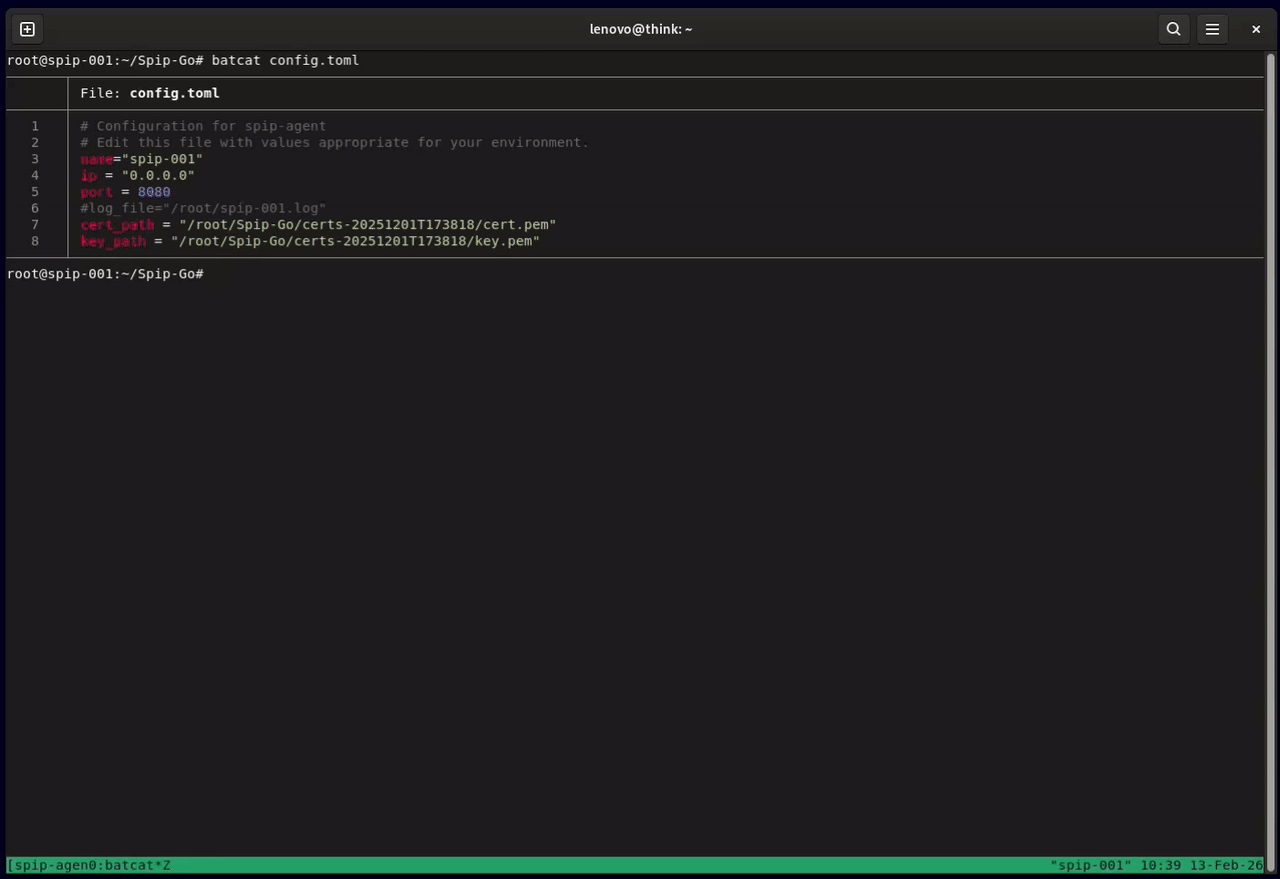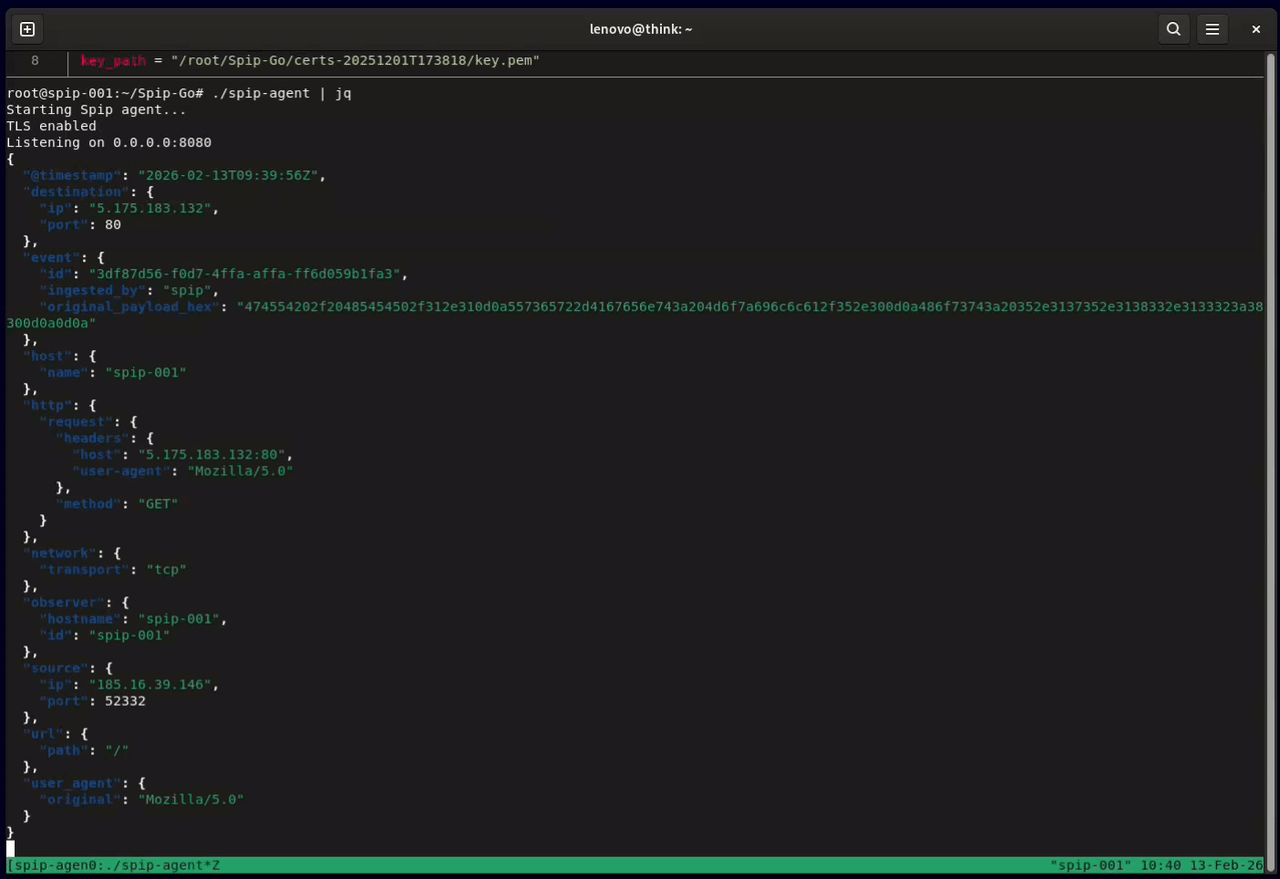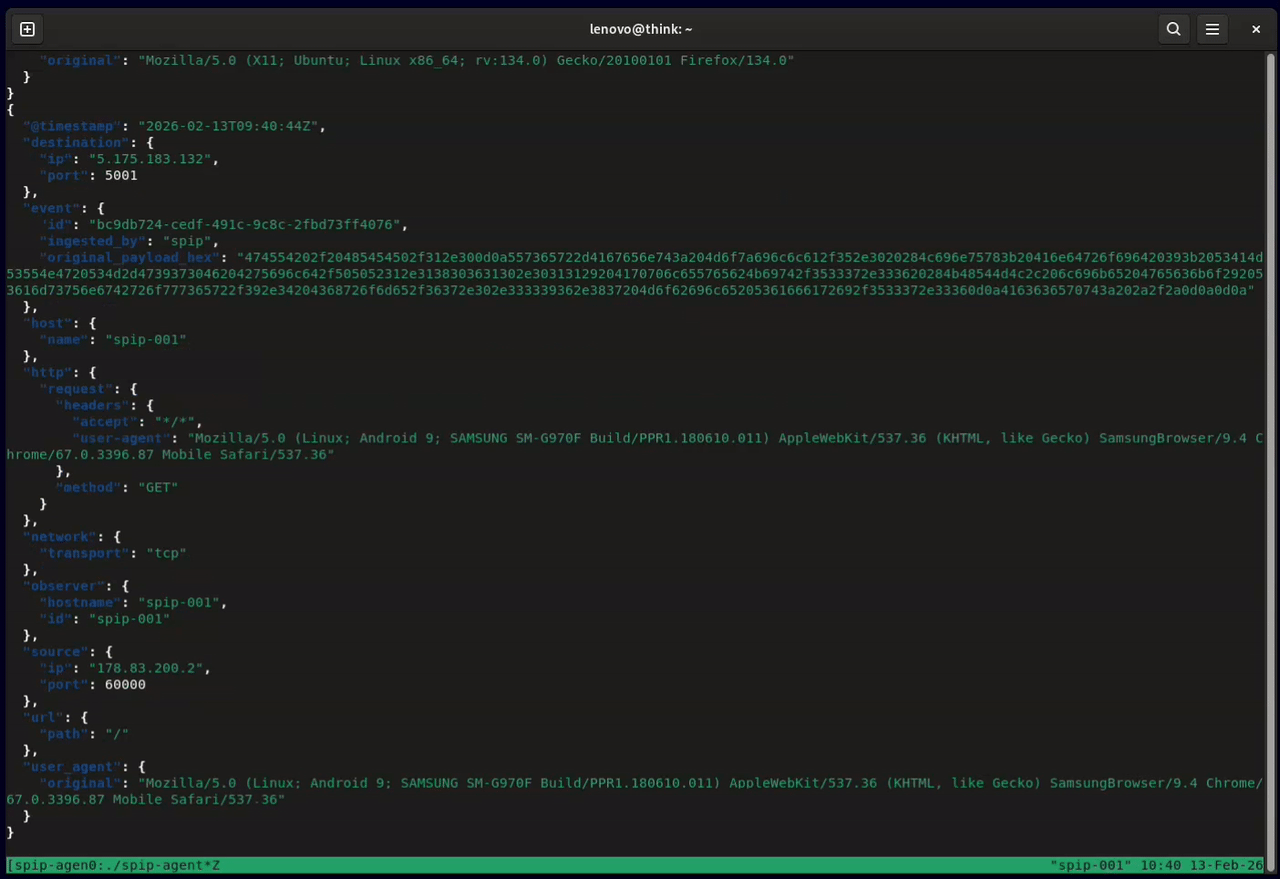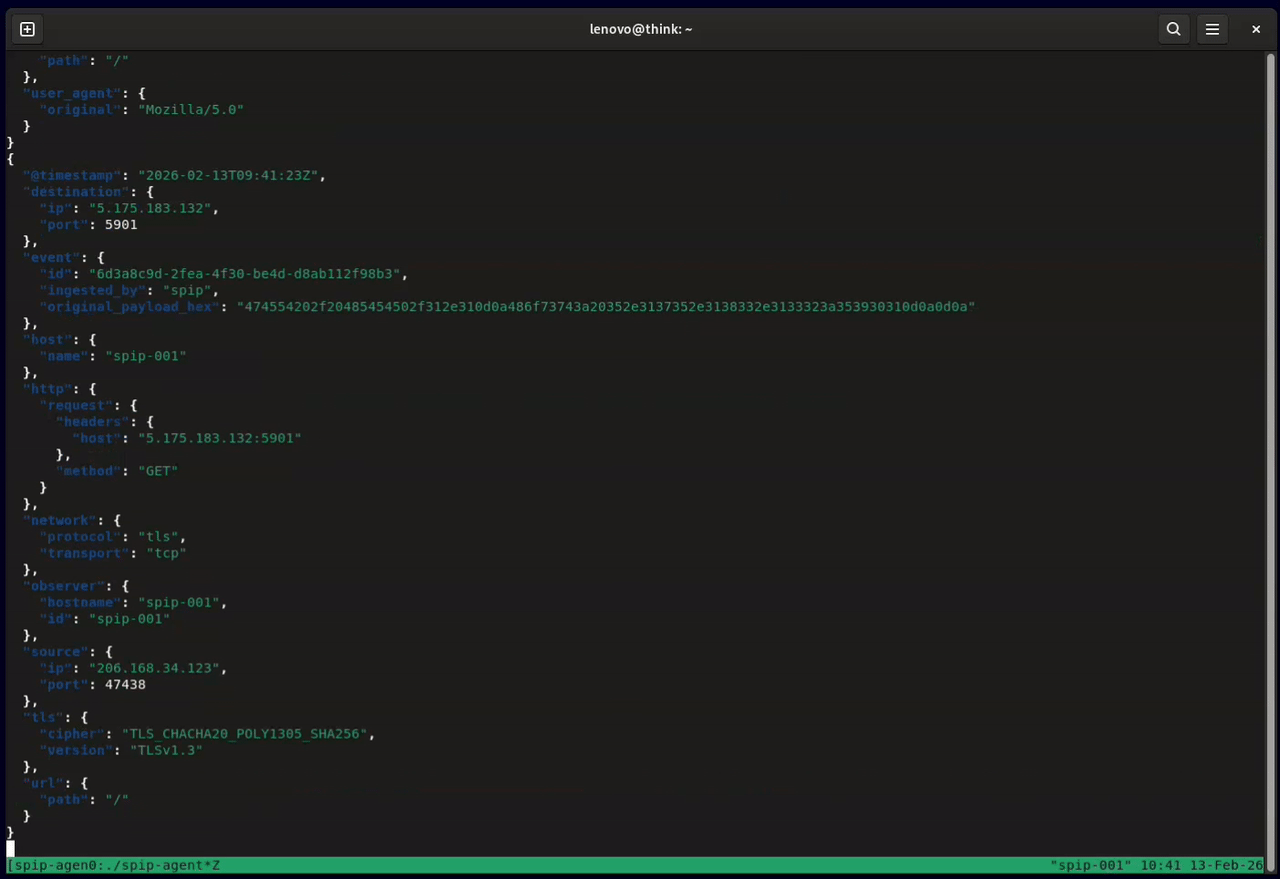 honeylabshq/spip-go
Spip network sensor written in Go
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
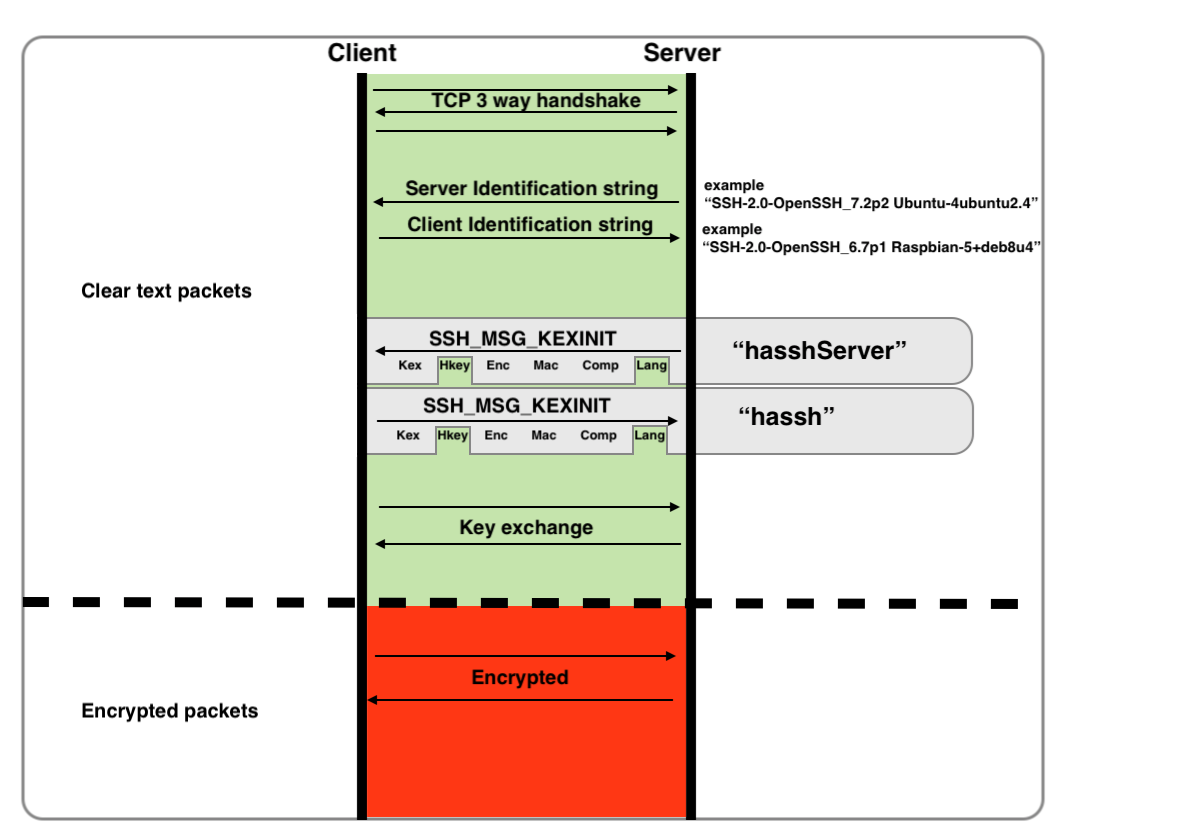 corelight/hassh
Fingerprint SSH clients and servers.