ndaal_public_SBOM_Auditor

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)

Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…

This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…

This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…

A read-only, passive scanner that checks a REDCap host for exposure to and compromise by **CVE-2026-90817** — the unauthenticated survey-endpoint…


Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…

Python Decoders for Common Remote Access Trojans

Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…

Malicious Extension Database

Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…

A curated collection of DFIR skills and workflows for InfoSec practitioners.


TAXII server implementation in Python from EclecticIQ

Resources for DFIR Professionals Responding to the REvil Ransomware Kaseya Supply Chain Attack

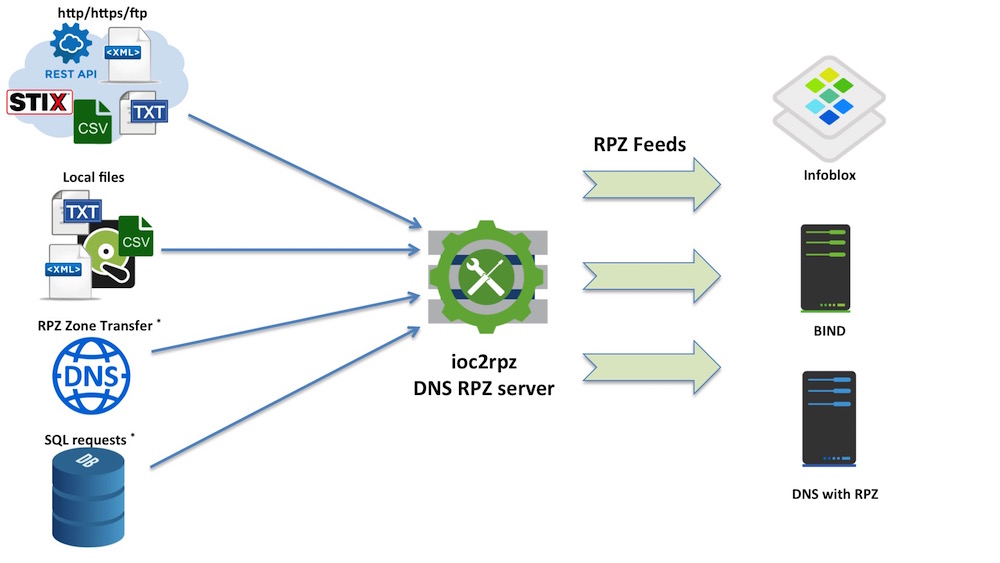
ioc2rpz is a place where threat intelligence meets DNS.