
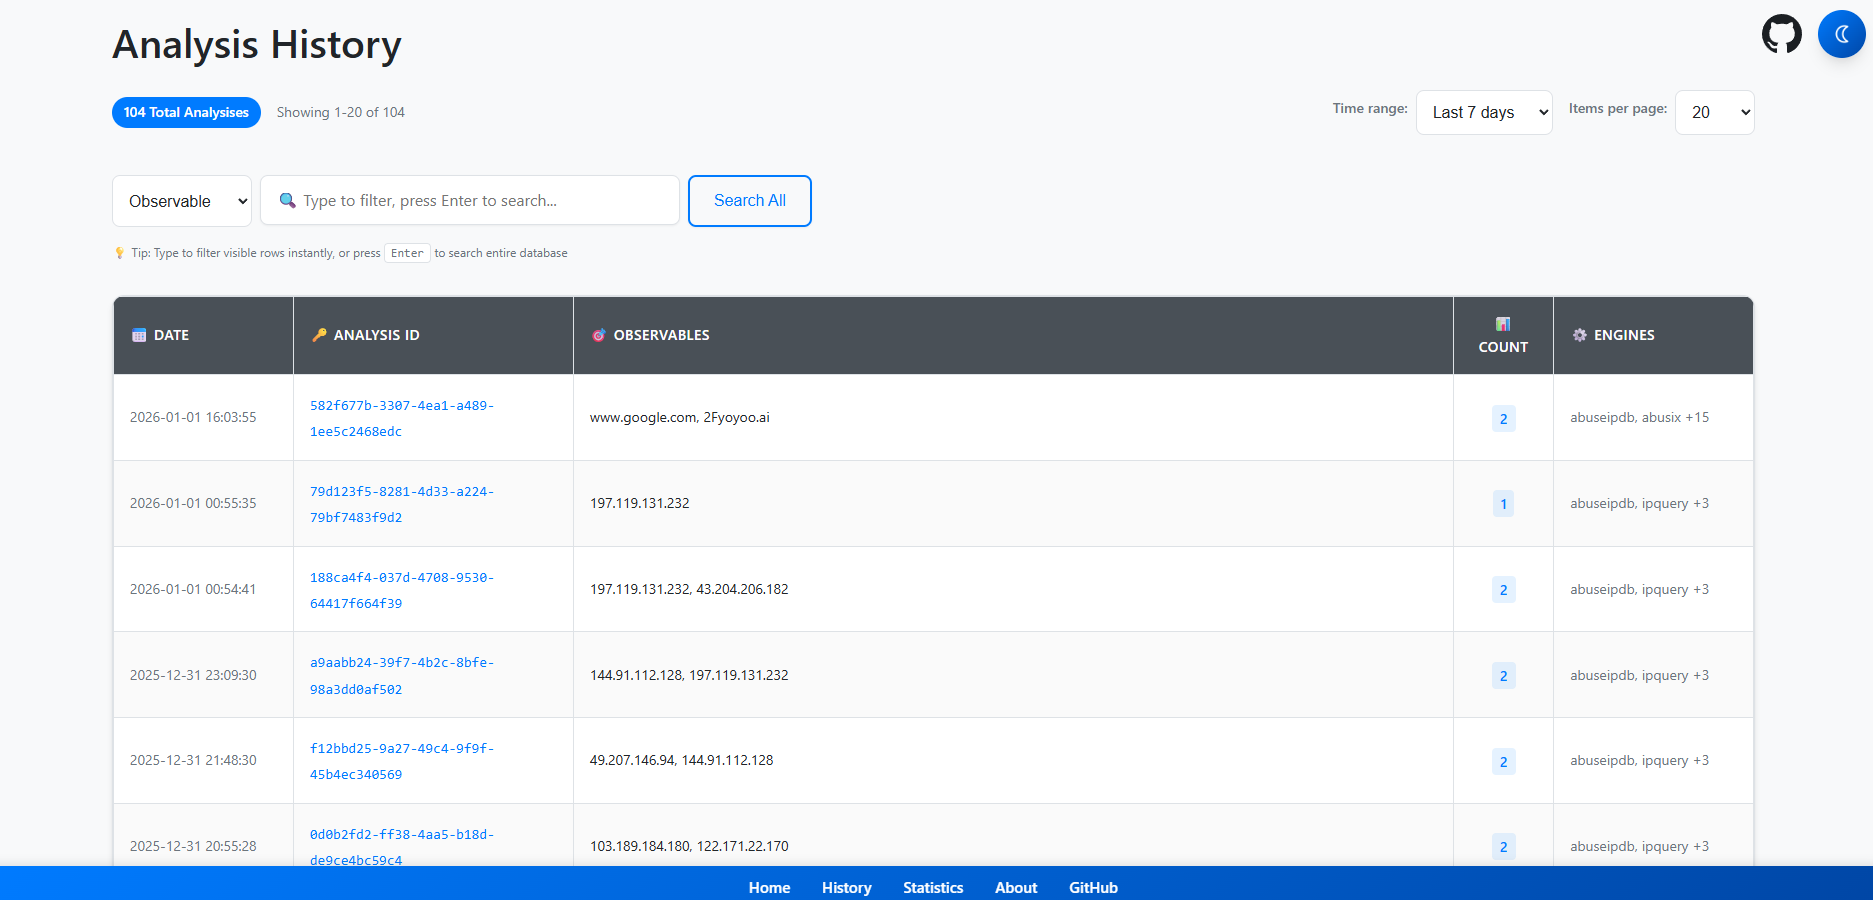
cyberbro
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
defensive-toolsdns-analysiseducation+9
687
stanfrbd/cyberbroA simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 executemalware/malware-iocs
Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…
 ncsc-nl/openssl-2022
Operational information regarding CVE-2022-3602 and CVE-2022-3786, two vulnerabilities in OpenSSL 3
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
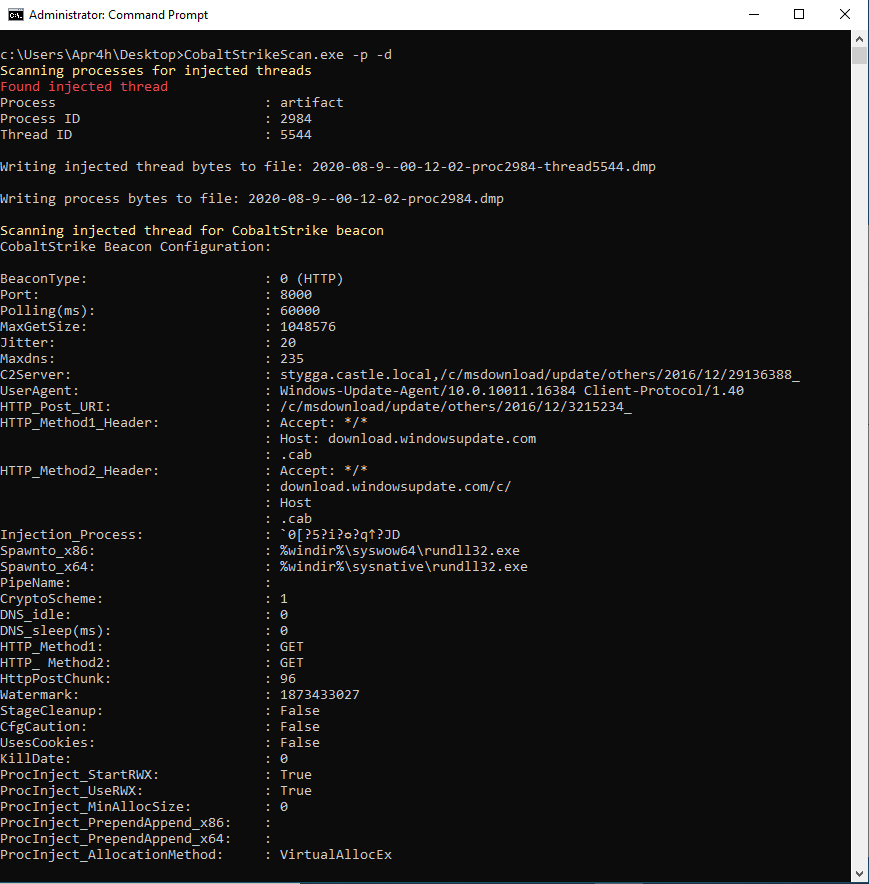 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 fhightower/ioc-finder
Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 paloaltonetworks/unit42-threat-intelligence-article-information
This is the repository for indicators of compromise (IOCs) and other data for threat intelligence articles posted on the Palo Alto Networks Unit 42…
 wiz-sec-public/wiz-research-iocs
Curated public database of indicators of compromise aggregated by Wiz Research for threat detection, hunting, and incident response workflows.
 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…