Detection-Tool-Kit-for-CVE-2026-31431

Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…

Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…

Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…

Comprehensive SOC analysis of Log4Shell (CVE-2021-44228) including technical breakdown, detection indicators, remediation strategies, and incident…

Claude Code skill to scan machines for Mini Shai-Hulud (CVE-2026-45321) supply chain worm IOCs

Curated vulnerability research repository with in-depth writeups, PoC scripts, and IOC detection tools for real-world security incidents like…

Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes vulnerability analysis, detection rules…

Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…

IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…

Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…

Defender-focused reference pack for CVE-2025-68645 Zimbra LFI, including Sigma/Splunk detection rules, WAF mitigation snippets, IOC patterns, and…

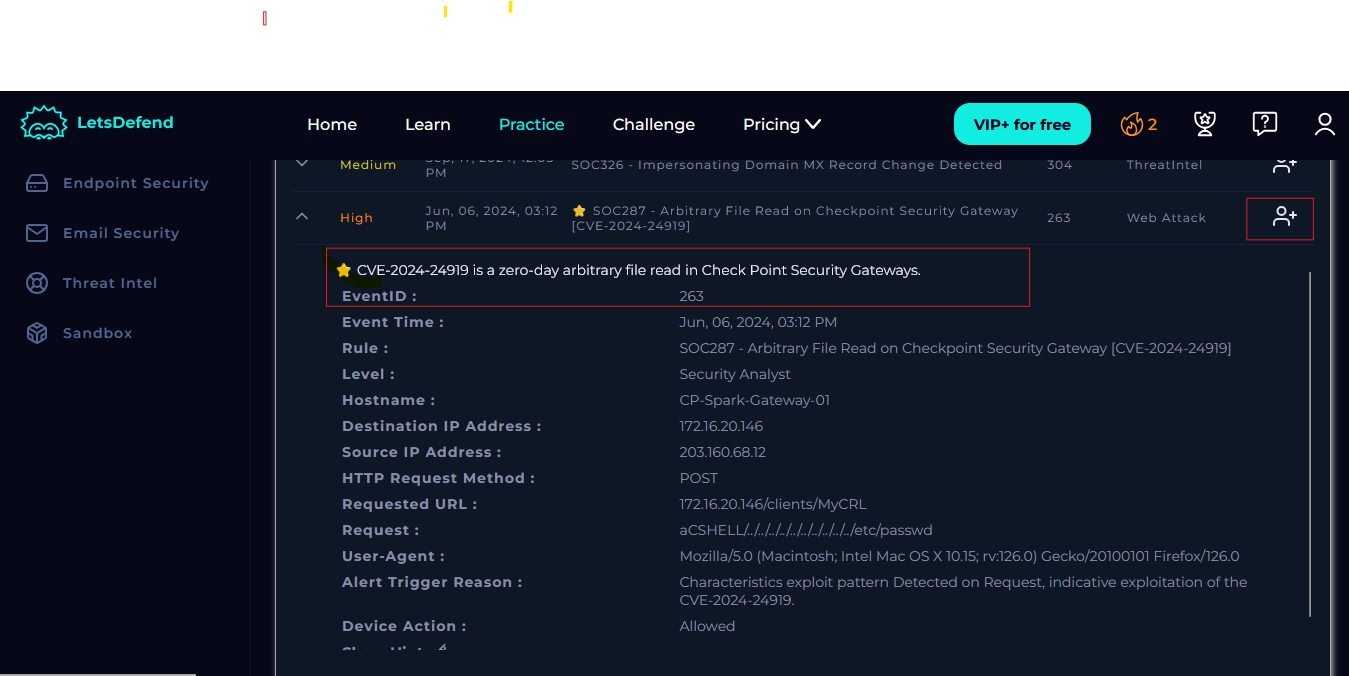
Step-by-step SOC incident response walkthrough for CVE-2024-24919 arbitrary file read on Check Point gateways, covering detection, analysis,…

Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.

Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…

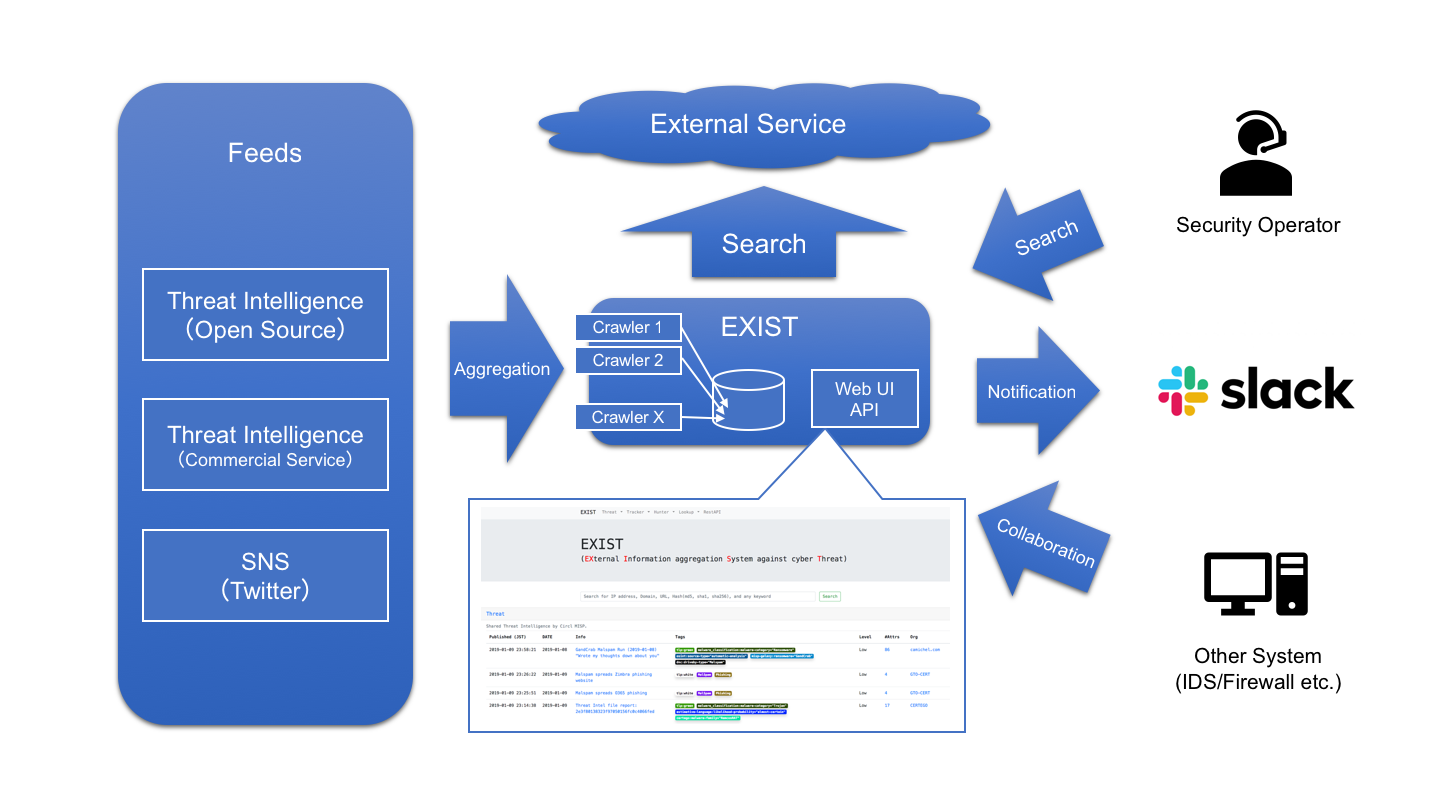
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

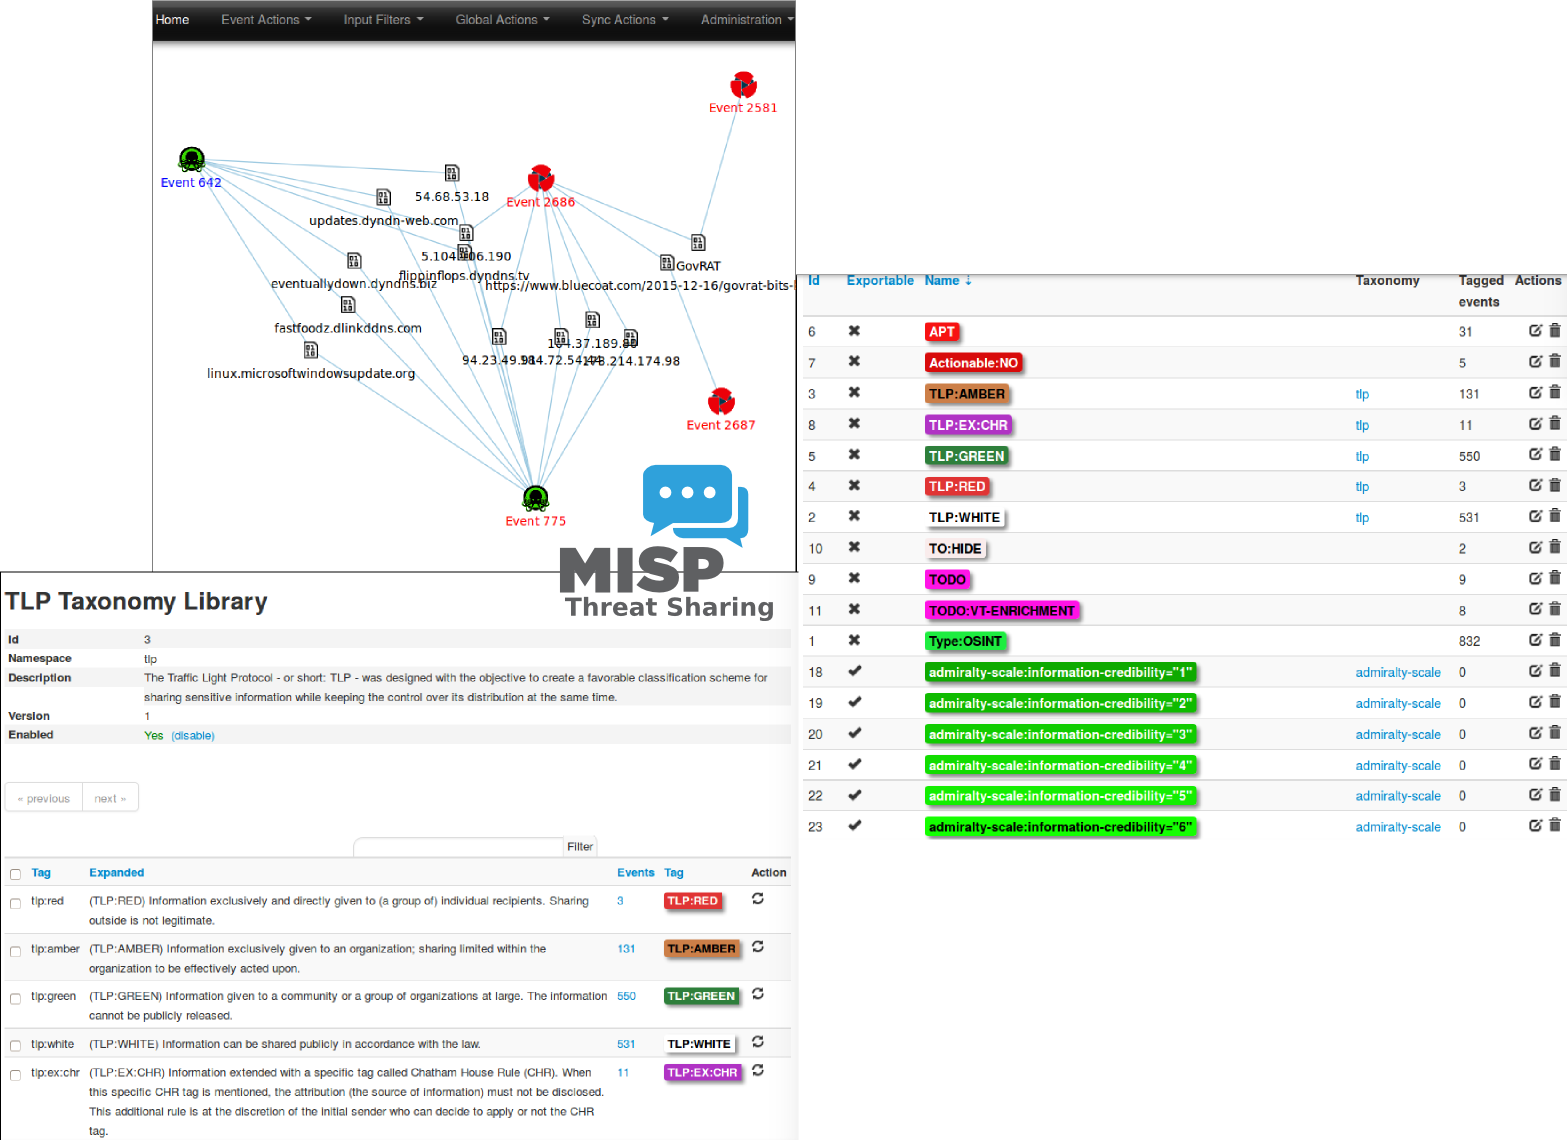
MISP (core software) - Open Source Threat Intelligence and Sharing Platform

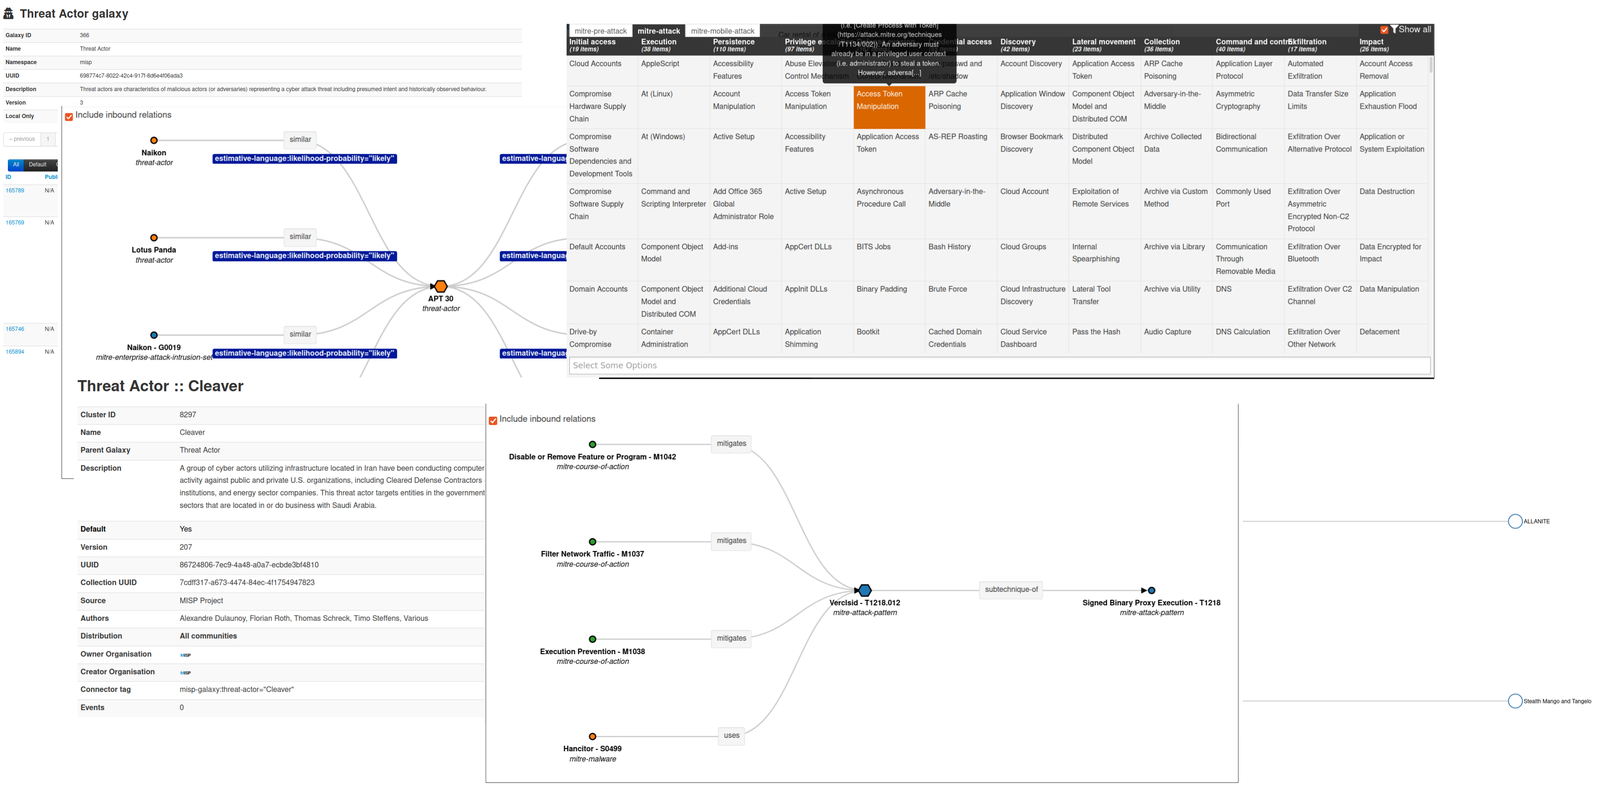
Clusters and elements to attach to MISP events or attributes (like threat actors)

Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.

No longer maintained. Please refer to Google Threat Intelligence / Virus Total collections.