
irdoc-app
 soc-irdoc/irdoc-app
Incident Response Documentation Platform
defensive-toolsdigital-forensicseducation+5
soc-irdoc/irdoc-appIncident Response Documentation Platform
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
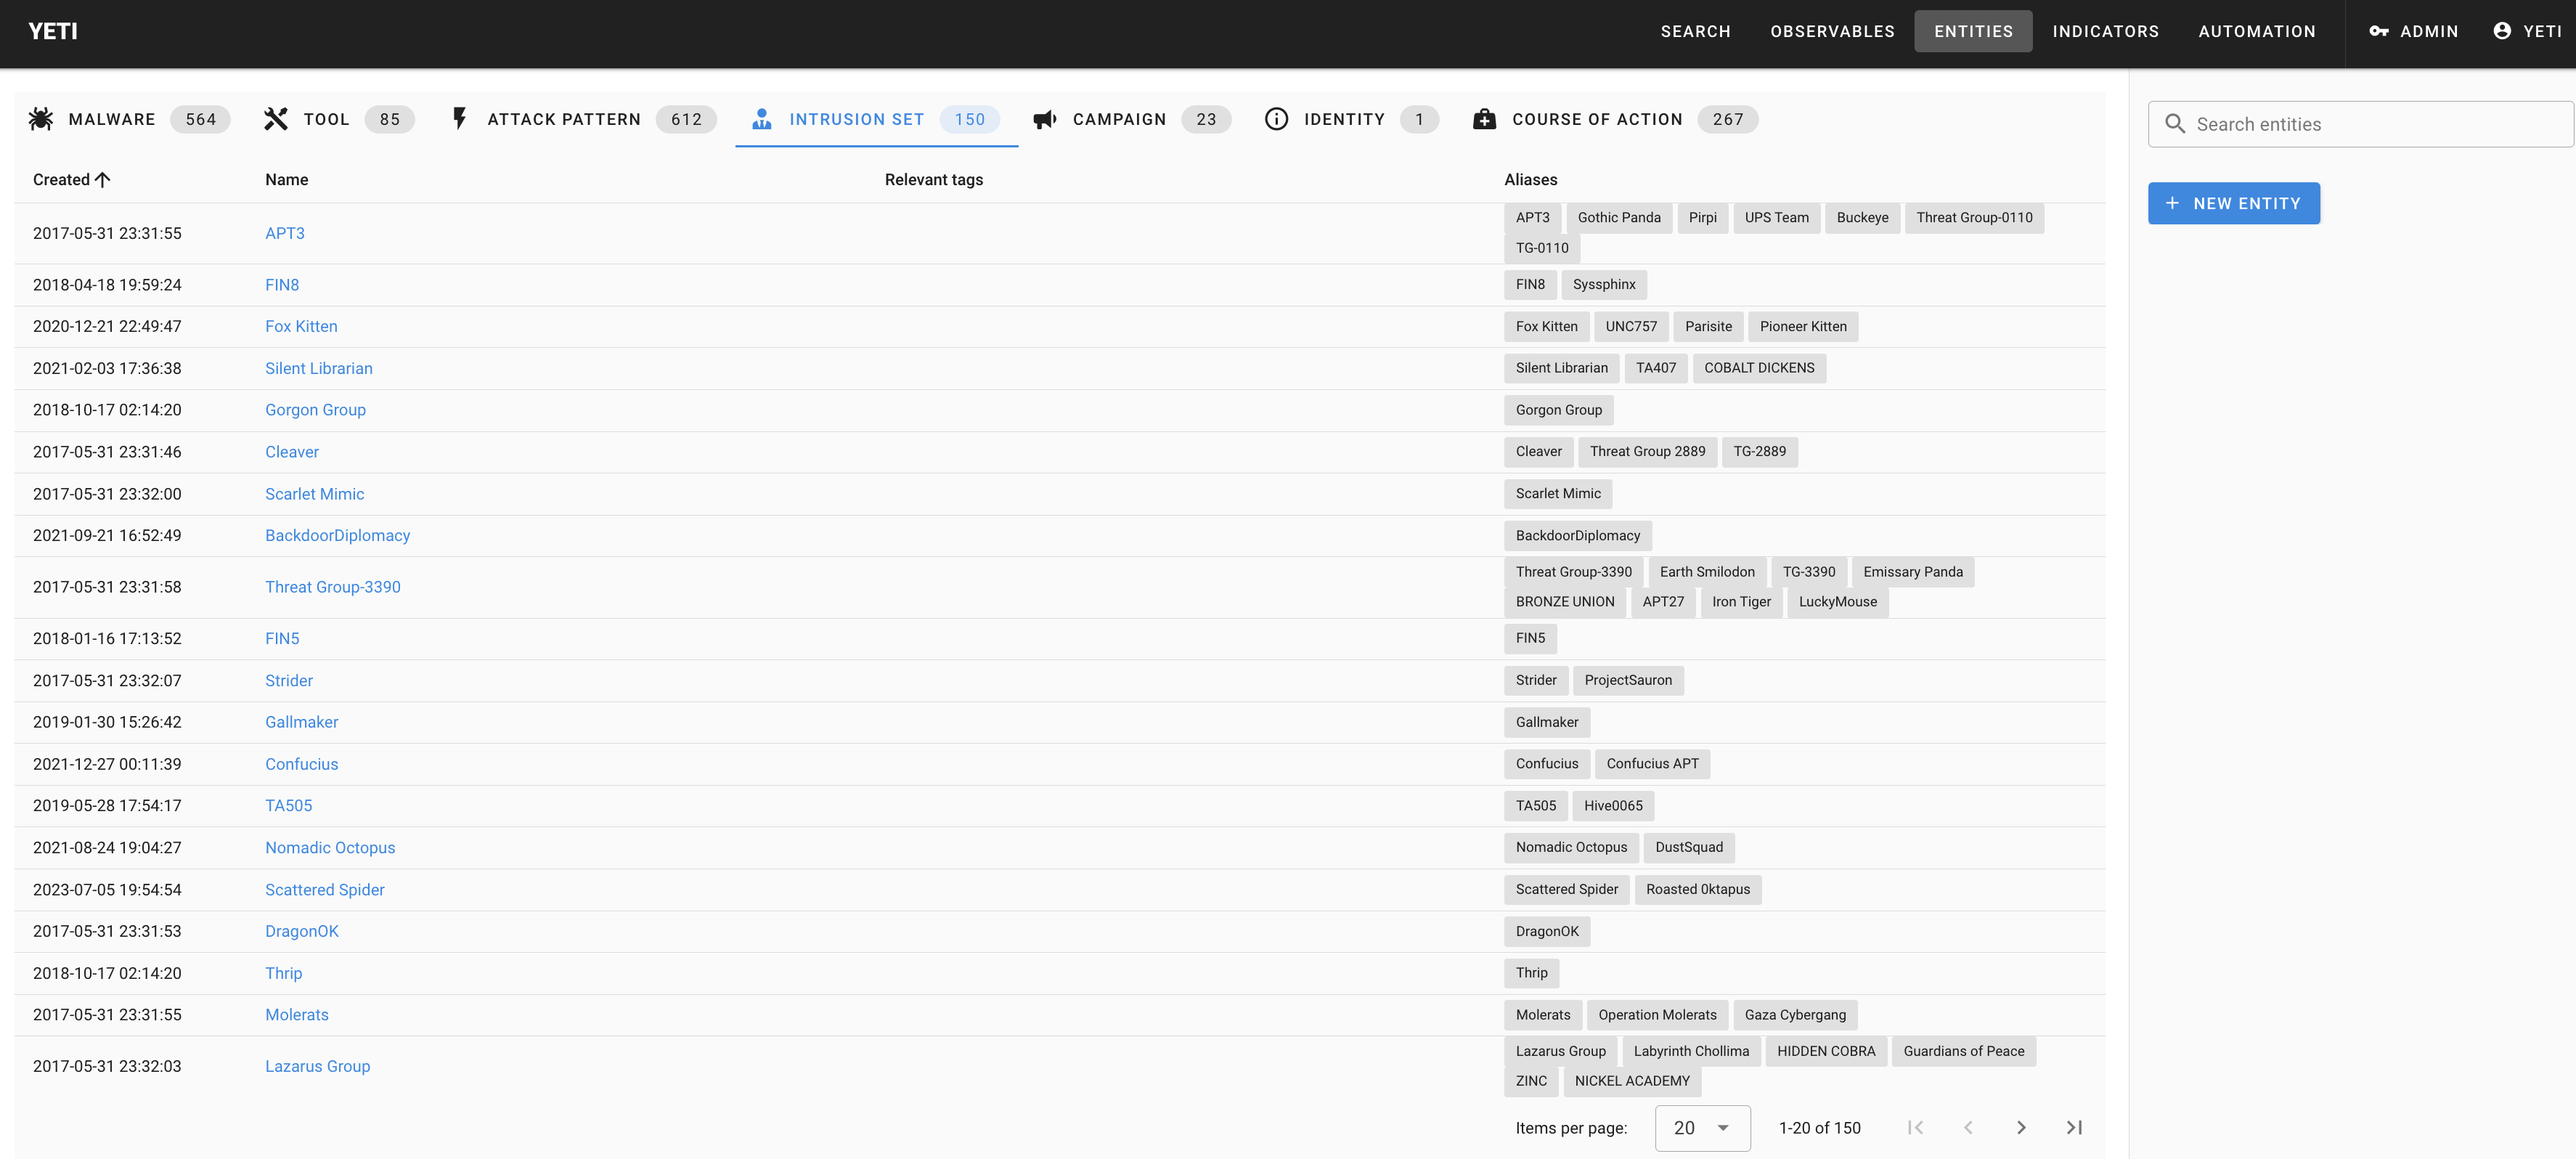
 toborrm9/malicious_extension_sentry
Malicious Extension Database
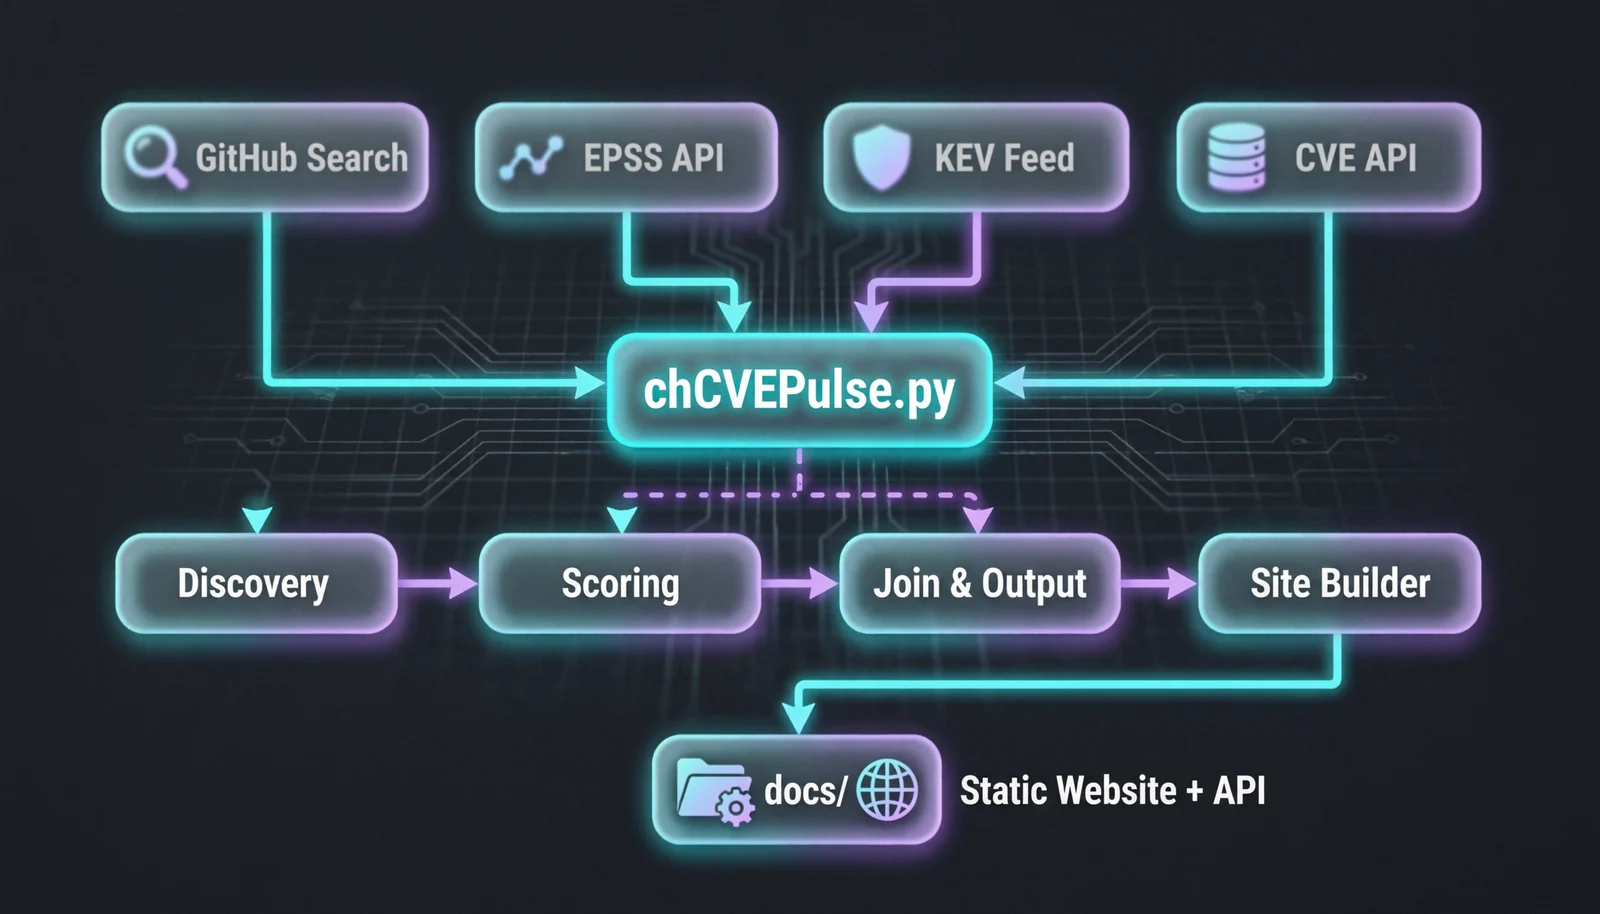 ch4120n/ch4120n-cve-pulse
Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence
 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
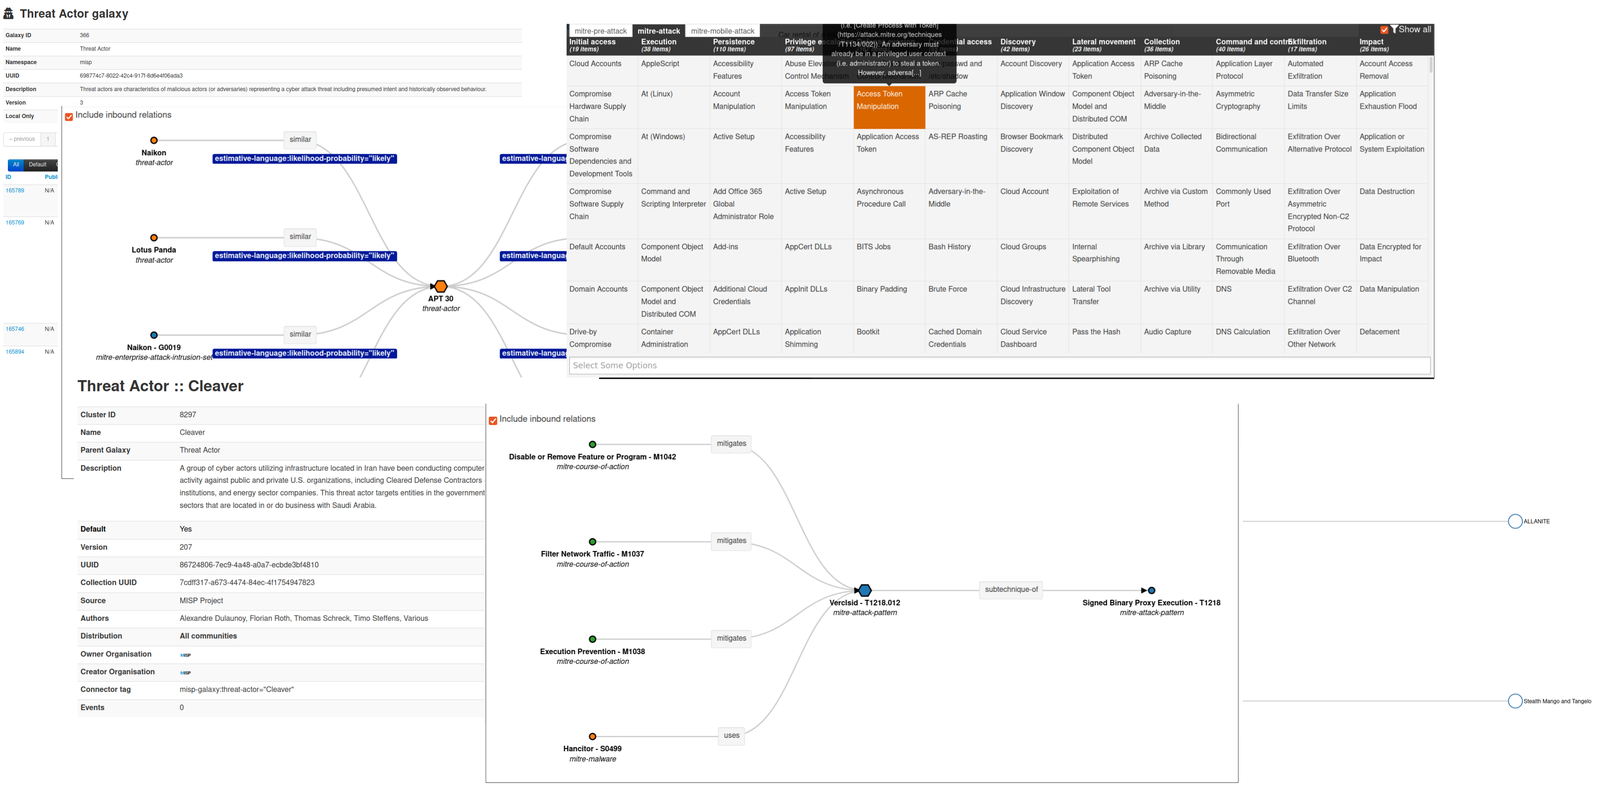 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 dahnutz/zimbra-cve-2026-73570-ir
Detection-first incident-response toolkit for Zimbra administrators investigating CVE-2026-73570. Searches logs for exploit indicators, examines…
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 securewithumer/exploit-index
The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and Threat…
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…