

malware-iocs
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
curated-resourcesforensicsincident-response+4
244
doctorwebltd/malware-iocsCurated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 kiteworks/security-advisories
Publishes Kiteworks security advisories and CVE disclosures, including vulnerability details, disclosure policy, and bug bounty information for…
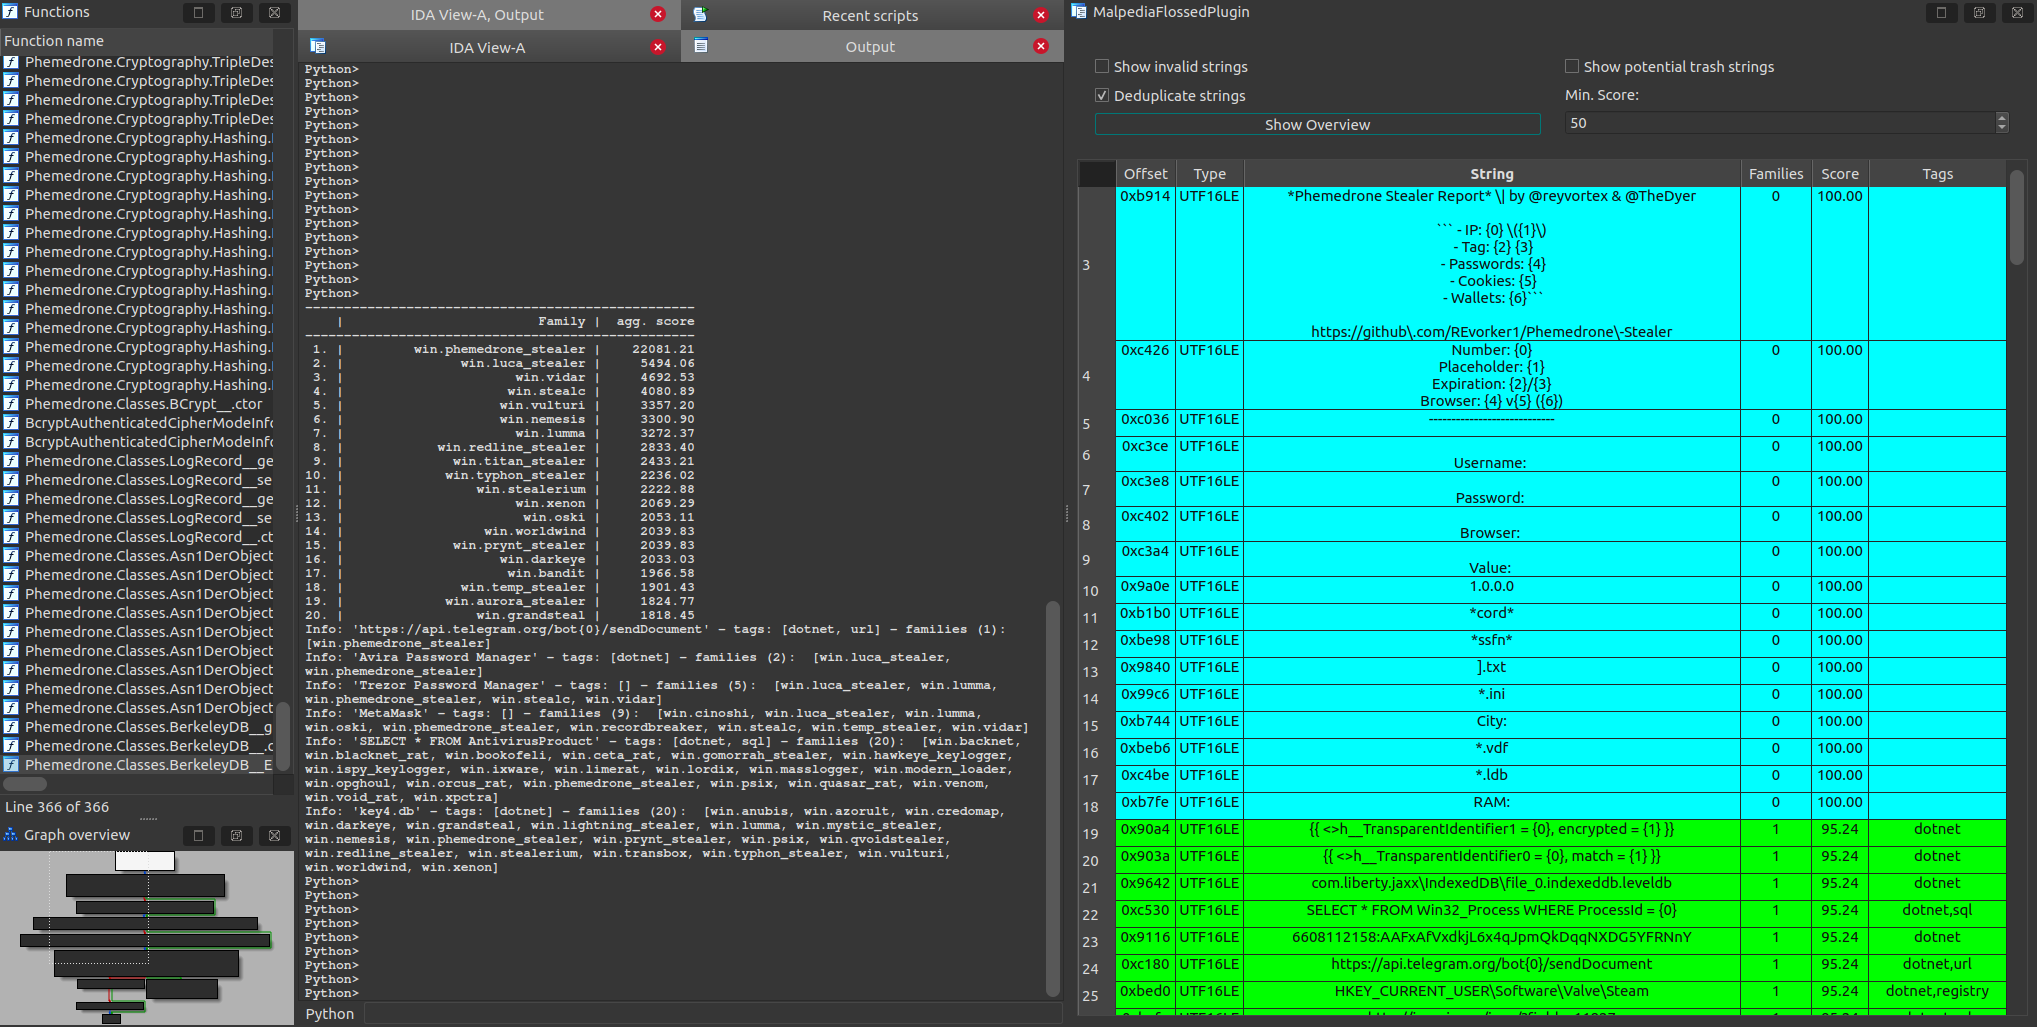 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 swaybs/cve-2024-3400
Python script to check Palo Alto firewalls for CVE-2024-3400 exploit attempts
 hahasagined/cve-2024-3400
External Dynamic List (EDL) of IP addresses actively exploiting CVE-2024-3400, for use in firewall and SIEM blocklists to defend against ongoing…
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 ma1am/cve-2022-26134-exploit-detection
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…
 cert-lv/exchange_webshell_detection
Detect webshells dropped on Microsoft Exchange servers exploited through "proxylogon" group of vulnerabilites (CVE-2021-26855, CVE-2021-26857,…