

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
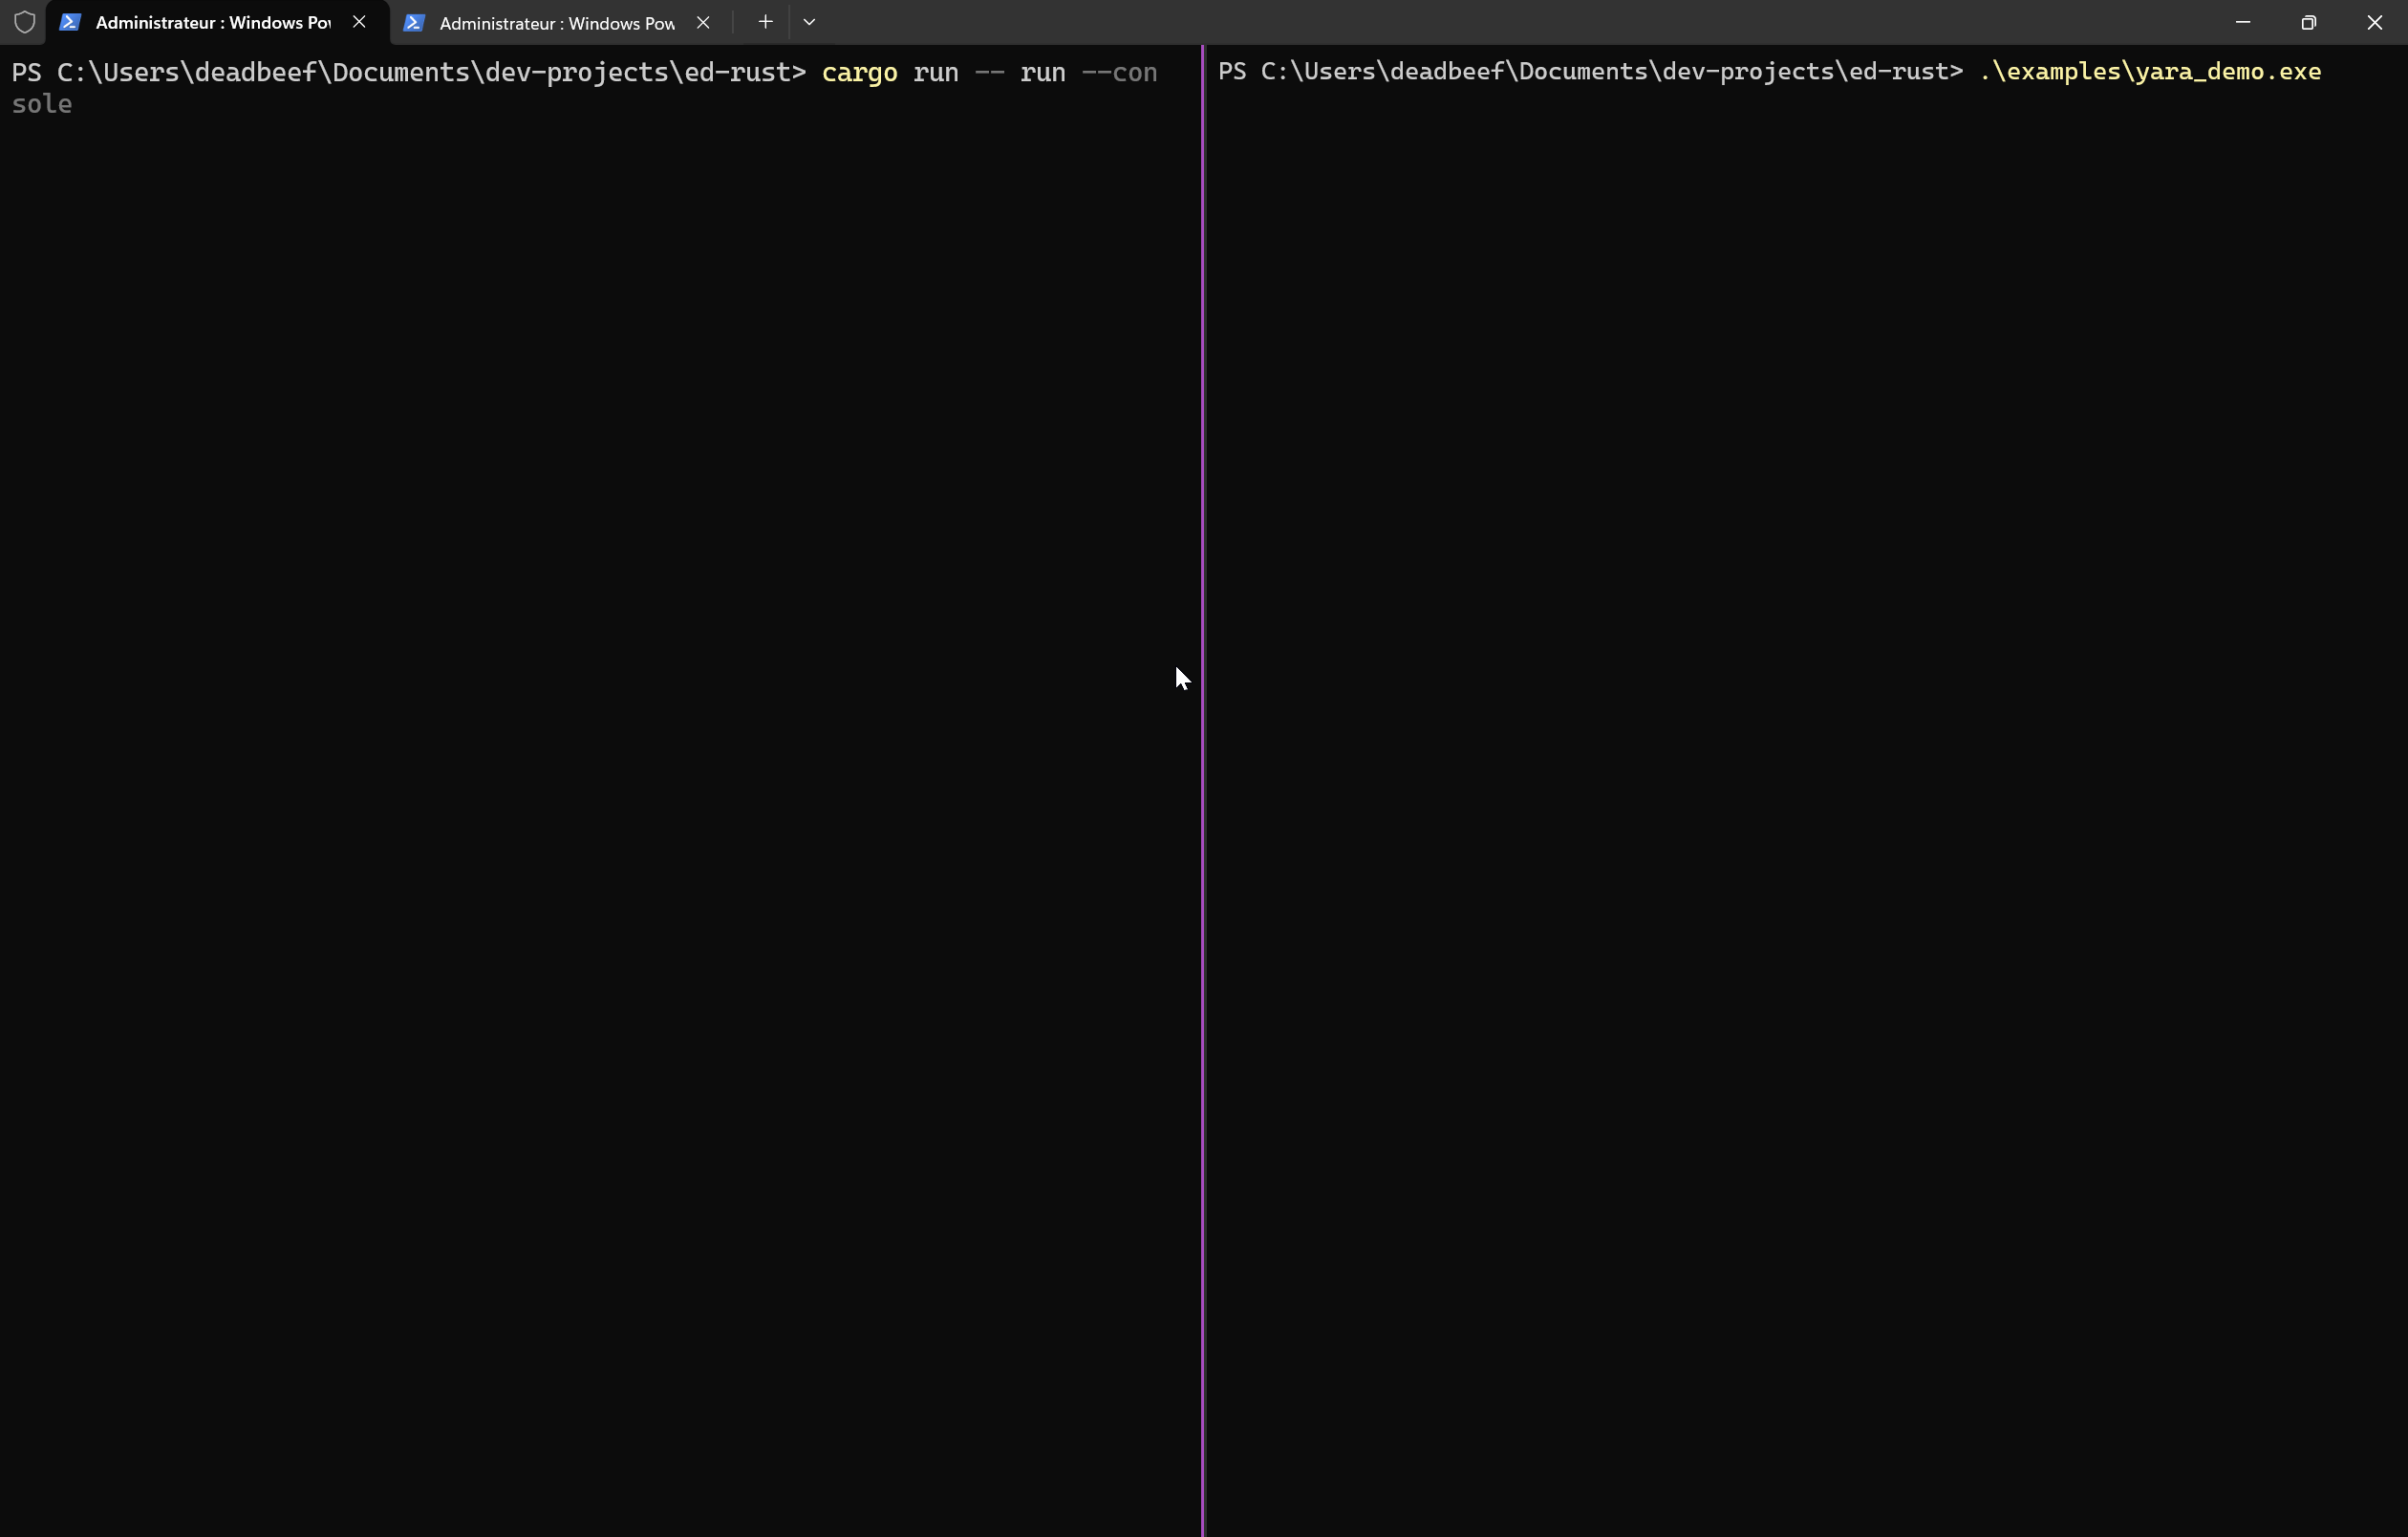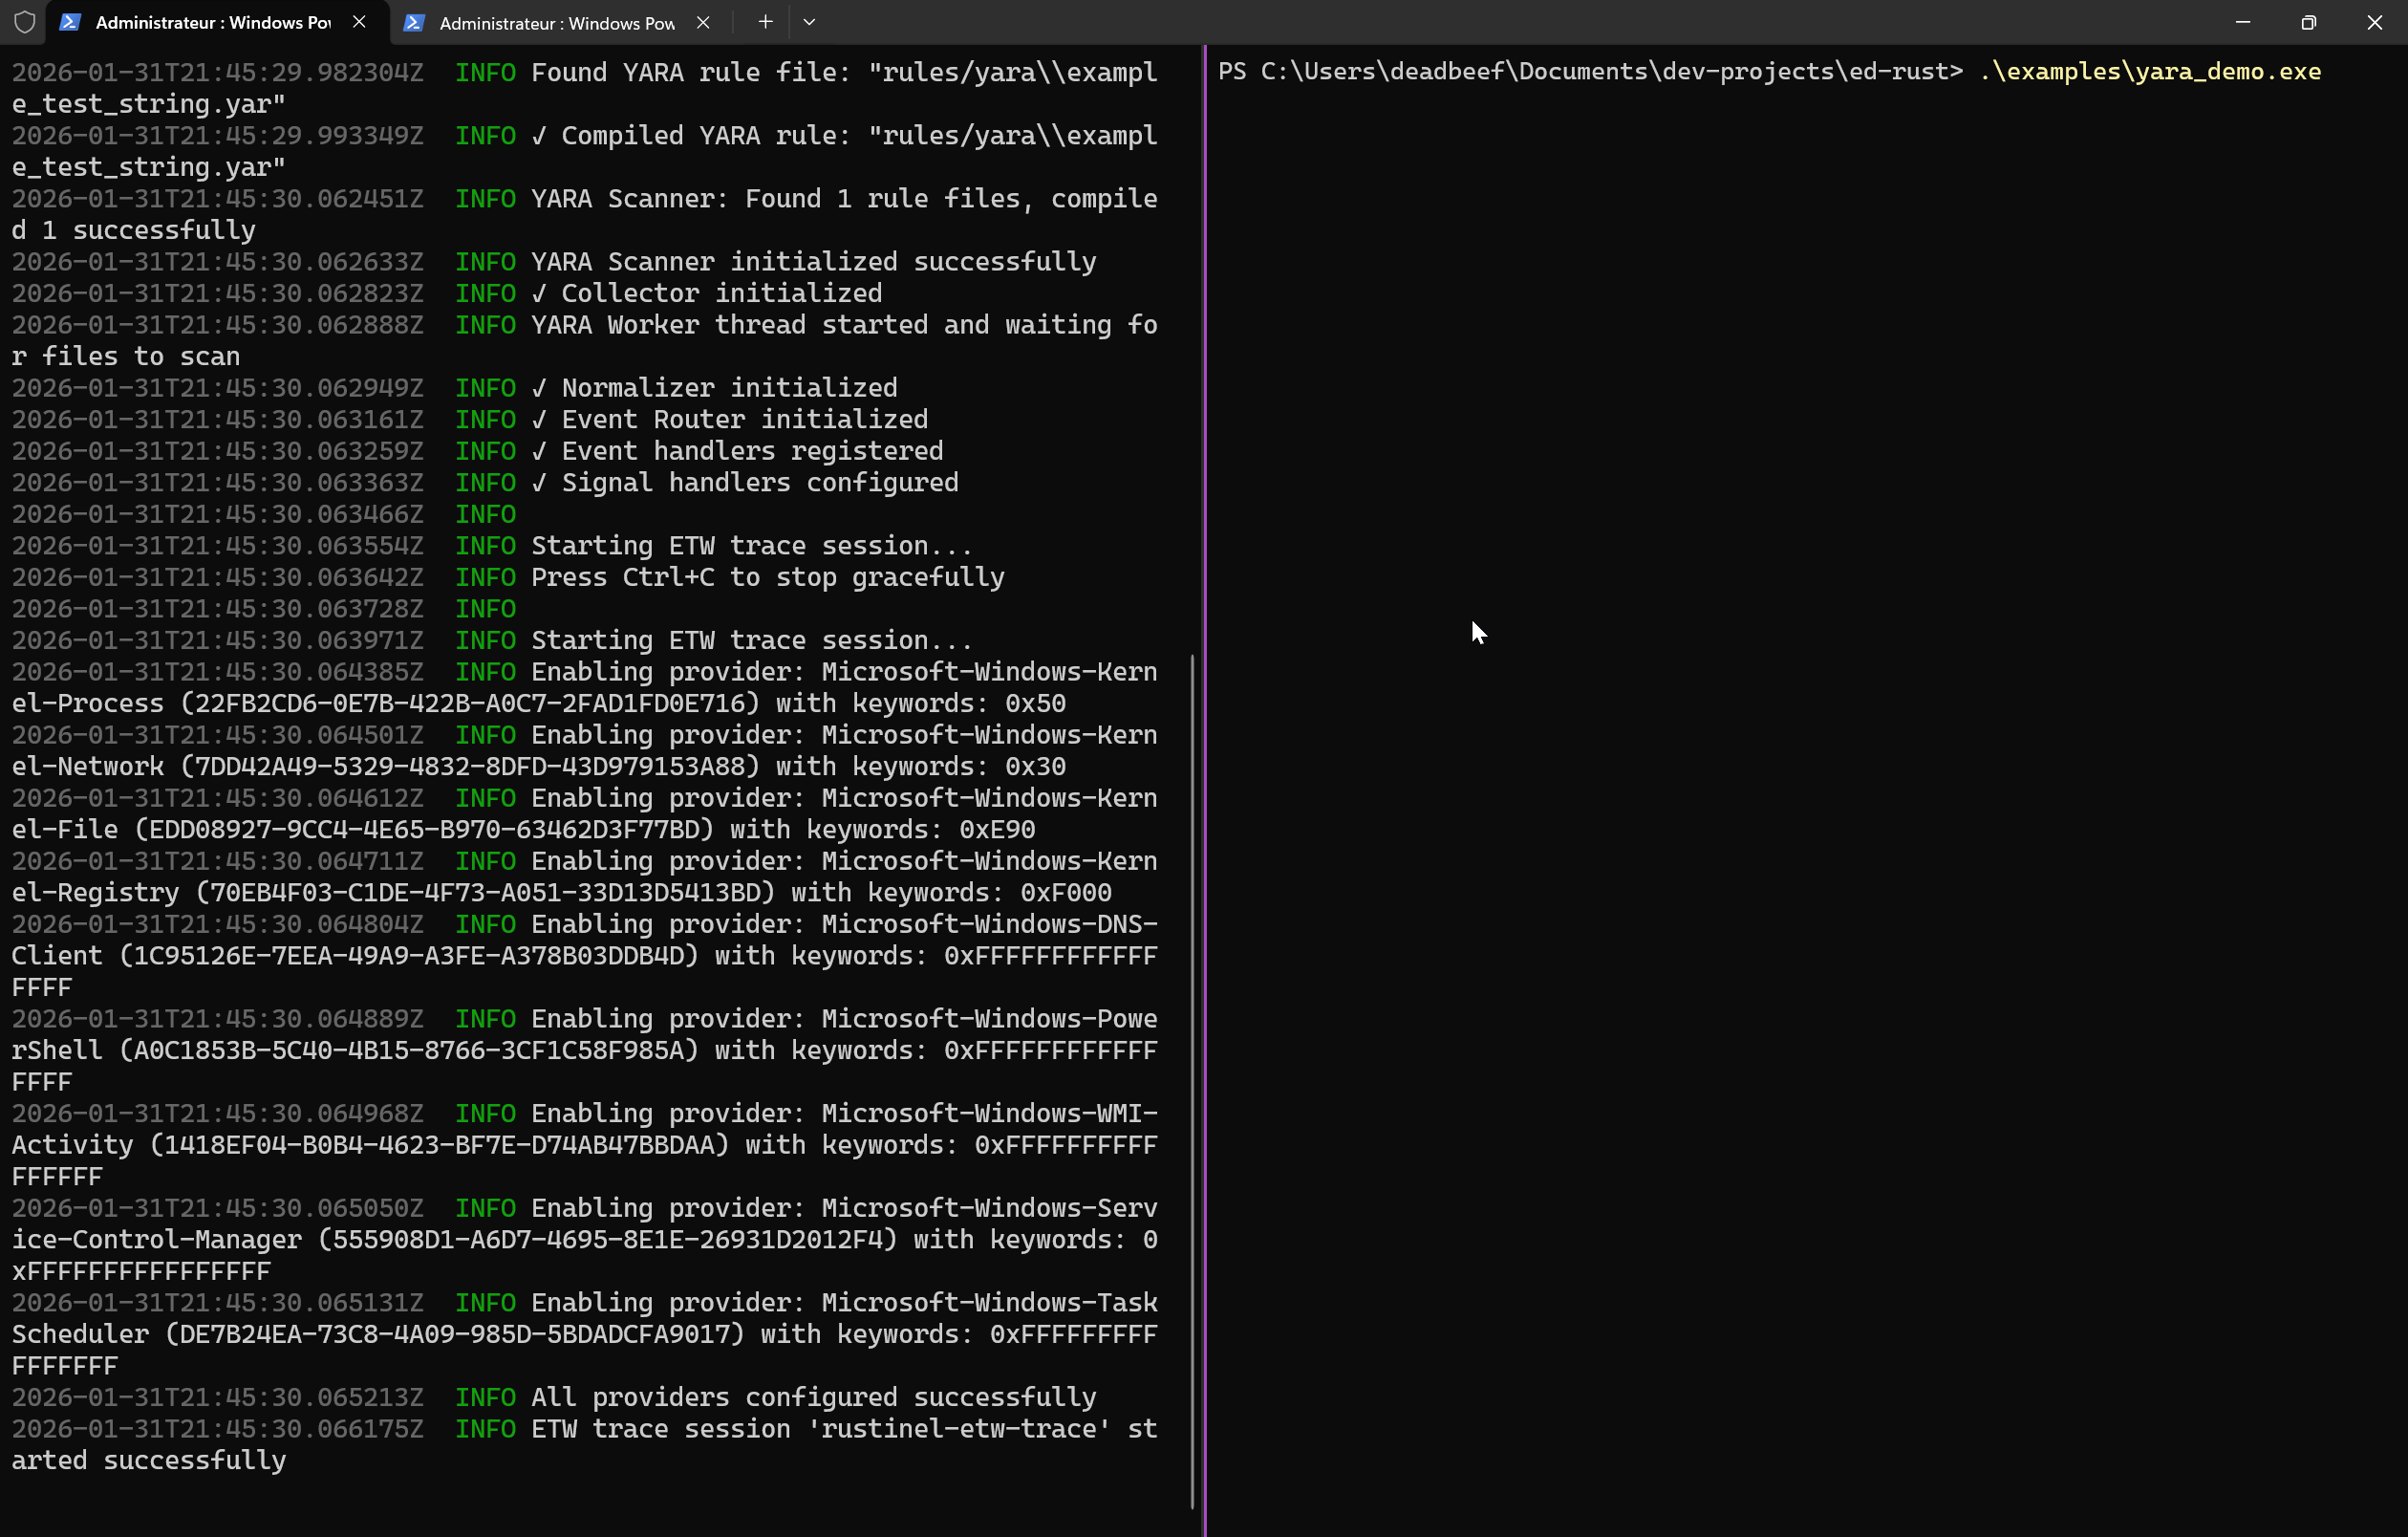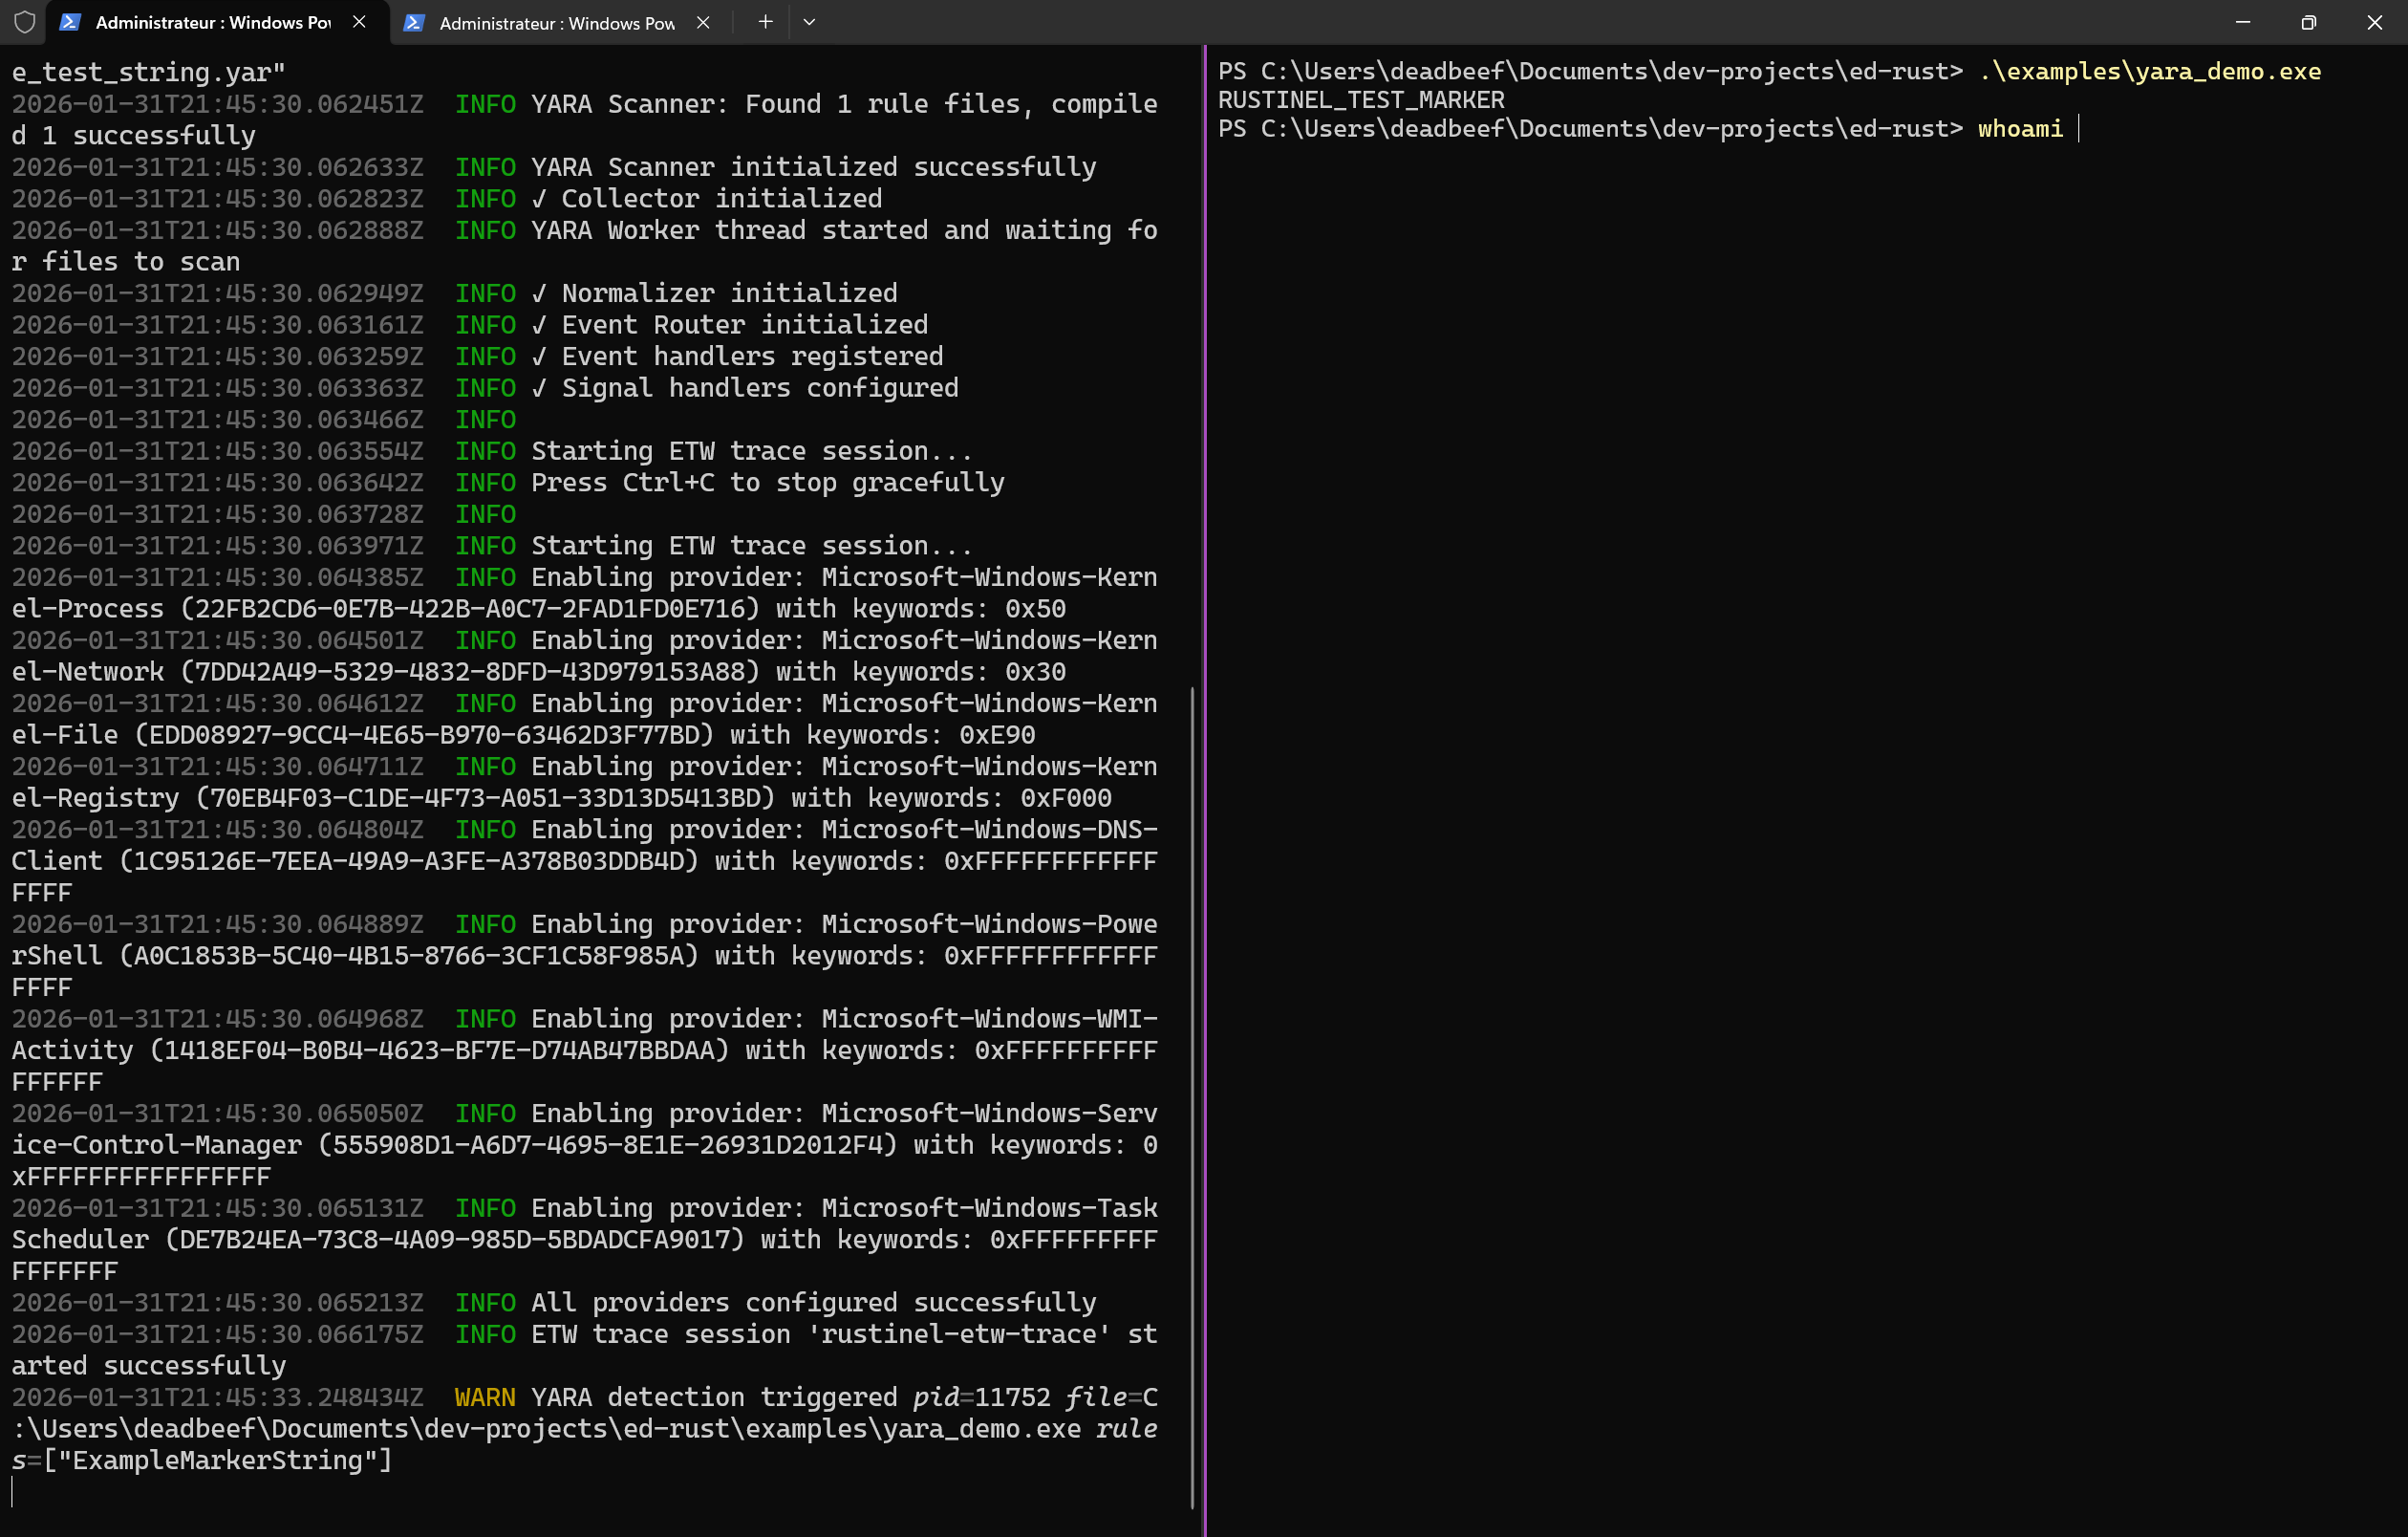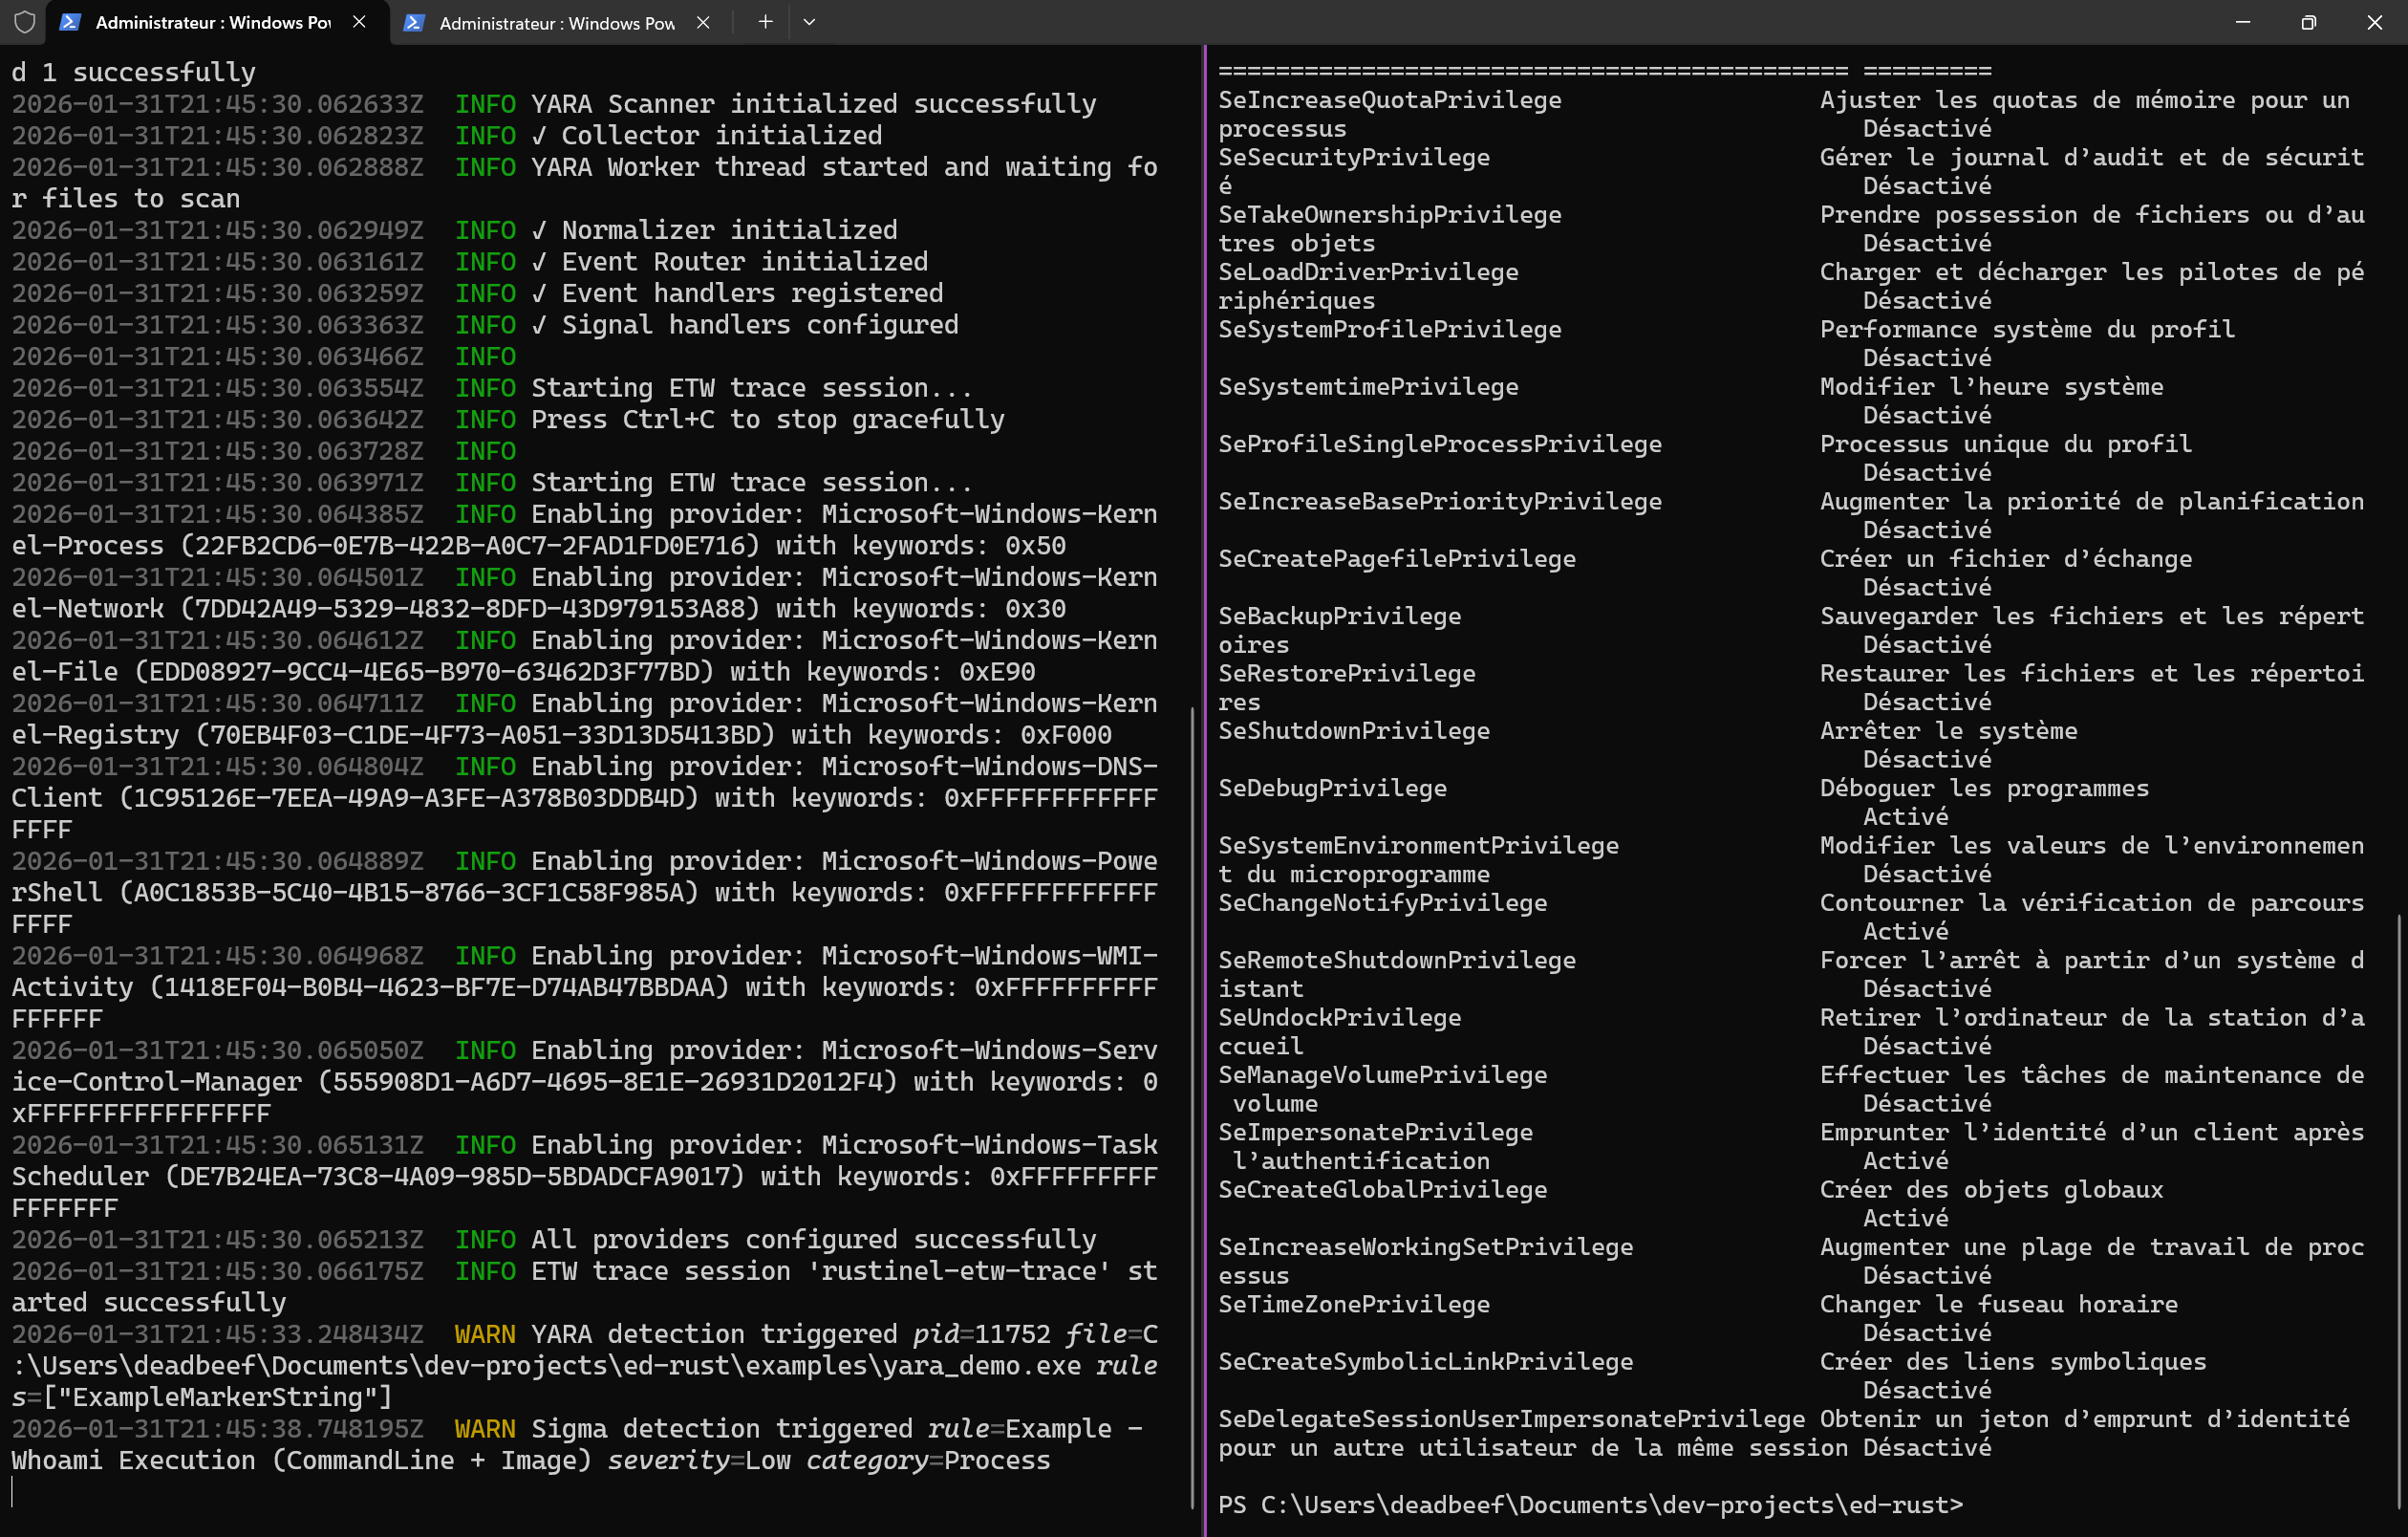 karib0u/rustinel
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.
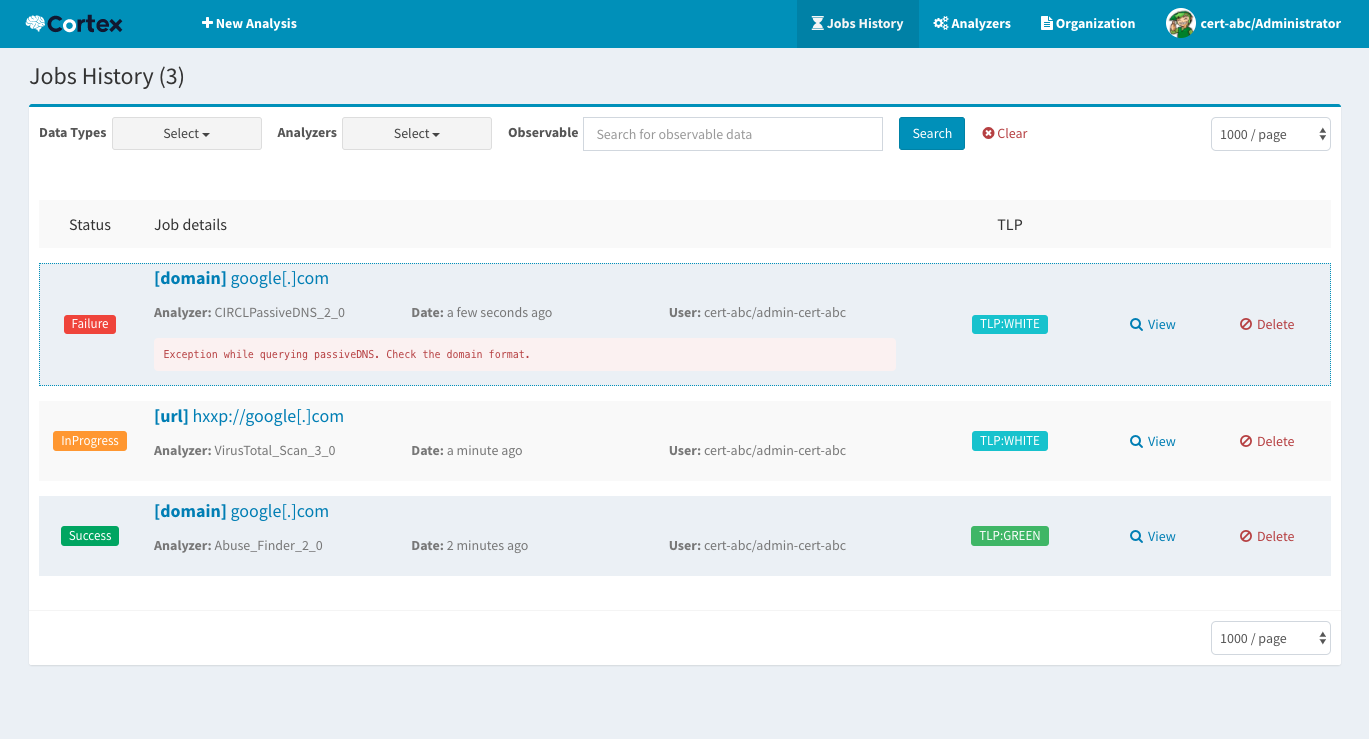 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
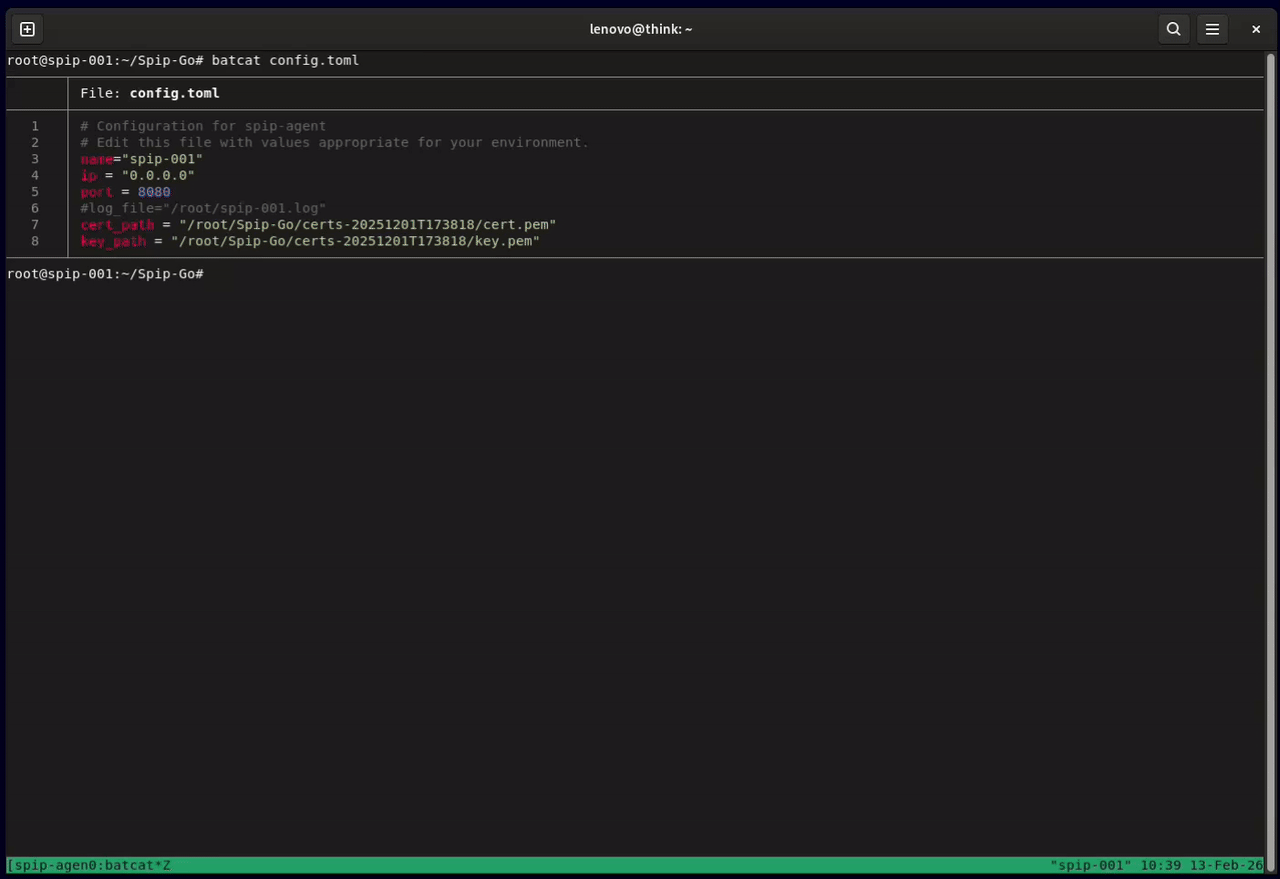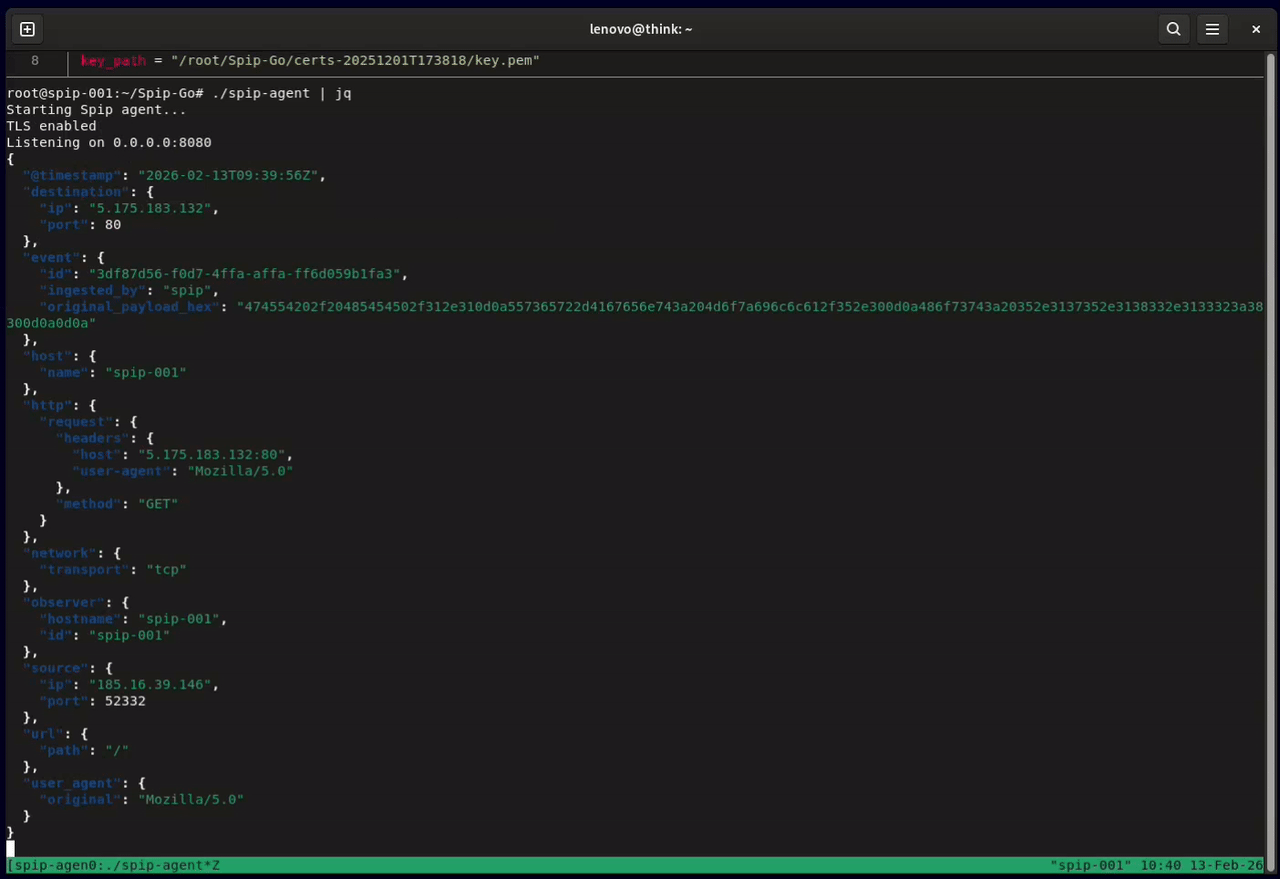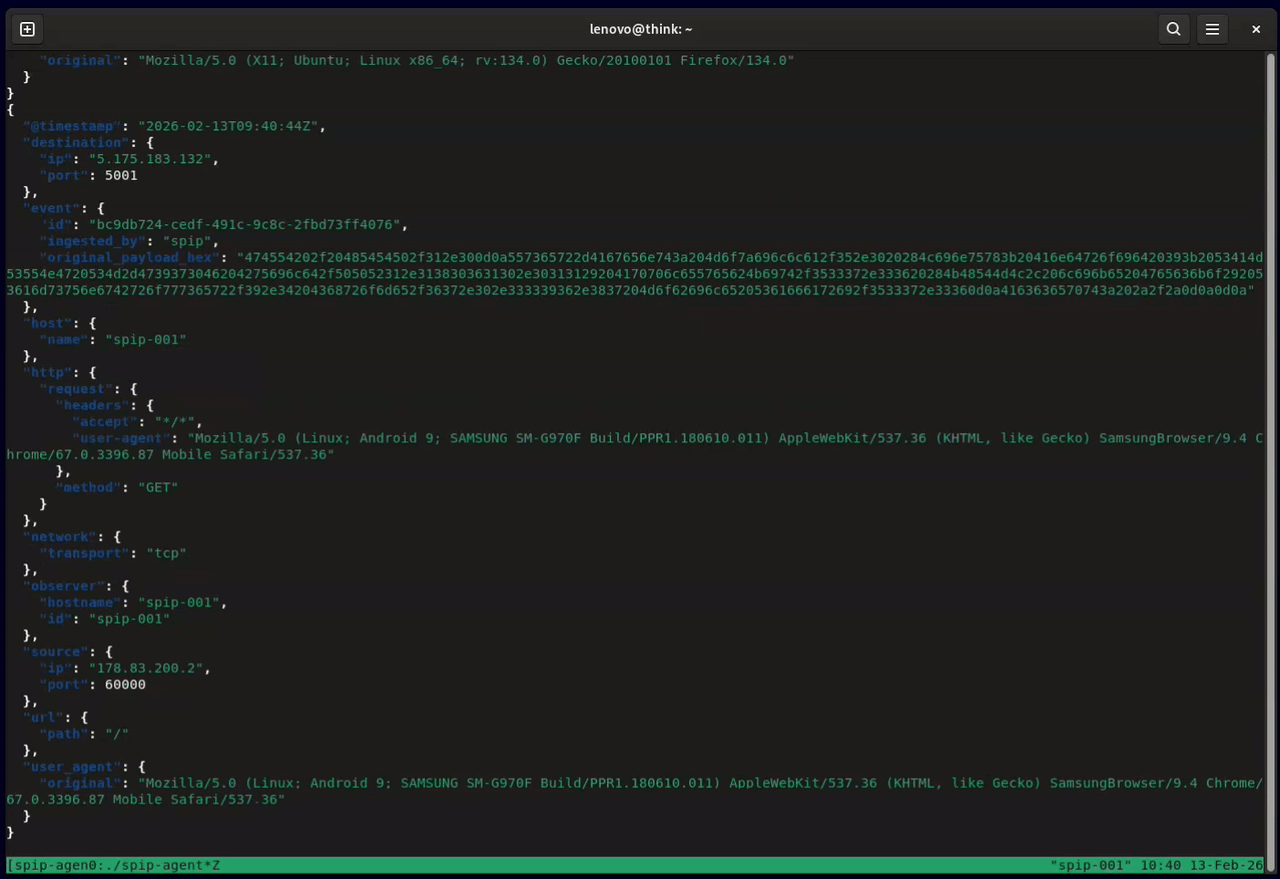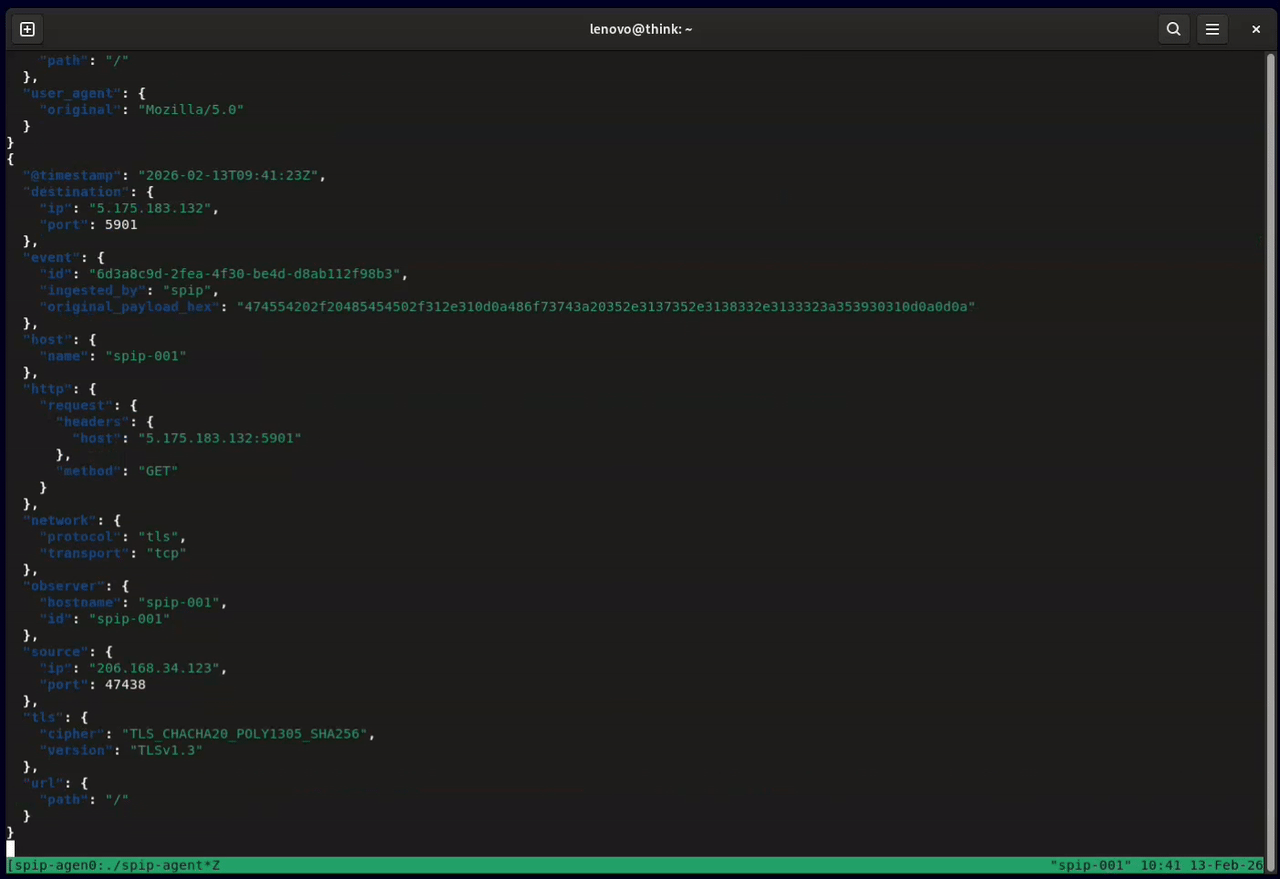 honeylabshq/spip-go
Spip network sensor written in Go
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 vulncheck-oss/cli
VulnCheck's official command line tool
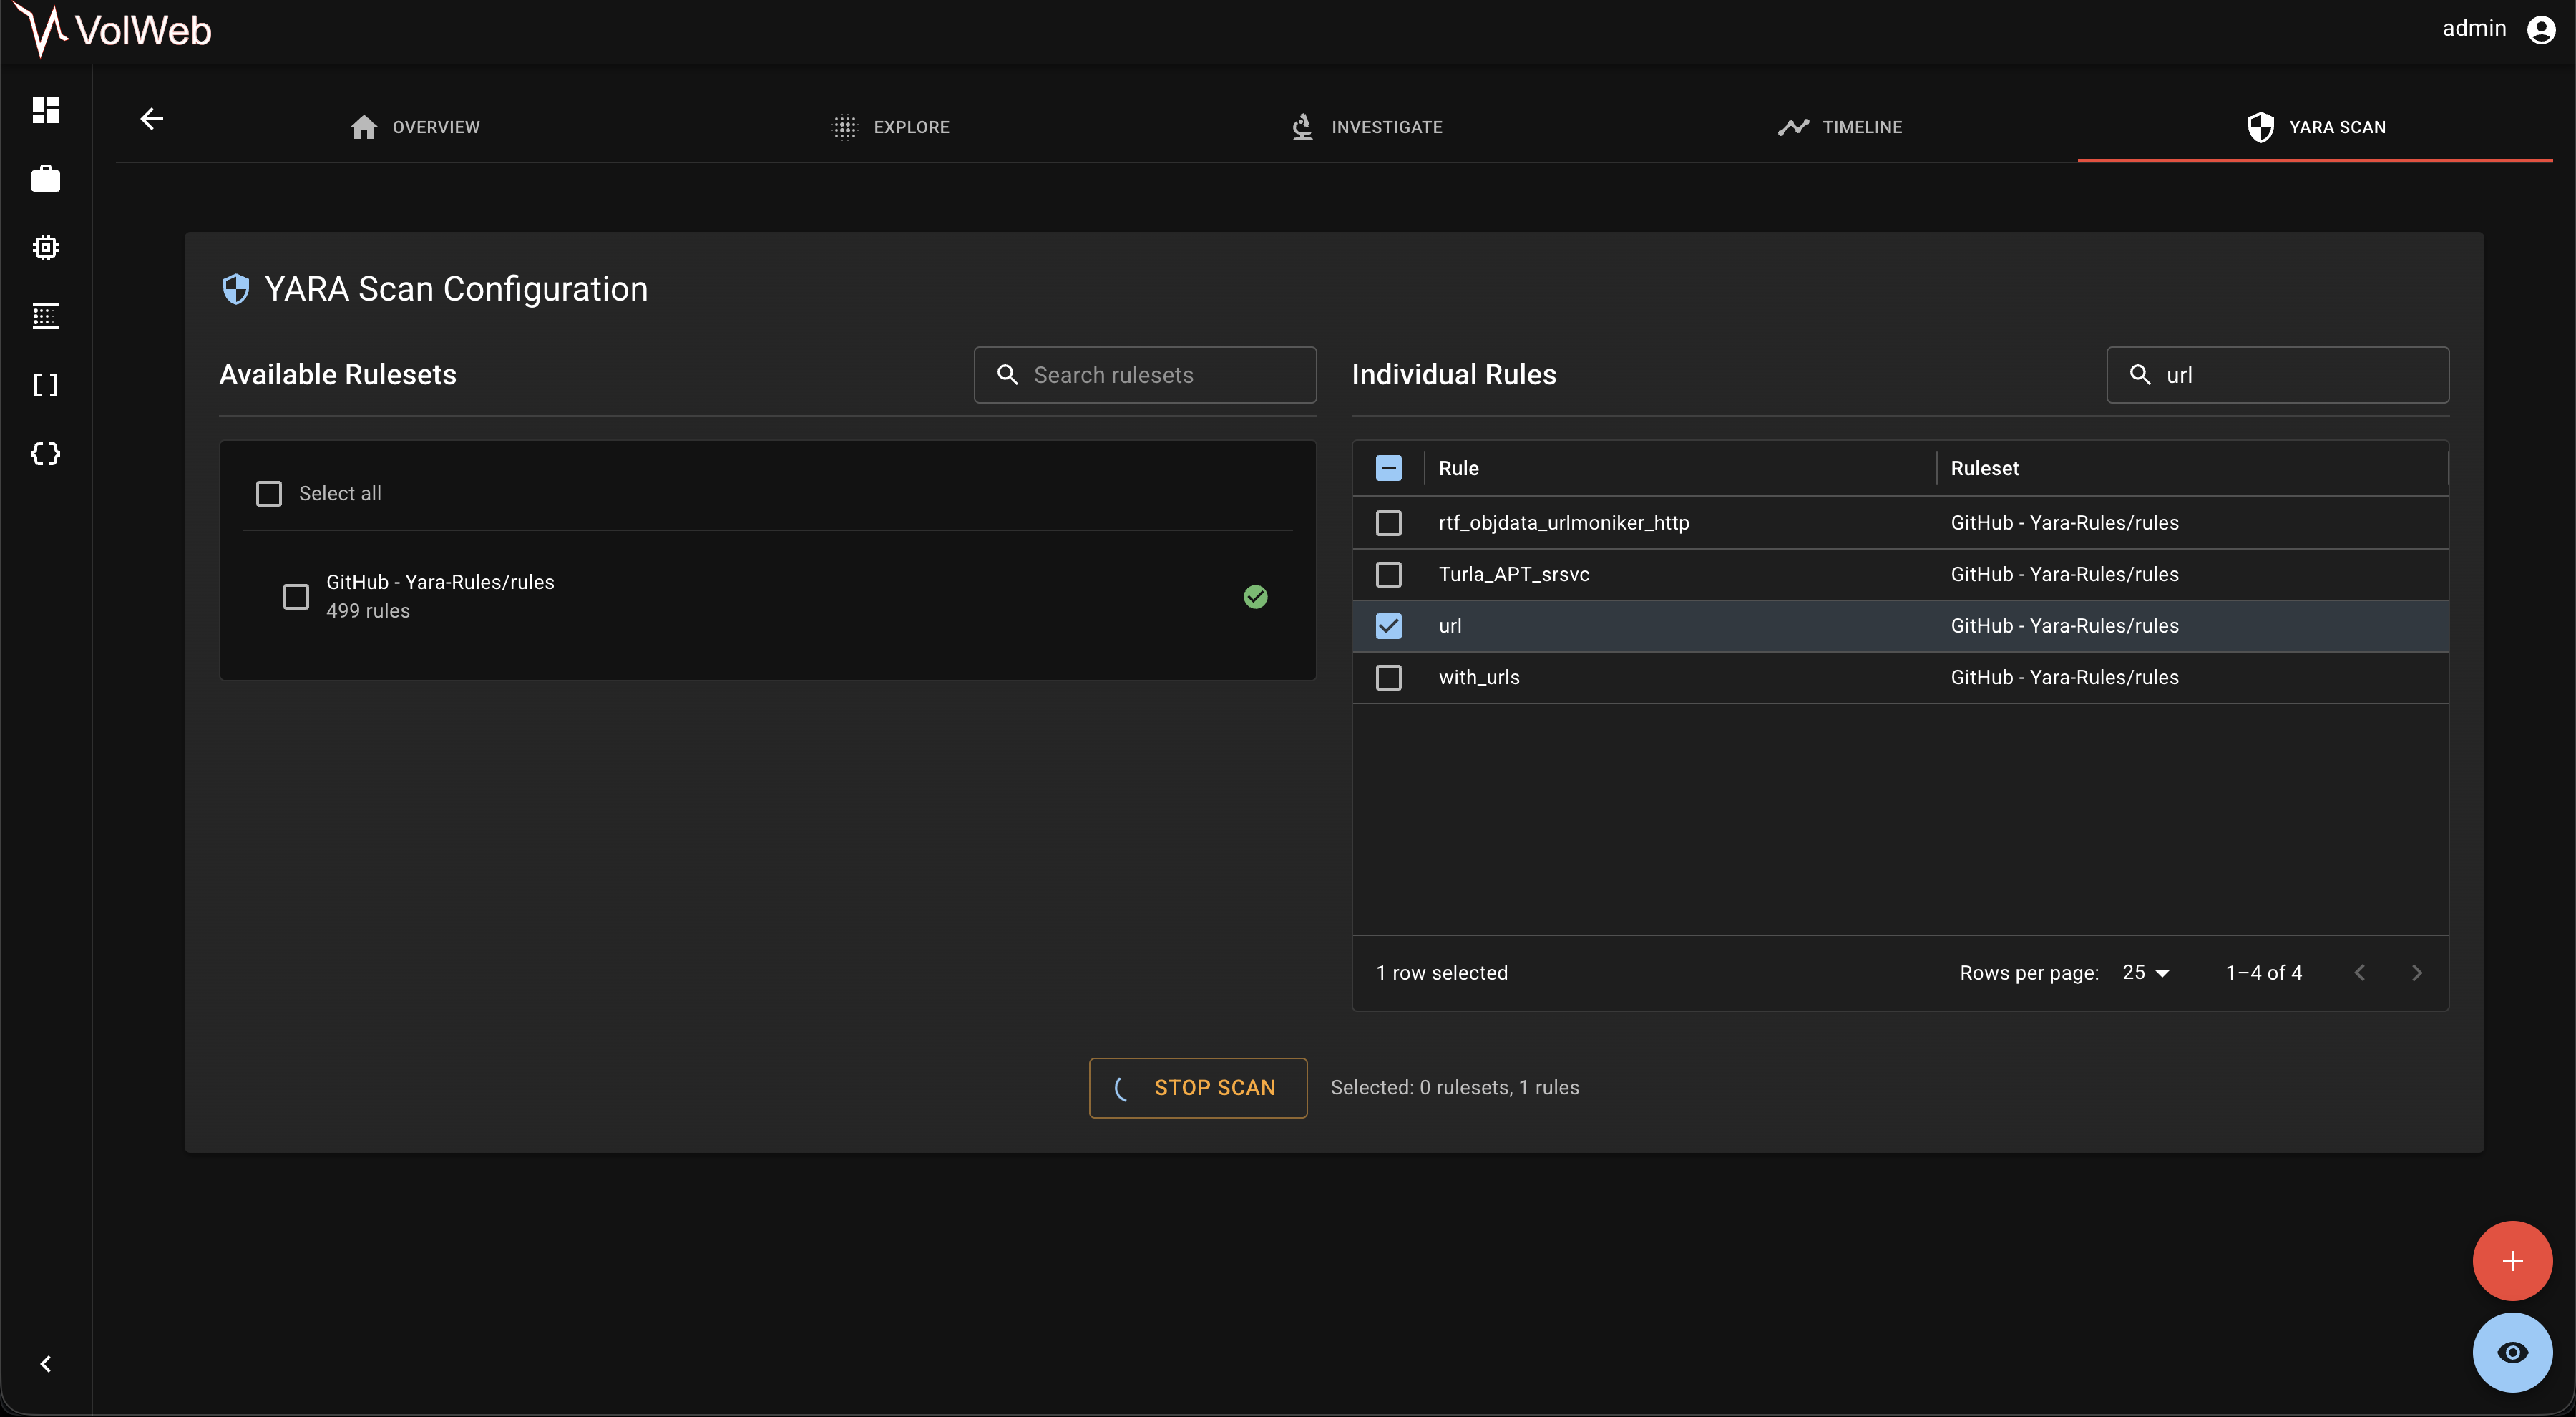 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 lukeslp/redtail-ioc
IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…