
labs-releases
 elastic/labs-releases
Elastic Security Labs releases
curated-resourcesioc-managementmalware-analysis+2
elastic/labs-releasesElastic Security Labs releases
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 ares-sys/uefi_bootkit_softlanding
First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 ben-smash/l4j-info
Compiling links of value i find regarding CVE-2021-44228
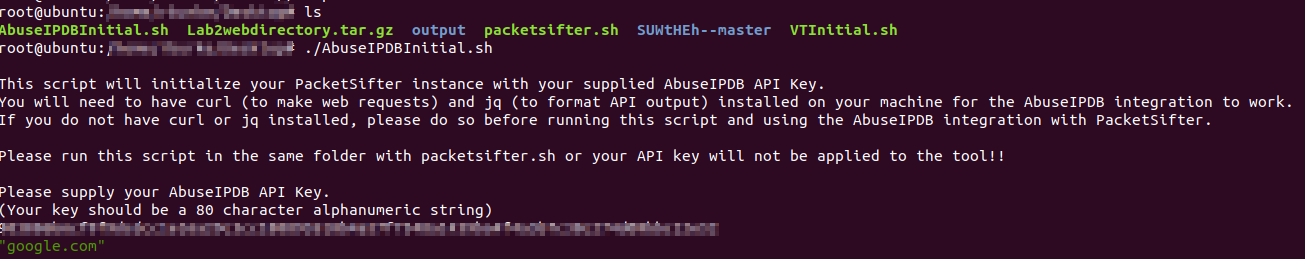 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781