
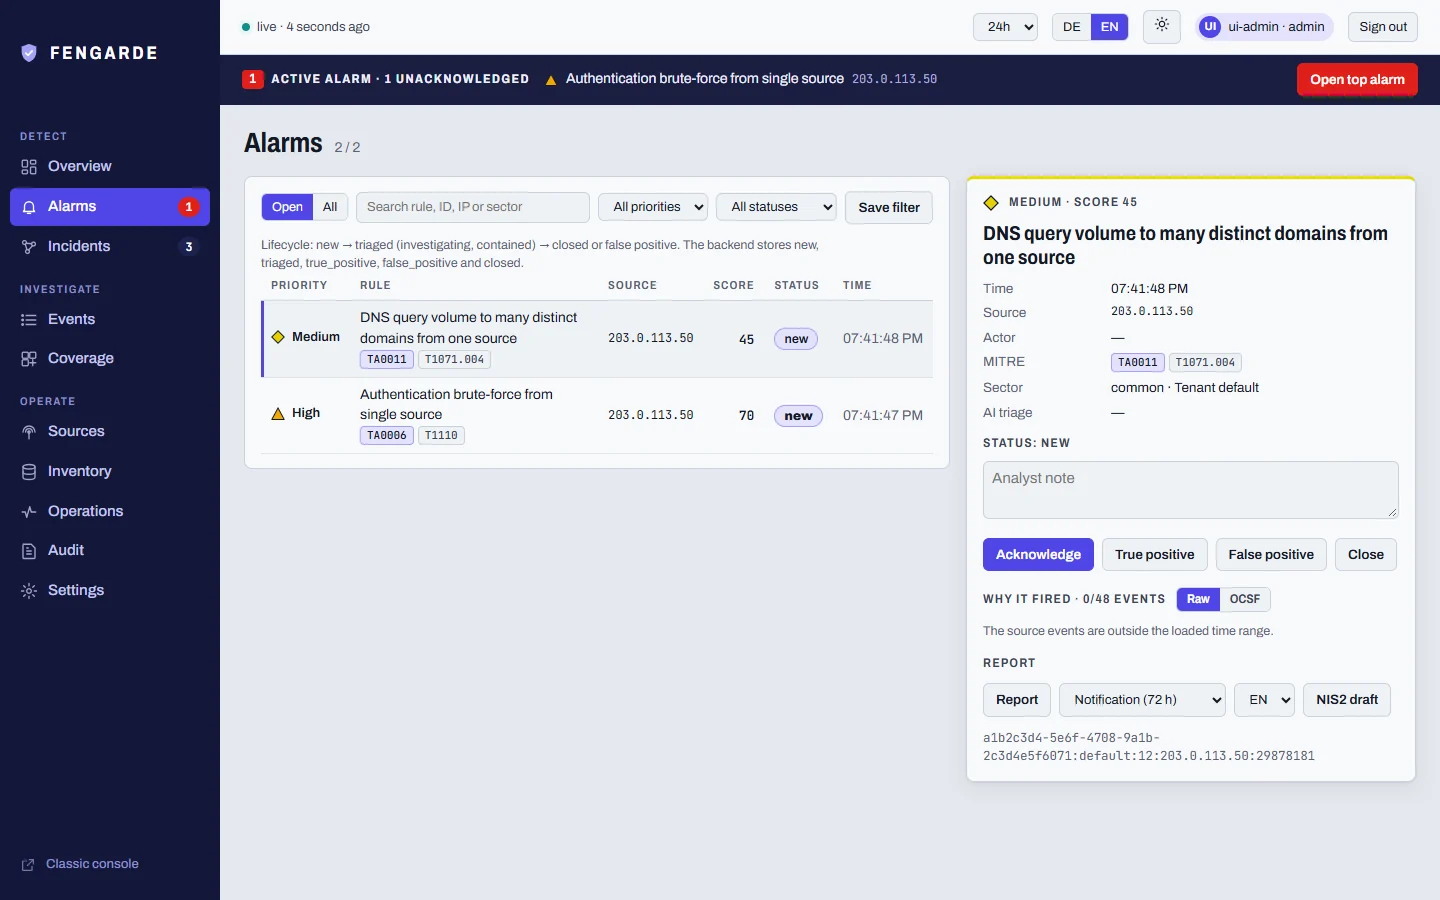
fengarde
 supermhel/fengarde
Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
ai-securitydefensive-toolsincident-response+4
20
supermhel/fengardeOpen-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
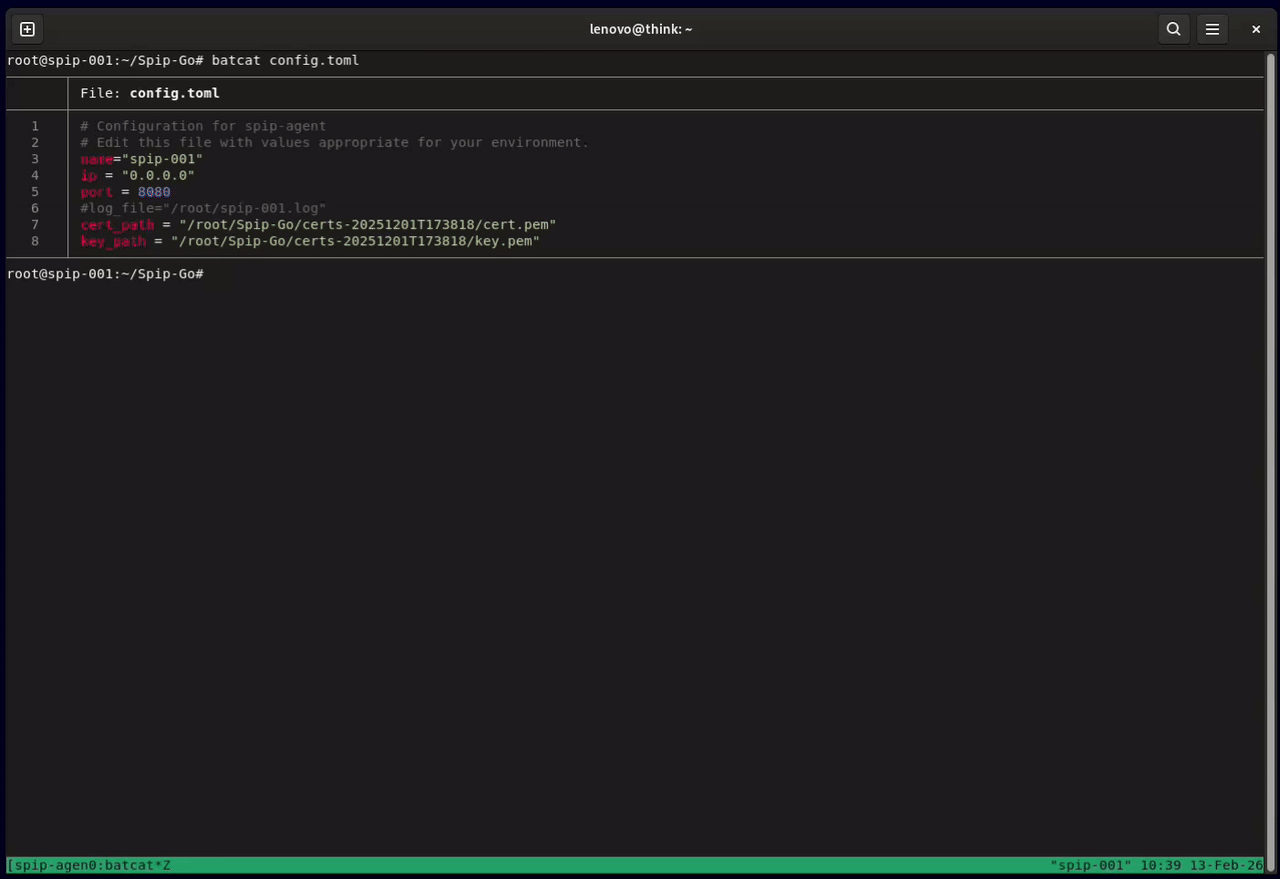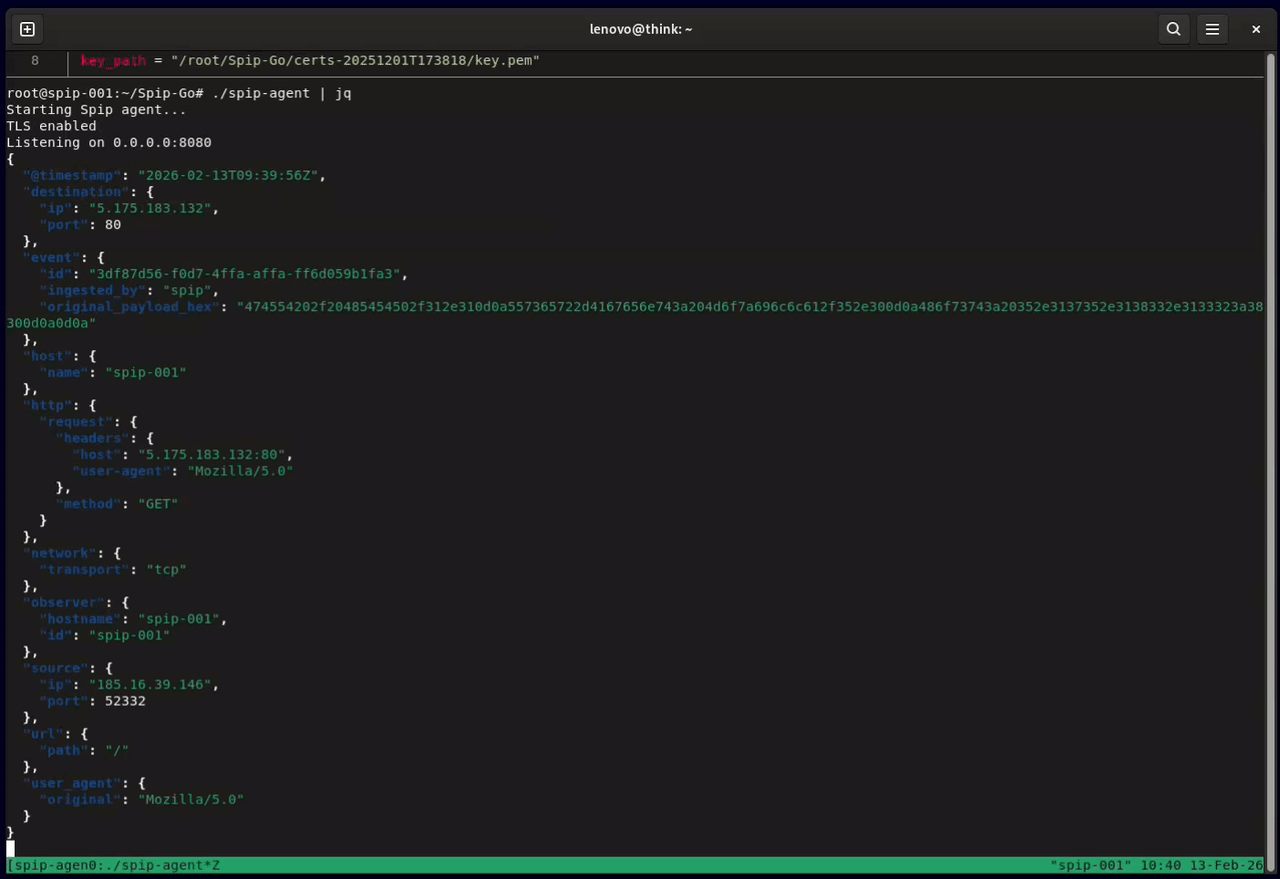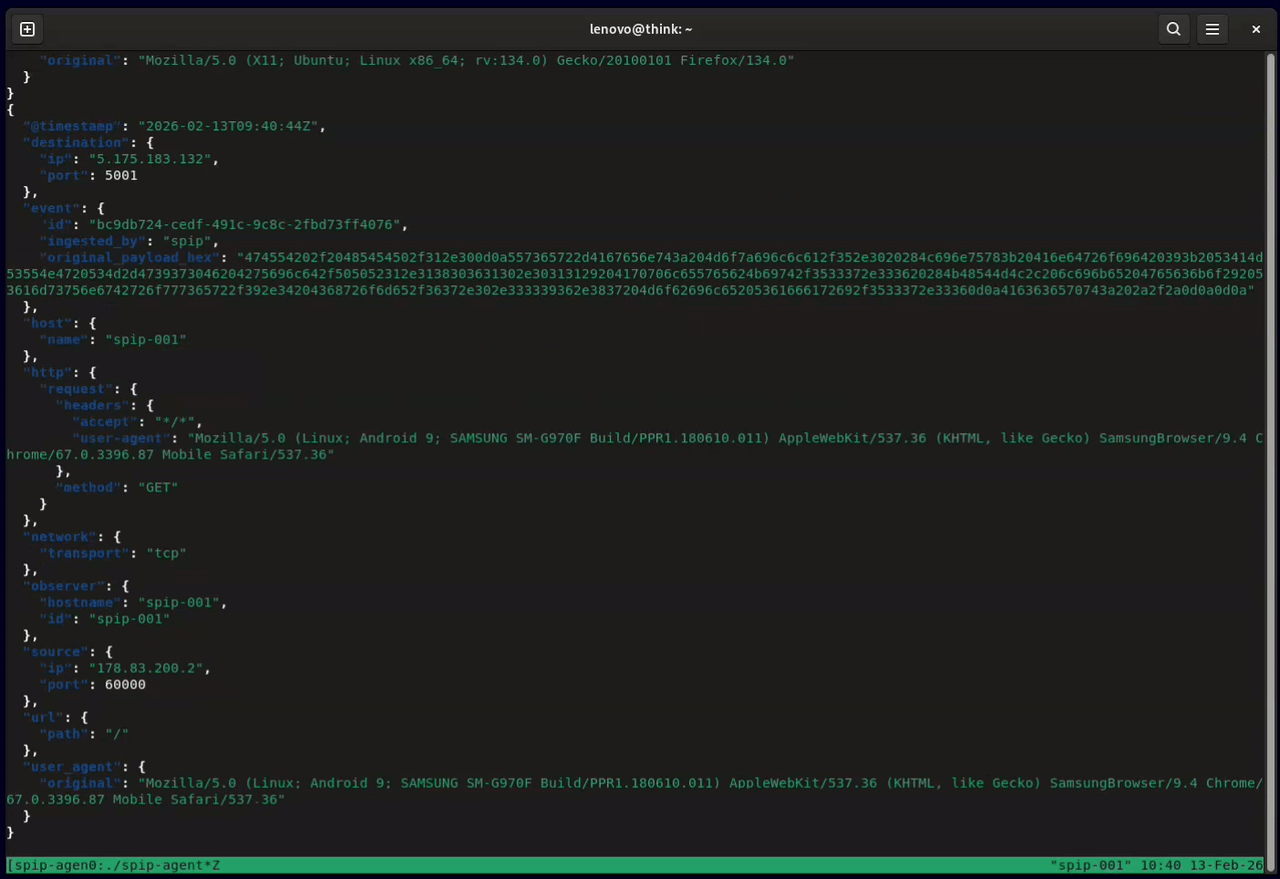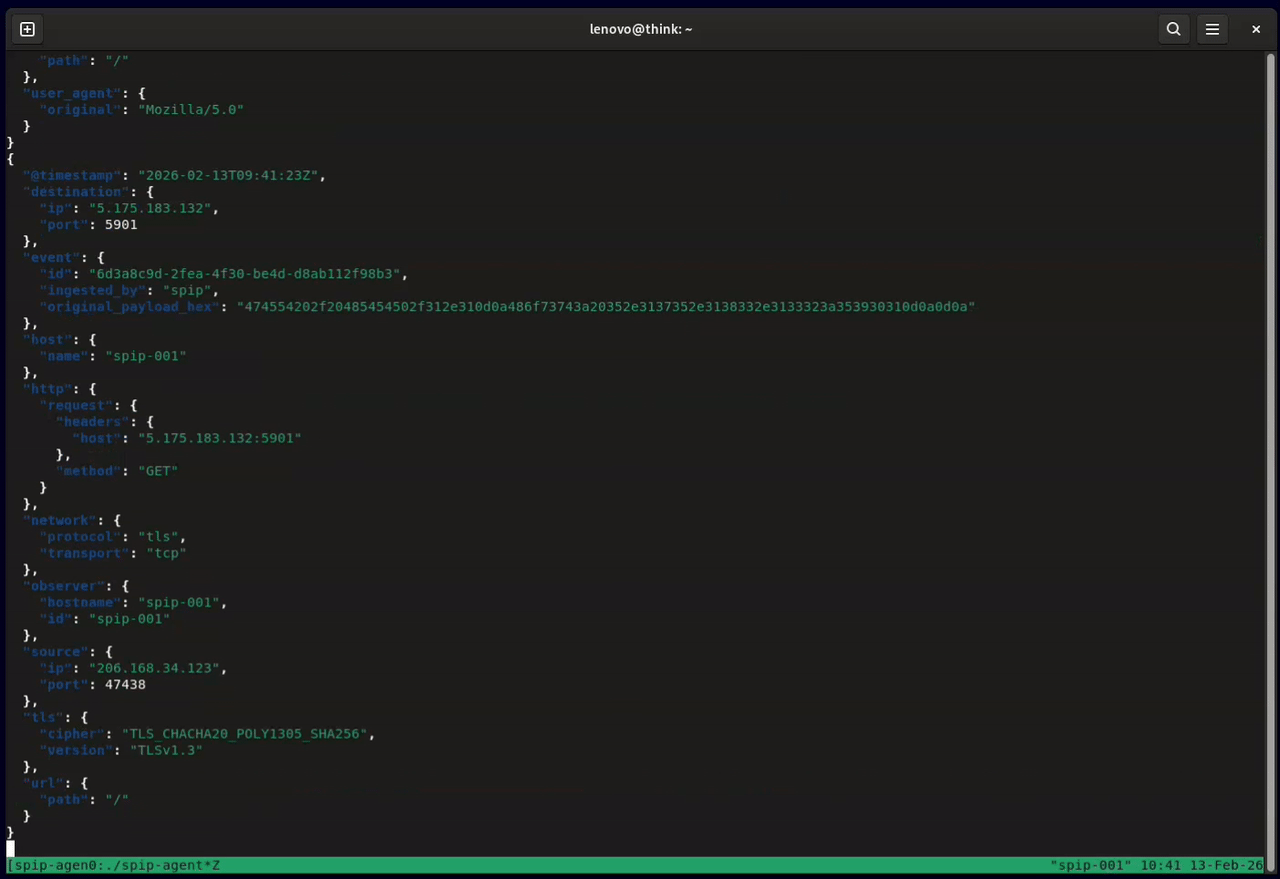 honeylabshq/spip-go
Spip network sensor written in Go
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 pastelghost3/cve-2026-76504-nuclei
Nuclei template for CVE-2026-76504 — Cisco vManage authentication bypass
 0xajstrike/emsign-trust-scan
Offline scanner for the October 2026 eMudhra/emSign CA key compromise, finds affected certificates across OS trust stores, CA bundles, Java cacerts,…
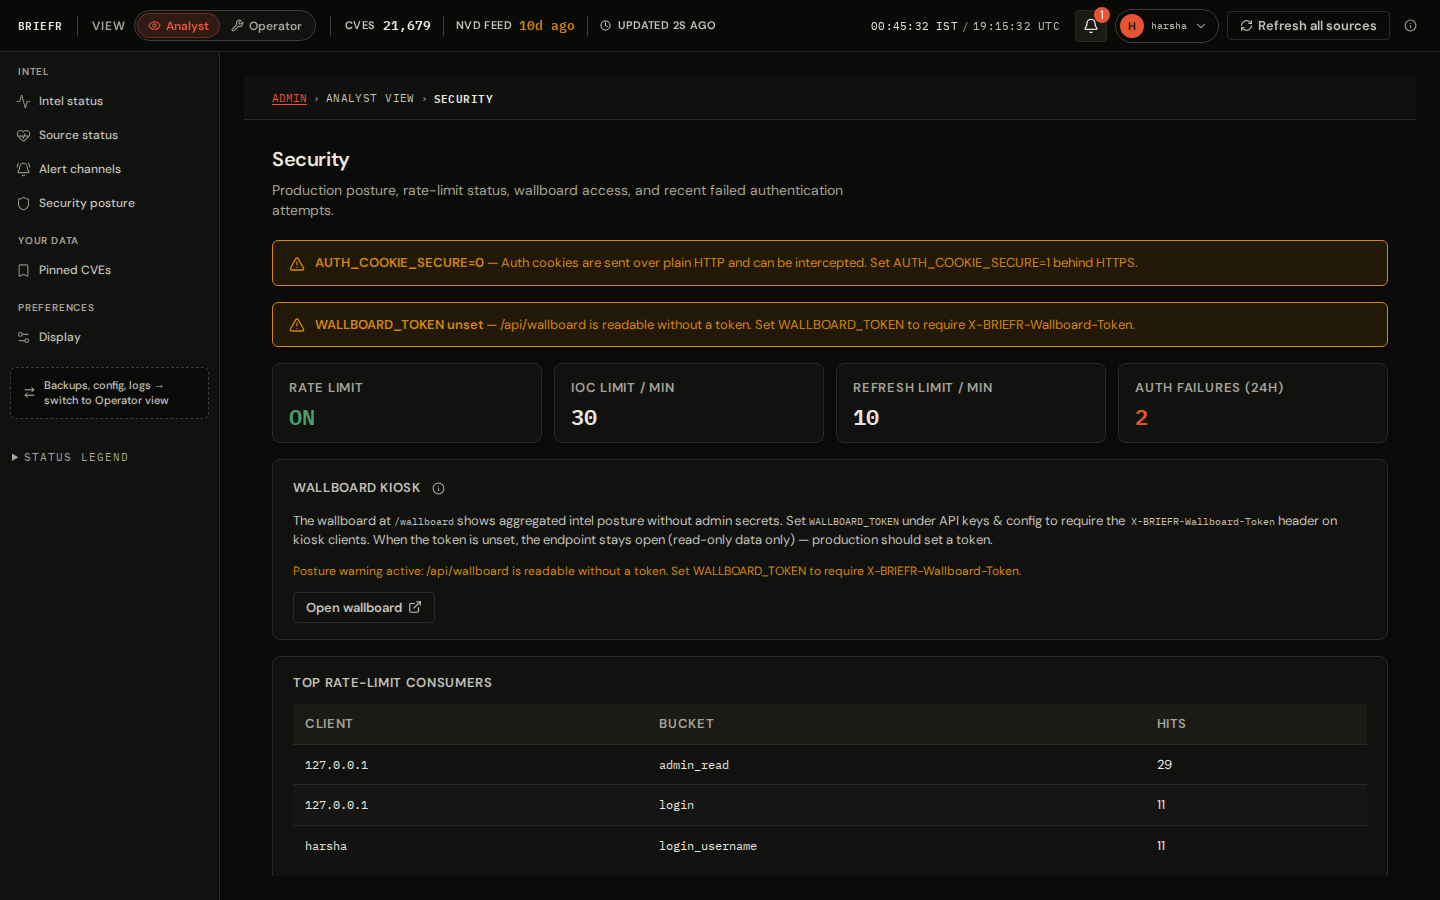 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 chrislpjones/plex2shell-check
Read-only Linux check for Plex2Shell (CVE-2026-96652/-96654/-96655/-96656) exploitation and the XMRig/proxy payloads seen in the wild
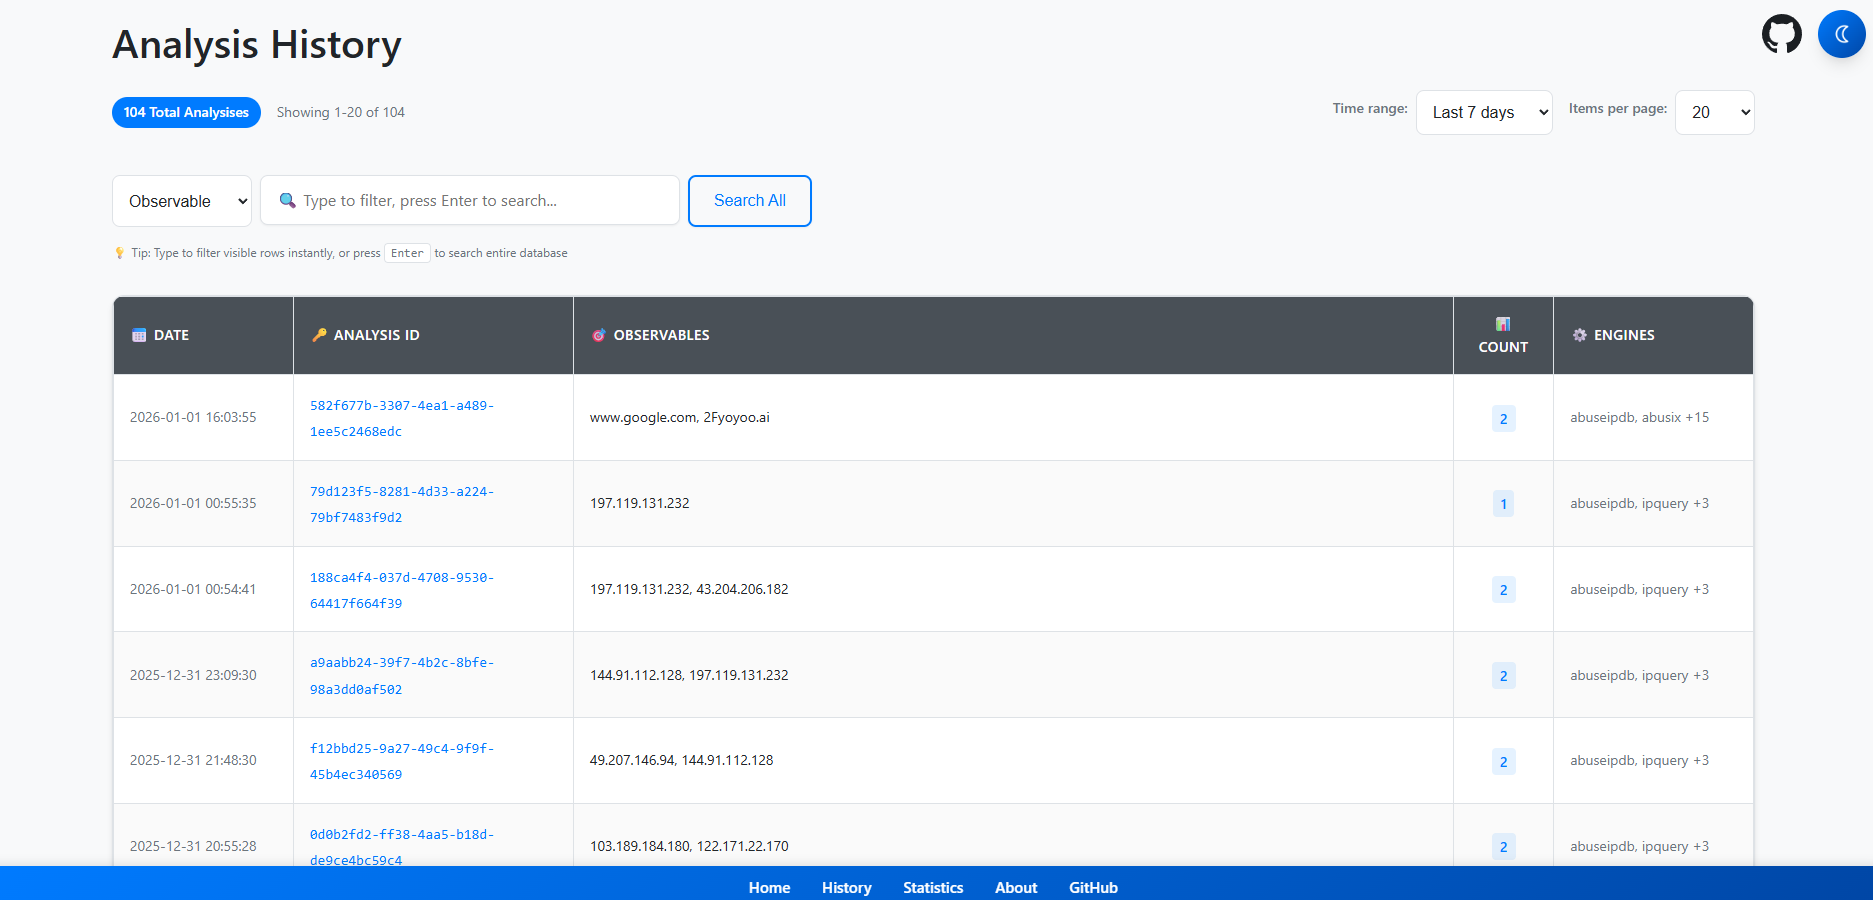 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 a3igner/plex-codec-cache-implant
Incident write-up: unsigned .so in the Plex Media Server codec cache executes a dropper on every transcode (CVE-2026-96656) — IOCs, STIX, YARA
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.