
Antiphishing
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
defensive-toolsdns-analysisids-ips-evasion+6
4039 minutes ago
julioliraup/antiphishingAdvanced Phishing Protection: Suricata rulesets open and free
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 infostealers-stats/data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…
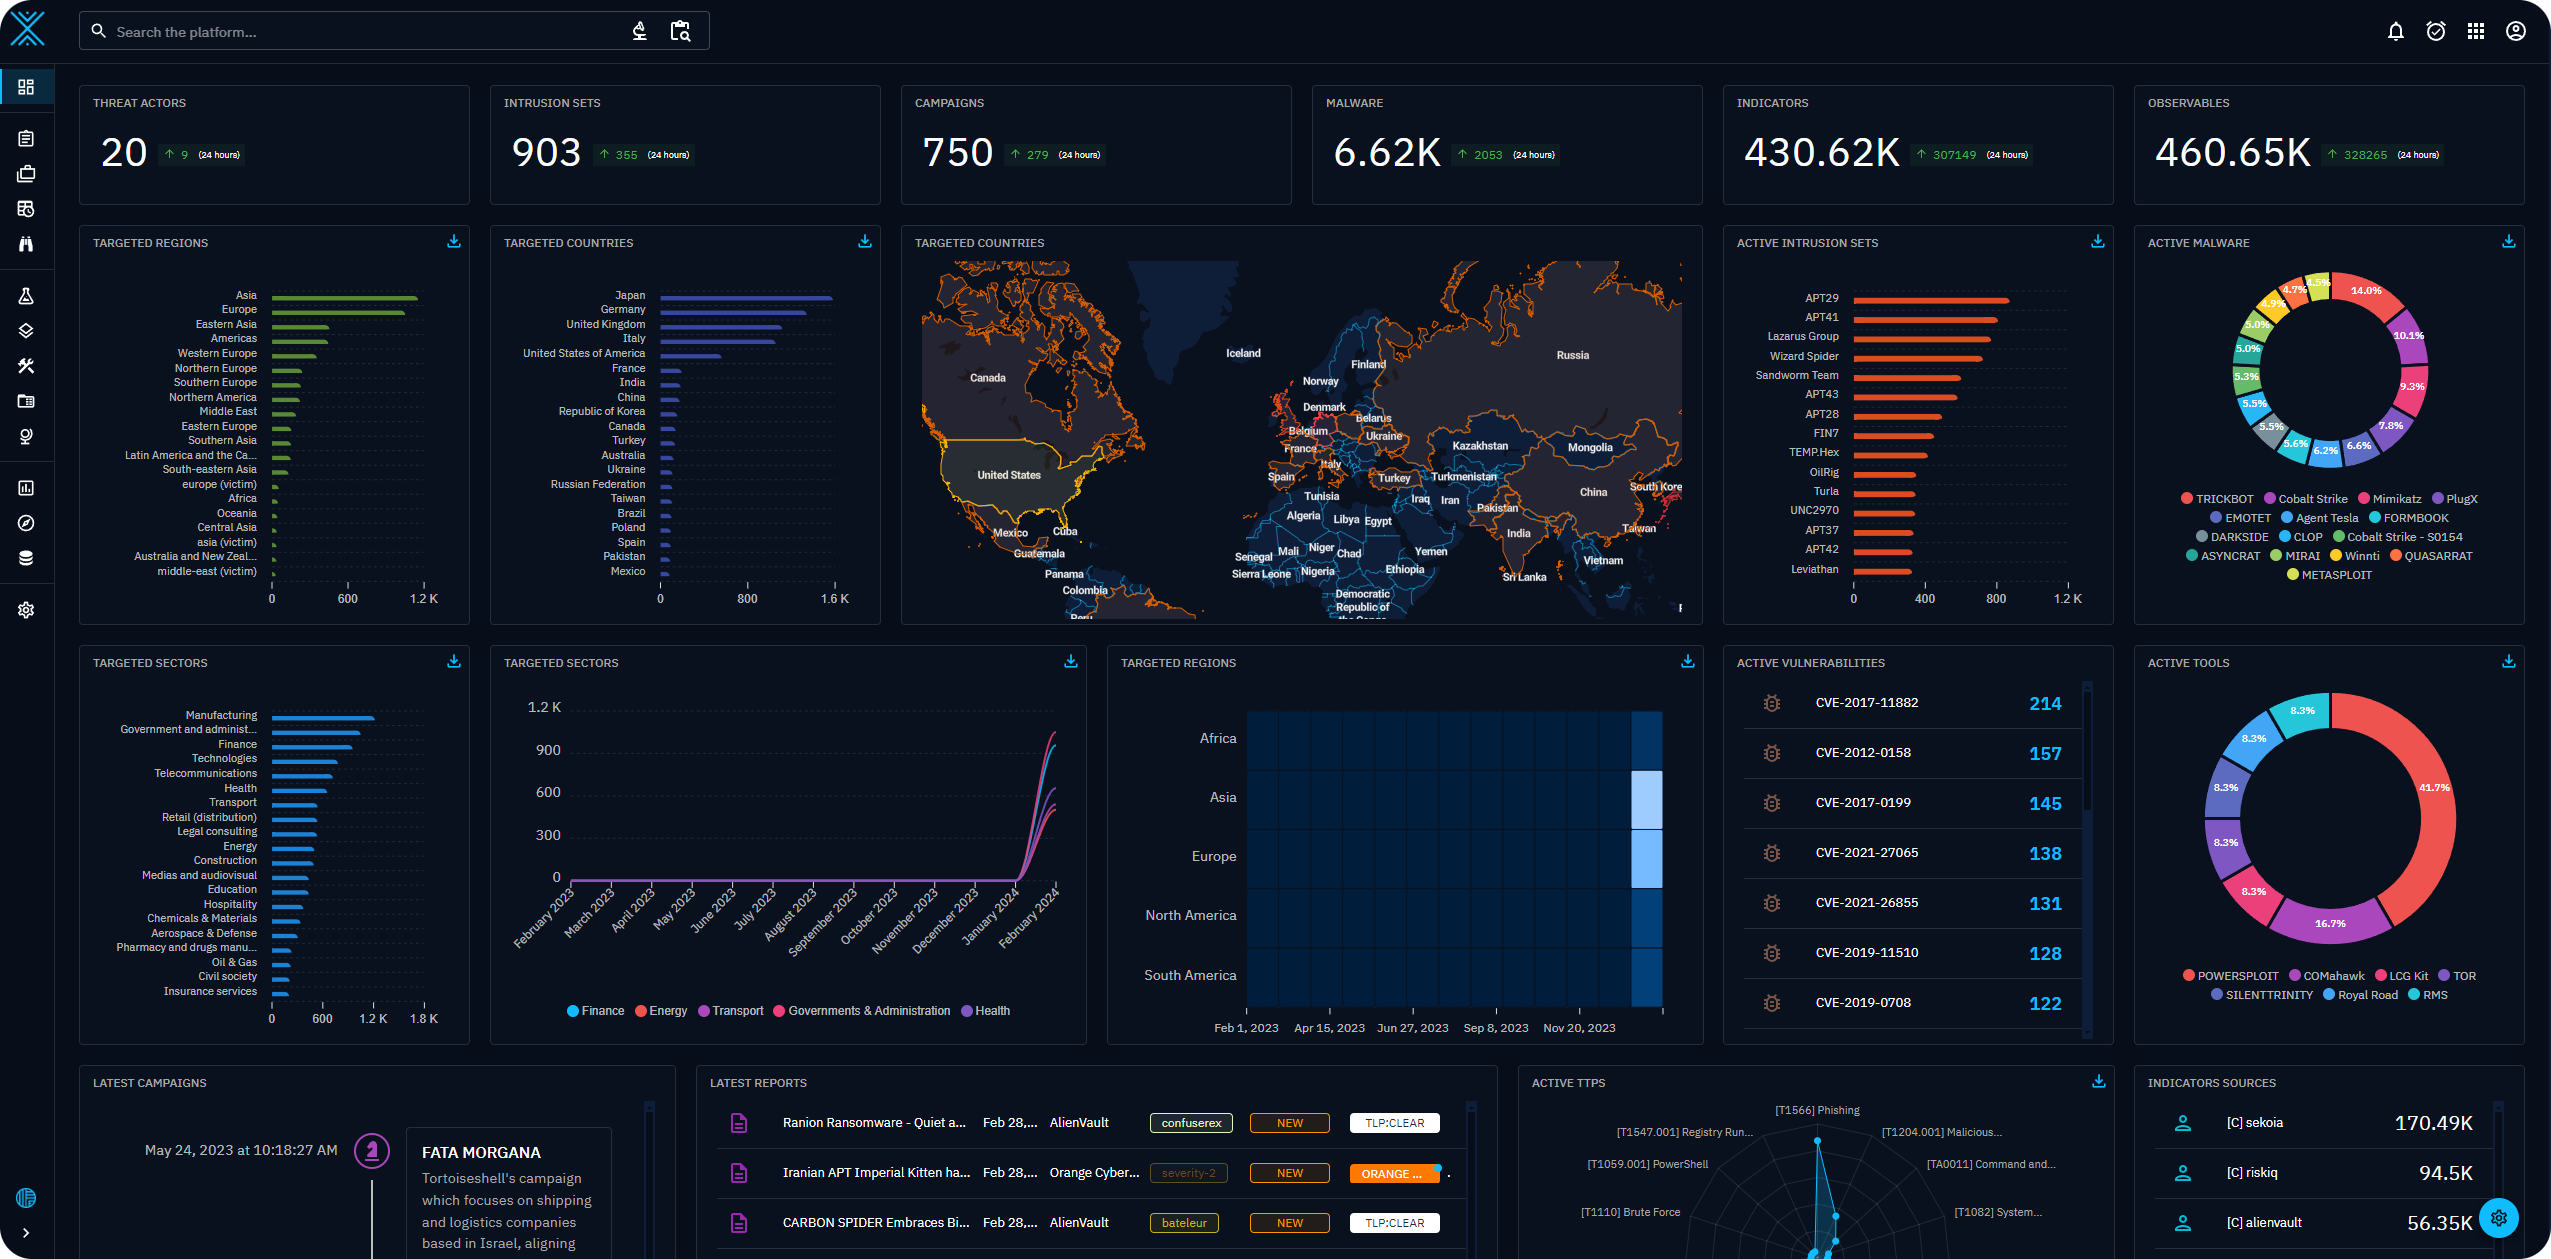 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
 soc-irdoc/irdoc-app
Incident Response Documentation Platform
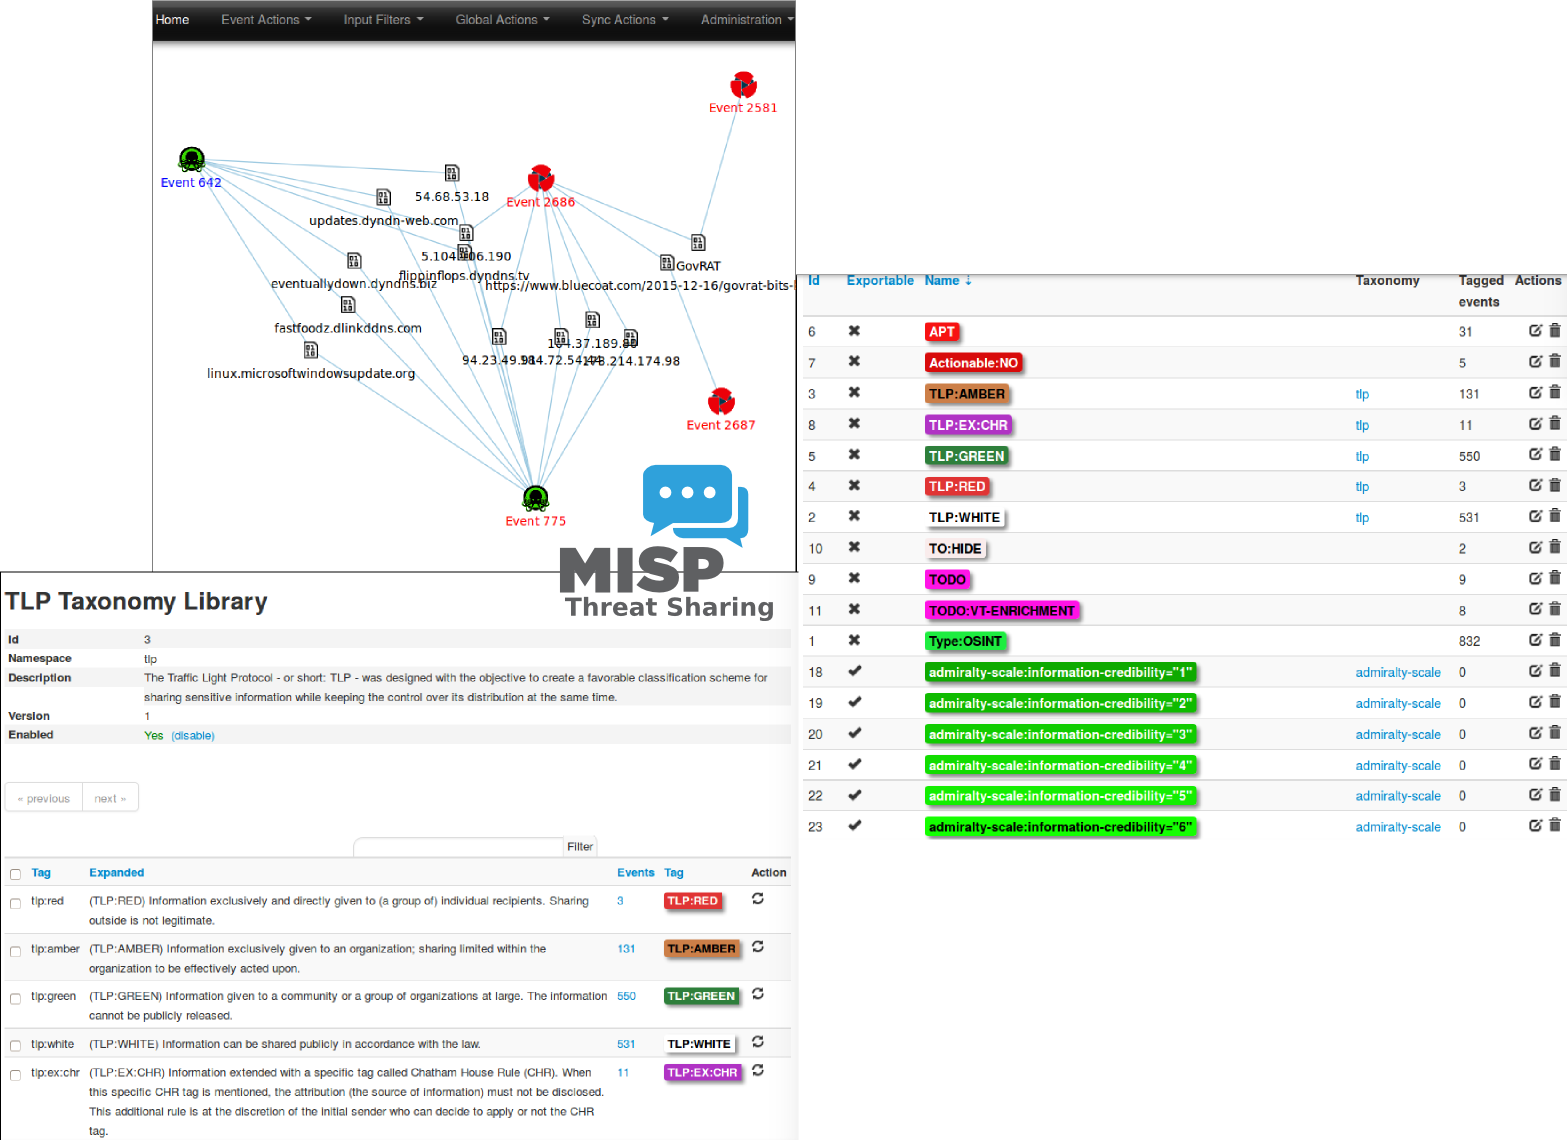 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
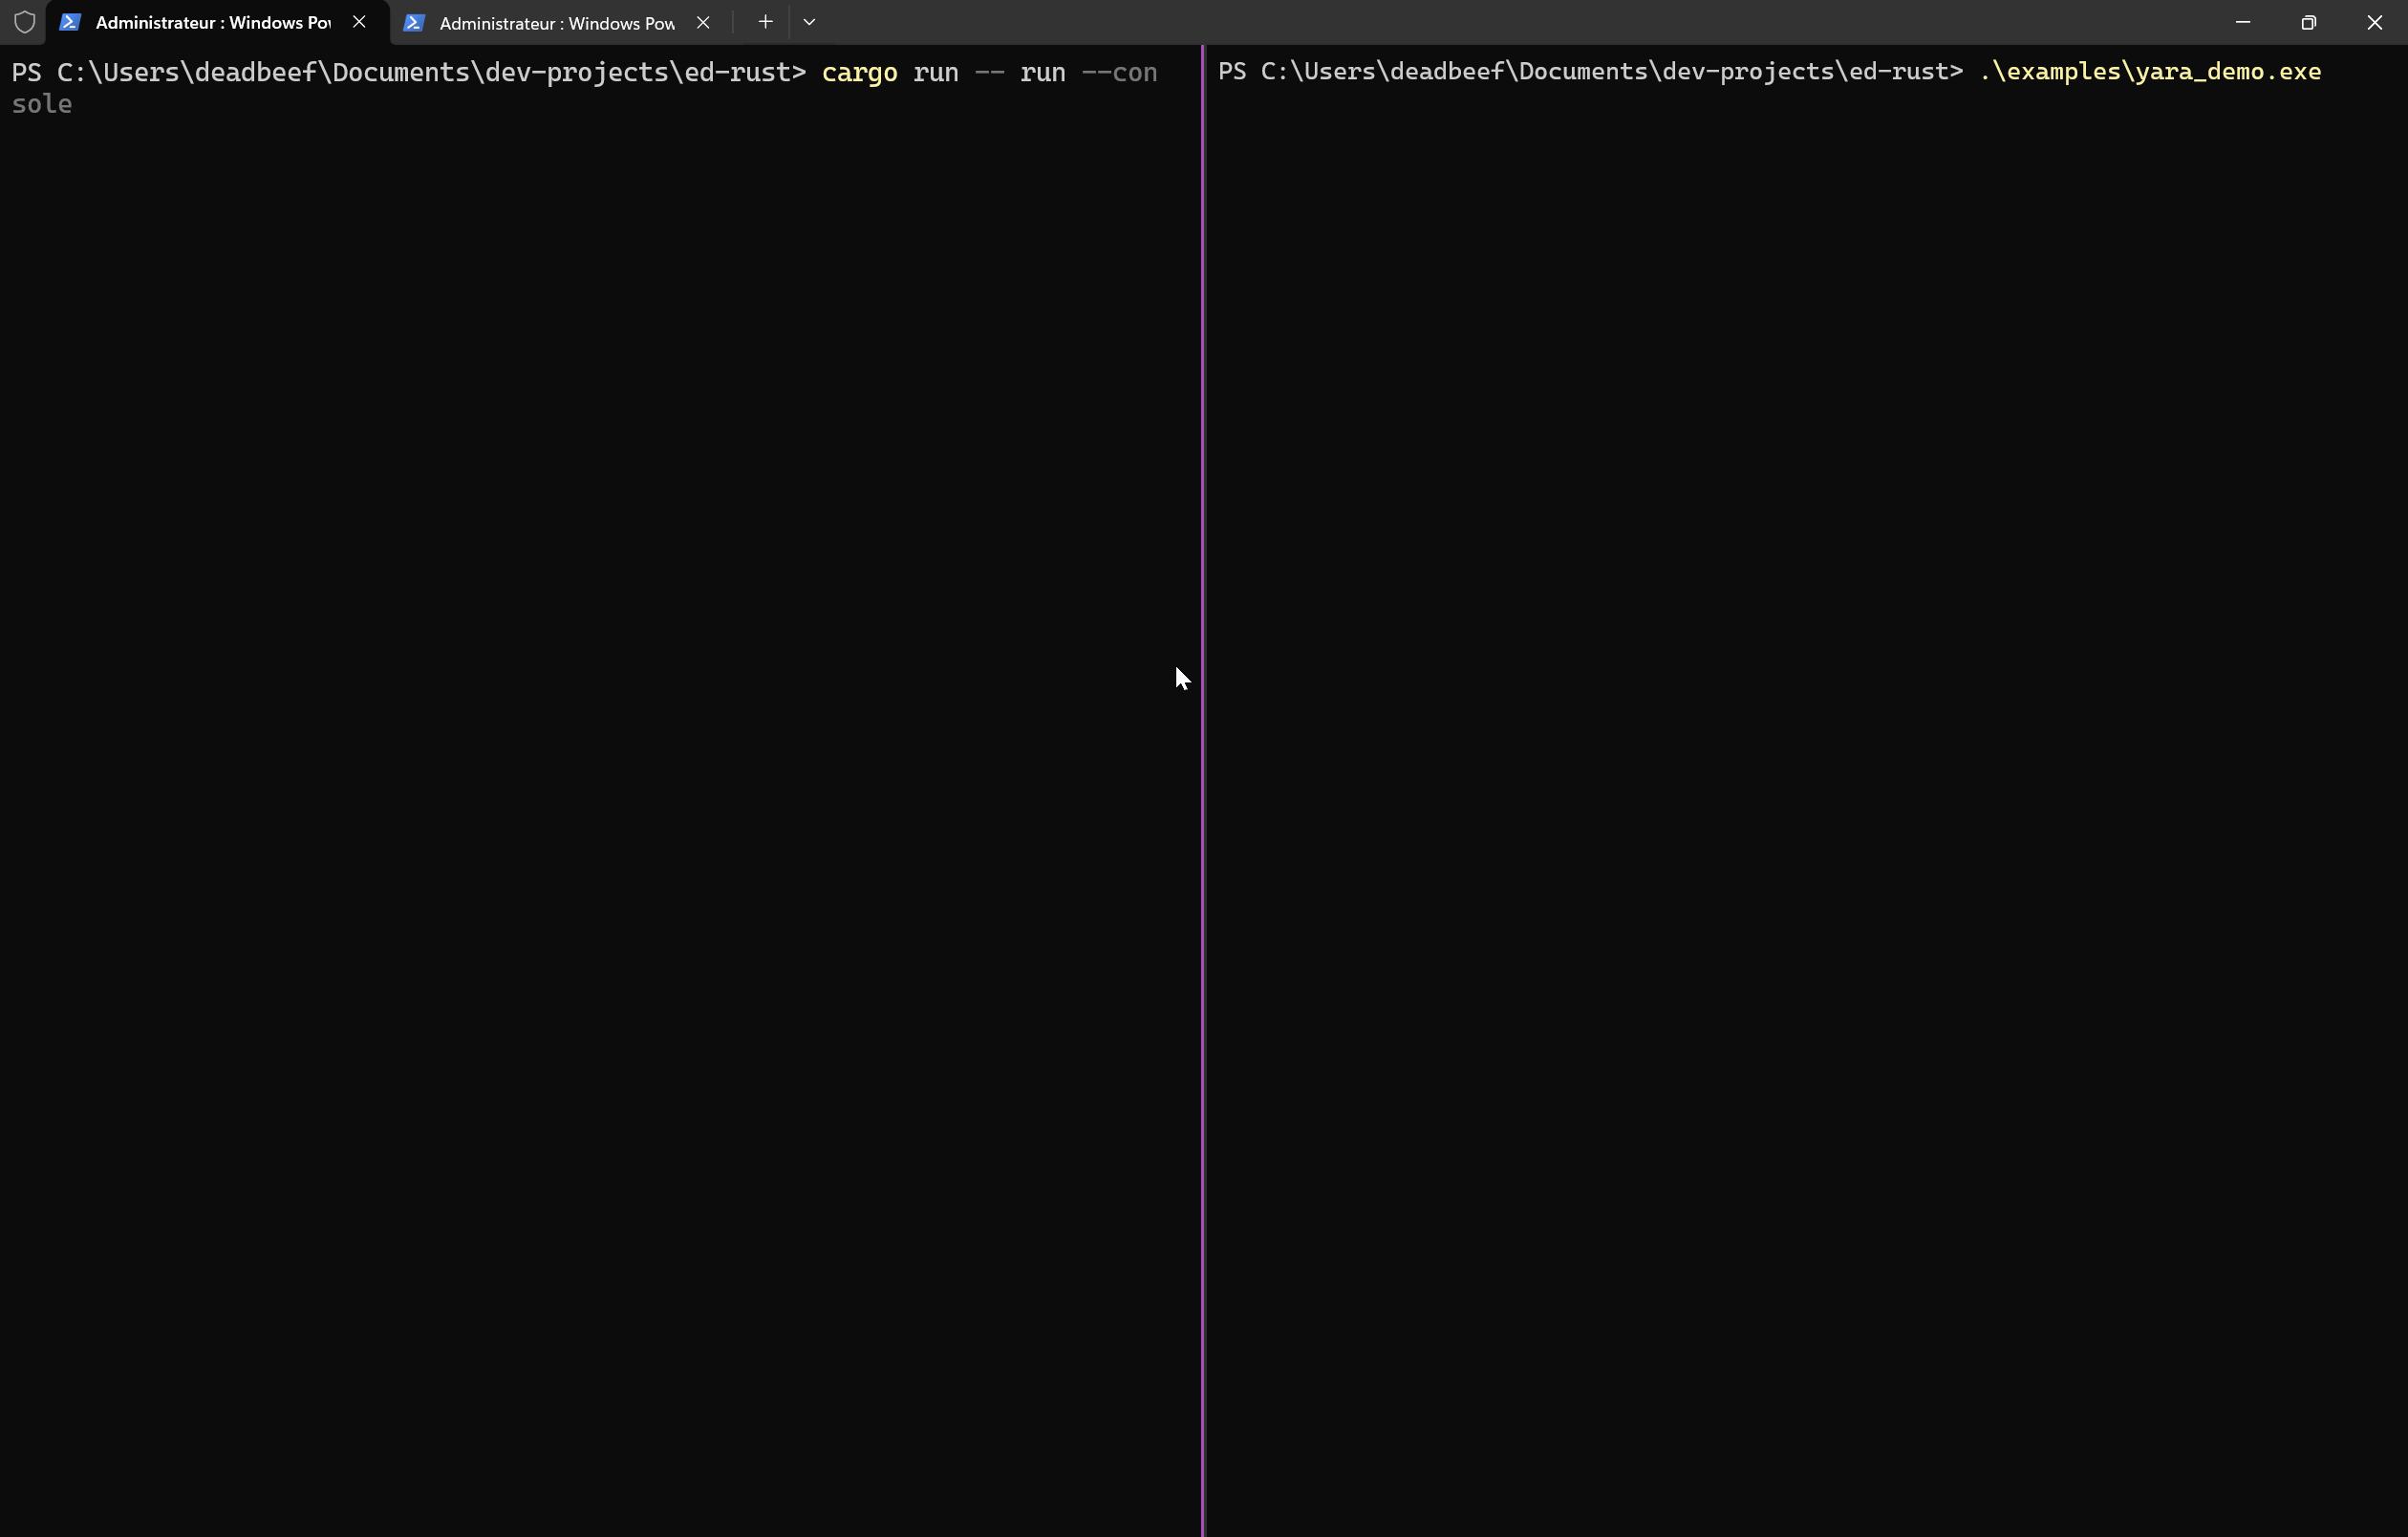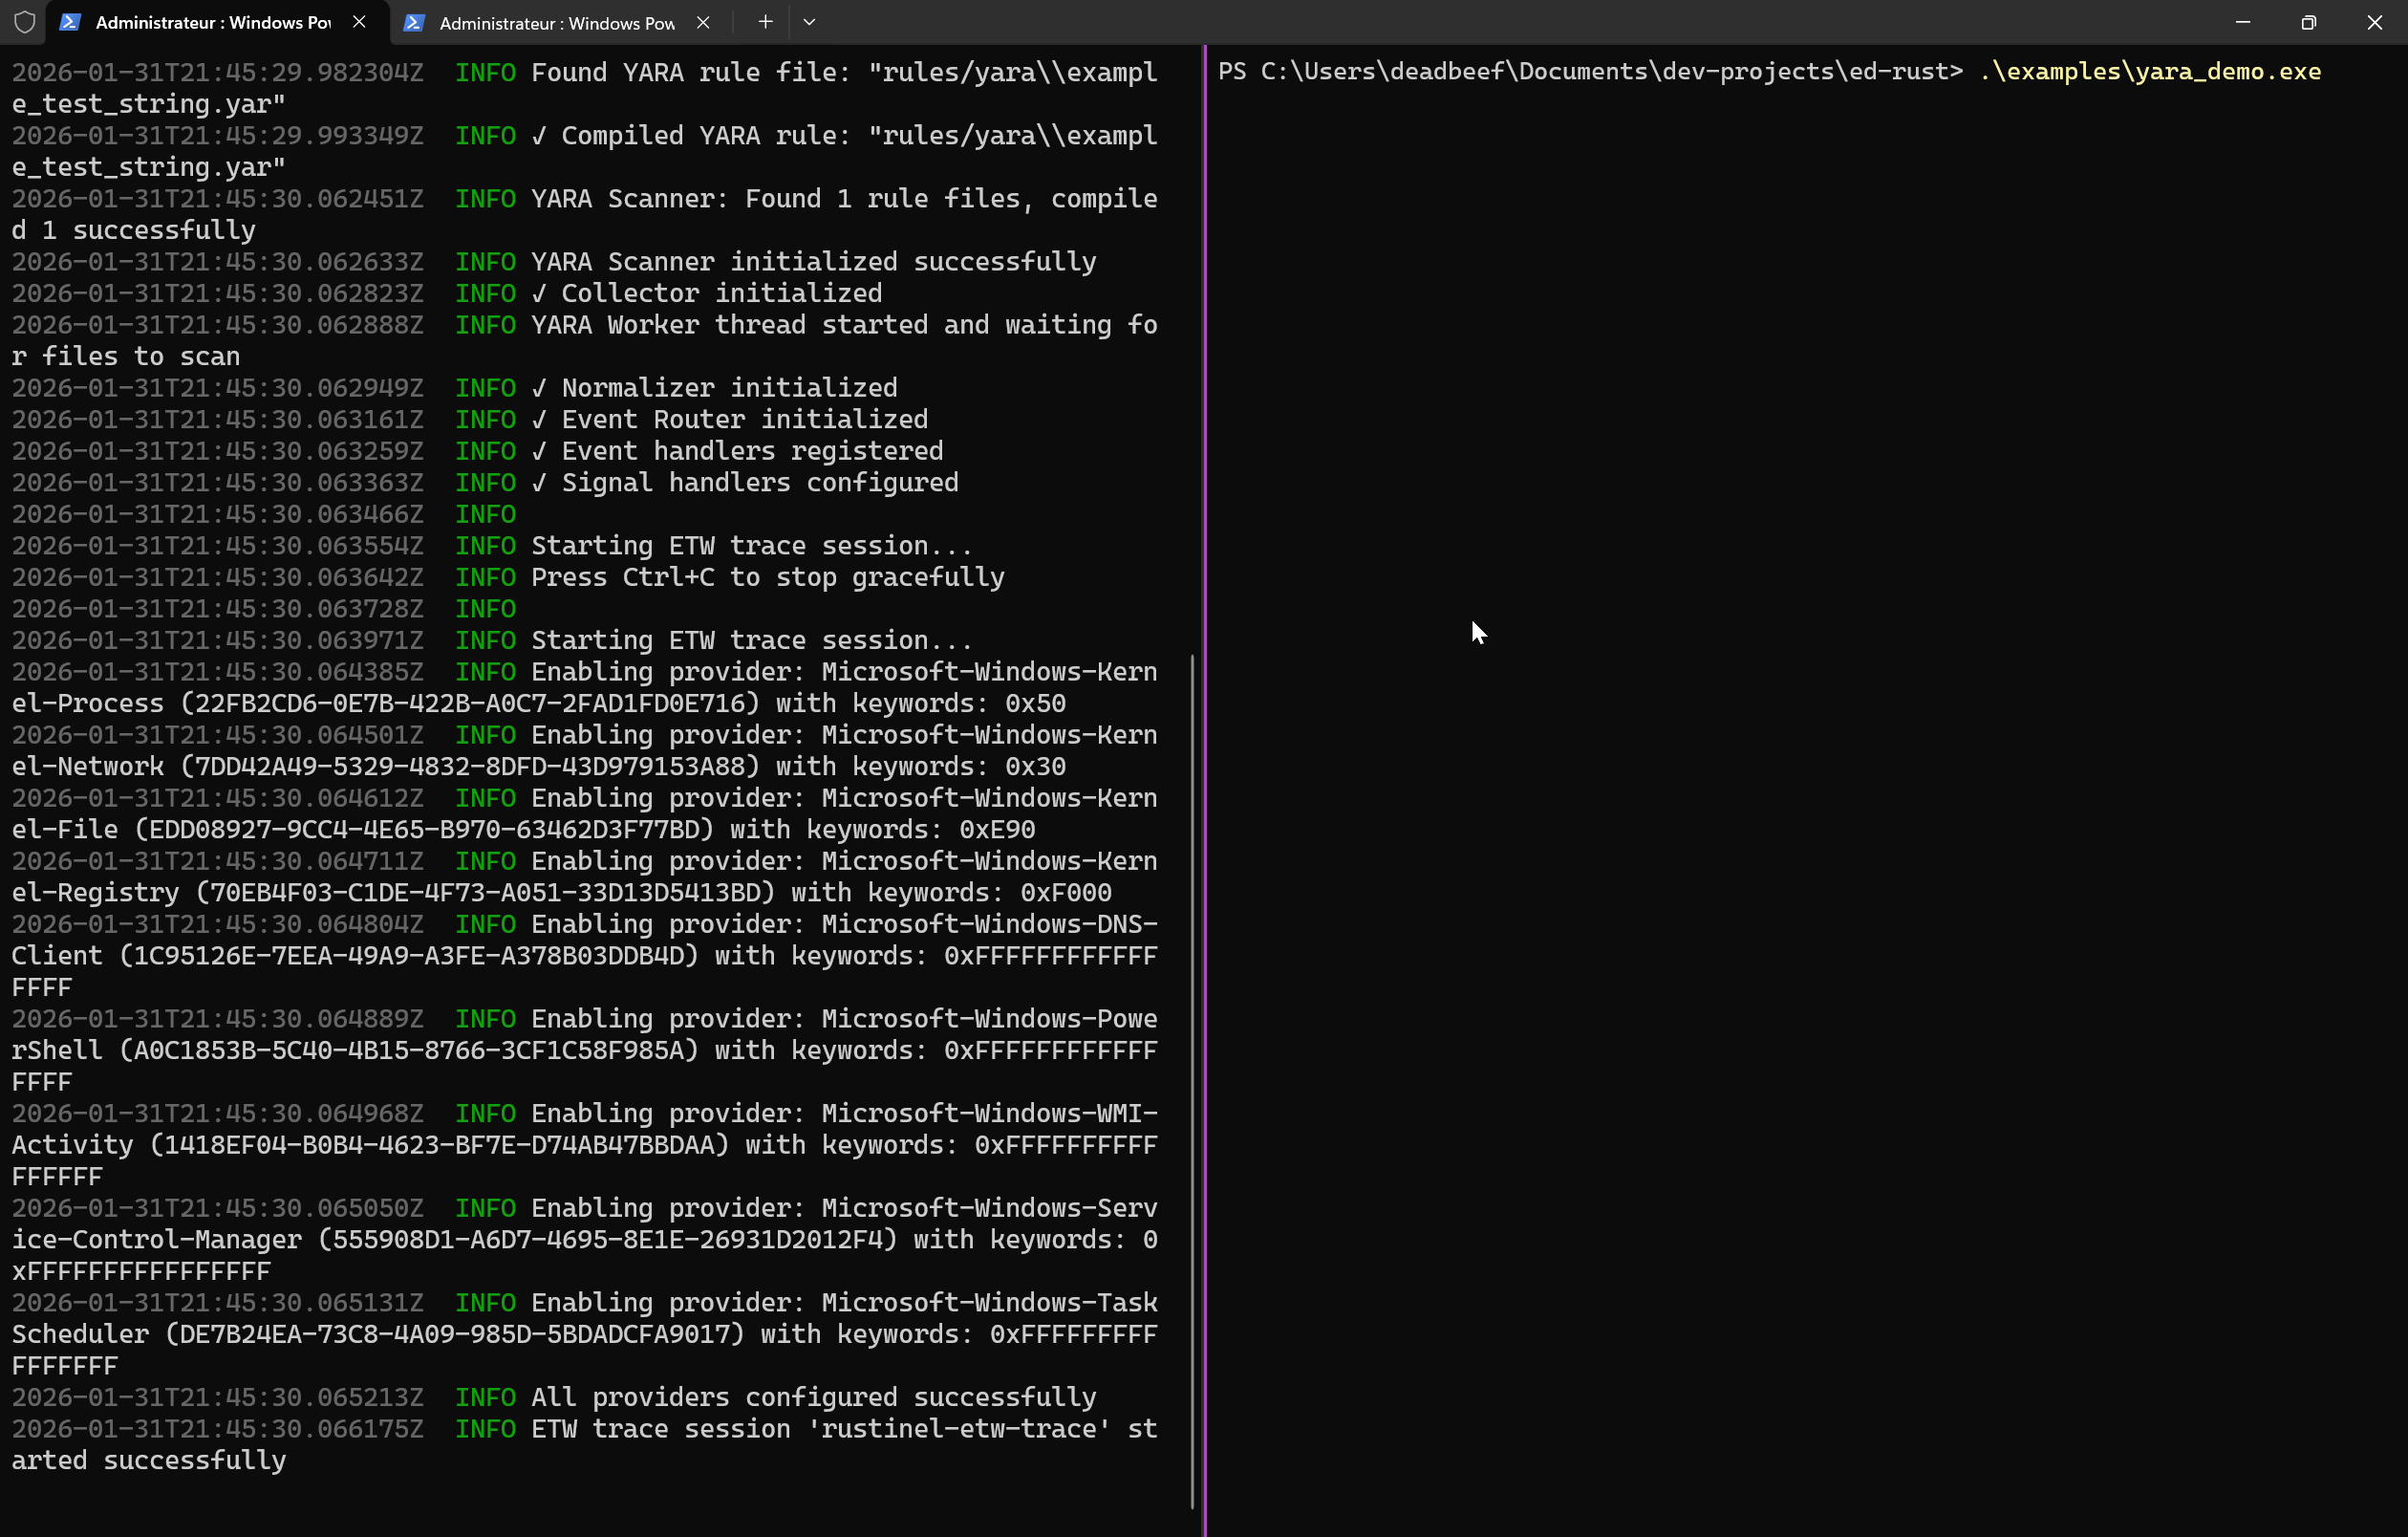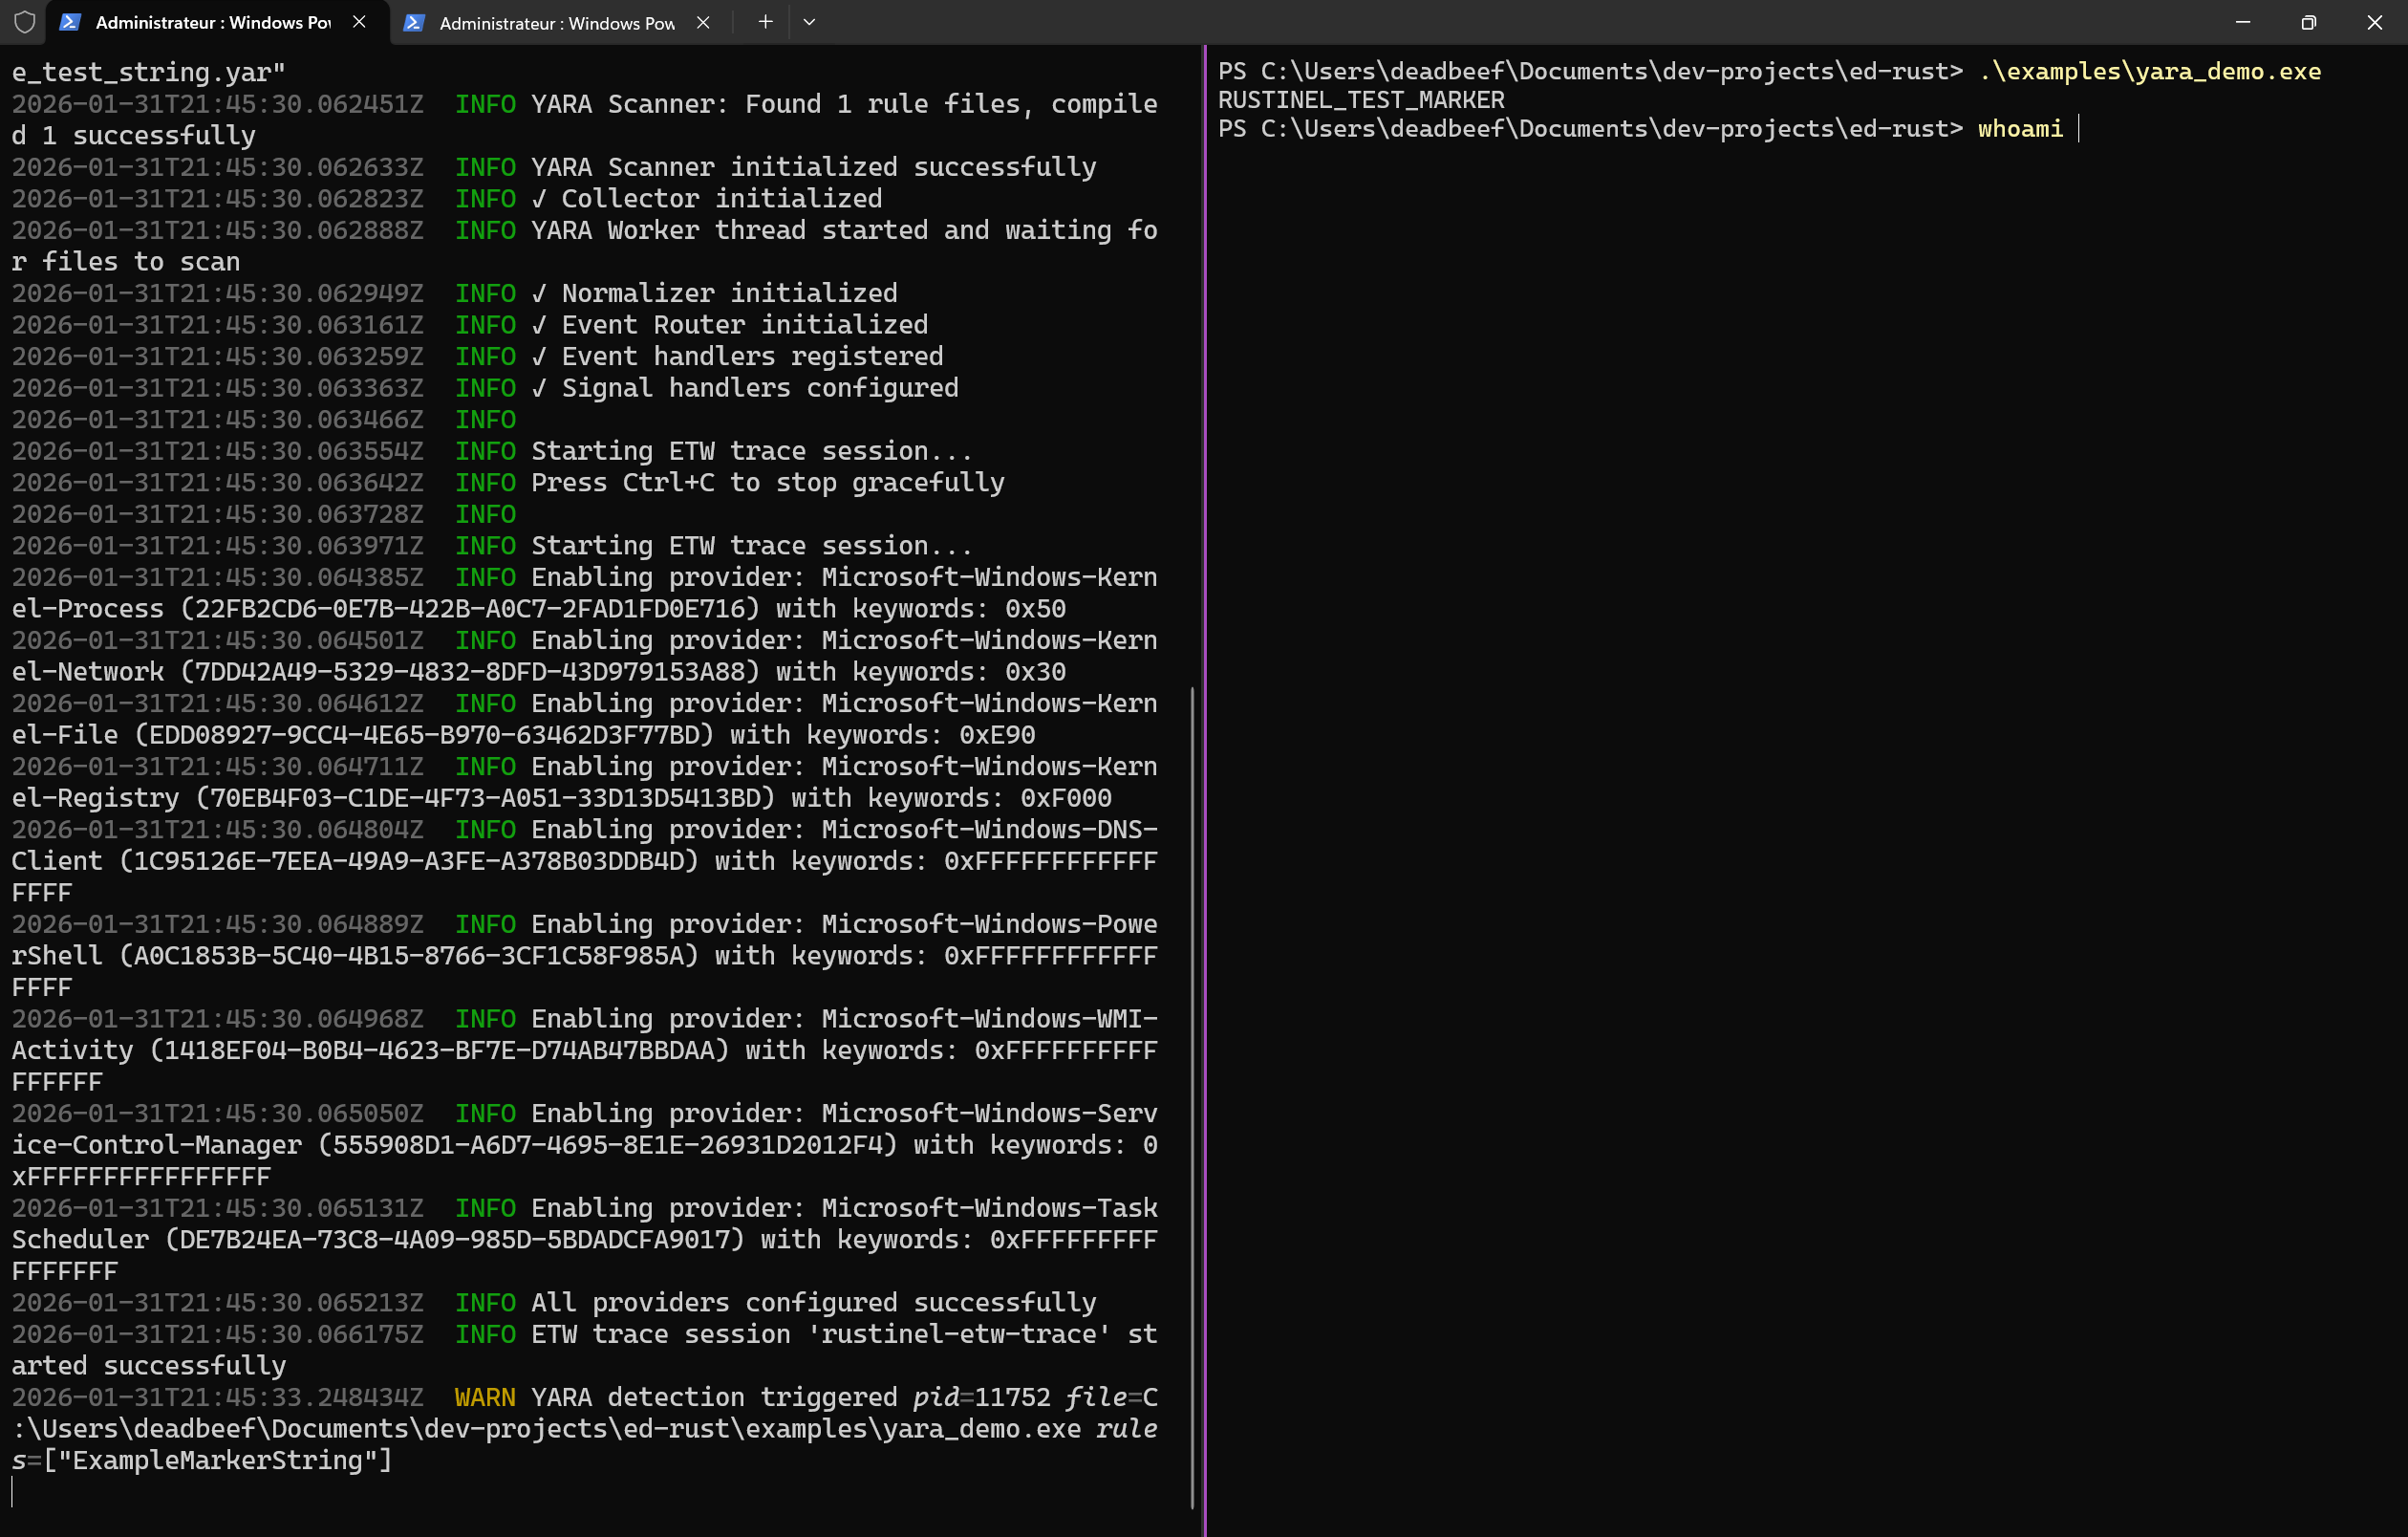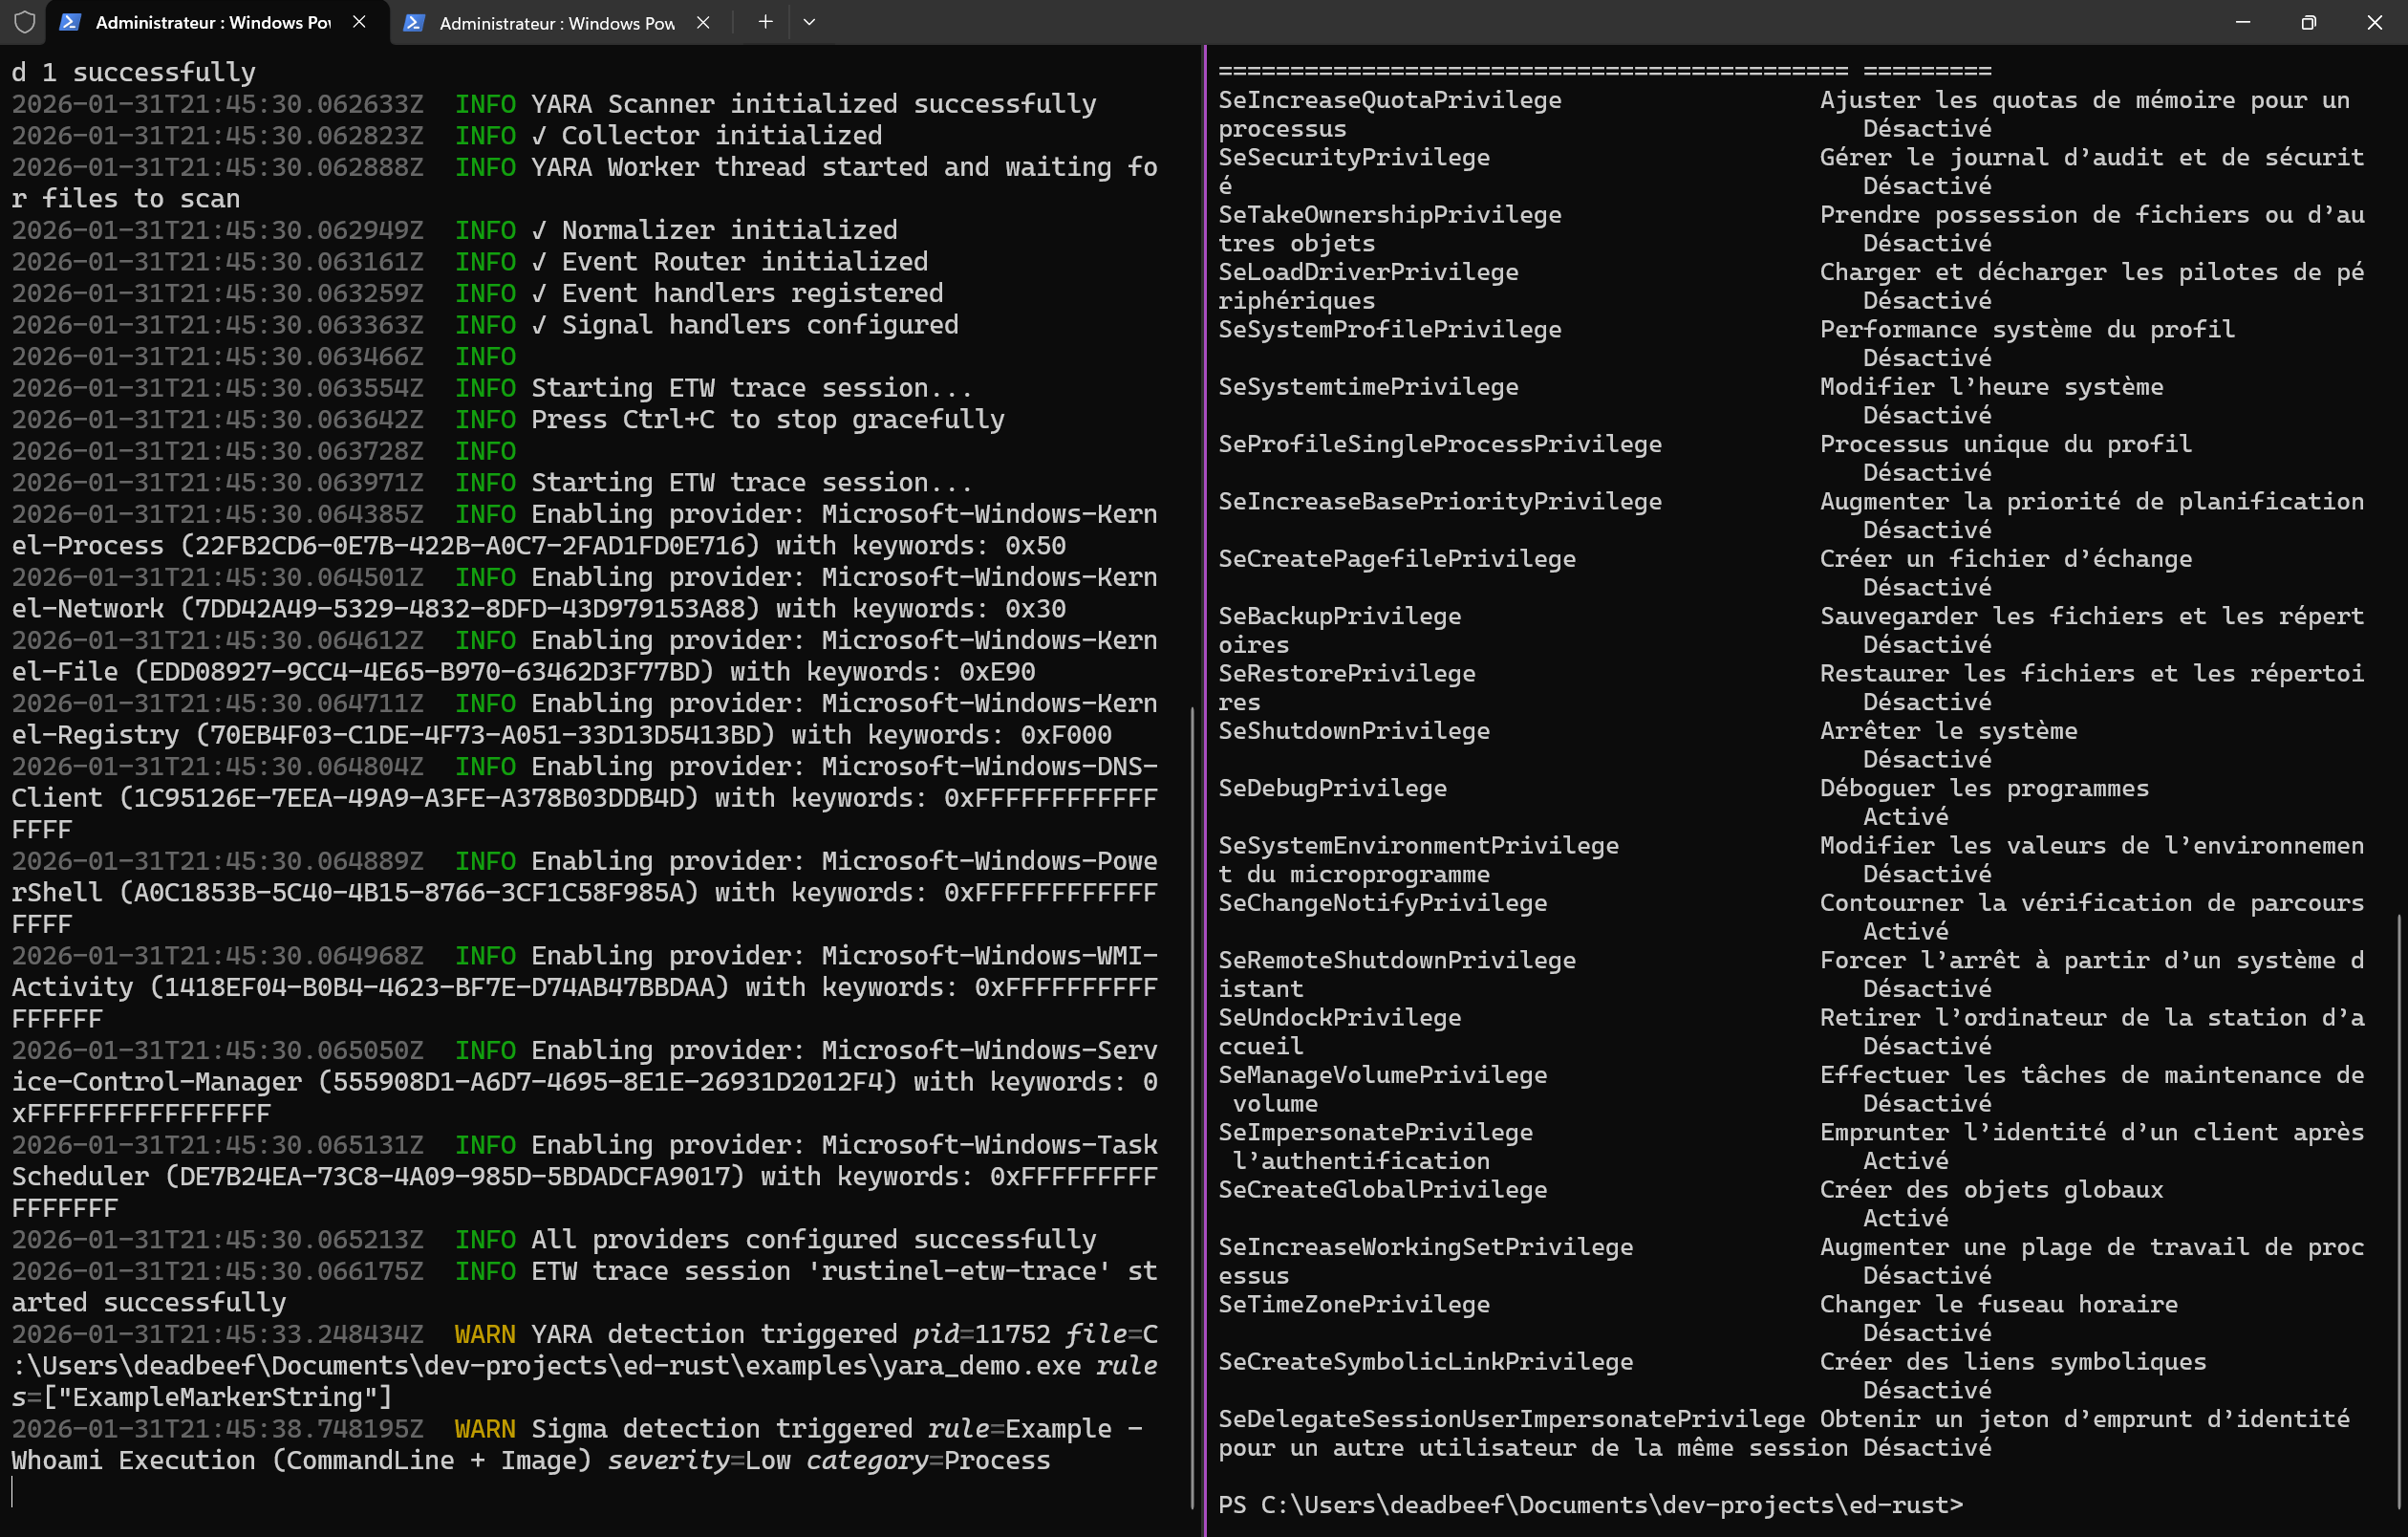 karib0u/rustinel
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.
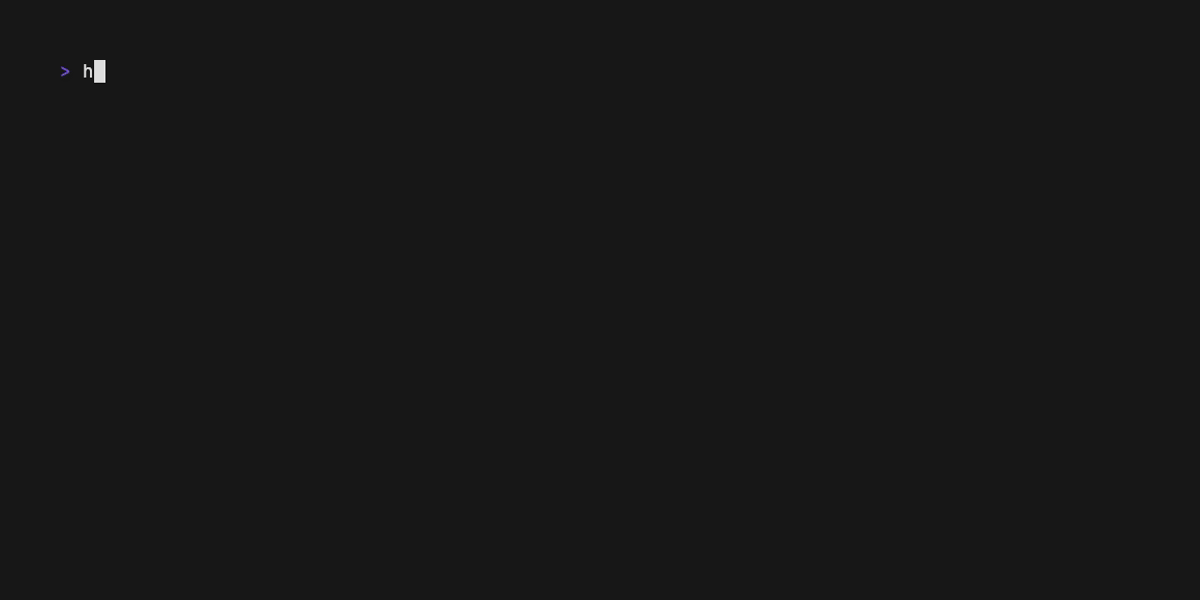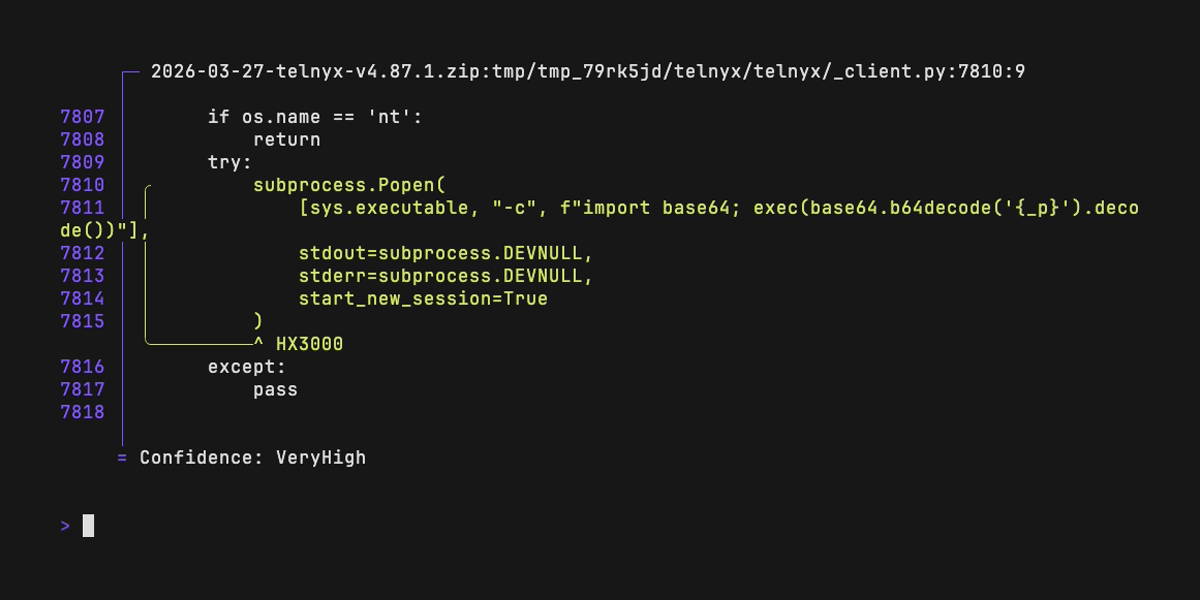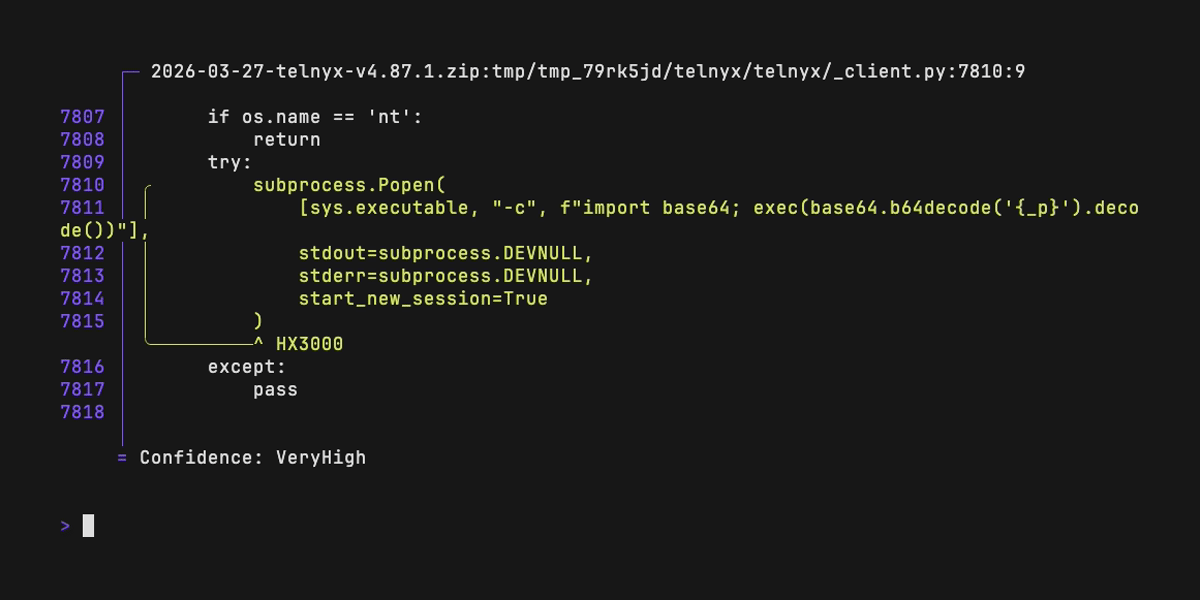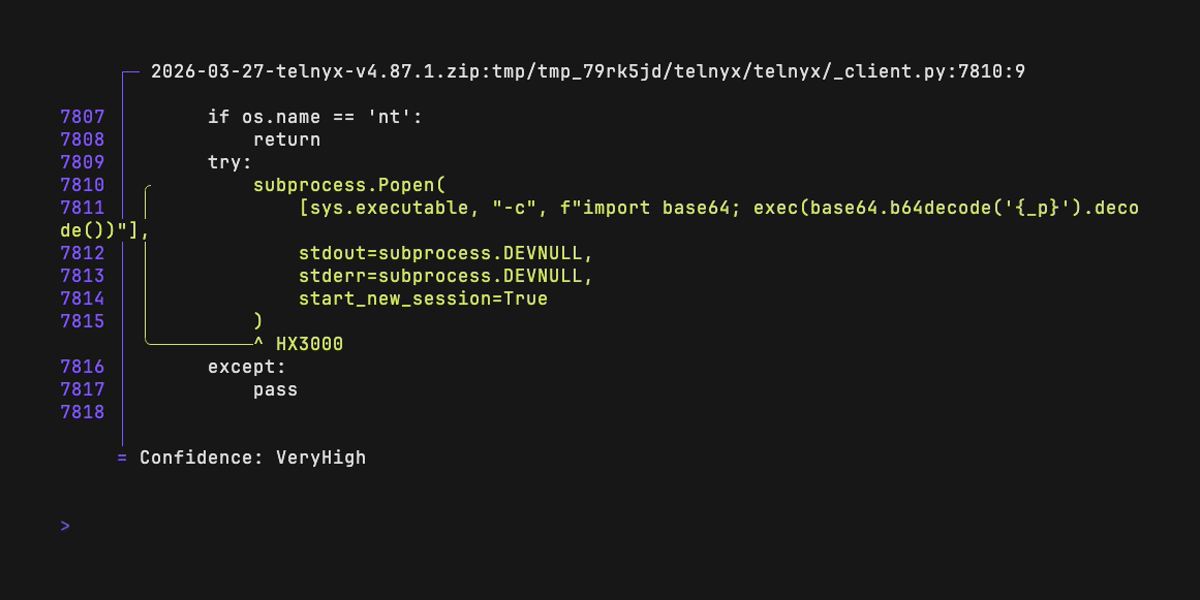 rushter/hexora
Static analysis of malicious Python code
 nomi-sec/nvd-database
📕NVD Database
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.